31 results for “CryptoBilis”

 bleepingcomputer.comarticle🛡️ Security
Trezor warns of a suspected crypto-theft implant in a Trezor Safe 5 sold by reseller CryptoBilis in Southeast Asia. An Indonesian buyer found an extra board with a cellular module and antenna between the main board and screen, apparently able to read the recovery phrase and send it over mobile networks. Trezor has not examined the device, advises moving funds to a new wallet for any CryptoBilis purchase since March 2026, and notes a similar Ledger implant was confirmed.
TrezorLedger
CryptoBilisTokopediarecovery phrase
Blockchain, Hardware & RF, Supply Chain· Published and added 30 Oct 2026

 protos.comarticle🛡️ Security
Trezor says a user reported a Safe 5 wallet bought from Malaysian reseller CryptoBilis in August 2026 with a hidden board between the main board and screen, carrying a cellular module and antenna. The implant allegedly reads the screen, including the wallet backup, and sends it over a mobile network when plugged in. Trezor has not yet examined the device, has dropped CryptoBilis (9 October), and is replacing wallets bought since March 2026.
TrezorLedger
CryptoBilisDanny Sanders
Hardware & RF, Blockchain, Threat Intel· Published and added 30 Oct 2026

 decrypt.coarticle🛡️ Security
Trezor warned buyers of its wallets from reseller CryptoBilis (March 2026 onward) to move funds, after an Indonesian customer reported a hardware implant in a Safe 5 bought in August 2026. The report describes a board with a cellular module between mainboard and screen that reads the wallet backup and sends it over a mobile network. Trezor has not yet examined the device. It found no tampering in four other CryptoBilis units.
Trezor Safe 5LedgerBitcoin
CryptoBilisTrezorLedger Donjon+3
Hardware & RF, Supply Chain, Blockchain· Published and added 30 Oct 2026
📡
 theblock.coarticle🛡️ Security
Trezor reported a suspected hardware implant in a Safe 5 bought in August 2026 from reseller CryptoBilis via Tokopedia. The alleged implant is a board with a cellular module that reads the screen, including recovery phrases. Trezor has not examined the device and found no tampering in four other units, and it told buyers who purchased from the reseller since March 2026 to move funds.
Trezor Safe 5
CryptoBilisTokopediaTrezor
Hardware & RF, Blockchain, Supply Chain· Published and added 30 Oct 2026

 en.cryptonomist.charticle🛡️ Security
Trezor advised everyone who bought wallets from reseller CryptoBilis since March 2026 to move funds to a new wallet with a new recovery phrase. An Indonesian customer reported a Safe 5 bought via Tokopedia in August 2026 with an extra board holding a cellular module that allegedly sends the wallet backup out. Trezor has not yet examined the device. Ledger separately confirmed tampering on CryptoBilis devices in October 2026.
TrezorLedger
CryptoBilisTokopediaSEAL 911+1
Hardware & RF, Supply Chain, Blockchain· Published and added 30 Oct 2026

 hackers-arise.comarticle🛡️ Security
Hackers Arise article on the October 2026 attack in which Ledger Nano X devices sold by the reseller CryptoBilis carried a hidden circuit board that taps the SPI bus to the screen, rebuilds the 24-word recovery phrase and sends it out over LTE. Losses are estimated at $86 million to over $100 million. The device still passes Genuine Check. It lists safe purchasing, checking and recovery steps, plus BIP-39 passphrase and multisig advice.
LedgerBitcoinEthereum+1
CryptoBilisMark KarpelèsTibane Labs+4
Hardware & RF, Blockchain· Published and added 21 Oct 2026
🔗
 halborn.comarticle🛡️ Security
The Ledger supply chain incident of October 2026: on-chain analysis estimates $93 million was stolen after devices sold by the reseller CryptoBilis carried an implant with an eSIM. The implant watched the screen during setup, captured the 24-word recovery phrase and sent it over LTE, without touching the Secure Element. Tether froze about $10 million USDT. Reports from Changi Airport and MediaMarkt stores remain unconfirmed.
Ledger
CryptoBilisMark KarpelèsTether
Blockchain, Hardware & RF, Supply Chain· Added 20 Oct 2026

 rekt.newswriteup🛡️ Security
Rekt write-up on LTE-equipped hardware implants found in Ledger Nano X and Flex wallets sold through resellers such as CryptoBilis and MediaMarkt. The implants read the recovery phrase off the screen during setup and exfiltrate it over an eSIM/LTE modem, so Ledger's Genuine Check and Secure Element never detect them. It covers the teardown timeline (Joe Grand, Mark Karpelès, a Japan-based researcher), the 47-minute multi-chain drain (Bitquery estimates about $102M across 324 wallets, unverified by Ledger), the laundering path via USDD, THORChain, Tornado Cash and Zcash, the CryptoBilis ownership change, and the failure of "authorized reseller" trust.
LedgerTrezorTron+3
CryptoBilisMark KarpelèsJoe Grand+14
Blockchain, Hardware & RF, Threat Intel· Added 17 Oct 2026
 galaxy.comarticle🛡️ Security
Galaxy Research's weekly brief leads with the roughly $91M theft from Ledger devices sold via the reseller CryptoBilis. A hidden hardware implant read the 24-word recovery phrase off the screen during setup and sent it over LTE through an eSIM, leaving the Secure Element untouched so Genuine Check still passed. Galaxy's onchain tally covers 474 victim addresses, 88% of the value moved in one hour on Oct. 9, and about $56.6M was still parked as of Oct. 15, with Tornado Cash use and a $10M Tether freeze. It places the theft alongside the Coldcard weak-seed, Liquid peg-out and Bitget compromises, and ends with buyer and custody advice. The Papertrade and OCC debanking sections are unrelated to security.
LedgerColdcardBitcoin+2
CryptoBilisGenuine CheckTornado Cash+8
Blockchain, Hardware & RF, Supply Chain· Added 16 Oct 2026
galaxy.comarticle🛡️ Security Galaxy Research newsletter piece on the roughly $91M theft from buyers of Ledger hardware wallets sold by the reseller CryptoBilis. A hidden component reads the 24-word recovery phrase off the screen during setup and sends it over LTE via an eSIM. The Secure Element and Genuine Check are untouched, so the check passes on tampered units. It traces the drain across 474 victim addresses on Bitcoin, Ethereum and TRON, including 88% of the value moving in one hour on Oct. 9, and the laundering and freezes (Tornado Cash, Tether). It also places the incident among the quarter's other custody and infrastructure failures (Coldcard weak seeds, Liquid, Bitget) and gives buying and operational guidance.
LedgerBitcoinEthereum+2
CryptoBilishardware implantGenuine Check+9
Blockchain, Hardware & RF, Supply Chain· Added 16 Oct 2026

en.cryptonomist.charticle🛡️ Security News report on a Southeast Asia supply-chain breach in which Ledger devices sold via resellers such as CryptoBilis were modified with hidden chips. The chips read 24-word recovery phrases from the screen signals during setup and sent them out over LTE. Tether froze $10M USDT tied to the theft, and Ledger suspended sales in several Asian markets. It also covers Ledger's Android-based Atom signer, which adds a protective enclosure, screen and back-cover removal sensors with their own battery, tamper-evident packaging, and website-only initial sales.
LedgerAndroid
CryptoBilisTether
Hardware & RF, Blockchain· Published and added 15 Oct 2026
decrypt.coarticle🛡️ Security Ledger asked resellers and distributors in Indonesia, Singapore, Thailand, the Philippines, Vietnam, Malaysia and Hong Kong to pull its hardware wallets while it investigates devices fitted with a hidden implant. Its Donjon team found the implant reads the 24-word recovery phrase from the screen during setup and sends it out over LTE. All confirmed losses trace to devices sold through reseller CryptoBilis, and Specter has traced over $86M in suspected thefts, which Ledger has not verified. Ledger says its own infrastructure and direct channel show no compromise. MediaMarkt Saturn halted sales after a German customer reported an implant, and Trezor is ending reseller authorizations on January 1, 2027.
LedgerTrezor
CryptoBilisSpecterDonjon+1
Blockchain, Supply Chain, Hardware & RF· Published and added 14 Oct 2026
 bankless.comarticle🛡️ Security
News roundup on hardware implants found in Ledger wallets sold through authorized resellers, starting with CryptoBilis in Southeast Asia and then Singapore, Japan and German MediaMarkt stores. The implants read the 24-word recovery phrase off the screen during setup and send it out over a hidden cellular link, while Ledger's secure chip stays untouched so the devices look genuine. Researchers describe three generations dating to 2025, each harder to detect. Suspected losses are put at $86M (Specter) to $103M (Yfarmx), and neither figure is verified by Ledger.
Ledger
CryptoBilisSpecterYfarmx+3
Hardware & RF, Blockchain· Published and added 13 Oct 2026
🔗
theblock.coarticle🛡️ Security Ledger's Donjon team confirmed that Ledger signers sold by the reseller CryptoBilis contain an unauthorized implant. It captures the 24-word recovery phrase during setup and sends it over LTE using a provisioned eSIM. It does not touch the Secure Element, the OS, or transaction signing. Onchain researchers estimate losses above $86M, but Ledger says that figure is unverified. MediaMarkt Saturn halted European Ledger sales after a tampered unit was reported in Germany, and Trezor and OneKey tightened or revoked reseller authorizations. The case shows a reseller-channel tampering risk for hardware wallets.
LedgerTrezorOneKey
CryptoBilisLedger DonjonMediaMarkt Saturn+2
Blockchain, Hardware & RF, Threat Intel· Published and added 13 Oct 2026
protos.comarticle🛡️ Security Protos reports that German retailer MediaMarkt pulled all Ledger products after teardowns of Ledger hardware wallets showed physical spyware implants, tied to an $86M drain of wallets bought from Malaysian reseller CryptoBilis. Ledger's investigation concluded the implant recorded the 24-word recovery phrase and sent it out over an attached eSIM. Mark Karpelès has helped identify implants in dismantled devices from MediaMarkt, LazMall (Philippines), CryptoBilis and Metapod (Singapore airport). Ledger has so far confirmed only the CryptoBilis devices and says it is reviewing reports of implants elsewhere.
Ledger
CryptoBilisMark KarpelèsMediaMarkt+2
Hardware & RF, Supply Chain, Blockchain· Published and added 13 Oct 2026

en.cryptonomist.charticle🛡️ Security Ledger's Donjon team confirmed on October 10, 2026 a physical implant inside a hardware wallet sold by Malaysia-based reseller CryptoBilis. The implant reads the device display, decodes the 24-word recovery phrase with a microcontroller, and exfiltrates it over LTE via a provisioned eSIM, leaving the Secure Element, OS, transactions and signatures untouched. Onchain investigator Specter traced over $86 million in suspected thefts across Ethereum, Tron and Bitcoin; Ledger advises CryptoBilis buyers to migrate funds to a new device with a new recovery phrase.
Ledger
CryptoBilisSpecterLedger Donjon
Hardware & RF, Blockchain· Published and added 13 Oct 2026
decrypt.coarticle🛡️ Security Ledger's Donjon security team confirmed an unauthorized hardware implant inside Ledger signers sold by Southeast Asian reseller CryptoBilis. The implant sits in the enclosure, reads the 24-word recovery phrase from the screen during setup, decodes it with a microcontroller, and exfiltrates it over LTE via a provisioned eSIM, without touching the Secure Element, OS, or signatures. Onchain investigator Specter traced over $86M in suspected thefts across Ethereum, Tron and Bitcoin; Ledger is reviewing reports of tampered devices elsewhere and advises affected buyers to move funds to a new device with a new seed.
Ledger
CryptoBilisLedger DonjonSpecter+2
Hardware & RF, Blockchain, Threat Intel· Published and added 13 Oct 2026
 securityweek.comarticle🛡️ Security
SecurityWeek reports that Ledger signers sold through the Southeast Asia reseller CryptoBilis had a hardware implant soldered onto the circuit board. The implant reads the screen during setup, decodes the 24-word recovery phrase with a microcontroller and sends it over LTE through a provisioned eSIM. Ledger says all confirmed losses trace to CryptoBilis devices and advises buyers from the last 90 days to move funds to a new signer with a new seed. On-chain investigator Specter puts losses at up to $86M, a figure Ledger has not confirmed.
Ledger
CryptoBilisSpecter
Blockchain, Hardware & RF, Supply Chain· Published and added 13 Oct 2026
 coindesk.comarticle🛡️ Security
Ledger says some hardware wallets sold by the reseller CryptoBilis contained a covert implant inside the enclosure. Its microcontroller recognised the 24-word recovery phrase when it was displayed during setup and sent it to attackers over LTE using an eSIM. Ledger says its secure element, OS, transaction signing and internal systems were not compromised. Onchain researchers estimate up to $93.2M lost across more than 300 wallets, and Tether froze $10M of USDT. Ledger's guidance is not to initialize units bought from the reseller and to move funds to a new device with a fresh phrase if already used.
Ledger
CryptoBilisTether
Hardware & RF, Blockchain, Threat Intel· Published and added 13 Oct 2026
 thedefiant.ioarticle🛡️ Security
The Defiant reports that Mt. Gox's Mark Karpelès says a Ledger Flex hardware wallet bought at an airport contained a spy implant. The buyer, Ben Yorke, named Metapod as the retailer. Ledger says the verified fund losses in its investigation remain tied to wallets sold by CryptoBilis. The captured text is only the headline and standfirst, so the technical details of the implant are not available. The claim is an allegation of third-party-retailer hardware tampering against a Ledger statement that points elsewhere.
Ledger
Mark KarpelèsBen YorkeMetapod+1
Supply Chain, Hardware & RF· Published and added 13 Oct 2026
thedefiant.ioarticle🛡️ Security The Defiant reports Ledger's claim that hardware wallets sold by the reseller CryptoBilis carried added LTE-capable implants that transmit users' recovery phrases. Ledger says the implant leaves the secure chip and operating system untouched, and that its Genuine Check attestation cannot rule out this kind of tampering. It shows how reseller-channel hardware modification can defeat device attestation and compromise key custody. The fetched page held only the standfirst, so technical details such as the implant's design and how many devices were affected are not confirmed.
Ledger
CryptoBilisGenuine Check
Hardware & RF, Blockchain· Published and added 13 Oct 2026
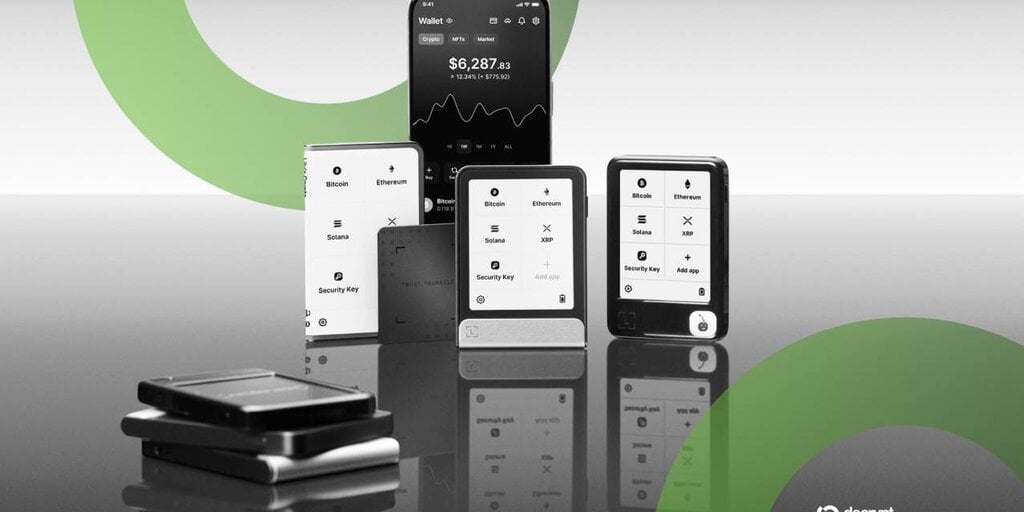
decrypt.coarticle🛡️ Security Decrypt reports Ledger's 72-hour update: all confirmed wallet-draining cases involve devices sold by Southeast Asian reseller CryptoBilis, which has stopped hardware wallet sales. Onchain investigators Specter and YFarmX traced over $86M in suspected thefts across Ethereum, Tron and Bitcoin. They describe laundering through Tornado Cash, Zcash's shielded pool and a USDT-to-USDD swap to avoid Tether freezes. An unverified claim of tampered devices (extra cables, LTE module) bought at European retail stores is also covered. Ledger advises CryptoBilis buyers not to set up devices and to move funds to a new seed phrase on a device bought from Ledger.
LedgerEthereumBitcoin+2
CryptoBilisSpecterYFarmX+5
Blockchain, Hardware & RF, Threat Intel· Published and added 12 Oct 2026
protos.comarticle🛡️ Security Protos reports additional alleged Ledger hardware wallets with physical spyware implants, found in devices from a German MediaMarkt reseller, a Philippine LazMall reseller and a Stax model bought from CryptoBilis. Mark Karpelès found that the implants read the device's screen output to capture seed phrases and evade Ledger's Genuine Check. The earlier CryptoBilis-linked incident of Oct 9 drained over $86M. Ledger told resellers to use only authorized channels and never restock returned units, and teardowns have also shown many devices to be clean.
Ledger
CryptoBilisGenuine CheckMark Karpelès+4
Hardware & RF, Blockchain· Published and added 12 Oct 2026
coindesk.comarticle🛡️ Security CoinDesk reports that up to $93–94.5M in mostly USDT and TRON tokens was drained from 315–521 wallets across six or seven blockchains. The wallets were tied to Ledger hardware wallets sold by the authorized reseller CryptoBilis. Ledger confirmed an unauthorized hardware implant in at least one device but did not say how the devices were tampered with. Tether froze $10M, some funds moved through Tornado Cash and Zcash, and Ledger told affected users not to set up unused devices and to move funds to a new device with a fresh recovery phrase. The figures come from Bitquery and YFarmX onchain estimates, not a confirmed Ledger loss total.
LedgerTronZcash+1
CryptoBilisTetherBitquery+1
Blockchain, Supply Chain, Hardware & RF· Published and added 12 Oct 2026
bleepingcomputer.comarticle🛡️ Security Ledger confirmed that devices sold by Southeast Asian reseller CryptoBilis carried an unauthorized hardware implant that drained users' crypto wallets. Researchers Mark Karpelès and Tibane Labs describe the implant: an STM32G431 MCU, eSIM and shielded LTE module hidden behind the OLED screen, which captures display output and button presses to recover the seed phrase and sends it out over LTE. The article covers two implant variants, the telltale antenna wire, and Ledger's guidance (avoid unauthorized resellers, move funds to a new seed). Ledger also warns that its Genuine Check cannot detect implants when the original Secure Element is intact.
Ledger
CryptoBilisMark KarpelèsTibane Labs+3
Hardware & RF, Blockchain, Threat Intel· Added 13 Oct 2026, published 12 Oct 2026
coindesk.comarticle🛡️ Security CoinDesk reports that Ledger confirmed an unauthorized hardware implant in at least one device sold by the Southeast Asian reseller CryptoBilis. On-chain researchers estimate $86–93M was drained from more than 300 wallets across Bitcoin, Ethereum and Tron. Ledger says its internal systems and direct sales are unaffected, and it advises not initializing unused devices and moving funds to a new seed on a device bought directly from Ledger. It also covers the reseller's sales suspension, Ledger's tightened distributor chain-of-custody rules, unverified speculation that the reseller was bought out, and the July 2026 Coldcard seed-generation flaw.
LedgerBitcoinEthereum+1
CryptoBilisChangpeng Zhao
Blockchain, Hardware & RF, Threat Intel· Published and added 12 Oct 2026
protos.comarticle🛡️ Security Protos reports that Ledger users who bought devices from the Malaysian/Southeast Asian reseller CryptoBilis have been drained of an estimated $72M to over $86M, per on-chain tracing by analysts Specter and Tanuki42. Ledger told CryptoBilis to pause sales and shipments, and advised buyers from the past 90 days not to set up their devices, or to move funds to a new signer if they already had. The article cites Mark Karpelès on reseller wallets found tampered with and implanted with spyware, and Taylor Monahan warning that there is no sign of a zero-day and that panic migration invites phishing and fake-ad drainers.
Ledger
CryptoBilisSpecterTanuki42+3
Supply Chain, Blockchain· Published and added 9 Oct 2026
decrypt.coarticle🛡️ Security Ledger is investigating fund losses among Southeast Asian customers who bought hardware wallets from the reseller CryptoBilis. It has asked the reseller to pause sales and told buyers from the last 90 days not to set up their devices, or to move funds to a new device with a fresh seed phrase. Onchain investigator Specter traced about $86–87M in thefts across Ethereum, Tron and Bitcoin. Ledger has confirmed neither the figure nor the cause, though pre-compromised devices shipped with an attacker-known recovery phrase are the suspected mechanism.
LedgerEthereumBitcoin+1
CryptoBilisSpecterArkham
Blockchain, Supply Chain· Published and added 9 Oct 2026

en.cryptonomist.charticle🛡️ Security News report on a suspected supply-chain attack on Ledger hardware wallets sold by the Southeast Asian reseller CryptoBilis. Ledger asked the reseller to suspend sales and shipments, and told buyers from the last 90 days not to initialize devices. Customers who already set up a device should move funds to a new signer with a fresh seed. Onchain investigator Specter estimated more than $86M stolen from hundreds of wallets across Ethereum, TRON and Bitcoin, with 10 addresses listed. The figure is unconfirmed, and there is no evidence that Ledger's hardware or core infrastructure was compromised. The Security Alliance directs victims to its SEAL 911 Telegram bot.
LedgerEthereumTron+1
CryptoBilisSpecterSEAL 911+3
Supply Chain, Blockchain· Published and added 9 Oct 2026
🔗
theblock.coarticle🛡️ Security The Block reports that Ledger is investigating fund losses among Southeast Asian users who bought hardware wallets from the reseller CryptoBilis, an official reseller in Indonesia, Malaysia and the Philippines. Onchain researchers tanuki42 and Specter estimate losses above $72M and $86M across Bitcoin, Ethereum and Tron, but neither figure is confirmed. Ledger asked the reseller to pause sales and advised buyers from the past 90 days not to set up devices, or to move assets to a new signer with a new seed. Changpeng Zhao suggested a supply-chain attack with fake or tampered devices, and Mark Karpeles asked for circuit-board photos to check for tampering.
LedgerBitcoinEthereum+1
CryptoBilisSEAL 911tanuki42+3
Blockchain, Threat Intel· Published and added 9 Oct 2026