 Trezor warns of suspected crypto-theft implant in hardware wallet
Trezor warns of a suspected crypto-theft implant in a Trezor Safe 5 sold by reseller CryptoBilis in Southeast Asia. An Indonesian buyer found an extra board with a cellular module and antenna between the main board and screen, apparently able to read the recovery phrase and send it over mobile networks. Trezor has not examined the device, advises moving funds to a new wallet for any CryptoBilis purchase since March 2026, and notes a similar Ledger implant was confirmed.
 bleepingcomputer.comarticlePublished and added 30 Oct 2026
 Trezor reveals Malaysian reseller sold wallet with spyware
Trezor says a user reported a Safe 5 wallet bought from Malaysian reseller CryptoBilis in August 2026 with a hidden board between the main board and screen, carrying a cellular module and antenna. The implant allegedly reads the screen, including the wallet backup, and sends it over a mobile network when plugged in. Trezor has not yet examined the device, has dropped CryptoBilis (9 October), and is replacing wallets bought since March 2026.
 protos.comarticlePublished and added 30 Oct 2026
 In Other News: Anthropic Breach Dispute, UEFI Flaw Hits Most Servers, Cloudflare AI Data Leak
SecurityWeek's weekly roundup of 30 October 2026 covers CVE-2026-97631, a 16-year-old buffer overflow in TianoCore EDK II that affects PXE network boot on most servers. It also covers a Cloudflare Workers AI cross-tenant leak caused by an SGLang bug, Anthropic's dispute with Cathedral over a bug bounty intrusion, and fake AI bots probing for secrets. Other items include AI-assisted ransomware (Gold Ogre, Aur0ra), the NIK C2 framework, and North Korean IT worker sanctions.
 securityweek.comarticlePublished and added 30 Oct 2026
 Trezor Warns CryptoBilis Buyers After Report of Hardware Implant in Safe 5
Trezor warned buyers of its wallets from reseller CryptoBilis (March 2026 onward) to move funds, after an Indonesian customer reported a hardware implant in a Safe 5 bought in August 2026. The report describes a board with a cellular module between mainboard and screen that reads the wallet backup and sends it over a mobile network. Trezor has not yet examined the device. It found no tampering in four other CryptoBilis units.
 decrypt.coarticlePublished and added 30 Oct 2026
 Trezor hardware implant report: CryptoBilis buyers urged to move funds
Trezor advised everyone who bought wallets from reseller CryptoBilis since March 2026 to move funds to a new wallet with a new recovery phrase. An Indonesian customer reported a Safe 5 bought via Tokopedia in August 2026 with an extra board holding a cellular module that allegedly sends the wallet backup out. Trezor has not yet examined the device. Ledger separately confirmed tampering on CryptoBilis devices in October 2026.
 en.cryptonomist.charticlePublished and added 30 Oct 2026
- Hitachi Energy CoreTec Product
CISA advisory ICSA-26-302-03, republished from Hitachi Energy PSIRT 8DBD000258, covers OS command injection (CVE-2026-13162) and the Dirty Frag vulnerability (CVE-2026-43284) in Hitachi Energy CoreTec. CoreTec5 up to 3.4.0 and 5.0.0 are affected by both, and CoreTec4 up to 3.4.0 by CVE-2026-13162. The advisory was released 27 October 2026 and lists generic ICS mitigations. SSVC rates exploitation as none.
 cisa.govadvisoryAdded 29 Oct 2026, published 28 Oct 2026
- Hitachi Energy TRO600 series products
ICSA-26-302-02 is a CISA republication of Hitachi Energy PSIRT advisory 8DBD000224 on the TRO600 series. It covers CVE-2026-10756 and CVE-2026-106087, which allow remote code execution and disclosure of sensitive information. Affected versions are TRO600 up to 9.2.1.6 and 9.1.1.0, plus 9.2.2.1 and 9.1.2.0. The page gives no per-CVE detail or CVSS scores, only general ICS hardening advice. Released 27 October 2026.
cisa.govadvisoryAdded 29 Oct 2026, published 28 Oct 2026  Social Engineering: Modem-Based Persistence in a Compromised Environment
The article describes reflashing a Huawei E3372h-153 HiLink 4G USB modem so its embedded Linux OS runs an OpenVPN client over the mobile network, creating a covert, network-independent persistence channel after physical USB access. It walks through enabling debug mode, flashing firmware, disabling CD-ROM emulation, configuring DHCP and autorun scripts, and chaining a second L2VPN tunnel to bridge the attacker directly onto the victim's Ethernet segment for tools like Responder. Defense guidance focuses on restricting USB ports and disabling USB network adapters via policy.
 hackers-arise.comwriteupPublished and added 28 Oct 2026
 TLS Flaws Found in GoAhead Web Server Used in Hundreds of Millions of Devices
FoxIO disclosed three TLS flaws in the GoAhead embedded web server from EmbedThis, used on hundreds of millions of IoT, OT and network devices. CVE-2026-115881 (CVSS 9.1) leaves revoked client certificates accepted under mTLS with OpenSSL; CVE-2026-115884 (7.4) bypasses chain-length limits with LibreSSL; a third Mbed TLS bug (5.9, no CVE) weakens TLS 1.2 DHE. GoAhead 6.1.1 fixes the OpenSSL and Mbed TLS issues, and FoxIO released PoC code and fingerprints.
securityweek.comarticlePublished and added 28 Oct 2026 Christiaan Stoudt (@cstoudt) on X
Thread on CVE-2026-97631, a critical (9.5) flaw in TianoCore EDK II UEFI firmware, found by Alex Matrosov and Dan Holmes-Mitra. It is exploitable only while a machine is PXE network booting and the attacker sends an oversized ICMP error from the same network. Code execution also needs the exact firmware build, and Secure Boot does not help. The fix landed in EDK II main on 15 October but is not in a stable release. No known exploitation, and not in CISA KEV.
 x.comthreadAdded 30 Oct 2026, published 28 Oct 2026
 Long-Hidden Flaws Patched in EPICS Research Facility Control Software
Four vulnerabilities in EPICS Base 7.0.10 and earlier, the control-system toolkit used at ITER and the Advanced Photon Source, were disclosed by CISA. CVE-2026-114595 (CVSS 9.8) is an integer overflow that could allow remote code execution, though only an out-of-bounds heap write and crash were demonstrated. All flaws sit in Channel Access and pvAccess handling (TCP 5064 and 5075), need no authentication, and are fixed in 7.0.11.
securityweek.comarticlePublished and added 28 Oct 2026 Bitcoin Wallet Maker Keystone Pulls Devices as Stolen Key Opens Door to Fakes
Keystone, a Bitcoin hardware wallet maker, will destroy 18,835 unsold devices and has halted shipping after an attacker obtained the permanent WebAuth factory key used to verify genuine hardware, detected October 20, 2026. The key could let counterfeit wallets pass authentication. The breach also exposed 25,964 Shopify buyer records (2024 to 2026) that should have been erased under a 180-day policy; recovery phrases and private keys were not involved.
decrypt.coarticlePublished and added 27 Oct 2026 Tractable, Not Truncated: Colored-Noise TRNG Security via Fractional Brownian Motion
This ePrint paper models oscillator-based TRNG phase noise, both white and flicker, as fractional Brownian motion. It proves a quasi-renewal property that gives closed-form worst-case min-entropy and sampling requirements, and extends spectral and Allan-variance analysis so noise parameters come from a single timing trace. FPGA and ASIC experiments show flicker noise accounts for over 99% of uncertainty at a 0.99 min-entropy target, allowing a bitrate two to three orders of magnitude higher.
 eprint.iacr.orgpaperAdded 28 Oct 2026, published 27 Oct 2026
- Towards Quantum Sensing for Side-Channel Analysis
Preprint on using nitrogen-vacancy (NV) center quantum sensing for electromagnetic side-channel analysis of ICs. The authors build an NV-based RF spectrometer with 1.1 GHz real-time bandwidth and adjustable center frequency, which reads the spectrum in the time domain without Fourier transforms or frequency sweeps. They use it on RSA decryption emanations and for leakage detection on a software Number Theoretic Transform running on a Cortex-M4 microcontroller.
eprint.iacr.orgpaperAdded 28 Oct 2026, published 27 Oct 2026  Crypto wallet maker Keystone to destroy almost 19,000 devices after security breach
Keystone, a hardware wallet maker, will destroy 18,835 unsold devices after an attacker used a flaw in a third-party data monitoring tool to breach its website on 20 October 2026. The breach exposed 25,964 buyer records and a factory-set authenticity key that cannot be changed, so counterfeit wallets could pass checks. An automated deletion tool had failed unnoticed against the 180-day retention policy. The report also covers a Foundation breach with 23,000 phishing attempts.
 coindesk.comarticlePublished and added 27 Oct 2026
- Unshuffling Fisher-Yates: Practical Recovery of Length-128 Permutations and Application to ML-DSA
Paper (IACR ePrint 2026/2658) presenting a single-trace side-channel attack on a software Fisher-Yates shuffle of length 128, the butterfly count in one ML-DSA NTT layer. It removes rejection-sampling timing variation, extracts Hamming weight and identity leakage, and enumerates likely permutations with constraint programming. On a shuffled ML-DSA-44 NTT it recovers secret polynomial s1, fully or up to a few coefficients.
eprint.iacr.orgpaperAdded 28 Oct 2026, published 27 Oct 2026 - Poly2MsgLeaks: Certified Key Recovery from Polynomial-to-Message Leakage
Poly2MsgLeaks is a profiled chosen-ciphertext power-analysis attack on the SMAUG-T (TiMER parameter set) post-quantum KEM that recovers the full 512-coefficient PKE secret from six traces on an STM32F415. It recovers 999 of 1,000 unseen secrets and proves an incorrect key is released with probability at most 2^-2095.6. Single-write message assembly and a two-share masked P2M resisted the evaluated six-execution attack.
eprint.iacr.orgpaperAdded 28 Oct 2026, published 27 Oct 2026 - Falcon Key Recovery from Joint Sampler Leakages
Falcon Key Recovery from Joint Sampler Leakages is an ePrint paper presenting a power side-channel attack on Falcon and FN-DSA that fuses three SamplerZ leakages (exponent class of the center, sign bit, proposal magnitude). It turns them into slab and halfspace constraints solved by softplus interval regression, with no LLL or BKZ. On PQClean Falcon-512 (ARM Cortex-M4) it recovered all 50 keys with at most 34 signatures; on c-fn-dsa it recovered 38 of 50 keys within 200 signatures.
eprint.iacr.orgpaperAdded 28 Oct 2026, published 27 Oct 2026 - When Algebraic Structure Meets Too Many Hints
"When Algebraic Structure Meets Too Many Hints" is an ePrint paper (2026/2654) arguing that DDGR hint classes and too-many-hints thresholds are not standalone side-channel security metrics. In synthetic Kyber-512 experiments, NTT-domain residues recover the full secret with about half the hints the uniform mod-q bound predicts. Finite-precision FFT samples need 25% to 55% of the budget for uniform perfect hints. No new attack optimizations are proposed.
eprint.iacr.orgpaperPublished and added 27 Oct 2026 - Analyzing Compiler-induced Constant-time Violations with Compiler at Scale
CTGREP is a compiler-based framework that applies differential analysis across the whole Clang/LLVM compilation chain to find where, how and under which configurations compiler optimizations break constant-time cryptographic code. Applied to seven libraries, three Clang versions, six targets and thousands of configurations, it led to 48 cases fixed with developers. It also identified seven new problematic LLVM passes and bypassed existing compiler-flag mitigations.
eprint.iacr.orgpaperAdded 27 Oct 2026, published 26 Oct 2026  Keystone Breach Widens as Attacker Grabs Its Device Authentication Key
Keystone, a hardware wallet maker, disclosed on 26 October 2026 that the attacker behind its 20 October store breach also took the WebAuth device authentication key. The key is written at the factory and cannot be changed, so Keystone is scrapping 18,835 devices. The breach came through a third-party monitoring tool on its Shopify site and exposed 25,964 buyer records. Old-key units received after 20 October may be counterfeit.
 bankless.comarticlePublished and added 26 Oct 2026
 Keystone to destroy almost 19,000 wallets after device key leak
Keystone confirmed a breach of Shopify customer records (about 26,000 plus 13,000 incomplete orders), in which the attacker also took the WebAuth key used to verify device authenticity. It will destroy almost 19,000 unshipped wallets and issue a new key. Foundation Passport phishing emails (over 20,000) came from compromised Cloudflare API keys, and old WooCommerce database copies kept personal data past the stated 60-day deletion.
protos.comarticlePublished and added 26 Oct 2026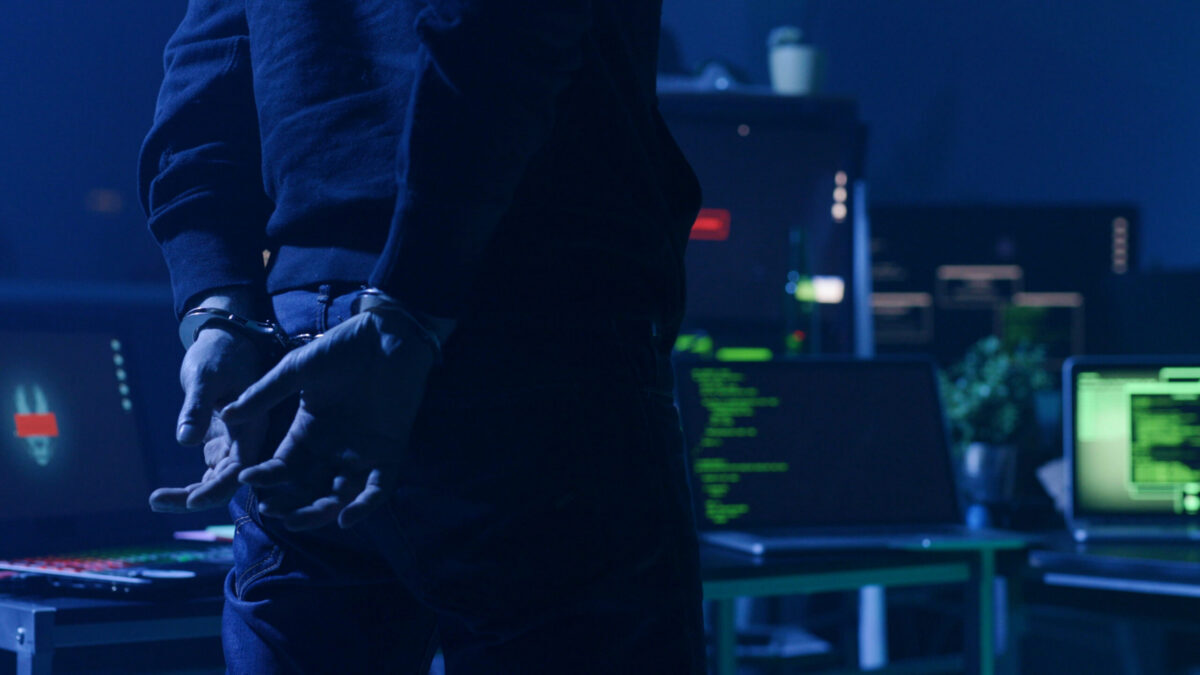 Dutch Police Arrest Two Over NFC Relay Attacks That Drained $400,000+ From Bank Accounts
Dutch police arrested two men, aged 23 and 25 from Vaassen and Ede, on October 6 over a bank helpdesk fraud that took over €380,000 from 170 victims. Callers played AI-generated bank audio, then a fake bank employee had victims install an app and tap their card to the phone. The app read the NFC chip data and relayed it to an accomplice at an ATM. Police seized the servers.
securityweek.comarticlePublished and added 26 Oct 2026- Non-profiled Single-Trace ML-DSA Secret Key Recovery by Horizontal Distribution Analysis
Non-profiled single-trace side-channel attack on ML-DSA-65 (Dilithium) running on ARM Cortex-M4, by Linus Backlund and Elena Dubrova (KTH). It compares observed sample distributions with expected Hamming weight leakage using a Gaussian mixture model, and stacks partitioned trace segments for multiple observations. Information-set decoding corrects misclassifications; with a 2^70 enumeration budget, the full secret key is recovered from one trace in 99% of attacks, using secret key unpacking as the attack point.
eprint.iacr.orgpaperPublished and added 26 Oct 2026 - Techjunkie Aman (@Techjunkie_Aman) on X
ns2jb is a software-only jailbreak for the Nintendo Switch 2 running firmware 23.0.1, announced in a post on X. It runs arbitrary native code, allows save dumping, reverse engineering and game modding, and reaches most peripherals via MMIO. It is tethered (rerun after reboot) and gives no CFW or full kernel control. The post says Mario Kart World has been modded with custom characters. It gives no technical detail on the exploit chain.
x.comthreadAdded 24 Oct 2026, published 22 Oct 2026 - Anti-Forensics: Building a Phantomdrive
Phantomdrive is an open source USB drive built on the WCH CH569 chip that appears as a plain 8GB disk and hides the rest of an SD card behind AES-256 encryption. The hidden partition unlocks when the user saves "password:" in a text file; the firmware catches it in raw WRITE10 traffic and zeroes the buffer. Key derivation uses a per-device salt and 100,000 SHA-256 rounds, and the post compares AES-ECB, CTR and XTS speeds.
hackers-arise.comarticlePublished and added 22 Oct 2026 - The Good, the Bad, and the Noisy: A Systematic Analysis of Ring-Oscillator-Based Noise Generators
This IACR ePrint paper (2026/2597) systematically compares ring-oscillator-based additive noise generators, a hiding countermeasure against side-channel attacks. Experiments show many existing designs ignore output amplification and the risk of the noise being filtered out, so they lower signal-to-noise ratio too little. The authors give a guideline on inverter chain length, output amplification and frequency randomization, and build a tailored generator for an AES implementation that outperforms prior designs.
eprint.iacr.orgpaperAdded 24 Oct 2026, published 22 Oct 2026  Your MCU likely escaped the eMudhra intermediate CA compromise
Analysis of the eMudhra intermediate CA compromise disclosed 20 October 2026, in which eight intermediate CA private keys were weak P-384 keys (top 376 bits zero, one key equal to 4) and publicly accessible. It explains web PKI chains and why browsers enforcing Certificate Transparency were not exposed. It argues MCU firmware that bundles only the single root it needs, as in Zephyr's HTTP GET sample, is likely safe unless it trusts an eMudhra or Sectigo cross-signing root.
 danielmangum.comarticleAdded 22 Oct 2026, published 21 Oct 2026
- Sotto Maschera: Masking the Sota-Voce Fixed-Weight Vector Sampling
Sotto Maschera is a masked implementation of the Sota Voce sparse fixed-weight vector sampler (Sota support sampler and MWSupport conversion) for embedded devices, protecting against power side-channel attacks. It bitslices sorting, merging and compaction and masks only in the Boolean domain, avoiding slow conversions. TVLA evaluations show no leakage, and HQC runs up to 45x faster than previous masked work.
eprint.iacr.orgpaperAdded 24 Oct 2026, published 21 Oct 2026 - Cryptocurrency: Security Analysis of Hardware Crypto Wallets
Hackers Arise article on the October 2026 attack in which Ledger Nano X devices sold by the reseller CryptoBilis carried a hidden circuit board that taps the SPI bus to the screen, rebuilds the 24-word recovery phrase and sends it out over LTE. Losses are estimated at $86 million to over $100 million. The device still passes Genuine Check. It lists safe purchasing, checking and recovery steps, plus BIP-39 passphrase and multisig advice.
hackers-arise.comarticlePublished and added 21 Oct 2026

Showing 30 of 156
Show more