Skip to content

🕵️ OSINT67

What you seeeverything
wired.comarticle

Leak Exposes 41,000 Homeland Security Workers–Including Undercover ICE Agents

Icepick is a leaked archive of records on more than 41,000 Department of Homeland Security employees and contractors, published by Distributed Denial of Secrets in 2026 and said to come from DHS's Okta login system. WIRED's analysis covers CBP, ICE, HSI, USCIS and CISA staff, plus over 55,000 permission groups that reference undercover programs, Palantir Falcon, PenLink, Signal and Mobile Fortify. Okta says it has no evidence of compromise.

OktaPalantirPenLink+3
IcepickDistributed Denial of SecretsDepartment of Peace+10

Threat Intel, OSINT, Identity & Access· Added 29 Oct 2026, published 28 Oct 2026
proton.metool

Proton Flock Camera Map

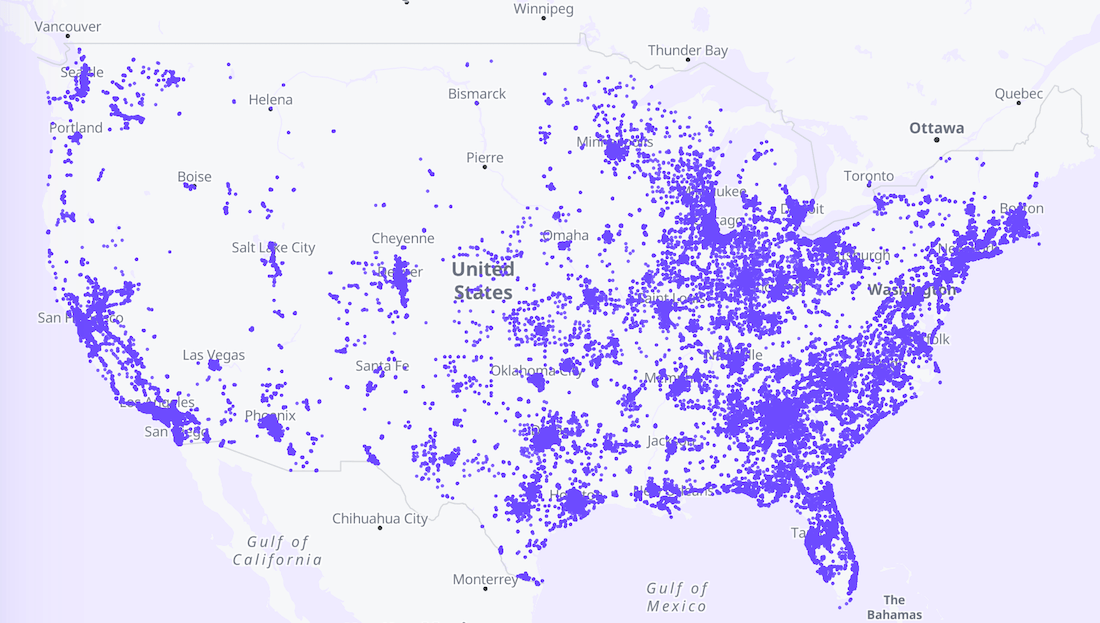
Proton Flock Camera Map is a ZIP-code search map of Flock license plate reader locations. Its data comes from researcher Joshua Michael, who found in November 2025 that Flock's servers exposed an access token to anyone without login, and published his map in December. His inventory lists over 170,000 cameras and 130,000 other devices, about 40% above Flock's cited 120,000 cameras. The page also covers what Flock records and cites a Washington Post review of officer misuse.

Flock Safety
Joshua MichaelGarrett LangleyVehicle Fingerprint+1

OSINT· Added 26 Oct 2026, published 25 Oct 2026

cyberinsider.comarticle

Proton hosts map of 300k Flock devices amid legal threats

Proton is hosting a public map of more than 300,000 Flock Safety surveillance devices (about 170,000 cameras and 130,000 other devices), built from an inventory researcher Joshua Michael obtained in November 2025 via an access token that could be fetched without login. Flock closed the path, later found anomalous token activity but no customer data impact, and sent Michael a cease-and-desist letter. The map is a December 2025 snapshot.

Flock SafetyProton
Joshua MichaelDeFlock404 Media+3

AppSec, OSINT· Added 25 Oct 2026, published 23 Oct 2026

blog.virustotal.comarticle

Sizing the PHP exposure window for CVE-2026-109618 and CVE-2026-109619 with VirusTotal

VirusTotal sizes the internet-facing PHP footprint around CVE-2026-109618 and CVE-2026-109619 (CVSS v4.0 9.2, session.upload_progress) using Internet Scanning. About 5.1M IPs run PHP, roughly 4 in 5 hide their version, and ~758K disclose an end-of-life branch. It gives queries that use the SSH banner to match leaked LiteSpeed lsphp 8.2.34 builds, plus mitigations.

PHPVirusTotalCloudflare+3
CVE-2026-109618CVE-2026-109619NOX Stealer+3

Blue Team & Detection, OSINT, AppSec· Added 22 Oct 2026

github.comrepo

Show HN: VoidAccess – open-source dark web OSINT, from query to a graph

VoidAccess is a self-hosted, MIT-licensed dark web OSINT platform that runs a 13-step pipeline from a research query to a relationship graph. It collects from Tor indexes, paste sites, code forges, security feeds and .onion seeds, applies content-safety filters, and exports STIX 2.1, MISP, Sigma, YARA, Snort, Suricata, CSV and JSON. It runs as a CLI with SQLite or as a Docker Compose stack with PostgreSQL, FastAPI and Next.js.

TorPythonDocker+3
LockBitSTIX 2.1MISP+6

OSINT, Threat Intel· Added 21 Oct 2026, published 20 Oct 2026

x.comrepo

Abhinav Singwal (@yogsec) on X

GetSubDomains is an open-source tool by yogsec that enumerates subdomains by querying crt.sh certificate transparency logs. It is aimed at the reconnaissance step of penetration tests and bug bounty work. The source is a short tweet pointing to a GitHub repository, so usage details and options are not given.

crt.shGitHub
GetSubDomainsyogseccertificate transparency

OSINT, Offensive Security· Added 21 Oct 2026, published 19 Oct 2026

hackers-arise.comarticle

Open-Source Intelligence (OSINT): Turn One Username into a Full Digital Dossier with Maigret

Hands-on walkthrough of Maigret, an open-source Python tool that checks a username against 3,000+ sites (top 500 by default) and builds a profile dossier by parsing public profile pages and recursively searching newly found usernames. Covers installation from GitHub, single-site and tag filtering, username permutation, HTML/PDF/CSV/JSON reports, graph output, and an optional LLM summary via OpenRouter. Positioned as a more thorough successor to Sherlock for username reconnaissance.

MaigretPythonKali Linux+2
Sherlock

OSINT, Learning· Published and added 16 Oct 2026

github.comrepo

bilawalsidhu/gods-eye-view

God's Eye View is an open-source, vanilla-JavaScript CesiumJS and Vite client that puts live aircraft, ships, satellites (SGP4), earthquakes, fires, public CCTV and mapped ALPR cameras on one photorealistic 3D globe. It adds cockpit tracking, FLIR/NVG sensor shaders and a voice agent built on the OpenAI Realtime API. It works without API keys, and the docs cover server-side key brokering with SSRF protection, localhost binding and a SECURITY.md threat model. For OSINT/GEOINT practitioners it is a hackable base for fusing public signals, with an explicit rule against person-tracking features.

CesiumJSOpenAIPinokio+3
SGP4ADS-BAIS+4

OSINT· Added 11 Oct 2026

x.comrepo

Dark Web Informer (@DarkWebInformer) on X

Infoooze is an open-source command-line OSINT reconnaissance toolkit (github.com/devxprite/infoooze) that consolidates common footprinting tasks into one CLI: username enumeration across platforms, email discovery, subdomain enumeration, port scanning, WHOIS/DNS lookups, IP/HTTP header analysis, EXIF metadata extraction, GitHub recon, and URL scanning/expansion. It automatically saves results, making it a lightweight all-in-one alternative to running several separate recon tools.

GitHub

OSINT· Published and added 8 Oct 2026

openai.comarticle

Disrupting AI-enabled “false front” operations

OpenAI reports banning ChatGPT accounts tied to two covert influence operations using "false front" entities. The Russian "Dark Clark" operation ran a think tank (Social Research Center) staffed by unwitting Latin Americans, planted fake emails, audio and documents targeting Ukraine and Argentine, Bolivian and Ecuadorian leaders, and was rated Breakout Scale Category 5. The Iranian "Bogus Bylines" operation used seven fake journalist personas to place nearly 100 articles in online outlets (Category 4) and generated batches of social media comments (Category 2), while using inflated impact metrics in internal reports.

ChatGPTOpenAIVPN+2
Dark ClarkBogus BylinesSocial Research Center+12

Threat Intel, AI Security, OSINT· Published and added 8 Oct 2026

protos.comarticle

Inside EQIBank’s $84M seizure

Protos investigative article unpacking the DOJ's $84M civil forfeiture against Capstone Limited, a payment processor used by Dominica-based EQIBank (which handles Tether reserves), for misrepresenting itself to Wells Fargo, JPMorgan Chase and Citibank as a software firm rather than a money services business. The piece uses OSINT techniques — corporate registry tracing, shared-hosting IP correlation, DNS lookups, and court filing cross-referencing — to map operator Kotaro Shimogori's decade-long history running shell payment processors (ComCopious, iCanPay, AuthPay, Pan Digital Network) for high-risk clients including gambling sites and, per the forfeiture complaint, impersonation-fraud scam proceeds funneled through Chase accounts. It also details EQIBank's EQIFi/EQX DeFi token, and links Marlin Capital Partners and Deltec Bank figures to Tether's banking history, drawing parallels to the earlier Crypto Capital Corp seizure.

TetherBitcoin
EQIBankCapstone LimitedKotaro Shimogori+22

Threat Intel, OSINT· Added 8 Oct 2026, published 7 Oct 2026

247wallst.comarticle

Chinese network laundered $1B+ for North Korea's Lazarus Group — ZachXBT

Blockchain investigator ZachXBT published a 12-part thread detailing how he spent months posing as a client of a Chinese money-laundering network to prove it laundered over $1 billion for North Korea's Lazarus Group, including a large share of the ~$1.5 billion Bybit hack (FBI codename TraderTraitor). He cross-referenced the operators' private messages with on-chain data — including a wallet receiving fees from Bybit-hack-linked addresses and THORChain bridge transfer timing/amounts matching what operators disclosed — turning chat screenshots into verifiable blockchain evidence. The laundering network converted BTC into ETH, Solana and Tron, used THORChain for cross-chain hops, and parked funds in low-volume Uniswap pools; the investigation led Tether to freeze 442,000 USDT, part of over $75 million ZachXBT claims to have gotten frozen from North Korea-linked hacks since 2022.

EthereumBitcoinSolana+3
ZachXBTLazarus GroupBybit+2

Threat Intel, Blockchain, OSINT· Published and added 6 Oct 2026

mailaccess.protool

Show HN: MailAccess – the true Email OSINT framework

MailAccess is an open-source email OSINT framework (pip install mailaccess, MIT licensed, 1.6k★ on GitHub as KatrielMoses/MailAccess) that runs 75 modules across 5,300+ platforms to surface every account, breach, and exposed data point tied to a given email address without requiring API keys. Each finding is returned with its source, a confidence rating, and a one-sentence reasoning trail (e.g. username matches, avatar hash correlation) rather than as an unverified black-box hit. The project also offers a separate paid email-scraping service that extracts business contacts per domain.

PythonGitHubpip

OSINT· Published and added 6 Oct 2026

thedefiant.ioarticle

ZachXBT Says He Fronted $349,700 to Infiltrate Alleged Laundering Ring

Pseudonymous on-chain investigator ZachXBT says he personally fronted $349,700 to infiltrate an alleged crypto money-laundering ring as an undercover source. He ties that operation to the freezing of 442,000 USDT after identifying a laundering cluster linked to the Bybit hack and valued at more than $12 million.

Tether
ZachXBTBybit

Threat Intel, OSINT, Blockchain· Published and added 5 Oct 2026

decrypt.coarticle

Crypto Sleuth ZachXBT Fronted $350K to Pose as a Client of Lazarus' Chinese Launderers

Decrypt reports on ZachXBT's account of infiltrating a Chinese money-laundering syndicate working for North Korea's Lazarus Group, by posing as a client ("fronted" $349.7K USDC) to a contact named "Jimmy Green" to gather intelligence on how Bybit's $1.5B hack proceeds were being laundered. The piece details the on-chain corroboration methods used (matching Telegram screenshots to Thorchain swap timing, wallet clustering across BTC/ETH/SOL/Tron) that exposed a $12M+ cluster of Bybit exploit funds, led to a 442K USDT Tether freeze, and separately traced $3M in fraud proceeds to Huione Guarantee, a Cambodian marketplace later targeted by FinCEN and shut down by Telegram.

EthereumSolanaTron+3
ZachXBTLazarus GroupDPRK+12

Threat Intel, OSINT, Blockchain· Published and added 5 Oct 2026

protos.comarticle

ZachXBT poses as money launderer to infiltrate Lazarus network

Crypto investigator ZachXBT details how he posed as a money-laundering client (contacting a launderer known as "Jimmy Green" over Telegram/Discord) to infiltrate a Chinese organized-crime network laundering funds for North Korea's Lazarus Group. He fronted roughly 350,000 dollars across transactions, collected addresses and bridging methods via THORSwap, and used the intel to link the launderer to the 1.5 billion dollar Bybit hack, the 100 million dollar Poloniex hack, and sanctioned conglomerate Huione Guarantee; findings also contributed to freezing funds tied to the Bybit theft.

Telegram
ZachXBTLazarus GroupBitget+5

Threat Intel, OSINT, Blockchain· Published and added 5 Oct 2026

thedefiant.ioarticle

ZachXBT Posed as a Client to Infiltrate Chinese Syndicate Laundering Bybit Hack Funds

Crypto investigator ZachXBT describes posing undercover as a client to infiltrate a Chinese OTC laundering syndicate handling stolen Bybit hack funds linked to North Korea (DPRK). He fronted 349,700 USDC, paid a 5% fee per order, and had the broker tell him in advance where the stolen funds would move next, surfacing operational detail on how DPRK-linked actors cash out stolen crypto through OTC desks.

Bybit
ZachXBTDPRK

Threat Intel, OSINT, Blockchain· Published and added 5 Oct 2026

x.comtool

The OSINT Newsletter (@osintnewsletter) on X

The OSINT Tools Map, built by @cyb_detective, is an interactive world map letting investigators click a country to find relevant local OSINT resources such as phonebooks, business registers, cadastral maps, and court records. The same tweet announces the companion "OSINT Tools Library" at tools.osintnewsletter.com, a curated, investigator-first directory of tools used in real cases that is actively soliciting community additions.

OSINT· Added 5 Oct 2026, published 4 Oct 2026

x.comrepo

the_OSINT_rack (@the_OSINT_rack) on X

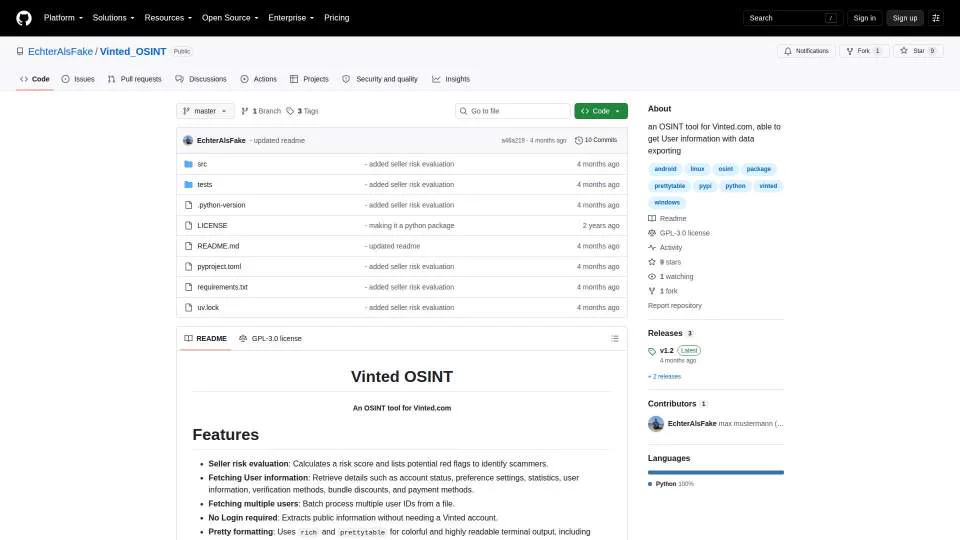
Vinted_OSINT is a GitHub tool by EchterAlsFake that performs open-source intelligence gathering against Vinted.com user profiles, pulling seller/buyer account information and computing a risk score to flag accounts likely run by scammers. It's aimed at buyers wanting to vet sellers before transacting on the second-hand marketplace.

EchterAlsFakeVinted

OSINT· Published and added 4 Oct 2026

x.comtool

texas actual (@texasactualUA) on X

A tweet highlights osinteuropetracker.com, an OSINT tracker built to map known and suspected Russian sabotage operations across the European Union. The tool is shared as a practical way for analysts to monitor and visualize ongoing hybrid-threat incidents attributed to Russia in EU countries.

OSINT Europe Tracker
Russia

OSINT, Threat Intel· Added 3 Oct 2026, published 1 Oct 2026

x.comrepo

Andrea (Drego) Draghetti 👨🏻‍💻 🎣 (@AndreaDraghetti) on X

Tosint v1.0.0 is an open-source Telegram OSINT tool for analyzing bots and chats, exporting message history and media. The new release adds richer JSONL metadata output, optional SHA-256 hashing of exported media, bot/user authentication support, and an automatic fallback from MTProto-based history retrieval to ID-scan mode when dealing with restricted chats.

TelegramTosint
Andrea Draghetti

OSINT· Added 2 Oct 2026, published 30 Sep 2026

github.comrepo

Outrider Recon

Outrider Recon is an open-source, Claude-native multi-agent OSINT and external attack-surface recon platform for authorized engagements, covering web/API, identity/SSO, cloud, secrets, and people/breach intelligence. It deliberately stops short of exploitation: active enumeration is approval-gated and intrusive validation is a human hand-off, with deterministic Python controls enforcing scope, evidence integrity, workflow state, and finding promotion around Claude skills and optional MCP-based enrichment. Output is ranked, evidence-backed finding cards (confidence/severity/handoff recommendations) meant to feed proxy-assisted testing or pen-testing rather than raw scanner dumps.

ClaudeClaude CodeModel Context Protocol+2
elementalsouls/Claude-OSINTSnailSploit/offensive-checklist

OSINT, Offensive Security, AI Security· Added 22 Sep 2026, published 19 Sep 2026

github.comrepo

MassPIIFinder v2

MassPIIFinder v2 is a Python recon tool that automates crawling a target's in-scope JavaScript (multi-hop HTML crawl, dynamic imports, chunk manifests, sourcemaps, plus optional passive CT-log subdomain discovery) and mines it for API keys, tokens, credentials, internal endpoints, and PII using ~90 named patterns plus a high-entropy freeform heuristic. Findings are validated offline (Luhn checks, JWT decode, AWS key-shape) and via scope-checked, rate-limited reachability probes, then triaged by severity and exported as JSON/HTML/SARIF/Markdown/CSV. It enforces authorization with a required --confirm-authorized flag and a ScopeGuard that blocks any out-of-scope requests, and explicitly avoids testing leaked keys against third-party providers or exploiting findings.

PythonFlaskSQLite+1

OSINT, AppSec· Added 22 Sep 2026, published 15 Sep 2026

chainalysis.comarticle

Tracing Crypto in a Narcotics Investigation: FBI Charges Alleged Opioid Distributors

Chainalysis details how blockchain analytics (its Reactor tool) helped the FBI trace Bitcoin proceeds from the darknet vendor account "BarbaraWhite" — which sold nitazene-laced counterfeit pills on Nemesis, Bohemia and Abacus — through a wallet cluster to a China-based chemical supplier and, ultimately, to a mobile payment account tied to defendant Stanislav Chernyshov. The case illustrates a concrete investigative pipeline: combining on-chain clustering with marketplace data, postal records, and off-chain identifiers to deanonymize a pseudonymous crypto-paid drug operation linked to overdose deaths.

BitcoinChainalysis Reactor
BarbaraWhiteVladislav ChernyshovStanislav Chernyshov+4

OSINT· Added 30 Sep 2026, published 8 Sep 2026

github.comrepo

eldarshiraliyev/BugScanner

BugScanner is an asyncio/httpx Python framework for recon and automated web vulnerability scanning, with a React and FastAPI dashboard. It covers subdomain enumeration (crt.sh, DNS brute force), TCP port scanning, fingerprinting, and modules for XSS, SQLi, CORS, SSRF, open redirect, JWT, IDOR and business logic, plus a Nuclei wrapper. A 5-rule false-positive filter with SPA detection, adaptive rate limiting, WAF detection and SARIF export are included.

PythonNucleiFastAPI+3
IDORSSRFCWE-89

AppSec, Offensive Security, OSINT· Added 20 Oct 2026, published 5 Sep 2026

chainalysis.comarticle

FBI Seizes $560K in Crypto From Hamas Fundraising Network

Chainalysis details five related U.S. law enforcement actions (March 2025–August 2026) that seized over $560,000 in cryptocurrency tied to Hamas and al-Qassam Brigades fundraising, plus the group's donation website domains and servers. The piece walks through the forensic methodology — using Chainalysis Reactor to cluster addresses via a shared gas-funding wallet, trace funds through consolidation wallets and a Lebanon-based OTC broker, and follow Hamas's later shift to cross-chain bridging and single-use donation wallets — showing how earlier on-chain findings compounded into a broader mapping of the group's financing network over time.

Chainalysis Reactor
Hamasal-Qassam BrigadesFBI+1

Threat Intel, OSINT, Blockchain· Added 30 Sep 2026, published 3 Sep 2026

github.comrepo

subScraper

subScraper is a self-contained, single-file (main.py) Python orchestrator that chains subdomain enumeration tools (Amass, Subfinder, Assetfinder, Findomain, Sublist3r) into httpx probing, screenshot capture, ffuf fuzzing, nuclei, and nikto scans, all driven from a live web UI with resumable job state, worker concurrency controls, and Docker packaging. It ships 34 custom nuclei templates for CVEs lacking official coverage and exposes a scoped, API-key-authenticated "bug bounty agent API" for programmatic recon and attack-surface queries against a target's scope.

NucleihttpxDocker+3
AssetfinderFindomainSublist3r+2

OSINT, Offensive Security· Published and added 27 Aug 2026

huntress.comwriteup

Insights into Suspected DPRK Workers

Huntress details investigations into five suspected DPRK (FAMOUS CHOLLIMA) remote workers who infiltrated partner organizations in IT, sales/marketing, and healthcare roles in 2026. The writeup covers detection methodology using Microsoft 365 Unified Audit Logs, Huntress ITDR, and analysis of infrastructure (Astrill VPN, IPRoyal Proxy, WorkTitans B.V. bulletproof hosting), plus forensic evidence of fraudulent identity documents (fake Chinese passports/ID cards with matching forged details) used during onboarding.

Microsoft 365SharePointExchange
Famous ChollimaAstrill VPNIPRoyal Proxy+2

Threat Intel, Identity & Access, OSINT· Added 3 Sep 2026, published 26 Aug 2026

github.comrepo

Ashmmmm/crockTail

crockTail is a passive OSINT tool that, given a domain, aggregates DNS records, IP/ASN ownership, TLS certificate details, WHOIS data, and crt.sh certificate-transparency history into a single report. It layers analysis on top of the raw data: plain-language warning/info observations (near-expiry or expired certs, recently registered domains, unusual reissuance, historical subdomains from CT logs), multi-resolver (Google vs Cloudflare) DNS cross-verification to flag possible tampering, and a 0-100 confidence score per scan based on module success and cross-check agreement. It supports batch domain queries and query logging, and is explicitly limited to passive lookups and a standard TLS handshake, no port scanning or active probing.

JavaMavenVue+1

OSINT· Added 30 Sep 2026, published 25 Aug 2026

submap.nettool

Submap

SubMap is an enterprise-facing subdomain discovery and attack-surface-mapping SaaS that aggregates multiple reconnaissance data sources, streams results live via SSE, and exports to TXT/CSV/JSON for integration into a security workflow. It also runs 49 service fingerprints to detect subdomain-takeover conditions (dangling CNAMEs pointing at AWS, Azure, GitHub, Heroku, etc.) and layers in CVE monitors/alerting for tracked assets. The public page gates full scan output behind account creation, showing only the first 110 results in the free preview.

AWSAzureGitHub+1

OSINT· Added 3 Sep 2026, published 25 Aug 2026

Showing 30 of 67

Show more