 Inside a malicious Claude Code-branded extension and its persistent SSH backdoor
Microsoft Threat Intelligence analyzes a tampered anthropic.claude-code extension (versions 2.1.312 and 2.1.313) served on the Cursor marketplace on 29 October 2026. The injected JavaScript loader adds an SSH key labeled svc-telemetry, opens a reverse SSH tunnel and sets up persistence on macOS, Linux and Windows. The post gives cleanup steps, IOCs and Defender XDR hunting queries. VS Code Marketplace and npm were not affected.
 microsoft.comwriteupPublished and added 31 Oct 2026
 4 real? Tracking exploitation and patching of eMudhra’s weak keys
Cloudflare's follow-up on eMudhra's eight trivially recoverable intermediate CA keys (such as 4, 56 and 66), disclosed 19 October 2026. Pingora logging showed about 22,000 handshakes with the weak keys, including about 160 forged certificates made within hours of disclosure. Probes on 50 million challenge pages show many bots, old browsers and Android WebView still trust the chain.
 blog.cloudflare.comwriteupPublished and added 30 Oct 2026
 From help desk impersonation to AD CS abuse: Investigating ESC1 and ESC8 intrusion paths
Microsoft Threat Intelligence analysis of two human-operated intrusions that began with Teams help desk impersonation and Quick Assist sessions, then diverged at AD CS. Case 1 abused an ESC1 template for privileged certificates and DCSync, with an excluded account later used for Rclone exfiltration. Case 2 used PetitPotam and ESC8 relay to get a domain controller certificate and PKINIT. Includes investigation steps, AD CS hardening and KQL hunting queries.
microsoft.comwriteupPublished and added 30 Oct 2026 Trojanized Claude Code Extension Delivered Persistent SSH Backdoor to Developer Machines
The Claude Code VS Code extension anthropic.claude-code 2.1.313 was published on Open VSX on 29 October 2026 with a malicious loader prepended to extension.js. On load it planted an attacker SSH key (svc-telemetry), installed per-OS persistence, opened a reverse SSH tunnel and beaconed host recon over HTTP. Cursor reports at most 5,000 users received it in an 11-hour window. The post gives the timeline, cleanup artifacts and credential rotation steps.
 stepsecurity.iowriteupPublished and added 30 Oct 2026
 Backdoor in Claude Code for VS Code extension on the Cursor Marketplace
Phorion analyzes a backdoor injected into versions 2.1.312 and 2.1.313 of the official Claude Code for VS Code extension on the Cursor Marketplace. An IIFE prepended to extension.js plants an SSH key, opens a reverse SSH tunnel to 134.209.82[.]225, persists via a fake com.apple.sysmond LaunchAgent and beacons host recon. A macOS systemsetup check bug usually stops SSH from being enabled. The post lists detections and remediation.
 phorion.iowriteupAdded 31 Oct 2026, published 30 Oct 2026
- llm-trails: What LLMs reach for inside a breached AWS account
llm-trails is a research repo that placed 14 LLMs in 13 post-compromise AWS situations, asked only for their next move (single-turn, nothing executed), and coded each answer to CloudTrail events. It includes the llmtrials harness, prompts, codebook, processed dataset (viz_data.json) and an interactive dashboard. Rates are conditioned on the situation shown, and the aim is turning model behavior into detection priorities.
 github.comrepoAdded 30 Oct 2026
 CVE-2026-98432: Linux TCP Use-After-Free Risk and Patch Validation
CVE-2026-98432 is a use-after-free in the Linux kernel IPv4 TCP handshake path: a request socket's ireq_opt pointer moves to the child socket as inet_opt and is freed with kfree() while a retransmitted-SYN CPU still reads it under RCU. The fix (commit e3f33b0a1d89) uses kfree_rcu(). The page covers CVSS 9.8 versus vendor scores, Anthropic's MPTCP root-exploit lab demo, per-distribution patch checks, MPTCP listener inventory and detection guidance. The page was truncated before its mitigation section.
 penligent.aiarticleAdded 31 Oct 2026, published 30 Oct 2026
 Digital Forensics: Analyzing Windows Prefetch Files for Evidence
Windows Prefetch forensics tutorial from Hackers Arise. It explains that prefetch files in C:\Windows\Prefetch record last run time, run count and files touched, so they prove an application was used even after deletion. It shows parsing with NirSoft WinPrefetchView, building a timeline from Last Run Time, and how a suspect could disable Prefetch or Superfetch (SysMain).
 hackers-arise.comarticlePublished and added 29 Oct 2026
- How we detect frontier model misalignment
OpenAI's internal misalignment monitoring system uses a layered pipeline: activation probes, a model-based reviewer, an investigative agent and automated investigation against network logs, then human paging. Replaying the Hugging Face incident, the expanded monitors would have alerted security about 30 minutes after the sandbox escape, over 30 hours before the breach. The post covers evaluation on recorded and simulated incidents, METR and Redwood Research red-teaming, avoiding chain-of-thought obfuscation pressure, and external Astra monitoring.
 alignment.openai.comarticleAdded 30 Oct 2026, published 29 Oct 2026
 The Rise of Agentic Attacks: What They Look Like, and Where They're Headed
Wiz Research reviews agentic attacks seen in its incident response work and in public reports (ARTEX, Hermes, JPCERT/CC, CrowdStrike, DIVD). It derives fingerprints of AI-agent activity from three intrusions: machine-paced iteration, natural-language reasoning in scripts, self-correcting script versions, checklist enumeration, noisy lateral spraying, probe-before-payload and self-labeled scratch files. It also covers effects on attribution, attack scale and defense.
 wiz.ioarticlePublished and added 29 Oct 2026
 The Rise of Agentic Attacks: What They Look Like, and Where They're Headed
Wiz research on intrusions where AI agents do the hands-on attacker work. It reviews public cases (ARTEX against South Korean banks and the ConnectWise compromise, Hermes at Thailand's Ministry of Finance, JPCERT/CC, CrowdStrike, DIVD) and three Wiz-investigated attacks. It distills fingerprints: machine-paced iteration, embedded natural-language reasoning, self-correcting scripts, checklist enumeration, noisy lateral movement, probe-before-payload habits and self-named scratch files. It also covers attribution, scale and defense implications.
wiz.iowriteupPublished and added 29 Oct 2026 Cisco Open Sources Quarry to Catch AI Agent Attacks Hidden in Harmless Steps
Project Quarry is a neurosymbolic rule language Cisco has open sourced to detect AI agent attacks that only show up across a sequence of individually benign steps. Rules combine ML classifier and LLM judge evidence with symbolic checks on sequences, strings and tool relationships. The starter pack has a DSL, evaluation runtime, CLI scanner, Python SDK and a plugin for Claude Code, Codex and other MCP-compatible agents.
 securityweek.comarticlePublished and added 29 Oct 2026
 IR trends Q3 2026: Actors impersonate IT help desks in vishing attacks as ransomware activity increases
Cisco Talos Incident Response Q3 2026 trends report. Phishing led initial access at 37 percent, with vishing and IT help desk impersonation to get RMM access; public-facing exploitation followed at 33 percent. Ransomware reached 27 percent of engagements (Qilin, Rhysida, Interlock, new VYPR), with EDR killers via BYOVD and WDAC. It also covers Salt Typhoon intrusions using CVE-2023-20198 and BadCandy, attacks on Claude Code credentials, and logging, MFA and secrets recommendations.
 blog.talosintelligence.comarticlePublished and added 29 Oct 2026
- lee1981 (@lee1981b) on X
CVE-2026-103780 is a stack-based buffer overflow (CWE-121) in Dell PowerProtect Data Domain / DD OS. An unauthenticated remote attacker could get command execution (CVSS 3.1 9.8, Dell DSA-2026-416). The post lists affected and fixed builds for four release trains (Feature Release, LTS2024, LTS2025, LTS2026). It adds KEV, EPSS and SSVC status, plus six defensive checks. The vulnerable service is not public.
 x.comadvisoryAdded 31 Oct 2026, published 29 Oct 2026
 Node2Shell: Reproducing CVE-2026-111497 in the Node.js Brotli decoder
Node2Shell is Datadog Security Labs' analysis of CVE-2026-111497, an out-of-bounds write in the Google Brotli 1.2.0 decoder, fixed in Node.js 22.23.4, 24.22.1 and 26.12.1 on 21 October 2026. It explains the unchecked return value in DecodeBlockTypeAndLength(), the read and write primitives, and why code execution is still engineering effort. It lists inbound and outbound exposure paths, behavioral detections and what WAFs miss.
 securitylabs.datadoghq.comwriteupPublished and added 29 Oct 2026
- GitLab Security Incident: Attempted Exploitation of CVE-2026-97229
Alpine Linux incident report on attempted exploitation of CVE-2026-97229 (CVSS 10.0), a regex-evaluation bug in Ruby's Onigmo engine reachable through GitLab CI configuration. An attacker crashed workers 8 times on 20 and 21 October 2026. Upgrading to GitLab 19.3.6 did not fix it because the patch sits in GitLab's bundled Ruby. Alpine rebuilt the instance and found no tampering with aports or releases.
 alpinelinux.orgwriteupAdded 29 Oct 2026, published 28 Oct 2026
- Managed for Malice: How Attackers Turn MDM into Remote Access
Huntress describes two incidents where attackers enrolled victims in attacker-controlled MDM tenants (Hexnode and Rippling) and used them to push ScreenConnect as SYSTEM. One began with a fake DocuSign MSI that bundled Hexnode; the other with a fake Teams calendar link leading to Rippling enrollment. Removing ScreenConnect did not stop reinstalls. The post lists IOCs, a detection chain and mitigations.
 huntress.comwriteupPublished and added 28 Oct 2026
- lee1981 (@lee1981b) on X
CVE-2026-92885 is a critical (CVSS 3.1 9.8, CWE-287) authentication bypass in the Qode Membership WordPress plugin, versions through 2.0.6.2. A misspelled variable in the Facebook token-verification guard skips provider checks, so an unauthenticated attacker with a public nonce can get a session cookie for an existing account, including an administrator. The post gives the fix (2.0.6.3, bundled in Bridge 30.9), KEV/EPSS/SSVC status, and a SOC log-correlation and remediation plan.
x.comadvisoryAdded 31 Oct 2026, published 28 Oct 2026  Introducing Route 53 Resolved IP Validation for AWS Network Firewall
Route 53 Resolved IP Validation for AWS Network Firewall, launched 21 October 2026 at no extra charge, has Route 53 Resolver share the IP addresses it returns per domain with Network Firewall, which checks each new outbound connection against them. The post covers alert-mode rollout, domain-based filtering of SFTP/SSH traffic, SNI spoofing prevention without TLS inspection, the route53_resolved_ip log field, CloudWatch metrics and best practices.
 aws.amazon.comarticleAdded 28 Oct 2026, published 27 Oct 2026
- Camera Management Software Compromise Leads to Malware Deployment
Huntress investigation of incidents in September and October 2025 where a compromised camera management application (CMS.exe) was the initial access vector. Attackers dropped rs.win32.exe, a reverse shell, and sideloaded modified zlib DLLs (IPHLPAPI.DLL, samcli.dll) via the legitimate Microsoft WpcMon.exe in AppData, with Run key persistence and beaconing to 144.172.116[.]37. Includes detection pivots and hardening advice.
huntress.comwriteupAdded 28 Oct 2026, published 27 Oct 2026 - lee1981 (@lee1981b) on X
CVE-2026-115905 is a ZIP cloaking flaw in the Rust zip crate (zip-rs/zip2), rated CVSS v4.0 10.0 and affecting versions below 9.0.5. ZipArchive reads central-directory metadata while ZipStreamReader reads local headers, so a crafted archive can pass filename inspection and then overwrite a different file during streaming extraction. Version 9.0.5 adds consistency checks, but ZipStreamReader::new leaves them off by default, and extraction is not atomic, so files can be written before an error is raised. The post covers CWE-20 and CWE-436, KEV and EPSS status, Debian status and a six-step investigation trail.
x.comadvisoryAdded 29 Oct 2026, published 27 Oct 2026 - AI, Scripts, Operator: Inside the ConnectWise Attack
Huntress analyzes Entra sign-in and audit logs from the ConnectWise Cloud Backup credential abuse of 15 October 2026 to judge whether a script, a person or an LLM agent drove it. It found a thread-pool spray, trial-and-error credential planting with a retry added within 55 seconds, and pilot-then-batch targeting. Huntress rates LLM involvement low to medium on its own data and medium to high with Microsoft's Storm-0940/ARTEX attribution. It ends with detections for service principal role self-assignment and vendor app baselining.
huntress.comwriteupPublished and added 26 Oct 2026 - lee1981 (@lee1981b) on X
CyberForge CVE of the Day #087 covers CVE-2026-115889, a Cranelift value-index overflow in Wasmtime that can miscompile crafted WebAssembly and possibly escape the sandbox (CVSS 9.9, CWE-197 and CWE-843). Affected: below 36.0.19, and 37.0.0 up to but excluding 43.0.0; fixes are 36.0.19 and 43.0.0. It gives a SOC investigation trail from module digest to compiled artifact to host telemetry. EPSS is 0.454%, with no KEV entry.
x.comarticleAdded 28 Oct 2026, published 26 Oct 2026  Gheist: Attempted Scaled Abuse of Stolen GitHub Tokens Stumbles
Gheist is a campaign tracked by Wiz Research since 15 September 2026 that uses stolen GitHub tokens to push a sync-check workflow on ci-sync-* branches in every reachable repository. The workflow prints base32-encoded secrets into logs, which the tool downloads through the GitHub API and then deletes. Over 13,500 branches from 850+ accounts were recovered. The post covers the two tool variants, a buggy self-hosted runner payload, GitHub's approval hold (which does not cover private repositories), overlaps with other campaigns, hunting queries, IOCs and hardening steps.
wiz.iowriteupPublished and added 25 Oct 2026- lee1981 (@lee1981b) on X
CyberForge Weekly CVE Rundown #007 covers six CVEs from 19 to 24 October 2026: SiteGuard command injection (CVE-2026-106931), DB-GPT (CVE-2026-77932), Siemens Software Center DLL side-loading (CVE-2026-110936), Cisco Expressway (CVE-2026-76466), Node.js Brotli (CVE-2026-111497) and Arista VeloCloud (CVE-2026-114625). Each entry gives defender actions, fixed versions, exploitation status and primary-source links. Updated 25 October 2026 with CISA KEV and EPSS findings.
x.comarticleAdded 27 Oct 2026, published 25 Oct 2026  Argus – a free, open-source agentic security operations platform – MIT
Argus is a free, MIT-licensed, self-hosted security operations platform that maps cloud, identity, code, device, network and Kubernetes assets into one evidence graph and detects fast, AI-driven attacks. Read-only AI agents investigate and only propose actions. Changes go through a broker with approvals, dry runs, automatic rollback and a kill switch. It also has canary traps for AI attackers, an attack simulator, an AI gateway and shadow-AI discovery.
 thomasunise.comtoolAdded 25 Oct 2026, published 24 Oct 2026
- CISA: Critical Vulnerabilities in PHP Require Immediate Patching
CISA alert on CVE-2026-109618 and CVE-2026-109619 ("php2shell"), unauthenticated remote code execution flaws affecting PHP installations serving web requests, including mod_php, PHP-FPM, php-cgi, FrankenPHP and LiteSpeed. Fixed in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35. Updated 23 October 2026 with a Sigma rule, partner advisories (NSA, NCSC-UK, ASD ACSC, NCSC-NL, NCSC-NZ, Cyber Centre) and guidance to inventory PHP, patch internet-facing systems first, and watch for PHP workers spawning shells. No in-the-wild exploitation had been observed.
 cisa.govadvisoryAdded 24 Oct 2026
 New Evidence Shows LiteLLM Secret-Stealing Workflows Ran 11 Days Before Supply Chain Attack
Socket's Threat Research team reports that malicious cache.yml workflows ran in the BerriAI/litellm repository on 10 and 12 October 2026, eleven days before the 21 October release attack that published litellm==1.107.0. Each commit pushed to a short-lived ci-tmp-<hex> branch, then deleted it, sending base64-encoded CI secrets to webhook.site. Evidence comes from Actions metrics and environment deployment records; 20 secret names were exposed.
 socket.devwriteupPublished and added 23 Oct 2026
- Inside the LiteLLM 1.107.0 supply chain compromise: Credential theft through Python startup hooks
Microsoft's analysis of the LiteLLM 1.107.0 compromise, published to PyPI and container images on 21 October 2026. The wheel shipped cook.pth, cook.py and sitecustomize.py, so a credential collector (PRIVCOLLECT) ran whenever Python started, even without importing LiteLLM. It covers AES/RSA-encrypted exfiltration to litellm.dev, a re-armable Unix loader, Defender KQL hunting queries, ATT&CK mapping and rotation guidance.
microsoft.comwriteupPublished and added 23 Oct 2026  CVE-2026-109618 / CVE-2026-109619 | NodeZero Rapid Response Check Now Available
PHP2Shell is the name for CVE-2026-109618 and CVE-2026-109619, critical unauthenticated RCE flaws in PHP core fixed on 21 October 2026 in PHP 8.2.35, 8.3.36, 8.4.27 and 8.5.12. The page explains the out-of-memory corruption and stale global state causes, mod_php and PHP-FPM exposure, interim mitigations, hunting guidance, exploitation reports from October 2026, and the 23 October CVE-2026-115560 upload-progress advisory. Horizon3 also announced a non-exploiting NodeZero check.
 horizon3.aiadvisoryAdded 29 Oct 2026, published 23 Oct 2026
 PHP2Shell: What This Week Tells Us About the Web We Built
PHP2Shell is the name for two unauthenticated remote code execution flaws, CVE-2026-109618 and CVE-2026-109619 (CVSS v4 9.2), in the PHP engine back to version 5.4. The post covers the leaked October 2026 embargo, AI-assisted exploit building by Calif and others, patch availability by PHP version, and a 72-hour and quarterly response plan covering inventory, patching, secret rotation and edge virtual patching. It ends with a short Orca product section.
 orca.securityarticlePublished and added 23 Oct 2026
 Preliminary Report Oct 21st Security Incident
Railway's preliminary report on a security incident between 20 and 22 October 2026, in which an attacker reached internal systems and decrypted stored environment variables. At most 1.85% of workspaces (about 100,000) were confirmed affected. The attacker was after AI provider API keys for distillation. Railway notified vendors such as GitHub and Anthropic, rolled all keys, moved to single-tenant builders and advised customers to rotate secrets. Exploit details are withheld.
 blog.railway.comadvisoryAdded 24 Oct 2026, published 23 Oct 2026
- Previdian (@PrevidianCyber) on X
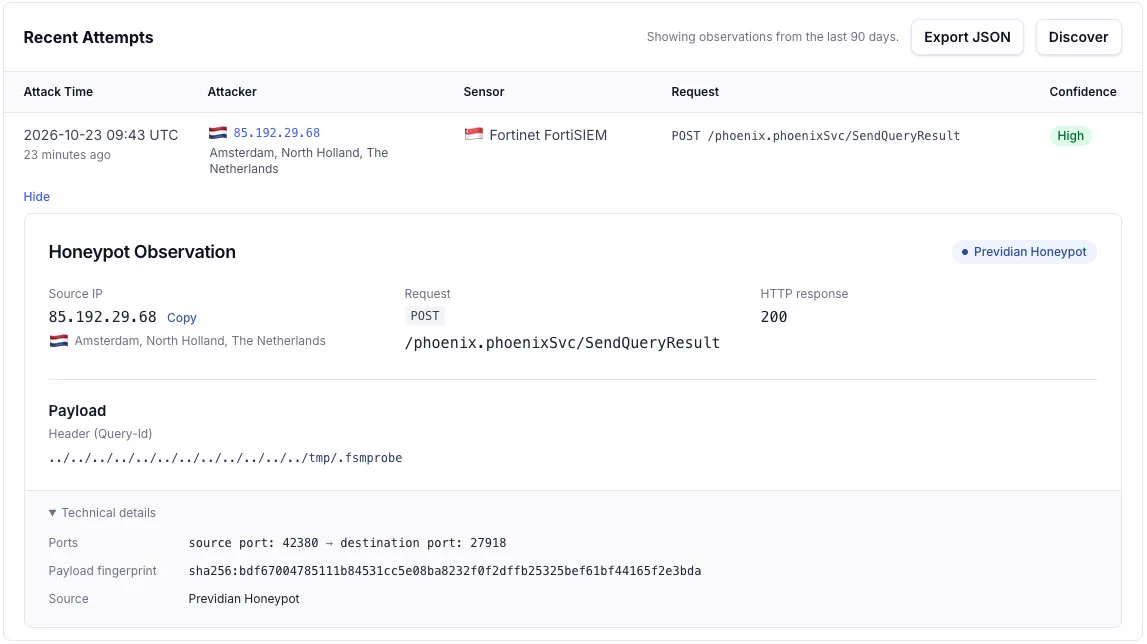
Previdian Cyber reports an exploitation attempt against its FortiSIEM honeypot on 23 October 2026 at 09:43:32 UTC, targeting the FortiSIEM path traversal CVE-2026-106173. The request, from 85.192.29[.]68, POSTed to /phoenix.phoenixSvc/SendQueryResult on TCP 27918 with twelve ../ sequences in the query-id header, trying to overwrite /tmp/.fsmprobe with an empty file. It matches the file overwrite mode of the Horizon3.ai PoC; success is not confirmed. Mitigation: upgrade to FortiSIEM 7.5.1 or later and restrict TCP 27918.
x.comthreadAdded 25 Oct 2026, published 23 Oct 2026 - lee1981 (@lee1981b) on X
CVE-2026-111497 is an out-of-bounds write in the Brotli decoder bundled with Node.js (CWE-787, CWE-252), rated CVSS v4.0 9.2 by the Google CNA and High by the Node.js project. Fixes are Node 22.23.4, 24.22.1 and 26.12.1, and 24.22.1 still labels Brotli 1.2.0 because the fix was cherry-picked. The post gives a SOC trail from input to worker, with remediation and verification steps. It notes no KEV match, CISA SSVC exploitation none, and only unverified public lab claims.
x.comadvisoryAdded 26 Oct 2026, published 23 Oct 2026 - Field Notes: Reconstructing an Attacker’s Workflow
Field note from dfir.ch on PowerShell scripts an attacker left on disk during an incident: a file-watching command runner using Invoke-Expression, a fake Windows credential prompt that validates passwords via Start-Process and logs them in cleartext, AD computer enumeration with WMI access testing, and SMB share discovery via NetShareEnum. It notes where script labels overstate what they prove and lists hunting strings for Event IDs 4104, 4103, 4688 and Sysmon 1.
 dfir.chwriteupAdded 24 Oct 2026, published 22 Oct 2026
 EMudhra Intermediate CA Certificates Compromised
Unit 42 advisory on the compromise of eight intermediate CA private keys belonging to Indian CA eMudhra Limited. The keys were generated with insufficient randomness, so attackers could derive them from the public certificates and sign rogue TLS certificates for MitM attacks. eMudhra has revoked the certificates and browser and OS vendors have untrusted them. Interim guidance covers PKI and trust store audits, reissuance, strict CRL/OCSP checking, log hunting, CT monitoring and CAA records.
 unit42.paloaltonetworks.comadvisoryAdded 30 Oct 2026, published 22 Oct 2026
 The Current Landscape of OAuth Attacks
Unit 42 survey of OAuth attacks that steal tokens after MFA, so access survives password resets. It covers account hijacking (device authorization and authorization code misuse), permission hijacking (vague or impersonating app names), and malicious redirects, including the error-triggered redirect campaign Microsoft documented in March 2026. It also describes COSF and OAuth-as-a-service flaws, PhaaS and LLM evasion trends, and defenses such as admin-only consent and redirect_uri audits.
unit42.paloaltonetworks.comarticleAdded 30 Oct 2026, published 22 Oct 2026- Unboxing Phishing Kits: Huntress Examines 3 Real Kits
Recap of a Huntress Tradecraft Tuesday session (October 2026) on phishing kits that target Microsoft 365 tokens, including EvilTokens (a device-code phishing campaign abusing Railway) and the Kali365 control panel. It explains device-code phishing, adversary-in-the-middle and token replay. It lists detections (unfamiliar cloud sign-ins, device-code auth, new devices) and response steps (revoke refresh tokens, remove rogue devices, block device-code flow).
huntress.comarticlePublished and added 22 Oct 2026 - Anti-Forensics: Building a Phantomdrive
Phantomdrive is an open source USB drive built on the WCH CH569 chip that appears as a plain 8GB disk and hides the rest of an SD card behind AES-256 encryption. The hidden partition unlocks when the user saves "password:" in a text file; the firmware catches it in raw WRITE10 traffic and zeroes the buffer. Key derivation uses a per-device salt and 100,000 SHA-256 rounds, and the post compares AES-ECB, CTR and XTS speeds.
hackers-arise.comarticlePublished and added 22 Oct 2026 - M365 Token Spray and Replay Campaign Compromises Business Email Accounts
Huntress analysis of a July to September 2026 token replay ("token spraying") campaign: 497 successful Microsoft 365 sign-ins across 79 organizations, replayed from six addresses in 193.26.115.0/24 (1337 Services GmbH). Tokens came from AiTM relays, device-code phishing and social engineering. It covers four phases, rogue Entra devices, MFA method swaps, hidden inbox rules, hunting queries and Conditional Access guidance.
huntress.comwriteupPublished and added 22 Oct 2026  Tech and Security Companies Respond to PHP2Shell Vulnerabilities
SecurityWeek roundup of responses to PHP2Shell, two critical unauthenticated RCE flaws (CVE-2026-109618, CVE-2026-109619) fixed in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 on 21 October 2026. It covers the exploitation timeline (first attempt 17 October), vendor exposure checks, Red Hat's lower 8.1 score against NVD's 9.8, detections from Cisco Talos, CrowdStrike and Corelight, and government alerts.
securityweek.comarticlePublished and added 22 Oct 2026- lee1981 (@lee1981b) on X
CyberForge CVE of the Day #084 analyses CVE-2026-76466, a CVSS 9.8 flaw in clustered Cisco Expressway-C and Expressway-E. Persistent database cookies and weak client-certificate validation allow root OS command execution over the network. The fix is X15.5.20 (X14 and earlier must migrate), with no workaround. It adds a per-peer SOC investigation trail, reachability checks and exposure status from CISA SSVC, KEV and EPSS.
x.comadvisoryAdded 24 Oct 2026, published 22 Oct 2026  SecLog-Bench: A Scalable Benchmark for Cybersecurity Log Reasoning with Scaffolded Evidence
SecLog-Bench is a benchmark for LLM reasoning over cybersecurity logs, built on an extensible simulation platform covering 29 attack scenarios. It combines audit logs, application logs and network traffic, with attack-stage labels and step-by-step evidence chains. Eight LLMs were tested on post-detection attack-progress reasoning: the best reached 44.44% accuracy, 45.07% Macro-F1 and 54.87% Stage Reasoning F1.
 arxiv.orgpaperAdded 23 Oct 2026, published 22 Oct 2026
 Sizing the PHP exposure window for CVE-2026-109618 and CVE-2026-109619 with VirusTotal
VirusTotal sizes the internet-facing PHP footprint around CVE-2026-109618 and CVE-2026-109619 (CVSS v4.0 9.2, session.upload_progress) using Internet Scanning. About 5.1M IPs run PHP, roughly 4 in 5 hide their version, and ~758K disclose an end-of-life branch. It gives queries that use the SSH banner to match leaked LiteSpeed lsphp 8.2.34 builds, plus mitigations.
 blog.virustotal.comarticleAdded 22 Oct 2026
 Using AWS WAF to apply mitigations for PHP2Shell RCE vulnerabilities (CVE-2026-109618 and CVE-2026-109619)
AWS Security Blog guide to mitigating the PHP2Shell unauthenticated RCE flaws (CVE-2026-109618 and CVE-2026-109619, CVSS v4.0 9.2) with AWS WAFv2 rules. It covers rules for the PHP_SESSION_UPLOAD_PROGRESS trigger, blocking multipart/form-data, body size caps and rate limits, plus body inspection limits. It lists PHP fixes (8.5.12, 8.4.27, 8.3.36, 8.2.35) and server settings, and stresses WAF only reduces exposure.
aws.amazon.comarticlePublished and added 22 Oct 2026 Amazon Threat Intelligence identifies PHP2Shell exploitation prior to public disclosure in MadPot
Amazon Threat Intelligence reports PHP2Shell exploitation (CVE-2026-109618, CVE-2026-109619) seen in MadPot honeypot telemetry on 17 October 2026, four days before the 21 October disclosure, from anonymization-network IPs. Multiple actors and PoCs appeared within hours of the patch. It recommends upgrading PHP, hunting for PHP_SESSION_UPLOAD_PROGRESS in multipart POSTs, and investigating from the earliest exploitation date, with patch SLAs measured in hours.
aws.amazon.comarticlePublished and added 21 Oct 2026 AI-driven, large-scale nation-state campaign using ARTEX enables supply chain compromise
Microsoft Threat Intelligence report on Storm-0940, a China-state aligned actor that used the open-source agentic AI pentest framework ARTEX from September 2026 to automate attacks on hundreds of organizations. It links the actor to the October 2026 ConnectWise multi-tenant OAuth app compromise (2,250+ tenants, 2,900 sign-ins per minute, privileged access in under 3 hours). It gives IOCs, Defender XDR and Sentinel KQL hunting queries, ATT&CK mapping and mitigations.
microsoft.comwriteupPublished and added 21 Oct 2026 Google Hardens Chrome Against ClickFix Attacks, Insecure HTTP Connections
SecurityWeek reports new Chrome protections against scams and social engineering. Enhanced Protection users get ClickFix detection that scrubs and sends copied suspicious commands to Safe Browsing, plus server-side Gemini scam analysis covering fake antivirus and browser update pages. Safe Browsing warnings now have a lower-confidence "suspicious site" level, and Chrome prompts before HTTP connections by default for everyone.
securityweek.comarticlePublished and added 21 Oct 2026 Two critical RCEs in PHP core
Cisco Talos advisory on "php2shell", two unauthenticated RCE flaws in PHP core, CVE-2026-109618 and CVE-2026-109619 (CVSS v4.0 9.2), affecting every build since PHP 5.4. One flaw is an out-of-memory handling bug leaving request data partly initialized; the other reuses stale state after free. PHP 8.1 and older get no patch (about 50% of PHP systems). Includes ini-level mitigations and Snort SIDs 67359 and 67360. No exploitation seen as of 21 October 2026.
blog.talosintelligence.comadvisoryPublished and added 21 Oct 2026 ‘Context Bombs’ Cut AI Attack Success by Misleading Agents With Fake Targets
Tracebit's research "Making attacking agents pay" describes nine "context bombs", hidden prompts planted in a target that misdirect attacking AI agents with fake targets and endless problems. They stopped all attacks by GPT 5.6 Cyber, Kimi K3, Qwen 3.8 Max and DeepSeek V4 Pro, cut GPT-6 Astra successes by 54% and Claude Opus 5 successes by 91%. The best bomb was a fake pen test report; surviving attacks cost 23x more.
securityweek.comarticlePublished and added 21 Oct 2026 litellm 1.107.0 Compromised on PyPI: Backdoored Wheels Drop a Credential Stealer and an Hourly Remote Code Loader
litellm 1.107.0 was published to PyPI on 21 October 2026 with all seven wheels backdoored through an injected `data = "cook"` maturin build line. The wheels drop cook.pth, cook.py and sitecustomize.py, which run on every Python start. They install a "privcollect" credential stealer (browser, SSH, cloud, AI coding tool and LiteLLM proxy database secrets, sent to litellm.dev) and an hourly GitHub dead-drop remote code loader. The post gives IOCs, detection commands and recovery steps.
stepsecurity.iowriteupPublished and added 21 Oct 2026 Cloudflare deploys protections against php2shell vulnerability
Cloudflare describes its WAF protections for php2shell (CVE-2026-109618 and CVE-2026-109619), two PHP runtime memory-handling flaws affecting PHP 5.4 and later that can cause denial of service, remote code execution and data exposure. Rules shipped 21 October 2026, about 9 hours before disclosure, using a new "full transaction detection" that matches request and origin response together. It lists ruleset IDs and says patching PHP is still required.
blog.cloudflare.comarticleAdded 22 Oct 2026, published 21 Oct 2026 Introducing full transaction detection for Cloudflare WAF
Cloudflare announces full transaction detection and response-phase rules for its WAF. Detections evaluate an HTTP request together with the origin's response, so exploitation can be confirmed (for example, path traversal returning a config file) and the response replaced with a 403 block page. Covers managed and custom rules, the limit of three custom response rules, no response-body matching yet, and a first managed rule for php2shell. Available on all plans, including Free.
blog.cloudflare.comarticleAdded 29 Oct 2026, published 21 Oct 2026- Prompt Injection Through Forensic Evidence: A Taxonomy and Proof of Concept of Anti-Forensic Attacks on LLM-Assisted Digital Investigations
Paper on prompt injection delivered through forensic evidence, where the seized device's contents are attacker-controlled and the examiner must read them. It extends the anti-forensic model to cover manipulation of the reasoning layer and gives a taxonomy (objective, technique, payload location, concealment). Three proof-of-concept attacks on an LLM-assisted analysis pipeline change a reported conclusion, write attacker-chosen content to the analyst workstation, and trigger outbound network traffic. Mitigations are proposed.
arxiv.orgpaperAdded 24 Oct 2026, published 21 Oct 2026 - Amazon-Themed ClickFix Campaign Serves Up Finger-Licking Malware
Huntress analysis of an Amazon-themed ClickFix campaign that used a Google sponsored result, a fake Amazon login on Google Sites and a fake CAPTCHA to make victims run the Windows finger utility. The .plan script drives IronPython, a Cyrillic-substituted Base64 Python loader, Doina, a Node.js stage, Lumma Stealer via sRDI, and a pirated NetSupport RMM. It lists C2 domains and gives detection tips (aclk/gclid markers, blocking the Run dialog).
huntress.comwriteupPublished and added 21 Oct 2026 - Cyber Detective💙💛 (@cyb_detective) on X
Python Cybersecurity Libraries is a curated GitHub list by Yogsec, shared in a post by cyb_detective. It groups Python libraries by task: network analysis, penetration testing, threat intelligence, reverse engineering and malware analysis, forensics and investigation, web application security, CTF, and machine learning for security. The tweet shows only the category names, not the individual libraries.
x.comrepoAdded 24 Oct 2026, published 21 Oct 2026  RingTrace: Model-Free Spatio-Temporal Detection and Core Attribution for Cache Side-Channels
RingTrace is a monitoring framework that detects Flush+Reload cache side-channel attacks by combining per-core cache-miss counters with slice activity across uncore CBoxes. Its Joint Spatio-Temporal Attribution (JSTA) builds a joint-activity matrix without model training: the largest entry is the screening score and row sums point to a candidate core. The authors report detection before secret leakage, fewer false alarms under heavy memory load, and negligible runtime overhead on commodity processors.
 eprint.iacr.orgpaperAdded 24 Oct 2026, published 21 Oct 2026
 Parasitizing trust: How legitimate infrastructure becomes a delivery pipeline for attackers
Cisco Talos research on attackers using legitimate infrastructure to deliver lures, with abuse seen across more than 25 platforms in the past year. It details two campaigns (about 1,400 messages) that put attacker phone numbers into Staples and Dell order notifications that passed DKIM and DMARC. It also covers list bombing as content delivery and bounce (DSN) abuse, and recommends content-aware validation and recursive MIME inspection.
blog.talosintelligence.comwriteupPublished and added 21 Oct 2026- lee1981 (@lee1981b) on X
CVE-2026-110936 is an uncontrolled DLL search path flaw (CWE-427) in Siemens Software Center below V4.0.9.8, listed in CISA KEV on 20 October 2026. The post covers CVSS v4.0 8.4 and v3.1 6.7, Siemens' Romulus ClickFix campaign indicators (IPs, domain, hashes, file leads) and a six-step SOC trail using Sysmon, EDR and network records. It separates delivery from DLL load and from compromise.
x.comarticleAdded 24 Oct 2026, published 21 Oct 2026 - eness/php2shell-CVE-2026-109618-CVE-2026-109619-PoC
php2shell is the name given to two critical pre-auth remote code execution flaws, CVE-2026-109618 and CVE-2026-109619, in PHP core's session upload progress handler (php_session_rfc1867_callback), where zend_hash_update frees live zval pointers that are later reclaimed and redirected into zend_call_function to run zif_system. This repository ships poc_109618.py, a fully automated four-stage HTTP exploit that leaks ASLR offsets via Set-Cookie headers against php:8.4.26-apache on Debian Bookworm, along with a root-cause C source patch, mitigation scripts to disable session.upload_progress, and WAF/ModSecurity/Lighttpd/Apache rules plus detection guidance for anomalous PHP worker child processes. Confirmed PHP versions include 8.4.4 and 8.2.34, with EOL branches (5.x, 7.x, 8.0, 8.1) left without official vendor patches.
github.comrepoAdded 23 Oct 2026, published 21 Oct 2026















Showing 60 of 431
Show more