 x.comthread
Previdian (@PrevidianCyber) on X
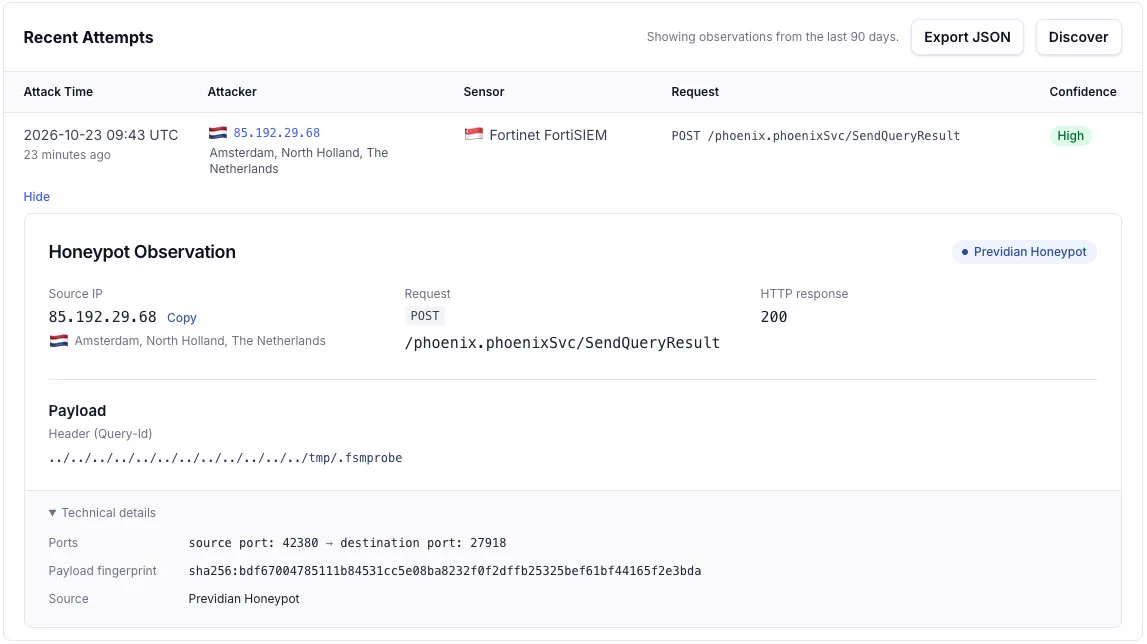
Previdian Cyber reports an exploitation attempt against its FortiSIEM honeypot on 23 October 2026 at 09:43:32 UTC, targeting the FortiSIEM path traversal CVE-2026-106173. The request, from 85.192.29[.]68, POSTed to /phoenix.phoenixSvc/SendQueryResult on TCP 27918 with twelve ../ sequences in the query-id header, trying to overwrite /tmp/.fsmprobe with an empty file. It matches the file overwrite mode of the Horizon3.ai PoC; success is not confirmed. Mitigation: upgrade to FortiSIEM 7.5.1 or later and restrict TCP 27918.
What it is
Previdian Cyber recorded a single exploitation attempt against its FortiSIEM honeypot on 23 October 2026 at 09:43:32 UTC. It targeted CVE-2026-106173, a path traversal in Fortinet FortiSIEM. The source was 85.192.29[.]68, and it was the only request from that address. The request matches the file overwrite mode of the Horizon3.ai proof of concept, which was published on 20 October 2026, so exploitation began three days after the PoC appeared.
How it works
The request has these features, which can be used for detection:
- Method and path: POST /phoenix.phoenixSvc/SendQueryResult
- Transport: HTTP/2 over TLS on TCP 27918
- Traversal: twelve
../sequences in the query-id header, pointing at /tmp/.fsmprobe - Body: a 7-byte gRPC message carrying empty file contents
The goal was to overwrite /tmp/.fsmprobe with an empty file. The request contained no shell commands. The file name suggests a probe to test whether the target is vulnerable, though the page does not say so.
What to do
- Upgrade to FortiSIEM 7.5.1 or later, following Fortinet's advisory.
- Restrict access to TCP 27918.
- Check hosts for unexpected /tmp/.fsmprobe files.
- Search proxy or network logs for requests to SendQueryResult with repeated
../in the query-id header.
Caveats
The capture does not confirm a successful file write or code execution. It comes from a decoy system, so it shows scanning activity rather than a compromise of a real deployment. The page does not describe the other PoC modes, the affected version range below 7.5.1, or the attacker's intent beyond the file overwrite.
Organisations named here
- 85.192.29.68
- Previdian Cyber
CVEs named here
- CVE-2026-106173
Technologies named here
- FortiSIEM honeypot decoy
- Fortinet FortiSIEM
- Horizon3.ai proof of concept, published 20 October 2026
- grpc
- Horizon3.ai
- FortiSIEM
Techniques named here
- Path traversal
Threat actors named here
- Source IP 85.192.29[.]68
- PHP2Shell
Related in Threat Intel

 huntress.comwriteup
Reverse Engineering the Six Stages of MacSync Stealer and RAT
 huntress.comwriteup
AI-Coded Malware | Analyzing Vibe-Coded AD Enumeration | Huntress

 blog.talosintelligence.comtool
Introducing CAIRN: Frontier tracking for AI-integrated malware (Cisco Talos)
 huntress.comwriteup