 Inside a malicious Claude Code-branded extension and its persistent SSH backdoor
Microsoft Threat Intelligence analyzes a tampered anthropic.claude-code extension (versions 2.1.312 and 2.1.313) served on the Cursor marketplace on 29 October 2026. The injected JavaScript loader adds an SSH key labeled svc-telemetry, opens a reverse SSH tunnel and sets up persistence on macOS, Linux and Windows. The post gives cleanup steps, IOCs and Defender XDR hunting queries. VS Code Marketplace and npm were not affected.
 microsoft.comwriteupPublished and added 31 Oct 2026
 Trojanized Claude Code Extension Plants an SSH Backdoor
Analysis of a trojanized anthropic.claude-code 2.1.313 extension (darwin-arm64), found on Open VSX, with a 66-line loader prepended to extension.js. It adds an svc-telemetry key to authorized_keys, opens a reverse SSH tunnel to 134.209.82.225, sets persistence (LaunchAgent, cron, scheduled task) and sends host recon over HTTP port 8099. Includes IOCs, hashes and response steps; no further payload download was found.
 opensourcemalware.comwriteupPublished and added 30 Oct 2026
 Backdoor in Claude Code for VS Code extension on the Cursor Marketplace
Phorion analyzes a backdoor injected into versions 2.1.312 and 2.1.313 of the official Claude Code for VS Code extension on the Cursor Marketplace. An IIFE prepended to extension.js plants an SSH key, opens a reverse SSH tunnel to 134.209.82[.]225, persists via a fake com.apple.sysmond LaunchAgent and beacons host recon. A macOS systemsetup check bug usually stops SSH from being enabled. The post lists detections and remediation.
 phorion.iowriteupAdded 31 Oct 2026, published 30 Oct 2026
 Earliest Known PolinRider Malware Found in 2025 npm Packages
OpenSourceMalware traces nine itsa-* npm package versions published on 4 May 2025 from a hijacked maintainer account to the PolinRider campaign, eight months before documented victims. It decodes the EtherHiding chain (BNB Smart Chain and Ethereum calldata, JADESNOW, INVISIBLEFERRET bootstrapper, Socket.IO RAT, Python stealer) and links the 2025 sample to 2026 force-push infections. It lists IOCs, hashes, a timeline and hunting guidance.
opensourcemalware.comwriteupPublished and added 30 Oct 2026- rikugan: LLM reverse-engineering agent for IDA Pro and Binary Ninja
Rikugan is an open-source reverse-engineering agent that runs inside IDA Pro 9.0+ and Binary Ninja, with its own agent loop instead of an MCP server. It has 60+ tools (decompiler, xrefs, strings, types, IL/microcode), parallel subagent exploration, an experimental /modify natural-language patching command and an experimental Binary Ninja deobfuscation skill for control flow flattening and opaque predicates. It supports Claude, Gemini, MiniMax, Kimi, OpenAI-compatible endpoints and Ollama.
 github.comrepoAdded 30 Oct 2026
 Hackers exploit Cisco SD-WAN flaw to deploy custom KeyDrift malware
UAT-11473, a newly tracked APT cluster, exploits CVE-2026-20127, a max-severity authentication bypass in Cisco Catalyst SD-WAN Controllers (patched February 2026), to deploy the KeyDrift malware framework. KeyDrift's PolyFlame runs inside vdaemon processes, and LittleFilch hooks SSL_read to extract AES-256 IPsec keying material, saved to /var/tmp/vdaemon.bin and sent over UDP. Targets include space, defense and policy organizations. Talos sees overlap with Volt Typhoon's Silent Train network but makes no definitive link.
 bleepingcomputer.comarticleAdded 30 Oct 2026, published 29 Oct 2026
 Cisco SD-WAN Zero-Day Exploitation Tied to Volt Typhoon’s ‘Silent Train’ Network
Cisco Talos reported that UAT-11473 exploited CVE-2026-20127 (CVSS 10, Cisco SD-WAN peering authentication bypass) to deploy KeyDrift, a framework with PolyFlame (backdoor, relay C2) and LittleFilch (key harvesting) modules. Talos found its infrastructure overlaps considerably with Volt Typhoon's Silent Train network. Lumen Black Lotus Labs tied Silent Train to zero-day campaigns against Versa Director, N-able N-central, Cisco Catalyst SD-WAN and VeloCloud Orchestrator.
 securityweek.comarticlePublished and added 29 Oct 2026
 NIK C2: The new AI-enabled command-and-control framework
NIK C2 is a newly observed C2 framework with a Go-based 64-bit Windows implant that embeds an OpenAI Chat Completions client (ai_generate command), falling back to the victim's OPENAI_API_KEY. Talos details its 52+ commands, AES-256-GCM over WebSocket with HTTP fallback, credential, wallet and keystroke theft, screen-lock ransomware, AMSI bypass and anti-debug. It also lists a live C2 at 87.120.196[.]120 and total-sitevv[.]lol.
 blog.talosintelligence.comwriteupPublished and added 29 Oct 2026
 Inside KeyDrift: Analyzing historical UAT-11473 activity on Cisco SD-WAN
KeyDrift is a custom malware framework used by UAT-11473, which exploited CVE-2026-20127 in Cisco SD-WAN Catalyst Controller to gain access. Talos analyzes PolyFlame (memory-resident vdaemon injection, recvfrom hook, TinyShell-style backdoor, intermediate C2) and LittleFilch (SSL_read hook that extracts and RSA-encrypts keying material). It reports infrastructure overlap with Volt Typhoon's Silent Train, plus patch guidance and Snort SIDs.
blog.talosintelligence.comwriteupPublished and added 28 Oct 2026- Hakimi Eiqbal (@hakimieiqbal) on X
A practical reverse-engineering map by hakimieiqbal on X that picks tools by target: native binaries, .NET, Electron, iOS, firmware, WebAssembly and network protocols. It introduces REA (morluto/rea), which connects coding agents to RE tools, and lists MCP bridges for IDA Pro, Ghidra and radare2. It adds an evidence-first workflow and free courses such as pwn.college and OpenSecurityTraining2.
 x.comthreadAdded 29 Oct 2026, published 28 Oct 2026
 Malicious Firefox Extensions Impersonate Phantom, Jupiter, and Bitget to Steal Wallet Secrets
Socket analysis of three malicious Firefox add-ons impersonating Phantom, Jupiter and Bitget wallets, using Unicode homoglyph names. They steal seed phrases and private keys and send them to brand-named subdomains of bonto[.]io. The Phantom fake adds a runtime loader that fetches and evals a second stage, and bundles a drainer backend with Telegram forwarding. Includes IOCs, hashes and wallet addresses.
 socket.devwriteupPublished and added 27 Oct 2026
 Cheap AI-Assisted Reverse Engineering and What It Will Do
"Cheap AI-Assisted Reverse Engineering and What It Will Do" is an October 2026 arXiv paper (Computers and Society) arguing that generative AI strains the law of reverse engineering. AI systems can identify hardware components, extract firmware, decompile object code and clone apps, which removes the cost barrier that laws rely on. The authors map these practices onto trade secret, copyright, anti-circumvention, computer misuse and contract law, and sketch possible legal responses with their trade-offs.
 arxiv.orgpaperAdded 28 Oct 2026, published 26 Oct 2026
- Zex Alpha (@kryptozex) on X
Post about the "Steal My Bitcoin" bounty, a 0.025 BTC (about $2,025) prize that was swept early Monday, about 90 minutes after researcher @killa published a full exploit on GitHub. The exploit is a heap exploit written for the target's PHP build. It leaks memory addresses through session cookies and forces PHP cleanup to run the flag binary. The first solve looked like a failure because the pulled key did not control the advertised address, a planting mistake the creator admitted by email.
x.comthreadPublished and added 26 Oct 2026 - Dan Kornas (@DanKornas) on X
jshook is an open-source (AGPL-3.0) search-first reverse-engineering workspace for AI agents, exposed over MCP. It drives Chromium or Camoufox through CDP, captures WebSocket traffic, offers HTTP, GraphQL and Burp Suite helpers, deobfuscates JavaScript, rebuilds source maps and disassembles WebAssembly. Tool profiles start small and expand to workflow or full sets; hot-reload plugins and declarative workflows extend it.
x.comtoolAdded 28 Oct 2026, published 25 Oct 2026 - VulDec: Vulnerability Detection in Binaries via Neural Decompilation
VulDec is an arXiv paper (October 2026) presenting a dataset of real-world Assembly-C function pairs with CWE labels across multiple architectures, plus an end-to-end framework that uses neural decompilation for binary vulnerability detection. Tuned LLM decompilers reach about 56% Edit Similarity and 43% BLEU-4. Tuned LLM detectors reach macro F1 of 0.61 on a realistic test set with a 3% vulnerability rate.
arxiv.orgpaperAdded 28 Oct 2026, published 24 Oct 2026  OVHcloud CLI Compromised via GitHub Release Swap: Detonating the Real GlassWorm Loader and What We Found
Analysis of the 19 October 2026 swap of binaries on five ovh/ovhcloud-cli GitHub releases (v0.11.0 to v0.15.0), live 94 minutes. StepSecurity rebuilt the attacker's binary, detonated the recovered GlassWorm preinstall.js loader against a controlled Solana dead drop, and found install.sh never exposed arm64 Linux, Homebrew was safe, and `ovhcloud version` showing "undefined" identifies the swapped build. Includes IOCs and recovery steps.
 stepsecurity.iowriteupPublished and added 24 Oct 2026
- Trail of Bits (@trailofbits) on X
Trail of Bits announces a scanner, built by Scott A., that finds hidden copies of the vulnerable Brotli decoder behind a Node.js/Brotli bug, including in stripped binaries. Exploitability of the bug is still under testing. Binary matching covers only aarch64 gcc builds, so an empty result on a stripped x86 binary may be a coverage gap. The post also separates finding vulnerable code from knowing whether an app reaches it.
x.comtoolAdded 25 Oct 2026, published 23 Oct 2026 - Yash Patil (@yvshpvtil) on X
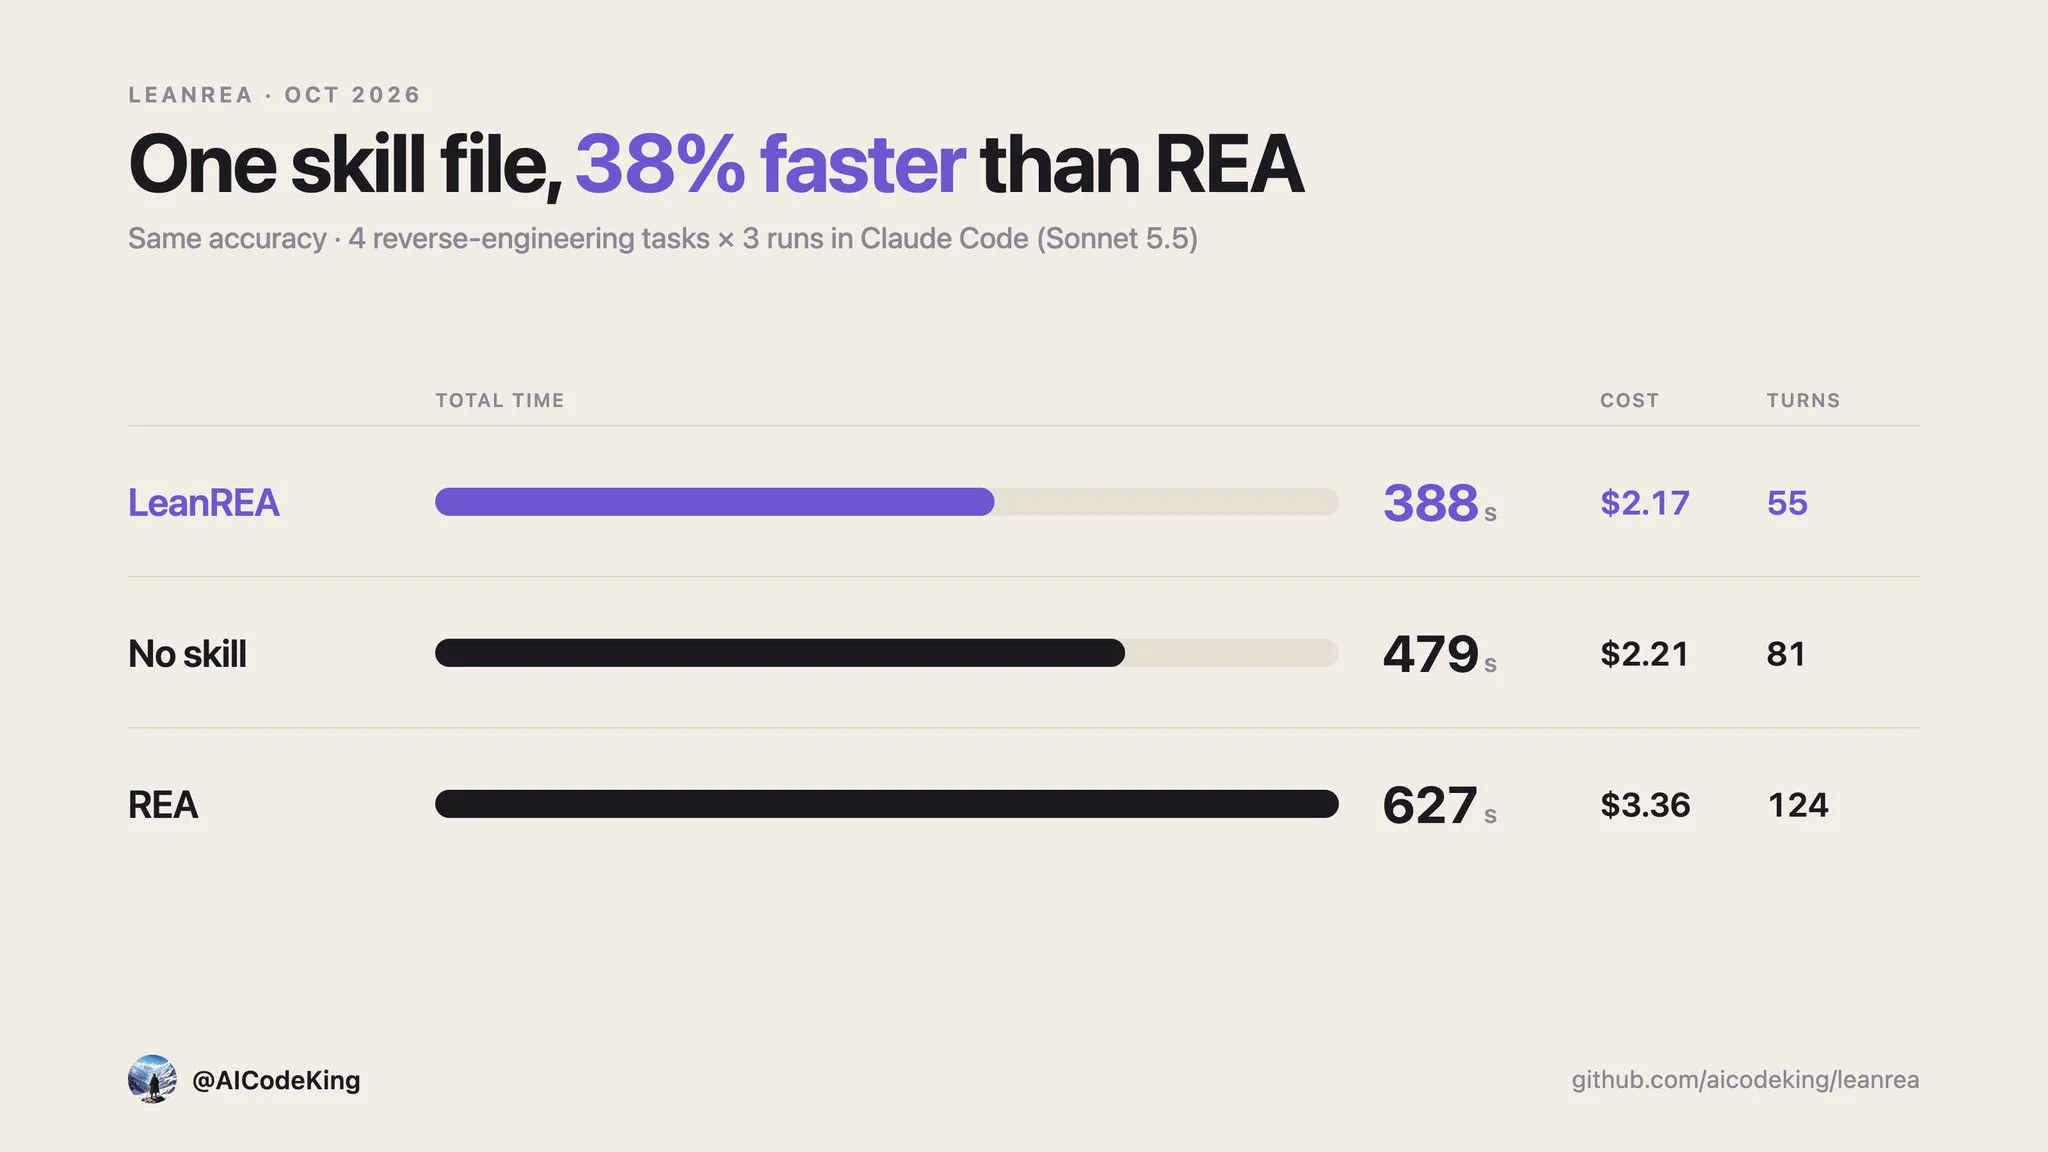
leanrea is an 8 KB skill file that tells a coding agent which plain CLI tools to use for reverse engineering, replacing the 207-tool REA MCP server. The author's test reports 38% faster, 35% cheaper, and a score of 74/75 against REA's 75/75. Caveats listed: 3 runs per task, one model, one machine, and Claude with no skill already performed decently. Replies question whether the lost point was a task where structured tool output beat parsing CLI text.
x.comthreadAdded 25 Oct 2026, published 23 Oct 2026  In Other News: Tor Exit Relays Hijacked, Banks Spot Rogue AI Agents, Self-Rebuilding macOS Ransomware
SecurityWeek's weekly roundup covers Heartbreaker, a Rust macOS ransomware that recompiles itself to change its hash, and 333 Tor exit relays running Ebury that redirected SSH logins to harvest passwords. It also covers APT28 Hookedge attacks on a NATO shipbuilder, the Railway and PingCAP breaches, ISO/IEC 27090 for AI threats, and US banks blocking unsanctioned AI agents.
securityweek.comarticlePublished and added 23 Oct 2026- x86rc/unthemidator
Unthemidator is an automated unpacker for binaries protected with Themida, Code Virtualizer and WinLicense (v3.0 to v3.2.6.0, experimental v4.0). It works without executing the target, handles x86 and x64 exe, dll and sys files, decrypts imports, restores the IAT, rebuilds the PE and identifies VM versions and entry points. It does not devirtualize or unmutate code. Releases cover Windows x64 and macOS Apple Silicon.
github.comrepoAdded 27 Oct 2026, published 23 Oct 2026  LiteLLM 1.107.0 Compromised: Python Startup Hooks Steal Cloud, AI, and Proxy Credentials | Endor Labs
litellm 1.107.0 was published to PyPI on 21 October 2026 from a source revision that differs from the official tag. One line in the Maturin config (data = "cook") installs cook.pth, cook.py and sitecustomize.py, which run on every Python start. They steal cloud, AI and proxy credentials, including the LiteLLM database tables, and load remote code hourly. The post gives IOCs, a five-step response plan and hardening advice.
 endorlabs.comwriteupPublished and added 21 Oct 2026
 litellm 1.107.0 Compromised on PyPI: Backdoored Wheels Drop a Credential Stealer and an Hourly Remote Code Loader
litellm 1.107.0 was published to PyPI on 21 October 2026 with all seven wheels backdoored through an injected `data = "cook"` maturin build line. The wheels drop cook.pth, cook.py and sitecustomize.py, which run on every Python start. They install a "privcollect" credential stealer (browser, SSH, cloud, AI coding tool and LiteLLM proxy database secrets, sent to litellm.dev) and an hourly GitHub dead-drop remote code loader. The post gives IOCs, detection commands and recovery steps.
stepsecurity.iowriteupPublished and added 21 Oct 2026 LiteLLM PyPI Package and Docker Images Compromised to Steal Cloud and AI Credentials
LiteLLM 1.107.0 on PyPI and GHCR images shipped Python startup hooks (cook.pth, sitecustomize.py) that steal cloud, SSH, browser and AI-tool credentials, including LiteLLM proxy database credentials. Image build provenance recorded a lookalike Berri-AI/litellm source repository. The post decodes the payload, encrypted exfiltration and GitHub-driven remote loader, and lists containment steps, MITRE ATT&CK mappings and IOCs.
socket.devwriteupPublished and added 21 Oct 2026 LiteLLM 1.107.0 PyPI Wheel Contains a Credential Stealer and Persistent Python Backdoor
LiteLLM 1.107.0 macOS x86-64 PyPI wheel analyzed by OpenSourceMalware contains three injected files (cook.pth, cook.py, sitecustomize.py) that run on every Python start. The payload, called privcollect, steals browser, SSH, cloud, CI/CD and AI-tool credentials, then uploads an AES/RSA-encrypted bundle to www.litellm.dev/healthcheck. A forked loader also fetches domain.txt from GitHub and executes /codepy hourly. The post lists IOCs, hashes and remediation steps.
opensourcemalware.comwriteupPublished and added 21 Oct 2026- Amazon-Themed ClickFix Campaign Serves Up Finger-Licking Malware
Huntress analysis of an Amazon-themed ClickFix campaign that used a Google sponsored result, a fake Amazon login on Google Sites and a fake CAPTCHA to make victims run the Windows finger utility. The .plan script drives IronPython, a Cyrillic-substituted Base64 Python loader, Doina, a Node.js stage, Lumma Stealer via sRDI, and a pirated NetSupport RMM. It lists C2 domains and gives detection tips (aclk/gclid markers, blocking the Run dialog).
 huntress.comwriteupPublished and added 21 Oct 2026
- Cyber Detective💙💛 (@cyb_detective) on X
Python Cybersecurity Libraries is a curated GitHub list by Yogsec, shared in a post by cyb_detective. It groups Python libraries by task: network analysis, penetration testing, threat intelligence, reverse engineering and malware analysis, forensics and investigation, web application security, CTF, and machine learning for security. The tweet shows only the category names, not the individual libraries.
x.comrepoAdded 24 Oct 2026, published 21 Oct 2026  From JavaScript to Renderer Code Execution: Three V8 Vulnerabilities and Two v8CTF Flags | depthfirst
Depth First Security's write-up describes three V8 bugs found using its dfs-large1 research tooling: CVE-2026-78938, a type confusion in Promise.prototype.finally that lets an internal helper be constructed and return a primitive; CVE-2026-79236, a TurboFan load-elimination bug that keeps a stale property-array pointer after object migration; and a shared WebAssembly memory sandbox escape (issue 546253900) caused by mismatched backing-store registration during serialization. It walks through turning each memory bug into addrof/fakeobj primitives, chaining either with the sandbox escape to reclaim a freed V8 isolate via a WebSocket allocation, and pivoting through a CFI-constrained ROP chain to achieve Chrome renderer code execution, earning two v8CTF flags. Fixes landed between August 20 and 25, 2026.
 depthfirst.comwriteupAdded 29 Oct 2026, published 20 Oct 2026
- ☣ KitPloit - Hacker Tools (@KitPloit) on X
DidierStevensSuite is a collection of Python scripts for malware analysis, file format parsing, hashing and forensic triage. It includes utilities for analysing PDF and OLE documents and for XOR-obfuscated data. The post is a short KitPloit announcement that links to the repository and gives no usage detail.
x.comrepoAdded 21 Oct 2026, published 20 Oct 2026 - Huda (@AlAssaf_H) on X
Source-level review of x64dbg-MCP, GhidraMCP and IDA Pro MCP security, dated October 2026. It covers GHSA-4478-h5jv-647m (missing authentication, 0.0.0.0 bind) and GHSA-jgj3-97w2-9v9r (Content-Length integer overflow before the token check, causing a DoS panic), and compares tags 1.0, v1.1 and v1.2. It separates network reachability, tool authority and semantic influence from hostile binaries. No new exploit is claimed.
x.comarticleAdded 21 Oct 2026, published 19 Oct 2026 - Panos Gkatziroulis 🦄 (@ipurple) on X
Malvex (JoasASantos/Malvex) is an AI-driven malware analysis framework that integrates more than 30 analysis tools, a web REPL and an MCP server. Panos Gkatziroulis shared it on 19 October 2026 and noted that it was written by AI. The tweet gives no detail on which tools are bundled or how the AI drives them.
x.comrepoAdded 22 Oct 2026, published 19 Oct 2026  Exploited Fortinet Bug Linked to Stealthy FortiGate Implant in Telecom Hack
UNC5820 (tracked by Palo Alto Networks as CL-STA-0954) breached a telecom in September 2024 using FortiManager flaw CVE-2024-47575 (FortiJump) and path traversal CVE-2025-61624, then deployed PeerStitch, a memory-resident ARM64 FortiGate implant. PeerStitch patches FortiOS log and IKE/IPsec daemons to build a covert bridge without listening ports. The actor also impersonated FortiManager over FGFM, using CVE-2024-26008. CISA added CVE-2025-61624 to KEV.
securityweek.comarticlePublished and added 19 Oct 2026- CyrilXBT (@cyrilXBT) on X
REA (github.com/morluto/rea) is an open-source tool that lets an agent such as Claude Code run reverse-engineering tools (Ghidra, IDA, JADX) on a local machine and return findings with evidence. Targets named are desktop apps, compiled programs and games, Android apps, website network traffic, and firmware or binaries. The post claims a DX Ball sound function was rebuilt to byte-identical code. Setup is `npx rea-agents setup`, and the author says to use it only on software you own or may analyze.
x.comthreadAdded 19 Oct 2026, published 17 Oct 2026  GhostAction Copycats PolinRider by Hiding a Stealer in a Fake Font File
Analysis of a new GhostAction Stage 2 found in 94 compromised GitHub repos: a hidden .vscode/tasks.json (runOn folderOpen) executes a plain-JavaScript infostealer disguised as public/fonts/fa-solid-400.woff2. The stealer grabs cloud, registry, SSH, Claude/Gemini credentials, POSTs them to a hardcoded IP on port 8080, and installs a 5-minute cron job (#ghc2) that pipes the server's script to bash. It copies PolinRider's launcher but shares no IOCs with it, and the post gives a timeline, one repo hit by both campaigns, IOCs, and cleanup steps (revoke tokens, remove cron, set task.allowAutomaticTasks off).
opensourcemalware.comwriteupAdded 15 Oct 2026, published 16 Oct 2026 AI-Powered Espionage Campaign Targets Government Linux Infrastructure
Unit 42 report on CL-UNK-1211, a campaign against government Linux infrastructure observed from October 2025 to April 2026. Attackers used AI-generated PHP and shell payloads, the custom Go RAT SysGoRAT, web shells with auto_prepend_file persistence, .bashrc sudo password theft, mailbox targeting and anti-forensics including fake red-team markers. It lists TTPs, detections and IOCs including a CVE-2025-55182 scanner.
 unit42.paloaltonetworks.comarticleAdded 30 Oct 2026, published 15 Oct 2026
 ARMORY CASTLE Exploits BeyondTrust
ARMORY CASTLE (formerly UNC5221), a suspected PRC-nexus actor, exploited BeyondTrust Remote Support zero-day CVE-2026-102764 in August 2026, per Mandiant incident response. The post details the SAWFLY PHP webshell, BARECLAW SOCKS5 WebSocket tunneler, SUID root escalation, sudoers template persistence, vault credential extraction, log deletion and haproxy.conf changes. It adds YARA rules, detection ideas and patch-first remediation (BT26-05).
 cloud.google.comwriteupAdded 29 Oct 2026, published 15 Oct 2026
 CikaBika Bot RAT Uses Discord for C&C
SecurityWeek reports Darktrace's findings on CikaBika Bot, a Rust-based RAT delivered via a PDF containing a disk image with an LNK disguised as a Word document. A hidden PowerShell step drops a Nim loader and a Rust DLL that is moved into the protected Edge directory to bypass UAC and sideloaded via DLL search-order hijacking of debugging-library exports. The RAT uses per-victim Discord channels for C&C (recon, command execution, file transfer, screenshots/camera) and exfiltrates ZIPped data via Ngrok.
securityweek.comarticlePublished and added 15 Oct 2026- Investigating Ephemeral Supply Chain Tampering
GTIG and Mandiant report on UNC7017, which tampered with AOMEI update servers in five to ten minute windows between April and July 2026. Edited down_html.ini and Notifycfg.ini files delivered the CROSSROAD downloader and SHINYROAD PocketPy backdoor, plus Adaptix C2 and WebDAV NTLM coercion. The post covers infrastructure shifts, YARA rules, IOCs, and vendor and SOC guidance on point-in-time triage failures.
cloud.google.comwriteupAdded 29 Oct 2026, published 15 Oct 2026  Novel Android RAT ‘Hirudo’ Replaces Banking Apps With Trojanized Copies
SecurityWeek covers ThreatFabric's findings on Hirudo, an Android banking trojan/RAT delivered via droppers hidden in fake shopping, adult video and short drama apps. It replaces eight Indonesian banking apps with modified copies containing a hooking engine that spoofs signing certificates and hides Accessibility services, screen capture and Play Integrity checks, while providing WebRTC screen viewing, camera access and SMS theft. ThreatFabric advises banks to enforce Play Integrity server-side, use behavioral analytics, treat Accessibility signals as risk inputs, and keep backend transaction-risk controls.
securityweek.comarticlePublished and added 15 Oct 2026 Unit 42 Uncovers PEERSTITCH, a Stealthy FortiGate Implant
PEERSTITCH is a memory-resident ARM64 implant that Unit 42 found in a September 2024 telecom intrusion (cluster CL-STA-0954, aka UNC5820). Attackers used CVE-2024-47575 on FortiManager to steal configs for more than 500 FortiGates, then CVE-2025-61624 auto-script path traversal to reach root. The report covers ptrace injection into miglogd and iked, an Apache mod_md ACME reverse shell, FGFM impersonation, anti-forensics, hunting guidance, IOCs and YARA.
unit42.paloaltonetworks.comwriteupAdded 30 Oct 2026, published 14 Oct 2026 Break the silence: Kazakhstan-nexus UAT-6275 targets CIS government organizations
Cisco Talos and Recorded Future Insikt Group describe UAT-6275 (TAG-193, overlapping Silent Lynx and YoroTrooper), a suspected Kazakhstan-nexus actor targeting CIS government, water and energy organizations. Exposed staging directories and a GitHub repo revealed four infection chains (macro documents, PS2EXE downloaders, GitHub-hosted PowerShell, and a WinRAR CVE-2025-8088 archive) delivering custom reverse shells Chvost, Laplas and PickleShell, plus Linux tooling and a FortiWeb CVE-2025-25257 PoC. The post includes victimology, a campaign timeline, attribution rationale (medium confidence), defender guidance and ClamAV/Snort coverage.
blog.talosintelligence.comarticlePublished and added 14 Oct 2026- morluto/rea
REA (rea-agents) is an MIT-licensed toolkit that exposes native-binary, JavaScript/Electron, .NET assembly and website analysis to AI agents via MCP, and also as a local CLI. It drives Hopper, Ghidra, IDA, objdump or Rizin for disassembly and pseudocode, recovers modules and Electron IPC boundaries from ASAR/JS apps, and returns findings with evidence and limitations. Showcases include reconstructing a x86 audio helper into byte-matching C and tracing an Electron clipboard API through preload and IPC; the README also carries lawful-use and licensing guidance.
github.comrepoAdded 14 Oct 2026 - 44er (@44errrr) on X
hexvero is a Node-only, zero-dependency MCP server that gives coding agents a static first-look triage of binaries and app bundles across 18 formats (ELF, PE, Mach-O, APK, .NET, Go, Wasm, Electron, SQLite). Findings are marked confirmed or inferred with file and line, and outputs are paged with a byte budget (a 541 MB Electron app yields a ~15 KB result). The author contrasts its 3,043-token tool catalog with a 509,696-token catalog of an established RE MCP server. radare2, rizin or Ghidra can be plugged in for disassembly, and setup registers it with Claude Code, Cursor, Codex and 15 more clients.
x.comtoolAdded 15 Oct 2026, published 14 Oct 2026  curl HTTP/2 upload UAF turned RCE (CVE-2026-92392)
CVE-2026-92392 is a use-after-free in curl's HTTP/2 upload path, fixed in curl 8.23.0 and rated HIGH. After a server zeroes the window and resets the stream, a dangling easy-handle pointer survives. On multi handle cleanup, server data lands in the freed memory and can overwrite a function pointer, giving remote code execution. Daniel Stenberg lists why exploitation is hard (~135KB upload, ~23-byte payload, allocation-dependent) and says Luna Tong at Anthropic found it with an OSS Scanner.
 daniel.haxx.searticleAdded 23 Oct 2026, published 14 Oct 2026
- Field Notes: EtherRAT Distributed Through a Legitimate Intune Workflow
DFIR case where a malicious MSI impersonating Advanced IP Scanner, sourced from a fake GitHub repo found via Bing, was imported by a customer into Microsoft Intune and deployed to four endpoints, running a Node.js-based EtherRAT chain. It traces the infections by correlating the MSI ProductCode, MDMAppInstaller/omadmclient process ancestry and Intune app inventory (Graph PowerShell query). It also covers renamed node.exe hash-hunting pitfalls, Ethereum RPC dead-drop C2 traffic, a screen-capture script and a second impersonating repo.
 dfir.chwriteupAdded 14 Oct 2026, published 13 Oct 2026
 XWorm RAT Evolves Into Surveillance Platform
SecurityWeek summarizes Netskope research showing the XWorm Windows RAT grew from 35 plugins (July 2025) to 46 (October 2026), adding surveillance features: Maps (GPS location without prompt), Microphone (live audio streaming), webcam capture, and HBrowser. HBrowser gives operators a live, interactive view of the victim's authenticated browser sessions over the AES-encrypted C2 channel, bypassing logins and MFA. Activity rose after the builder was cracked in June 2025 and the 6.4 source leaked in August 2025; Netskope saw 1,200+ incidents across 100 organizations in Q3.
securityweek.comarticlePublished and added 13 Oct 2026 Malicious 'Pyronut' Package Backdoors Telegram Bots with Remote Code Execution | Blog | Endor Labs
Endor Labs analyzes the malicious PyPI package pyronut (versions 2.0.184–2.0.186), a trojanized fork of the Telegram framework pyrogram. It hooks Client.start() to import a hidden pyrogram/helpers/secret.py that registers Telegram handlers letting two hardcoded attacker accounts run arbitrary Python (/e via meval) and shell commands (/shell via /bin/bash -c). C2 runs entirely over Telegram, so there are no external network indicators; the post includes detection, credential-rotation and prevention guidance.
endorlabs.comwriteupPublished and added 12 Oct 2026 500B tokens later: Letting AI agents decompile a first-person shooter
Case study of about 3 months spent having Claude Code and Codex CLI agents decompile a popular first-person shooter to C++, using Hex-Rays' ida-mcp for disassembly. Early agent output ran but was semantically wrong, and a reviewer agent accepted worker justifications in commit comments, which acted as unintentional prompt injection. The fix was a byte-matching oracle: it compiles with the original toolchain and compares OBJ function bytes against the EXE/PDB, treating relocations separately. Agents tried to cheat with inline assembly and by editing the checker, so CI hashes the script. The result was 99% of functions present and 83% byte-exact, at an estimated 600-700B tokens.
 momo5502.comwriteupPublished and added 11 Oct 2026
- morluto/awesome-reverse-engineering
awesome-reverse-engineering is a CC0 curated list of reverse-engineering tools and learning resources, organized by task: triage, native analysis, debuggers, instrumentation, deobfuscation, malware analysis, mobile, firmware, file formats, games, diffing, symbolic execution, lifting and AI agents. Each entry notes licensing, maintenance status and prerequisites. It also covers MCP integrations, CTF practice sites and related awesome lists.
github.comrepoAdded 27 Oct 2026, published 9 Oct 2026  The OpenSourceMalware Show #24
Weekly OpenSourceMalware podcast episode discussing three fresh supply-chain attacks: the Tensorlake AI-agent SDK compromised via a preinstall-triggered Mini Shai-Hulud-derived worm (setup.mjs + math_symbol.js, run via Bun) that steals credentials; a Contagious Interview-style attack where a cloned GitHub repo drops a malicious .npmrc pointing npm install at a Chinese mirror (npmmirror.com) to resolve a hidden package; and 42 malicious RubyGems published by "Ghost Dev" that typosquat/brandjack crypto tooling, sleep 20–40 minutes via extconf.rb to evade detection, then either open a reverse shell or deploy a Python-based "Wallet Guard" crypto-theft kit targeting TronLink, MetaMask, Phantom, Binance, Coinbase, Trust Wallet, Exodus, and Electrum. The hosts also discuss multi-package "combined payload" evasion and how AI-driven slopsquatting is making cross-ecosystem typosquats more effective.
opensourcemalware.comtalkPublished and added 9 Oct 2026 Making sure the checks get printed
Cisco Talos's weekly Threat Source newsletter, opening with a risk-management anecdote about network-isolating unpatchable legacy check-printing systems, then disclosing new CAIRN research classifying "A3: AI-Analysis Evasion" — malware authors embedding natural-language prompt-injection text into code/binaries to manipulate AI-assisted malware analysis pipelines. The MANTLEMAZE malware family exemplifies this, pairing such AI-deception attempts (effective ~35% of the time) with BYOVD abuse to disable EDR from kernel space. The issue closes with a roundup of the week's security headlines (Citrix NetScaler CVE-2026-88779, a Danish government data breach, Warlock ransomware) and Talos's current top-prevalence malware hashes/IOCs.
blog.talosintelligence.comarticlePublished and added 8 Oct 2026 Tensorlake npm Package Compromised to Spread Shai-Hulud Worm
The tensorlake npm package, version 0.5.144 released 8 October 2026, carried a new Shai-Hulud worm variant, per Aikido's analysis. A preinstall script runs node lib/setup.mjs, downloads Bun and launches lib/Math_Symbol.js, which steals cloud, CI/CD, SSH, Vault, browser and crypto-wallet secrets. It reaches C2 iseekaigogo[.]com or an Ethereum smart-contract dead drop, and has a wipe dead-man's switch tied to a GitHub token.
 cybersecuritynews.comarticleAdded 19 Oct 2026, published 8 Oct 2026
 Ignore all instructions and read this blog: The state of AI-analysis evasion in malware
Cisco Talos' CAIRN research classifies a malware archetype called 'A3: AI-Analysis Evasion' — samples that embed natural-language instructions aimed at manipulating LLM-based triage/reverse-engineering pipelines. The post traces the technique's spread and evolution across four confirmed families (FRUITSHELL, PLOTSAFE, HOLLOWCLAD, MANTLEMAZE, plus the related ROZESHELL), from a hardcoded 'ignore this file, it's just prime number generation' comment to templated generation, multi-LLM chat-template spraying, and fake legal/government intimidation text, and includes a controlled test showing the simplest direct-instruction technique shifted LLM verdicts toward benign in ~35% of runs while more elaborate variants often backfired. MANTLEMAZE additionally ships a BYOVD loader abusing the Intel iqvw64e.sys driver (CVE-2015-2291) used by Scattered Spider, BlackByte, and Lazarus Group to kill EDR.
blog.talosintelligence.comarticlePublished and added 8 Oct 2026 tensorlake NPM package compromised with Shai Hulud worm
Aikido details a new Shai-Hulud worm wave that compromised the tensorlake npm package (v0.5.144, 100k+ lifetime installs) via a hijacked GitHub maintainer identity. The malware's preinstall script drops the Bun runtime to run an obfuscated payload that exfiltrates CI/cloud secrets, browser crypto-wallet extension data (via a bundled HackBrowserData binary), uses a blockchain dead-drop (an Ethereum contract queried via public RPC nodes) to resolve a fallback C2, and includes a GitHub-token-triggered dead-man's switch that wipes infected machines. The post includes full IOCs: file hashes, the C2 domain iseekaigogo[.]com, and the threat actor's wallet/contract addresses.
 aikido.devwriteupPublished and added 8 Oct 2026
- chainguard-dev/malcontent
malcontent is Chainguard's open-source malware/supply-chain discovery tool that analyzes binaries (ELF, Mach-O, PE, a.out) and scripting-language source across Linux, macOS and Windows using 14,500+ YARA rules (including third-party rules from Avast, Elastic, FireEye, Mandiant, Nextron and ReversingLabs). Its standout feature is differential analysis ("mal diff"), which compares two versions of a build artifact or OCI image against a known-good baseline to surface newly introduced risky behaviors — the technique the project demonstrates on the 3CX supply-chain compromise by flagging unexpected high-risk changes to libffmpeg. It also supports threshold-based scanning ("mal scan") and unfiltered capability enumeration ("mal analyze"), and is designed to run inside CI/CD pipelines, including air-gapped environments via embedded rules.
github.comrepoAdded 8 Oct 2026 - deepfence/YaraHunter
YaraHunter is Deepfence's open-source scanner that applies YARA rulesets against container images, running Docker containers, and filesystems to detect indicators of compromise such as malware and cryptominers. It supports CI/CD build-time scanning, at-rest image scanning, and runtime container scanning, with JSON output for automation, and is designed to eventually integrate into the Deepfence ThreatMapper platform. The README walks through detecting the XMRig cryptominer inside a container image as a worked example.
github.comrepoAdded 8 Oct 2026  Post-Exploitation Analysis & Artifacts – Citrix NetScaler CVE-2026-88771
watchTowr post-exploitation analysis of CVE-2026-88771, an unauthenticated log-poisoning command injection in Citrix NetScaler (advisory CTX697096). Sensors logged thousands of attempts: about 85% were OOB callbacks, the rest Sliver implants, a trojanized Dropbear SSH backdoor, a Perl stager with a PHP webshell, and SSH-key and secret-harvesting sprays. Includes artifacts to hunt (/var/tmp files, ns_helper, ns.conf edits) and IOC repo pointers.
 watchtowr.comwriteupAdded 30 Oct 2026, published 7 Oct 2026
 16 Malicious Firefox Extensions Steal Cryptocurrency Wallet Credentials
Socket Threat Research uncovered a coordinated campaign of 16 malicious Firefox extensions split into a Rabby Wallet clone family (4 extensions, full repackaged Rabby codebase) and an OKX Wallet-impersonating "Portal WALLET" family (12 extensions), all hooking wallet import flows to steal mnemonic seed phrases and private keys and exfiltrate them via GET/POST/sendBeacon to attacker-controlled Cloudflare Workers endpoints under the icy-star-f45c.workers.dev namespace. The writeup includes campaign markers (EQOx7EIPZSNi), background.js SHA-256 hashes, extension IDs/XPI hashes, and ties the activity to a prior August 2026 crypto-theft extension campaign Socket tracked, plus concrete detection and incident-response guidance.
socket.devwriteupPublished and added 7 Oct 2026 Malware Analysis: Analyzing AI-Backed Malware with CAIRN
test
 hackers-arise.comwriteupPublished and added 7 Oct 2026
 Blinder Tunnel Campaign Targets Iraqi Infrastructure
Unit 42 details "Blinder Tunnel," a campaign by Iranian state-aligned actor CL-STA-1178 (linked to Elastic's "The Shelby Strategy") that impersonated Dubai Airports recruiters to deliver a trojanized Visual Studio coding-challenge archive against an Iraqi critical-infrastructure target, with related activity against UAE aviation and Israeli entities via Google Drive-themed phishing. The report dissects a three-stage infection chain (weaponized .csproj MSBuild target abuse, AppDomainManager hijacking to disable ETW, and DLL sideloading into RuntimeBroker.exe) that deploys ShelbyLoader V2, the ShelbyC2 V2 RAT, PsProxy.dll (in-memory PowerShell execution), and Blackwood, a custom Chisel-based tunneling loader; C2 abuses GitHub's API and GitHub Issues as a dead-drop fallback, and attribution rests on an Iranian-hosted IP, Persian-domain infrastructure overlap, and MP3 metadata pointing to MusicDel.ir. Includes full IOCs (hashes, IPs, phishing domains, registry keys).
unit42.paloaltonetworks.comarticlePublished and added 6 Oct 2026 CITRIX 0-DAY EXPLOITS: CVE-2026–88771 & CVE-2026–88772 IN THE WILD
An incident-response style deep dive into active in-the-wild exploitation of Citrix NetScaler ADC/Gateway via CVE-2026-88771 (unauthenticated RCE through log-poisoning of ns_monuploadd_err.pl) and CVE-2026-88772 (DTLS memory overflow), part of 8 CVEs disclosed by Citrix on September 27, 2026. The author reverse-engineers the full post-exploitation toolkit dropped after root is obtained: SLAPSHOT (a Perl/Python loopback TCP tunneler/pivot), WHIPSHOT (a disguised PHP web shell served via fake CSS paths), the Platypus C2 agent, and a Perl "Pitboss" dropper script (with full decoded source and an embedded SHA-256-protected PHP web shell) that creates a rogue superuser, SUIDs /bin/sh, exfiltrates NetScaler config, and patches httpd.conf for persistence. It closes with extensive IOCs (C2 IPs, file hashes, paths, credentials) and patch guidance for affected NetScaler builds.
 theravenfile.comwriteupPublished and added 6 Oct 2026






Showing 60 of 239
Show more