Skip to content

30 results for β€œBurp”

What you seeeverything
portswigger.netcourseπŸ›‘οΈ Security

Web Security Academy

Web Security Academy is PortSwigger's free online web security training. It is known to combine learning material with hands-on labs across web vulnerability classes such as SQL injection, XSS, SSRF, authentication flaws and request smuggling, and to be built around Burp Suite. The page had no extractable text, so this description comes from the URL and general knowledge of the site.

Burp Suite
PortSwigger

Learning, AppSecΒ· Added 30 Oct 2026

portswigger.netcourseπŸ›‘οΈ Security

Web Security Academy: Free Online Training from PortSwigger

The Web Security Academy is PortSwigger's free online training center for web application security. It combines written topic explanations, videos and interactive labs, with content from PortSwigger's research team and Dafydd Stuttard, author of The Web Application Hacker's Handbook. Labs can be solved with Burp Suite Community Edition, progress is tracked per account, and first solvers of new labs appear in a Hall of Fame.

Burp Suite
Dafydd StuttardThe Web Application Hacker's HandbookPortSwigger+1

Learning, AppSecΒ· Added 30 Oct 2026

x.comtool🧠 AI

Dan Kornas (@DanKornas) on X

jshook is an open-source (AGPL-3.0) MCP server that gives AI agents a search-first, profile-aware reverse-engineering workspace for JavaScript, browser traffic, WASM and native processes. Agents start with a small searchable tool surface and move to workflow or full profiles only when needed. It drives Chromium or Camoufox over CDP, captures WebSocket traffic, has HTTP, GraphQL and Burp Suite helpers, and supports hot-reload plugins and declarative workflows. The post is a short announcement; the repository link is in a reply.

Model Context ProtocolJavaScriptWebAssembly+6
jshookDan Kornas

mcp, agentsΒ· Added 28 Oct 2026, published 25 Oct 2026

x.comtoolπŸ›‘οΈ Security

Dan Kornas (@DanKornas) on X

jshook is an open-source (AGPL-3.0) search-first reverse-engineering workspace for AI agents, exposed over MCP. It drives Chromium or Camoufox through CDP, captures WebSocket traffic, offers HTTP, GraphQL and Burp Suite helpers, deobfuscates JavaScript, rebuilds source maps and disassembles WebAssembly. Tool profiles start small and expand to workflow or full sets; hot-reload plugins and declarative workflows extend it.

Model Context ProtocolBurp SuiteChrome+3
CamoufoxCDP

Malware & RE, AI Security, Offensive SecurityΒ· Added 28 Oct 2026, published 25 Oct 2026

aws.amazon.comarticleπŸ›‘οΈ Security

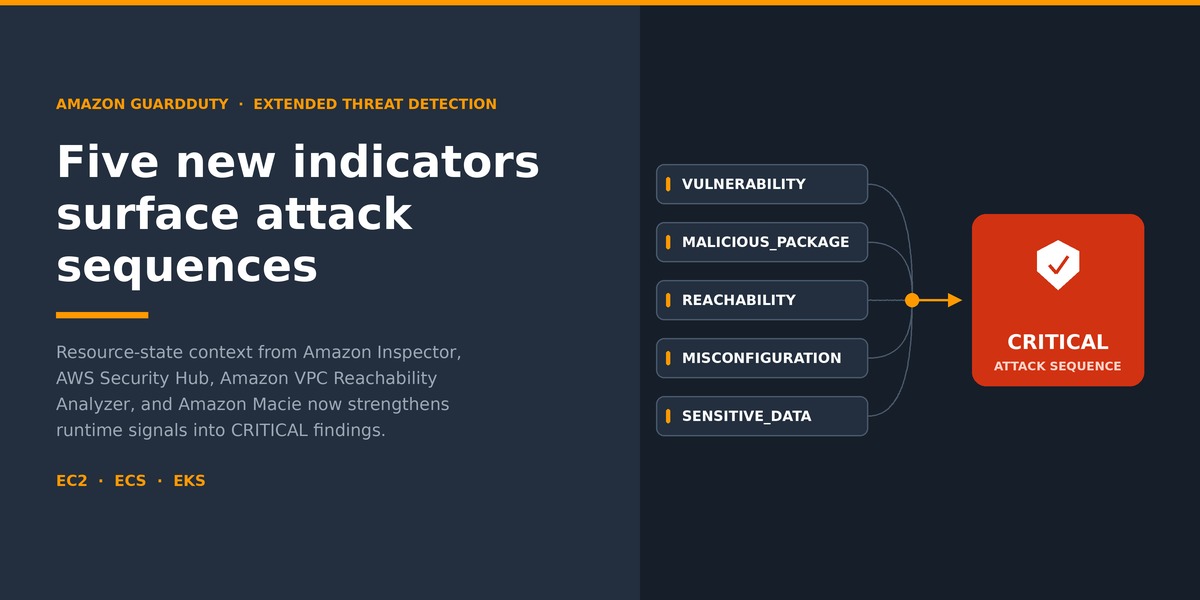
GuardDuty Extended Threat Detection has added five new indicators to surface attack sequences

Explains five new indicator types (MALICIOUS_PACKAGE, MISCONFIGURATION, REACHABILITY, SENSITIVE_DATA, VULNERABILITY) that GuardDuty Extended Threat Detection attaches to attack sequence findings, sourced from Inspector, VPC Reachability Analyzer, Macie and Security Hub. Walks through an EKS compromise (AttackSequence:EKS/CompromisedCluster) that only became a CRITICAL finding thanks to the new context, and a cryptomining EC2 case. Lists observed CVEs with EPSS scores, frp/Burp Collaborator artifacts, and response advice such as EPSS-weighted patching, isolating reachable hosts and rotating IAM credentials.

Amazon GuardDutyAmazon InspectorAWS Security Hub+5
CVE-2022-1471CVE-2024-4577CVE-2024-34351+13

Cloud & Infra, Blue Team & DetectionΒ· Published and added 12 Oct 2026

github.comrepoπŸ›‘οΈ Security

https://github.com/akha-security/akca

AKCA is an open-source, Go-based Dynamic Application Security Testing (DAST) scanner that combines HTTP and headless-browser crawling, JavaScript/AST analysis, API spec import (OpenAPI, GraphQL, gRPC, etc.), and adaptive active testing across a very broad set of vulnerability classes including SQL injection, XSS, SSRF, IDOR/BOLA, SSTI, JWT/OAuth flaws, race conditions, and cloud/CI exposure. It emphasizes evidence-oriented verification β€” replaying promising signals against baselines, negative controls, and OAST callbacks before promoting them to findings β€” and exports Burp-style HTTP evidence in HTML, JSON, CSV, Markdown, and SARIF reports. Positioned as a transparent, single-developer alternative inspired by but not claiming parity with Acunetix, Invicti/Netsparker, or Burp Suite Professional.

GoBurp SuiteSARIF+3
IDORBOLASSRF+1

AppSecΒ· Added 2 Oct 2026, published 23 Sep 2026

github.comrepoπŸ›‘οΈ Security

PortSwigger/http-terminator

http-terminator is PortSwigger's AI-assisted research pipeline for finding and exploiting HTTP request-smuggling and response-desynchronization vulnerabilities. It chains four stages: seeker extracts desync vectors from RFCs and URLs, flamer generates malformed test cases, validator checks candidates against a live target via Burp Suite, and investigator exploits, confirms, and reports findings. Released under AGPL-3.0 as a reference companion to the underlying research, with explicit warnings to only run against authorized targets.

Burp SuiteSQLite

AppSec, Offensive Security, AI SecurityΒ· Added 18 Sep 2026

github.comrepoπŸ›‘οΈ Security

GhostJS

GhostJS is an open-source Burp Suite extension by TrinetLayer that passively scans JavaScript, HTML, and JSON responses flowing through Burp for hardcoded secrets (AWS/GCP/Azure keys, Stripe/PayPal/GitHub tokens, JWTs, private keys, etc.) and hidden API endpoints, surfacing findings in a dedicated tab with severity, confidence scoring, remediation guidance, and Markdown export. It also actively fetches referenced <script> bundles using the tester's live session cookies and applies a false-positive filter to suppress doc-sample and placeholder keys, making it a practical recon aid during authorized web app pentests and bug bounty work.

Burp SuiteJavaScriptJava
TrinetLayer

AppSec, Offensive SecurityΒ· Published and added 7 Sep 2026

github.comrepoπŸ›‘οΈ Security

Awesome Cybersecurity Agentic AI

A curated GitHub awesome-list cataloging the emerging agentic-AI security ecosystem: dozens of Model Context Protocol servers that give LLM agents access to security tools (Nuclei, Shodan, VirusTotal, Burp Suite, Ghidra, BloodHound, x64dbg), autonomous penetration-testing and CTF-solving agent frameworks (CAI, pentagi, BreachSeek, Dark-Moon, D-CIPHER), scanners/guardrails that audit agent skills, MCP servers, and multi-agent chains for prompt injection and other risks (Aguara, Inkog, MCP Doctor, AI-Infra-Guard, ATR), agentic SOC/detection platforms (Vigil), threat-modeling frameworks for agentic systems (MAESTRO, ATFAA/SHIELD), research papers, benchmark datasets, and community/learning resources. It functions as a living index for anyone building or defending AI-agent-driven security tooling.

Model Context ProtocolLangChainCrewAI+3
OWASP Top 10 for LLM ApplicationsEU AI ActOWASP FinBot CTF+1

AI Security, Offensive Security, Blue Team & DetectionΒ· Added 3 Sep 2026, published 31 Aug 2026

intigriti.comarticleπŸ›‘οΈ Security

Web Fuzzing for Hackers

A practical guide to web fuzzing for bug bounty hunters, covering wordlist selection (custom vs. SecLists-style generic lists), and tool-specific configuration for content discovery, subdomain/VHost enumeration, and parameter/header discovery using ffuf, Burp Suite Intruder, OWASP Amass, dnsx, Arjun, and Param Miner. It details concrete techniques such as subdomain permutation patterns, extension fuzzing for leftover files (.md, .env, .sql), dotfile/prefix patterns (/.FUZZ, /-FUZZ, /~FUZZ), IIS-specific extensions (.asmx, .ashx, .aspx.bak), and hidden-header fuzzing (X-Forwarded-For, X-Debug, X-HTTP-Method-Override) that can lead to SQLi, cache poisoning, or access-control bypass.

Burp SuiteIIS
SecListsAssetnote

AppSec, Offensive SecurityΒ· Added 3 Sep 2026, published 21 Aug 2026

github.comrepoπŸ›‘οΈ Security

Teycir/BurpAPISecuritySuite

BurpAPISecuritySuite is a Jython-based Burp Suite extension that consolidates API reconnaissance, intelligent fuzzing (108+ payloads across 15 attack types including BOLA, IDOR, JWT exploitation, GraphQL abuse, SSTI, and WAF bypass), and passive deep-logic checks (counterfactual differentials, sequence invariants, token lineage, cross-interface parity drift) into a single tool covering the OWASP API Top 10. It auto-captures and normalizes API traffic, exports attack campaigns to Burp Intruder/Turbo Intruder/Nuclei, and generates AI-ready bundles (ChatGPT/Claude/Ollama) for LLM-assisted triage, while orchestrating external tools like ApiHunter, Katana, httpx, FFUF, Kiterunner, sqlmap, and Dalfox for verification.

Burp SuiteNucleiGraphQL+3
IDORBOLA

AppSec, Offensive SecurityΒ· Published and added 21 Aug 2026

portswigger.netarticleπŸ›‘οΈ Security

HTTP Terminator: Can AI Invent New Attack Techniques? (James Kettle, PortSwigger)

PortSwigger's Director of Research James Kettle built the HTTP Terminator, an autonomous system that automates his own research process (ideation, evaluation, weaponization, cascade) to invent novel HTTP attack techniques, extending his four years of HTTP desync research. The system parsed 138 technical specs into 15,000 inspiration fragments, generated 30,000 unique attack vectors, tested them against live bug-bounty targets, and confirmed roughly 700 vulnerable targets spanning government, financial, and enterprise infrastructure. Kettle found human intuition remained decisive at the "discovery cascade" stage where one finding seeds the next hypothesis, and he has released the HTTP Terminator's source code and a methodology blueprint alongside the full technical paper presented at Black Hat USA; PortSwigger contrasts it with its commercial Burp AT agent.

Burp Suite
James KettleHTTP TerminatorBurp AT+3

AI Security, Offensive Security, AppSecΒ· Added 21 Sep 2026, published 12 Aug 2026

github.comrepoπŸ›‘οΈ Security

Cariddi

Cariddi is a Go-based CLI tool that crawls a list of domains/URLs to discover endpoints, secrets, API keys, tokens, and juicy file extensions. It supports proxying through Burp Suite, custom headers, secret/endpoint regex files, JSON/HTML/TXT output, and configurable crawl depth and concurrency, making it a common recon tool in bug bounty and pentest workflows.

CariddiGoBurp Suite

Offensive Security, OSINTΒ· Added 3 Sep 2026, published 12 Aug 2026

portswigger.netwriteupπŸ›‘οΈ Security

Can AI Do Novel Security Research? Meet the HTTP Terminator

PortSwigger research paper on the 'HTTP Terminator', an autonomous LLM-driven pipeline (hypothesis generation from RFC micro-inspiration, live evaluation via a Burp Suite/SQLite harness against 30,000+ targets, and weaponization through an MCP-controlled Turbo Intruder agent) that discovered new HTTP desync triggers and Response Queue Poisoning exploits. It details concrete new techniques (the protocol-ruler recon method, the 'dangling byte' RQP-reliability trick, Response Forking, Status-Line Injection, Range Cache Poisoning) and a major new attack class, Shared Parser Confusion, plus a resulting CVE-2026-63078 zero-day in Apache Traffic Server, and real compromises of banks, an airport admin panel, a Beyond Trust product, a Meta server, and a Citrix NetScaler-based SSO deployment.

Burp SuiteTurbo IntruderModel Context Protocol+2
CVE-2026-63078Orange TsaiF5 Big-IP+3

AppSec, AI Security, Offensive SecurityΒ· Added 18 Sep 2026, published 5 Aug 2026

portswigger.netwriteupπŸ›‘οΈ Security

Can AI do novel security research? Meet the HTTP Terminator (James Kettle)

James Kettle (PortSwigger) built the "HTTP Terminator," an autonomous LLM-driven pipeline (Ideation β†’ Evaluation β†’ Weaponization β†’ Cascade) that generated ~30,000 novel HTTP desync vectors from RFC micro-inspiration, tested them 24/7 across 30,000 live bug-bounty targets via a Burp Suite extension, and weaponized findings with an MCP-wired Turbo Intruder agent to achieve Response Queue Poisoning. The work yielded new desync triggers, a "dangling byte" RQP-reliability technique, a novel attack class ("Shared Parser Confusion"), a patched Apache Traffic Server zero-day (CVE-2026-63078), and confirmed impact on banks, an airport, a US government site, Meta, a Beyond Trust product, and an SSO server behind Citrix NetScaler. It also documents concrete prompt-engineering lessons (micro-inspiration, context-contamination, reality-reframing an over-cautious agent) for building autonomous AI security research systems.

HTTP TerminatorBurp SuiteTurbo Intruder+3
CVE-2026-63078Orange TsaiHTTP Desync Attacks+14

AppSec, AI Security, Offensive SecurityΒ· Added 18 Sep 2026, published 5 Aug 2026

github.comrepoπŸ›‘οΈ Security

Awesome Android Reverse Engineering

A curated GitHub list covering the full Android reverse engineering toolchain: decompilers (JADX, Apktool, Ghidra, IDA Pro), dynamic instrumentation (Frida, Objection, FriDump, jnitrace), deobfuscation tools (Simplify, Obfu[DE]scate, deoptfuscator), network interception (Burp Suite, MITMProxy, SSLsplit), anti-tamper/root-detection bypass tooling, and malware analysis frameworks (MobSF, Quark Engine, Cuckoo Droid). It also links training courses (Maddie Stone's RE training, Azeria Labs ARM assembly), books (Android Hacker's Handbook, Android Security Internals), and CTF/practice targets (UnCrackable Mobile Apps, KGB Messenger, Flare-On).

AndroidFridaGhidra+3
SharkBotHouseparty

Mobile Security, Malware & RE, LearningΒ· Published and added 5 Aug 2026

github.comrepoπŸ›‘οΈ Security

Hetty

Hetty is an open-source HTTP toolkit for security research written to be a free alternative to Burp Suite Pro, aimed at infosec and bug bounty practitioners. It provides a machine-in-the-middle HTTP proxy with searchable logs, a manual HTTP client for crafting/editing/replaying requests, request/response interception for manual review, project-based scoping, and a web-based admin UI backed by a GraphQL API, distributed via Homebrew, Scoop, Snap, and Docker.

Burp SuiteDockerGraphQL+3

Offensive SecurityΒ· Added 3 Sep 2026, published 31 Jul 2026

medium.comarticleπŸ›‘οΈ Security

Claude as Autonomous Bug Bounty Hunter

Author describes Aii-Aii Hunter, a bug bounty framework built on Claude Code with 124 markdown skills (35.5k lines distilled from public HackerOne reports), three hooks (UserPromptSubmit regex auto-routing, PreToolUse scope.json guard, PostToolUse telemetry) and a Podman Kali container exposing 110 tools plus 18 Burp tools over MCP. It also covers an engagement flow with a 7-Question validation gate, evidence hygiene, an autopilot mode, and SAST/DAST correlation. Useful as a blueprint for scoped, AI-orchestrated offensive workflows; first of six parts with a companion repo.

Claude CodeModel Context ProtocolKali Linux+3
Aii-Aii Hunter7-Question Gatescope guard

Offensive Security, AI Security, AppSecΒ· Added 3 Sep 2026, published 30 Jul 2026

github.comrepoπŸ›‘οΈ Security

PentesterFlow/agent

PentesterFlow is an open-source terminal AI agent for authorized offensive-security engagements, connecting to local or hosted LLMs (Ollama, LM Studio, Anthropic, Gemini, DeepSeek, Groq, OpenRouter, etc.) to plan and execute recon, enumeration, vulnerability validation, and evidence-backed reporting against a scoped target. It gates sensitive actions behind analyst approval, bridges with Burp Suite for traffic capture/finding import via a local listener and companion MCP server, and maintains persistent project/personal memory (redacting secrets) to carry lessons and coverage state across sessions. The demo walks through discovering and confirming an IDOR on an orders API and writing findings to a local markdown report.

Burp SuiteOllamaModel Context Protocol+3
IDOR

Offensive Security, AI SecurityΒ· Published and added 29 Jul 2026

github.comrepoπŸ›‘οΈ Security

RamanMG/Burp-MCP-Unrestricted

An unofficial fork of PortSwigger's Burp Suite MCP server extension that removes the human-approval prompts before an AI client can send HTTP requests or read captured proxy data, and adds tooling aimed at long unsupervised engagements: newest-first proxy history, site map access, scan/crawl driving, and Repeater automation via direct Swing UI manipulation. It also removes the upstream 5000-character response truncation (configurable via maxLength) that could otherwise hide large findings like stack traces or GraphQL introspection dumps from an agent.

Burp SuiteModel Context ProtocolClaude Desktop+1

Offensive Security, AI SecurityΒ· Published and added 29 Jul 2026

github.comrepoπŸ›‘οΈ Security

1N3/Sn1per

Sn1per is an open-source Community Edition offensive-security platform that automates reconnaissance, vulnerability scanning, and exploitation by orchestrating 90+ third-party tools such as Nmap, Metasploit, Burp Suite, and Nessus into unified scan modes (normal, stealth, discover, airstrike, nuke). It ships with 600+ exploits and 10,000+ detections, supports Docker deployment, workspace-based loot management, and scheduled scans for external attack surface management. Paid Professional and Enterprise tiers add a web UI, reporting exports, and a JSON API on top of the same source-available CLI scanning engine.

Sn1perNmapMetasploit+3

Offensive Security, OSINTΒ· Published and added 26 Jul 2026

github.comrepoπŸ›‘οΈ Security

BountyForge

BountyForge is a Claude Code skill that spins up 8 specialized agents in parallel to hunt for vulnerabilities across web/API, smart contracts (EVM, Move, Solana, TRON), infrastructure, and supply-chain targets, then deduplicates and runs findings through a four-gate validation pipeline (Refutation, Reachability, Trigger, Impact) before CVSS-scoring them into submission-ready HackerOne/Bugcrowd/Intigriti/Immunefi reports. It orchestrates local tools (nmap, ffuf, sqlmap, amass, ZAP, Burp Suite) when Claude Code execution is enabled, integrates with a companion `bug-bounty-intelligence-mcp` MCP server for Solidity scanning via "Al-Mizaan v3" 7-gate deep validation, and also offers a paid Firecracker-microVM cloud version at bountyforge.xyz.

Claude CodeModel Context ProtocolSolidity+3
IDORSSRFAl-Mizaan v3+1

Offensive Security, AI Security, AppSecΒ· Published and added 22 Jul 2026

github.comrepoπŸ›‘οΈ Security

dinosn/fastjson-jsontype-rce-lab

A dual-track research lab reconstructing Fastjson RCE chains: a legacy JDK 8 direct-remote-class JSONType RCE for Fastjson 1.2.83, and a modern JDK 17 retained-JAR via proc-self-fd composition that works even with AutoType disabled and DTO binding in place, exploiting how ParserConfig.checkAutoType probes every type value via getResourceAsStream. It also reproduces an independent fastjson2 2.0.57/2.0.62 autoType bypass disclosed by Chaitin, where ObjectReaderSeeAlso hardcodes SupportAutoType, letting seeAlso/JsonSubTypes/sealed-type modeling trigger remote class loading even with autoType disabled. The repo ships dependency-free Python scanner tools for passive log detection, static artifact inventory, and safe active reachability probing via Burp Collaborator or interactsh.

Fastjsonfastjson2Java+3
CVE-2022-25845FearsOffKirill Firsov+1

AppSec, Offensive SecurityΒ· Added 2 Oct 2026, published 20 Jul 2026

github.comrepoπŸ›‘οΈ Security

Reverse-Skill

Reverse-Skill is a GitHub repo that gives AI coding agents (Claude Code, Codex, Cursor, OpenCode) a structured routing layer for reverse engineering and offensive security work: it detects the task type (APK, ELF binary, JS obfuscation, PCAP, CTF challenge) and routes to the correct methodology and toolchain (jadx, apktool, Frida, IDA Pro, Ghidra, radare2, Burp Suite, nmap, Metasploit) instead of letting the agent guess commands. It ships a case-init/scope workflow, an evidence-to-finding-to-report pipeline, a 173-case routing regression test run in CI on Windows and Ubuntu, and platform-specific docs for Kali/Ubuntu/macOS, positioned for lawful research, CTF, and authorized pentesting.

Claude CodeCodexCursor+3

Malware & RE, Offensive Security, Mobile SecurityΒ· Published and added 21 Jun 2026

youtu.bevideoπŸ›‘οΈ Security

Web LLM Attacks Lab: Exploiting AI agents to trigger secondary vulnerabilities

This walk-through demonstrates solving PortSwigger Web Security Academy's 'Exploiting AI agents to trigger secondary vulnerabilities' lab. The attack leverages Burp Suite to discover an internal administrative endpoint via SSRF fuzzing, then plants an indirect prompt injection payload in a public product review to coerce an automated AI site auditor into deleting a target user.

PortSwigger Web Security Academy Lab - Exploiting AI agents to trigger secondary vulnerabilitiesBurp Suite Professional v2024.2.1Burp Intruder+4
PortSwigger Web Security Academy

AI SecurityΒ· Added 3 Oct 2026, published 2 Jun 2026

github.comrepoπŸ›‘οΈ Security

OWASP Noir

OWASP Noir is a static analysis (SAST) tool that reads source code to extract every endpoint an application exposes β€” paths, methods, parameters, headers, cookies, and their originating files β€” across 205 supported frameworks, with an LLM fallback (OpenAI/Ollama) for unsupported ones. The endpoint inventory (including shadow APIs and undocumented routes) is exported as JSON/YAML/OpenAPI/SARIF/cURL/Postman/HTML to feed DAST scanners (ZAP, Burp Suite, Caido, Gori), human security reviewers, and AI SAST auditors, with optional --ai-context enrichment (guards, sinks, validators, callees) and GitHub Action/CI integration.

OWASP ZAPBurp SuiteSARIF+3
OWASP

AppSecΒ· Published and added 24 May 2026

github.comrepoπŸ›‘οΈ Security

CyberStrikeus/CyberStrike

CyberStrike is an open-source (AGPL-3.0) terminal-based framework that turns any LLM subscription (Claude, GPT, Gemini, local models via Ollama/LM Studio, etc.) into an autonomous red-team agent, providing 13+ specialized agents, 7,600+ Ed25519-signed security skill files mapped to OWASP WSTG/CWE, a built-in Chromium proxy browser for role/credential discovery, and remote "Bolt" MCP tool servers for orchestrating tools like nmap, sqlmap, and Burp-style traffic interception. It targets pentesters and bug bounty hunters for automated reconnaissance, vulnerability discovery, exploitation, and post-exploitation, explicitly restricted to authorized testing.

Model Context ProtocolClaude CodeOllama+3

Offensive Security, AI SecurityΒ· Published and added 23 May 2026

github.comrepoπŸ›‘οΈ Security

elementalsouls/Claude-BugHunter

Claude-BugHunter is a Claude Code "Agent Skills" plugin (83 skills, 15 slash commands) that turns Claude into a bug-bounty hunter or external red-team operator, auto-loading skills by topic. It codifies detection patterns and chain templates from 681 disclosed HackerOne reports across 24 core vulnerability classes, plus enterprise perimeter attack chains for M365/Entra ID, Okta, SharePoint (ToolShell), VMware vCenter, and SSL-VPN appliances, with Burp Suite MCP integration, a 7-Question validation gate, and engagement-folder scaffolding for reporting.

Claude CodeBurp SuiteModel Context Protocol+2
ToolShell

Offensive Security, AppSecΒ· Published and added 22 May 2026

github.comrepoπŸ›‘οΈ Security

matty69v/Bug-Bounty-Agents

Bug-Bounty-Agents is a collection of 43 specialized LLM system-prompt personas (recon, web hunting, exploit chaining, reporting, scope-guard, etc.) that turn Claude Code, Copilot Chat, Cursor, or any agent-capable LLM into offensive-security specialists for bug bounty and pentest engagements. It ships an install script that auto-detects and deploys agents to the correct client directories, and documents pairing the agents with PortSwigger's Burp Suite MCP server so an LLM can drive live traffic through Burp while following the repo's methodology.

Claude CodeGitHub CopilotCursor+2

Offensive Security, AI SecurityΒ· Published and added 12 May 2026

github.comrepoπŸ›‘οΈ Security

Titus by Praetorian

Titus is Praetorian's open-source secrets scanner that detects credentials, API keys, and tokens across source code, git history, container images, and binary files using 487 detection rules drawn from NoseyParker and Kingfisher. It combines Hyperscan/Vectorscan-accelerated regex matching with live credential validation (checking secrets against AWS/GitHub/etc APIs) and risk-based severity scoring, and ships as a CLI, Go library, Burp Suite extension, and Chrome extension sharing one detection engine.

GoDockerBurp Suite+3
NoseyParkerKingfisher

DevSecOps, Offensive SecurityΒ· Published and added 10 May 2026