securityweek.comarticle🛡️ Security
Max-Severity GitLab Vulnerability Exploited Against Alpine Linux
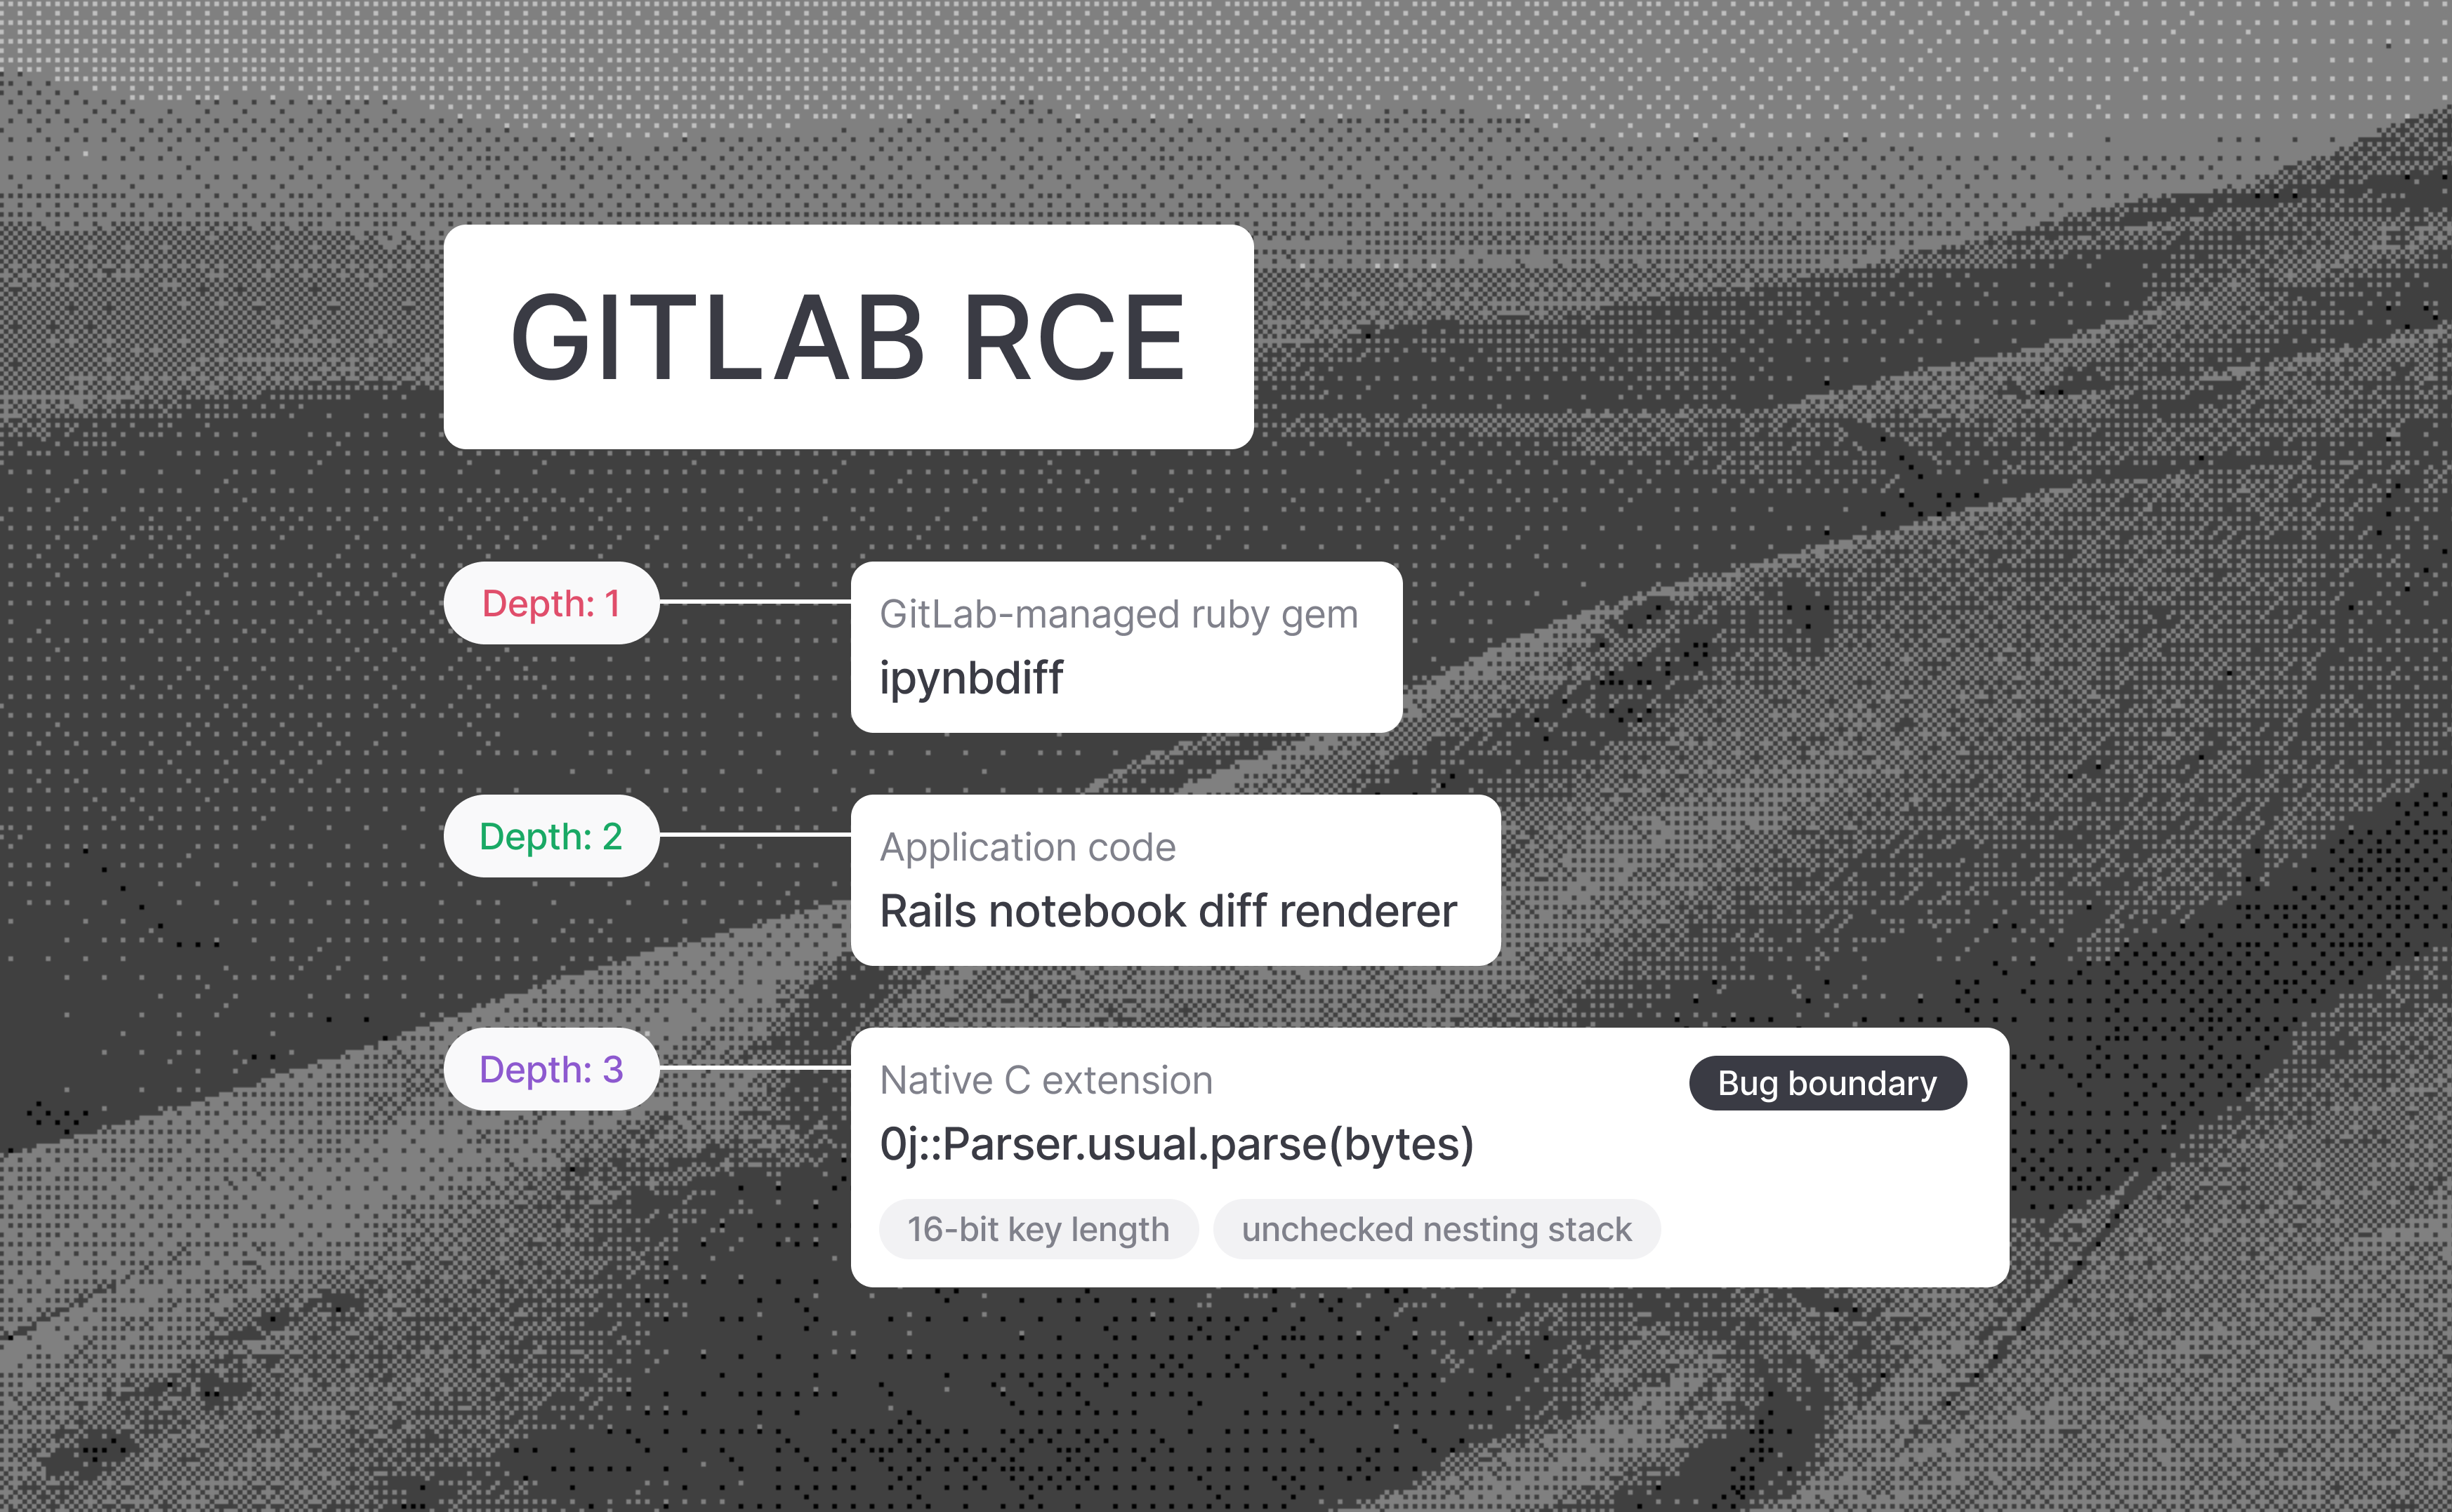
CVE-2026-97229 is a CVSS 10 code execution flaw in Onigmo, Ruby's regular expression engine, reachable through crafted CI/CD configuration in GitLab. Attackers used it against Alpine Linux's GitLab on 20 and 21 October 2026 and failed; Alpine rebuilt the instance and found no tampering with aports or packages. Self-managed installs with their own Ruby need Ruby 3.3.13, 3.4.12 or 4.0.9, not just GitLab 19.3.6. CISA added it to KEV.
GitLabRubyOnigmo+2
CVE-2026-97229CISA KEVBOD 26-04+1
AppSec, Threat Intel, DevSecOps· Published and added 30 Oct 2026