 x.comthread
Dark Web Intelligence (@DailyDarkWeb) on X
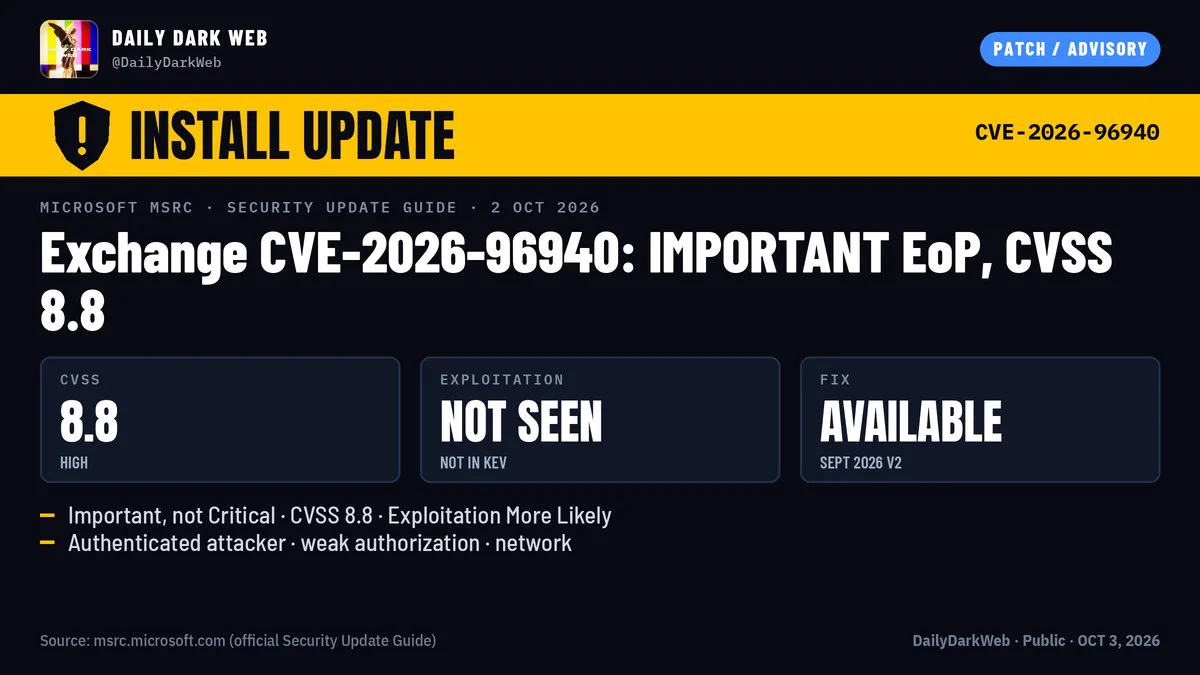
Summary of Microsoft's September 2026 V2 / October 2026 early security updates adding CVE-2026-96940, an Important elevation-of-privilege flaw (CVSS 8.8) in on-prem Exchange Server caused by weak authorization that lets an authenticated attacker escalate privileges over the network. Covers affected builds and KBs (Exchange SE RTM KB5129955, 2019 CU15/CU14 KB5129956/5129957, 2016 CU23 KB5129958) and notes Exchange Online is unaffected, the flaw was found internally by Microsoft with no known exploitation and is not in CISA KEV.
TL;DR CVE-2026-96940: Important (CVSS 8.8) auth-required privilege escalation in on-prem Exchange Server, patched in Sept/Oct 2026 updates, no known exploitation.
CVEs named here
Technologies named here
- Microsoft Exchange Server SE RTM
- Microsoft Exchange Server 2019 CU15
- Microsoft Exchange Server 2019 CU14
- Microsoft Exchange Server 2016 CU23
- Microsoft Exchange Online
- Microsoft Exchange
- CVSS
- CISA KEV
Techniques named here
- Elevation of privilege via weak authorization
Related in AppSec
 github.comadvisory
Flowise MCP Security Bypass Enables RCE

 huntress.comwriteup
Inside an Oracle Database SQL Injection Attack | Huntress
github.comrepoOASIS

 blog.trailofbits.comwriteup