 huntress.comwriteup
Rogue RMMs: Common Social Engineering Tactics We Saw in 2025
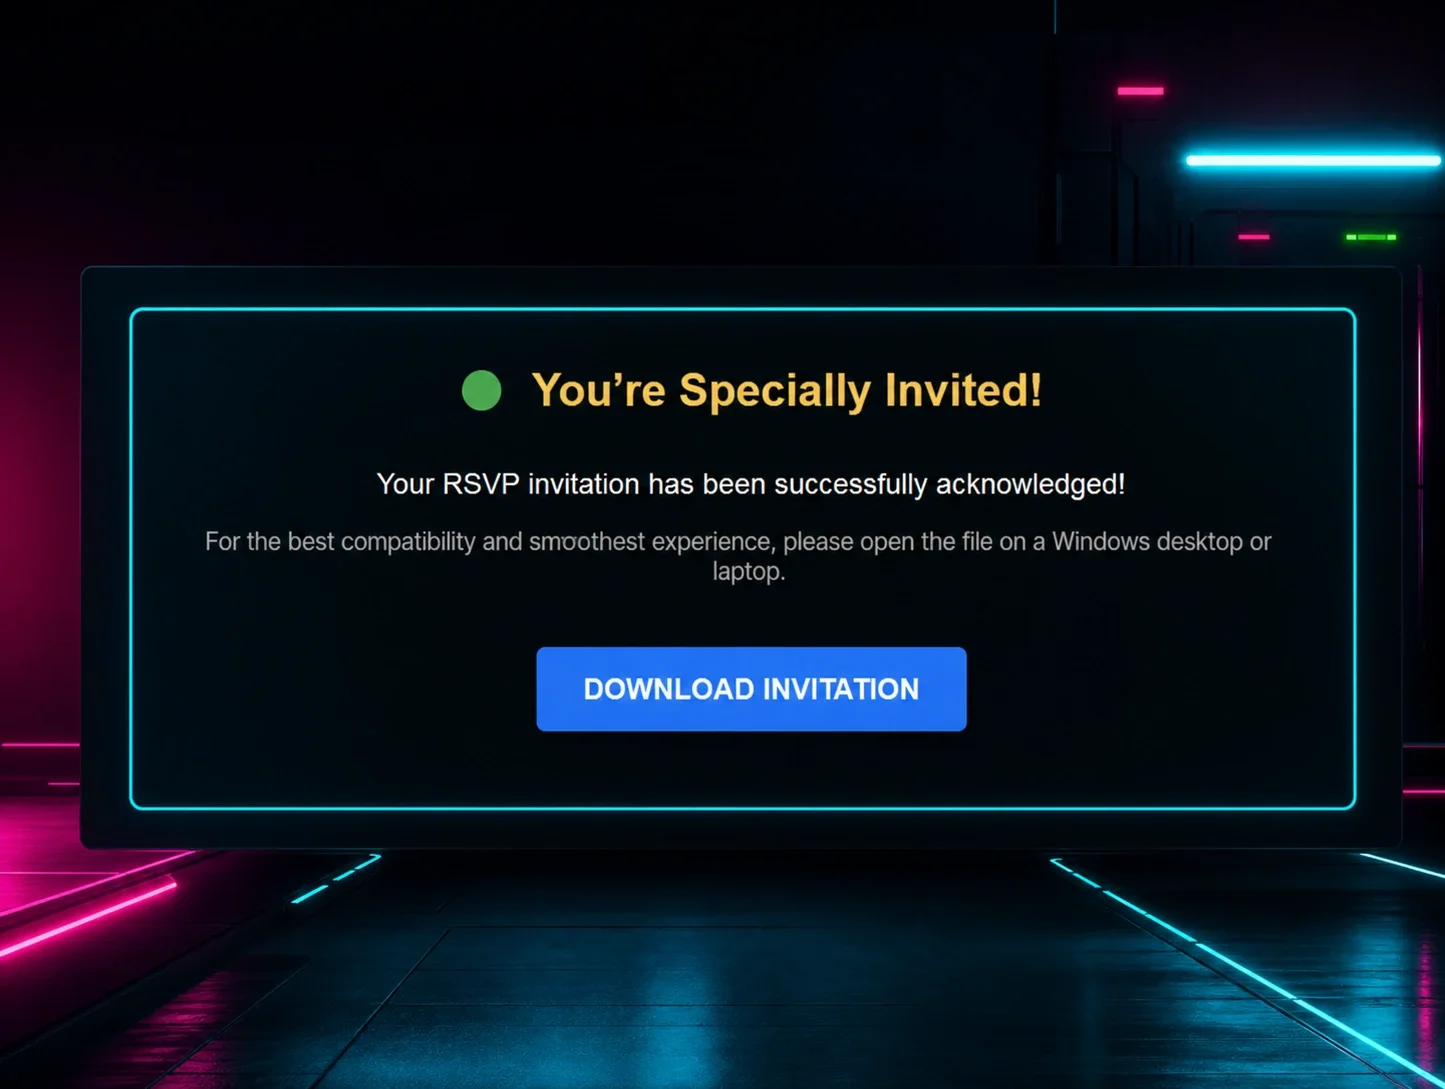
Huntress SOC details a year-long pattern of threat actors social-engineering employees into installing rogue ScreenConnect instances via lures disguised as Social Security statements, event invitations, and overdue invoices. The post shares specific malicious executable names, top C2 domains (lory473[.]top, subjent25.zapto[.]org, sans[.]infosedi[.]de, and others), a notable SHA256 hash, and a walkthrough of an incident where a Google Docs "invitation" page delivered a ScreenConnect installer. ScreenConnect accounts for 74.5% of abused RMMs Huntress observed, with recommendations to audit/monitor RMM usage and review execution logs.
What it is
A Huntress SOC writeup of 2025 social-engineering campaigns that deliver renamed ScreenConnect clients as "rogue RMMs." It goes beyond naming the three lure themes: it lists the actual observed executable filenames and the naming conventions that reveal a disguised ScreenConnect installer, which is the detectable substance the summary omits.
How it works
Attackers phish employees into downloading and running an executable that is a renamed ScreenConnect client. Running it triggers a ScreenConnect installation, giving remote access that blends in with legitimate RMM traffic. The page frames this as one of several RMM-abuse patterns (alongside hijacking already-installed RMMs and directly compromising RMM infrastructure — e.g., ConnectWise's May 28 disclosure affecting "a very small number of ScreenConnect customers"). ScreenConnect, TeamViewer, and LogMeIn are named as abused tools.
Preconditions / Affected
Any environment where employees can download and execute arbitrary binaries. Observed victims span an insurance agency, a real estate developer, and a retail organization — no vertical is exempt. RMM abuse accounted for 17.3% of threat-actor remote-access methods in 2024.
What to do
Detection hinges on the filename tell: disguised clients repeatedly embed ScreenConnect's .Client.exe / .ClientSetup build artifacts inside a lure name. Hunt for executables matching this pattern, especially with these lure themes and observed names:
- Social Security:
Social_Security_Statements_April2025_Updates.Client.exe,Social_Security_Statement_Viewer.exe,Social-S-Statement-May.exe - Event invites:
YourInvite.Clientsetup.exe,accessinvite.ClientSetup(3).exe,special invitation letter(2).exe,RSVPINVITE(1).exe - Invoice/statement:
SSA_Earnings_Statement_2025.pdf.Client.exe,Overdue-invoice.pdf—---DocuSignViewer.Client(1).exe,RevisedStatementJAN2025.exe,Invoice_Overdue.Client.exe
Note the double-extension and .pdf...Client.exe masquerade patterns. Block/alert on unexpected ScreenConnect installs originating from user Downloads. One hash is called out explicitly — SHA256 bdbac9fe9e7aca3a03d55867eddd905c4e222f3045b0015b823df4f034ee007a — tied to INVO-prefixed invoice-lure files whose numeric suffixes varied (so match on the prefix, not the whole name).
Caveats
The fetched text describes but does not reproduce the "top five domains" table or the full SHA256 list — those IoCs live in on-page tables you must open to get. Same-named files often shared one hash, so hash-only detection will miss the variant families; the naming-pattern heuristic is the more durable signal.
Organisations named here
- administrator.pulseriseglobal.com
- lory473[.]top
- rok628.mxhelp.top
- sans[.]infosedi[.]de
- slplegalfinance.com
- subjent25.zapto[.]org
- yoc736.ikhelp.top
Technologies named here
- Huntress Managed EDR
- ConnectWise ScreenConnect
- TeamViewer
- ScreenConnect
- LogMeIn
- RDP
- Atera
- VNC
- NinjaRMM
- Huntress
Techniques named here
- Social engineering via phishing lures
- Social engineering via event invitation lures
- Social engineering via invoice/statement lures
- Use of dynamic DNS services to hide infrastructure
Threat actors named here
- Threat actor behind lory473[.]top campaign
Also named here
- bdbac9fe9e7aca3a03d55867eddd905c4e222f3045b0015b823df4f034ee007a
Related in Threat Intel
 huntress.comwriteup
Reverse Engineering the Six Stages of MacSync Stealer and RAT
 huntress.comwriteup
AI-Coded Malware | Analyzing Vibe-Coded AD Enumeration | Huntress

 blog.talosintelligence.comtool
Introducing CAIRN: Frontier tracking for AI-integrated malware (Cisco Talos)
 huntress.comwriteup