 huntress.comwriteup
Nightmare-Eclipse Tooling Seen in Real-World Intrusion
Test summary.
What it is
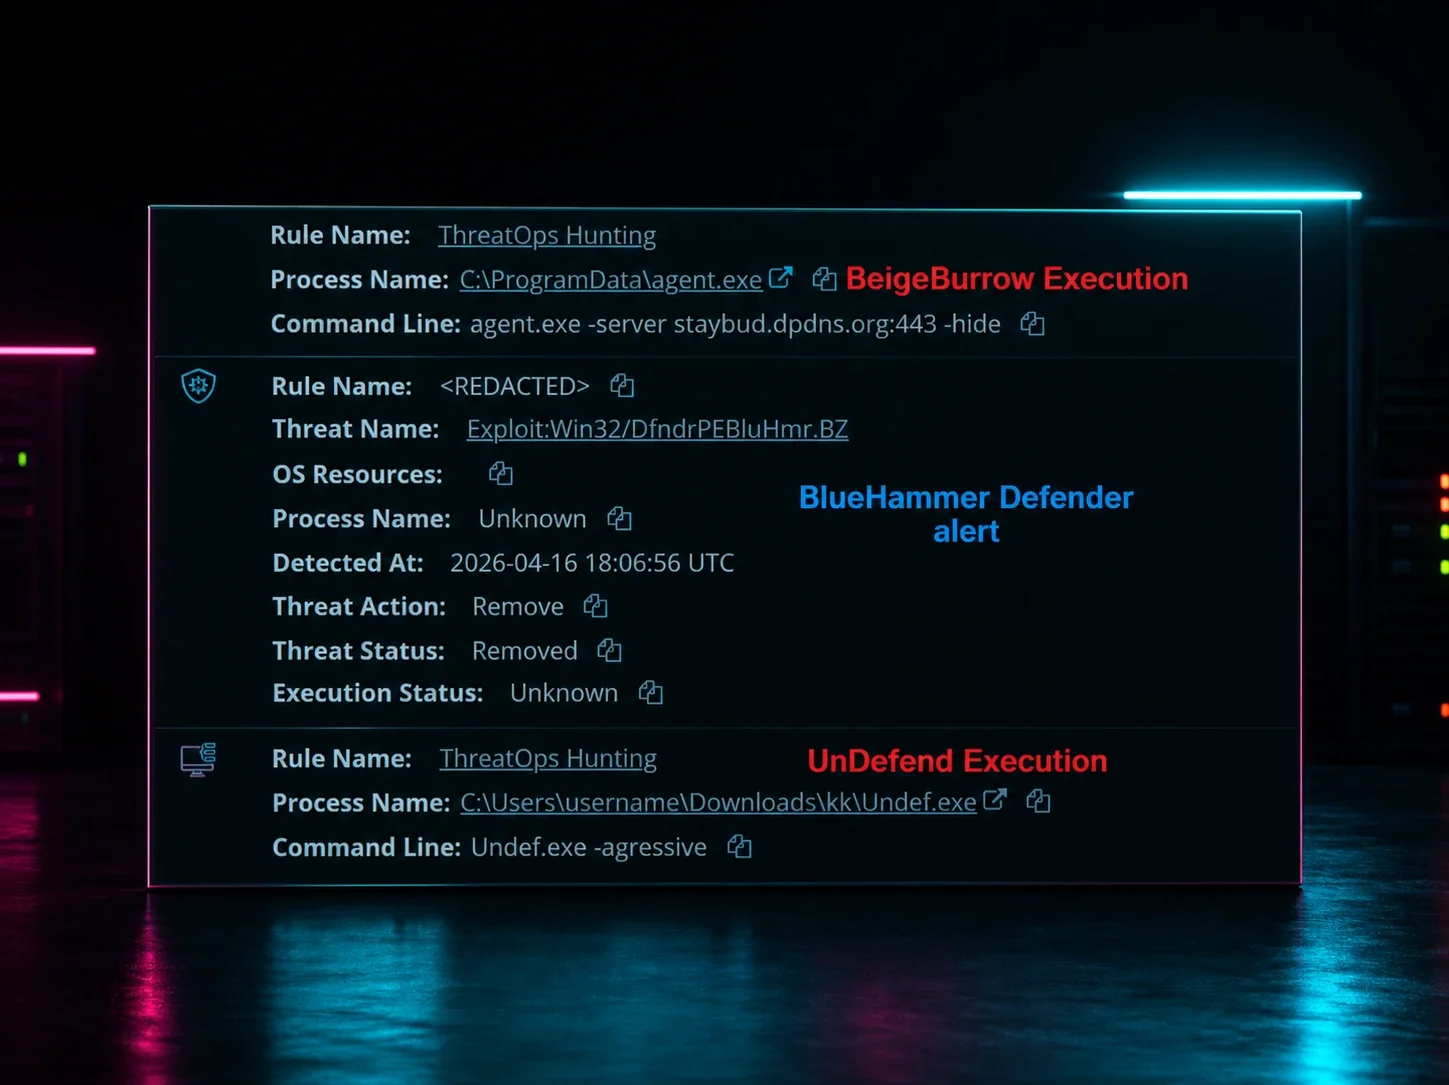
Huntress' write-up (published April 20, 2026) on the "Nightmare-Eclipse" (aka "Chaotic Eclipse") tooling — three Windows local privilege escalation PoCs: BlueHammer (CVE-2026-33825, publicly released April 2, 2026), RedSun, and UnDefend. The author is a researcher who published these after frustration with Microsoft's disclosure handling. The key fact the summary omits: BlueHammer was patched in Microsoft's April 2026 updates, but RedSun and UnDefend remain unpatched as of publication. Huntress assesses both BlueHammer and RedSun can take an attacker from an unprivileged account to SYSTEM.
How it works
All three abuse Windows Defender's interaction with the Volume Shadow Copy system, differing in how they detect the race window:
- BlueHammer and RedSun use oplocks (opportunistic locks) to hold files open and detect when Defender is scanning or remediating — this is their synchronization signal for a TOCTOU (CWE-367) race condition. BlueHammer's second, novel trick has no CWE: it pauses the Defender process while the Volume Shadow Copy is exposed, giving the attacker control over the otherwise-tiny race window and enabling an arbitrary read handle to the SAM database.
- UnDefend instead uses Directory Change monitoring and exploits a benign, necessary system action that produces exclusive file locks — not framed as TOCTOU.
BlueHammer's weaponization begins by polling the Windows Update API for a pending update (page text cuts off here).
Preconditions / Affected
Windows environments with Defender. BlueHammer requires an unprivileged local account (described as "unauthenticated user" reading a sensitive location). BlueHammer's own escalation stage targets currently logged-out users on the host. RedSun and UnDefend have no patch available.
What to do
The page's stated actions:
- Review VPN logs — Huntress tied the intrusion to suspicious FortiGate SSL VPN access, including a source IP geolocated to Russia and additional suspicious infrastructure in other regions.
- Investigate the artifacts and paths listed in the blog (suspicious binaries were staged in user-writable directories; the specific IOC list is beyond the fetched excerpt).
- Treat any confirmed execution as high-priority incident activity — Huntress observed hands-on-keyboard reconnaissance and follow-on tunneling, indicating a broader intrusion, not isolated PoC testing.
- Apply the April 2026 patch for CVE-2026-33825.
Caveats
- Patching CVE-2026-33825 addresses only BlueHammer; RedSun and UnDefend remain exploitable with no vendor fix at publication.
- Huntress' claim that RedSun also escalates to SYSTEM is stated as investigation-derived assessment ("investigation indicates"), not vendor-confirmed.
- The full exploit chain and IOC paths were truncated in the fetched text — consult the source for the complete artifact list before building detections.
CVEs named here
Technologies named here
Techniques named here
- TOCTOU race condition
- Oplock-based synchronization
- Volume Shadow Copy abuse
- Directory Change Notification racing
- Credential dumping via SAM database
- SYSTEM token theft/privilege escalation
- Staging/execution from user-writable directories
- Hands-on-keyboard reconnaissance
- VPN credential abuse for initial access
- Reverse tunneling / covert C2 relay
Threat actors named here
- Chaotic Eclipse
- Unattributed hands-on-keyboard threat actor / intruder
- BeigeBurrow
Related in Threat Intel
 huntress.comwriteup
Reverse Engineering the Six Stages of MacSync Stealer and RAT
 huntress.comwriteup
AI-Coded Malware | Analyzing Vibe-Coded AD Enumeration | Huntress

 blog.talosintelligence.comtool
Introducing CAIRN: Frontier tracking for AI-integrated malware (Cisco Talos)
 huntress.comwriteup