
 x.comtool
Md Ismail Šojal 🕷️ (@0x0SojalSec) on X
An x64dbg MCP server (GitHub repo by duty1g, shared via an X post) that lets Claude drive the x64dbg Windows debugger: set breakpoints, dump memory, step code and run other reverse engineering tasks programmatically. The post targets malware analysts. A reply notes that debugging a sample executes it, so the agent should run in a snapshotted VM with no shared folders or host route, with every command logged.
TL;DR Shares an MCP server that lets Claude control x64dbg for breakpoints, memory dumps and stepping, with a warning to run it only in a throwaway VM.
Also seen from another angle🧠 AI →
Technologies named here
- x64dbg
- Claude
- Model Context Protocol
- Windows
- x64dbg MCP Server
Techniques named here
- Reverse engineering
- Dynamic malware analysis
Concepts named here
- Agent action logging
- Sandboxing
Related in Malware & RE

 huntress.comwriteup
Reverse Engineering the Six Stages of MacSync Stealer and RAT
 huntress.comwriteup
Post-DEF CON Phishing Uses Malicious Google Doc to Deliver Malware
 huntress.comwriteup
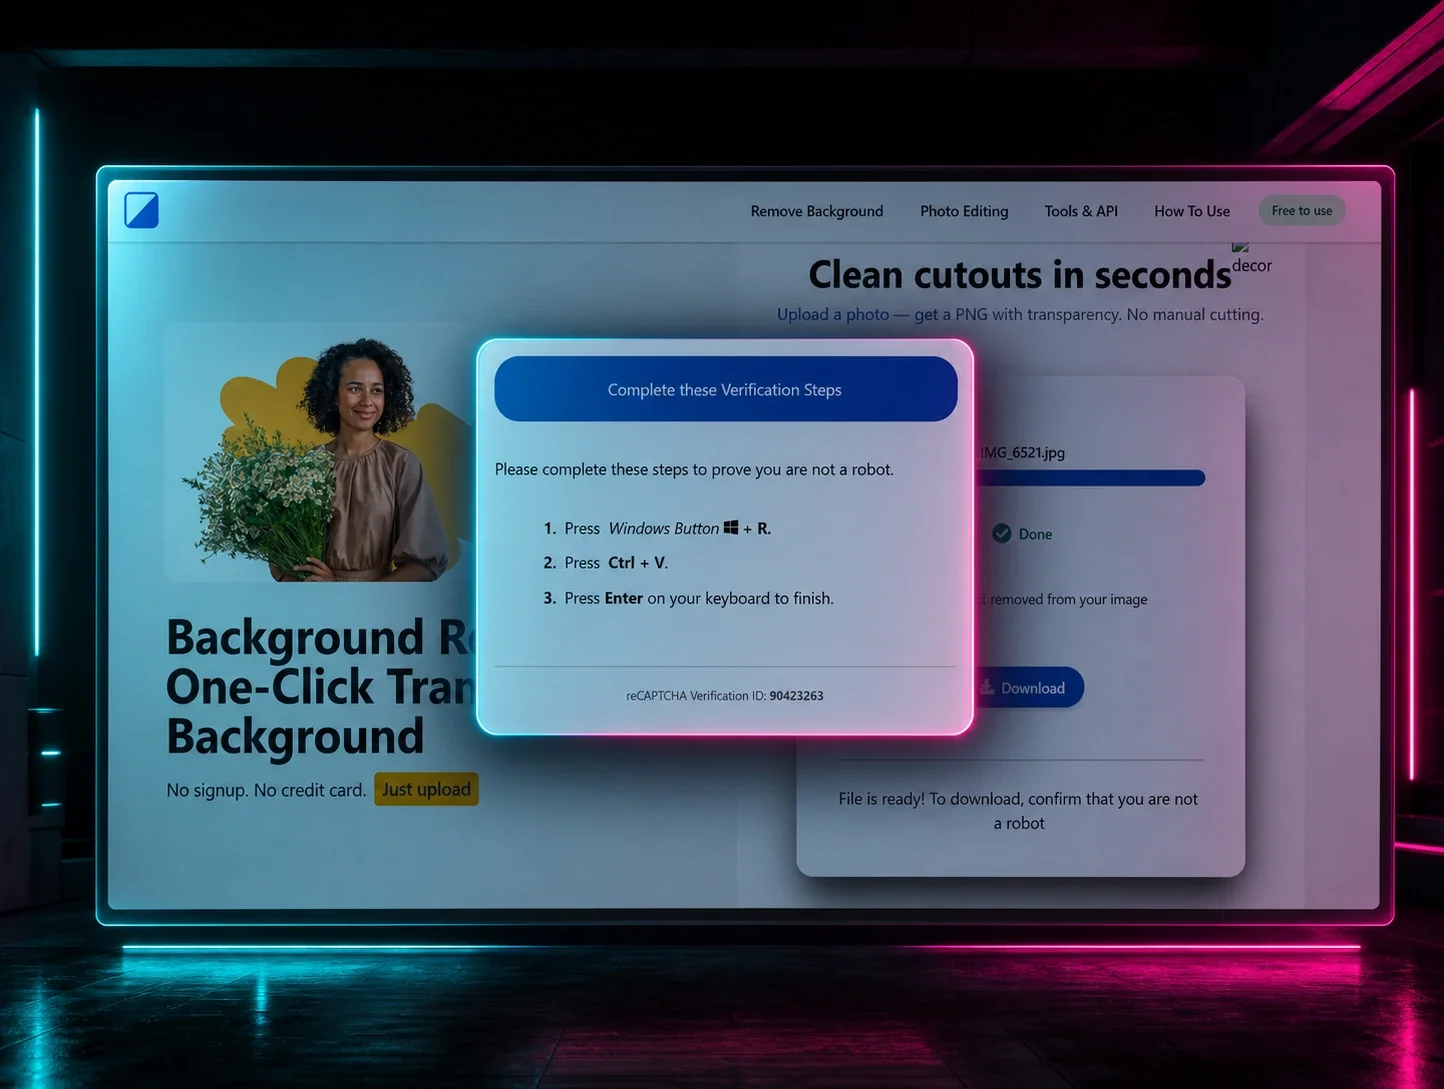
ClickFix Removes Your Background but Leaves the Malware

