 huntress.comwriteup
Threat Actors Weaponize Tiflux RMMs in Malspam Attacks
Huntress documents a malspam campaign, active since February 27, that uses fake "service agreement" document lures behind a CloudFlare CAPTCHA to trick targets into installing Tiflux, a lesser-known Brazil-based commercial RMM, before pivoting to UltraVNC, Splashtop, and ScreenConnect for persistent remote access. The Tiflux installer bundles suspicious extras beyond the legitimate agent: a decade-old UltraVNC build with hardcoded plaintext-recoverable passwords, an expired UltraVNC code-signing cert, registry files that stage a hidden TightVNC service (enabled even in Safe Mode) and a passwordless PuTTY SSH key to a peopleone[.]com[.]br server, registry tweaks that suppress Windows Secure Attention Sequence consent prompts, and a known vulnerable HwRwDrv.sys driver linked to privilege escalation with a revoked signing certificate. Huntress frames this as another entry in the ongoing "LOLRMM" pattern of attackers abusing legitimate commercial RMM tools for stealthy access and persistence.
What it is
A May 1 malspam incident dissected by Huntress SOC delivering Tiflux, a Brazil-based commercial RMM (signed by Tiflux Sistema de Gestão LTDA), as the initial-access foothold. This document carries the concrete indicators and detection artifacts the summary omits.
How it works
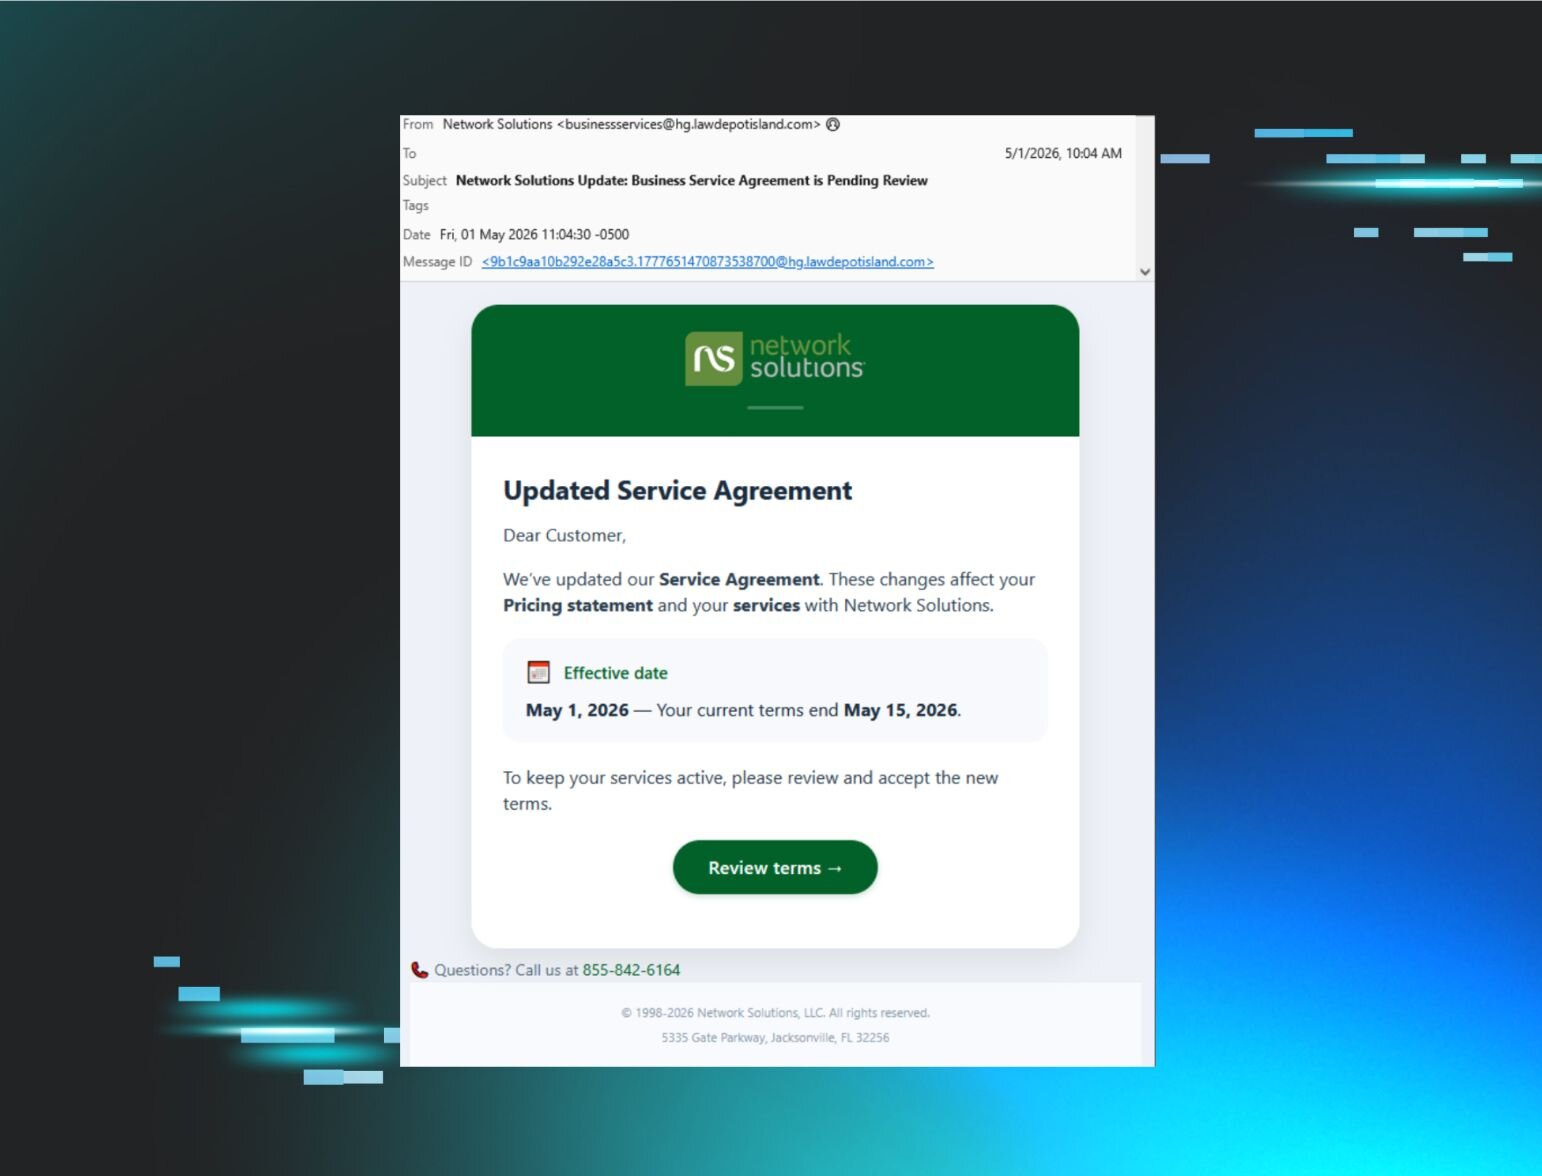
The lure email came from businessservices@hg[.]lawdepotisland[.]com. Its link led to a Cloudflare-CAPTCHA-gated page on lenwillfilenetwork[.]com, then to a fake "secured document" download delivering the installer renamed Network Solutions Agreement.msi. A newer variant (spotted the next day) used a fake CAPTCHA dialog inside Edge on Windows that oddly mimicked a Mac UI.
The .msi unpacks Tiflux components including TiAgent (orchestrator), TiPeerToPeer (support backchannel), si.exe, and bundled "dependencies" — UltraVNC plus 7zip and tar. After install, TiService silently pushes down Splashtop and/or ScreenConnect with no user notification. Huntress watched both RMMs connect to their management servers, transmit screenshots/thumbnails, and — via Splashtop — run osqueryl.exe to profile the system.
flowchart TD
  A[Malspam email] --> B[CAPTCHA gate<br/>lenwillfilenetwork]
  B --> C[Network Solutions Agreement.msi]
  C --> D[TiService installed]
  D --> E[Splashtop and/or ScreenConnect<br/>pushed silently]
  E --> F[osqueryl.exe profiling<br/>+ screenshot exfil]
  C --> G[Bundled UltraVNC 1.2.0.1<br/>+ mv video hook driver]
Preconditions / Affected
Windows endpoints where a user is tricked through the CAPTCHA gate into running the signed .msi. The installer's Tiflux signature is legitimate, so signature-based trust alone will not flag it.
What to do
The page gives no patch — this is abuse of legitimate software, not a CVE. Actionable detection signals to hunt on:
- Presence/execution of TiService, TiAgent, TiPeerToPeer, si.exe.
- TiService spawning Splashtop or ScreenConnect installs, and Splashtop invoking
osqueryl.exe. - UltraVNC components self-identifying as v1.2.0.1 (current is 1.6.4.0), a code-signing cert issued to uvnc bvba that expired March 2014, and a device-manager display adapter named
mv video hook driver2(driver dated April 11, 2007). - Block/alert on the IOCs above: sender domain, CAPTCHA host, and the installer filename.
Caveats
The deep analysis is of a single incident; other Tiflux-linked incidents shared traits (multiple RMMs, vulnerable kernel drivers, credential theft) but were not all fully detailed. The fetched text cuts off mid-sentence and does not complete the HwRwDrv.sys driver discussion the TL;DR references.
Organisations named here
- HwRwDrv.sys
- PeopleOne
- Secure Attention Sequence
Technologies named here
- Tiflux
- UltraVNC
- Splashtop
- HwRwDrv.x64
- TightVNC
- ScreenConnect
- osqueryl.exe
- 7zip and tar
- PuTTY
- LOLRMM
- Windows
Techniques named here
- Phishing with fake document lures
- Fake/mimicry CAPTCHA
- Abuse of legitimate RMM software
- Vulnerable driver deployment for privilege escalation
- Registry modification for persistence and concealment
- Hardcoded credentials in configuration files
- System information profiling and screenshot exfiltration
- C2 communication over UDP
Threat actors named here
- Unidentified threat actor behind Tiflux malspam campaign
Related in Threat Intel
 huntress.comwriteup
Reverse Engineering the Six Stages of MacSync Stealer and RAT
 huntress.comwriteup
AI-Coded Malware | Analyzing Vibe-Coded AD Enumeration | Huntress

 blog.talosintelligence.comtool
Introducing CAIRN: Frontier tracking for AI-integrated malware (Cisco Talos)
 huntress.comwriteup