 x.comthread
Aditya Agrawal (@exploitprotocol) on X
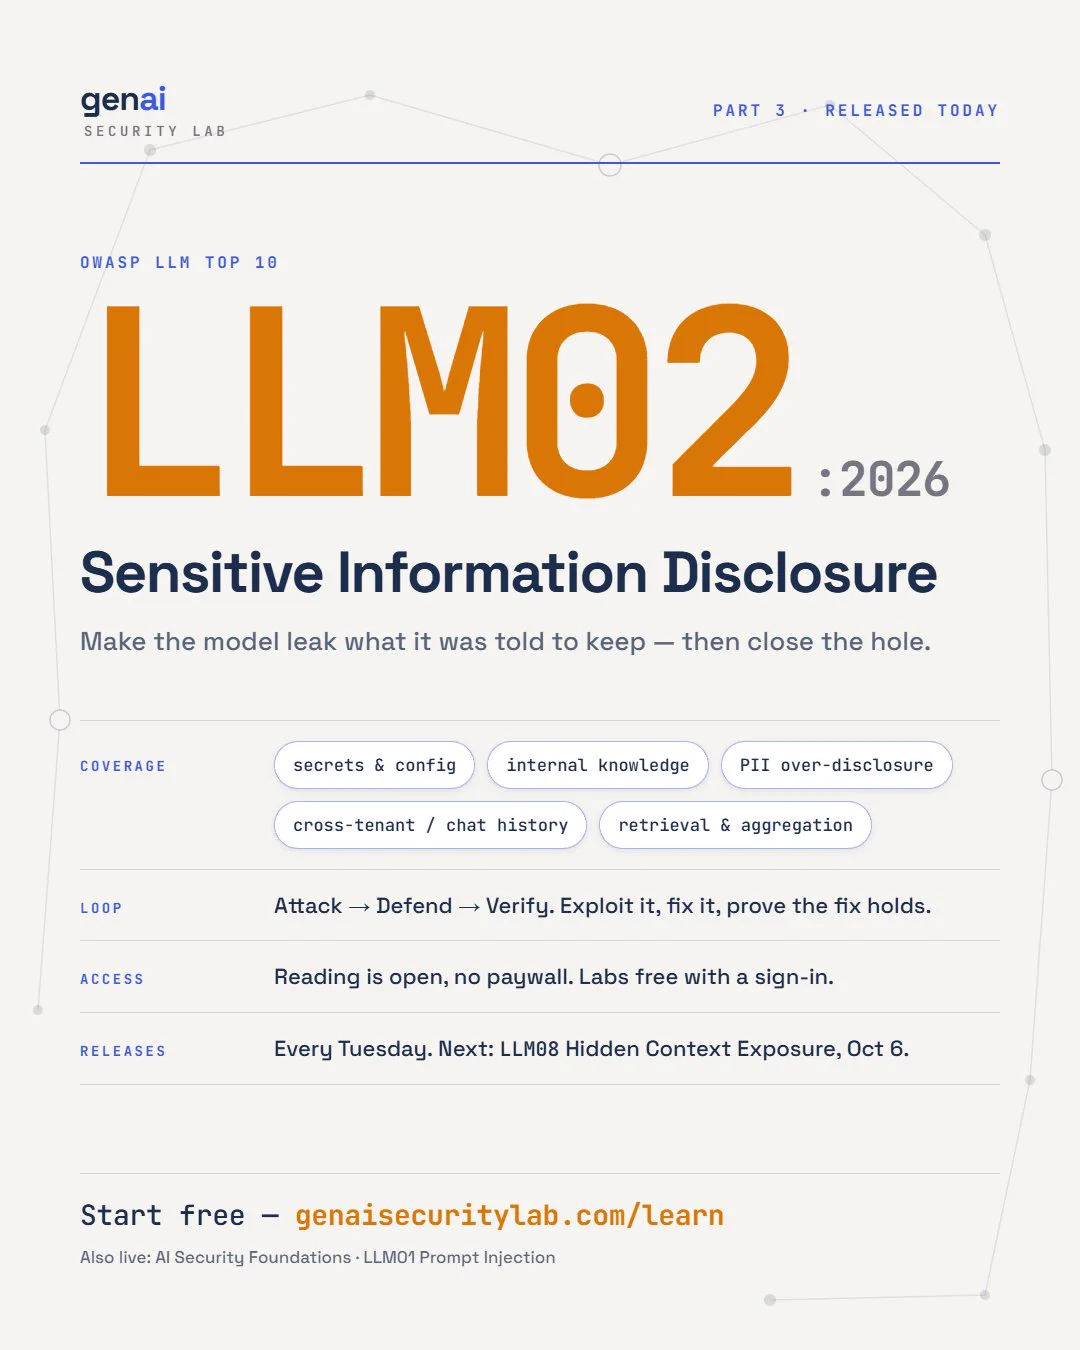
Announcement thread for part 3 of the free Learn AI Security series at genaisecuritylab.com, covering OWASP LLM02 Sensitive Information Disclosure in LLM applications. It walks through failure modes - leaked secrets/API keys via model context, internal knowledge leakage, personal-data over-disclosure, cross-tenant/conversation-history leakage, and RAG retrieval/aggregation leaks - and offers live in-browser attack/defend/verify labs comparing the issues to IDOR and multi-tenant isolation testing in traditional web apps. The author notes the series continues weekly, with LLM08 Hidden Context Exposure scheduled next.
TL;DR Free live-lab walkthrough of OWASP LLM02 Sensitive Information Disclosure, part of a weekly AI security learning series.
Technologies named here
- genaisecuritylab.com/learn
- LLM
- OWASP Top 10 for LLM Applications
Techniques named here
- OWASP LLM02
- Secrets and configuration exposure via model context
- Internal knowledge leakage
- Personal data over-disclosure
- Cross-tenant or conversation-history leakage
- Retrieval and aggregation leaks
- IDOR and multi-tenant isolation testing
- IDOR
Related in AI Security

 blog.talosintelligence.comtool
Introducing CAIRN: Frontier tracking for AI-integrated malware (Cisco Talos)
 github.comadvisory
Flowise MCP Security Bypass Enables RCE
github.comrepoYesWeHack Claude Kit

 jfrog.comarticle