 github.comrepo
manyuegong33/r0crawl_skills
r0crawl_skills is a beginner-friendly Chinese-language skill library of 196 specialized reverse-engineering modules for Codex-style AI coding agents, with a router that asks scoping questions and directs the agent to the right workflow (web RE, Android unpacking, Frida instrumentation, native binary analysis, protocol reconstruction, malware triage, firmware analysis, CTF). It ships lightweight scripts (case init, module router, artifact hashing) and ten sanitized example playbooks covering DEX dump verification, WebCrypto hooking, native loader tracing, PCAP reconstruction, and selective emulation, plus dedicated modules for CAPTCHA/WAF/anti-bot systems, mini-programs, hybrid apps (Flutter/React Native/Electron), and IDA/Ghidra/Rizin automation.
What it is
r0crawl_skills is a skill library for Codex-style AI coding agents. The catalog summary covers the 196 modules and their scope; what it does not carry is how you install and invoke the thing, the router's actual entry questions, and the exact script commands.
What to do
Install by copying the directory into the Codex skills path (PowerShell):
Copy-Item -Recurse .\r0crawl_skills $env:USERPROFILE\.codex\skills\r0crawl_skillsThen invoke it in-agent with the phrase (Chinese): 使用 r0crawl_skills。对这个目标开始一次新手友好的调查。 ("Use r0crawl_skills. Start a beginner-friendly investigation on this target.")
The router opens with four scoping questions rather than dumping terminology: what are we analyzing, which action is most critical, what material is already on hand, and what outcome is wanted — then it returns a single route.
The lightweight scripts under scripts/ run as:
python scripts/init_case.py demo-signature
python scripts/module_router.py "Android APK Frida dump dex"
python scripts/hash_artifact.py sample.apk
Preconditions / Affected
Windows/Codex-agent oriented: the install path uses $env:USERPROFILE\.codex\skills\ and PowerShell Copy-Item. All documentation is Chinese-only — the summary notes "Chinese-language" but the practical consequence is that the router prompts, module names, and playbooks are entirely in Chinese, which matters for an engineer deciding whether to route work through it.
Caveats
The page states an explicit "don't copy" ("不复制") distillation strategy — capabilities are refined from public reverse-engineering practice rather than copied source, with sources documented in the research notes (references/). The ten example playbooks are described as sanitized/desensitized (脱敏). Generated module index lives at references/generated-index.md.
Note the page lists coverage the summary omits: iOS, fuzzing (模糊测试), cloud/API, and game reverse-engineering, plus named verticals (aviation/travel, e-commerce risk control, financial data, logistics, government portals) and protocol targets (live-streaming WebSocket, Protobuf, GraphQL, WASM signatures) — relevant if your target falls in one of those domains.
Technologies named here
Techniques named here
- Web 逆向
- Android 脱壳
- Frida 追踪
- 原生二进制分析
- 协议还原
- 恶意软件分诊
- 固件分析
- 早期加载器追踪
- 系统调用观察
- 匿名可执行内存检测
- 转储/修复/重建校验
- 硬件断点观察
- OLLVM 还原
- eBPF 可观测
- C2 流量还原
- 检测工程
- 选择性仿真
- 反作弊内核分析
- 案件编排
- 安全实验管理
Related in Malware & RE

 huntress.comwriteup
Reverse Engineering the Six Stages of MacSync Stealer and RAT
 huntress.comwriteup
Post-DEF CON Phishing Uses Malicious Google Doc to Deliver Malware
 huntress.comwriteup
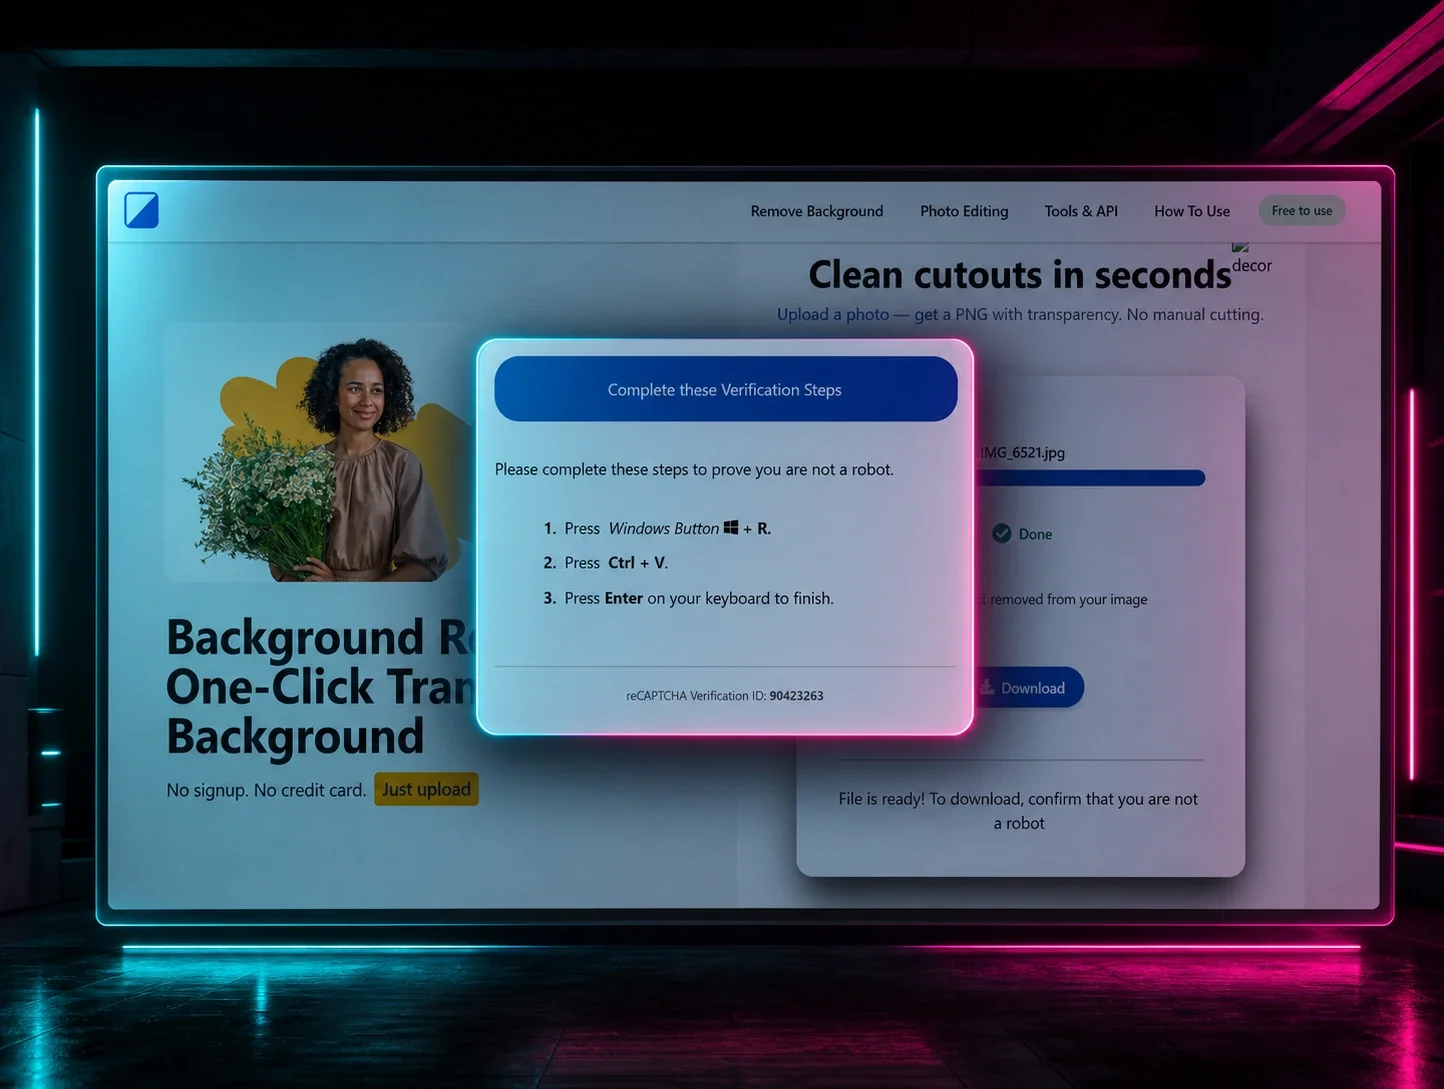
ClickFix Removes Your Background but Leaves the Malware

