 depthfirst.comwriteup
How An Authorization Flaw Reveals A Common Security Blind Spot: CVE-2025-59305 Case Study
How An Authorization Flaw Reveals A Common Security Blind Spot: CVE-2025-59305 Case Study | depthfirst
CVE-2025-59305 is a missing authorization flaw in Langfuse's tRPC background-migrations router. Endpoints for retry, list and status used protectedProcedure, which checks login but not admin role, so any self-registered user could restart migrations and cause data corruption or denial of service. Reported and patched on 9 September 2025 with a new adminProcedure; disclosed 15 September 2025. The post also argues SAST tools and AI code assistants miss AuthN vs AuthZ gaps.
What it is
CVE-2025-59305 is a missing authorization check in Langfuse, the open-source LLM engineering platform. The flaw is in background-migrations-router.ts, the tRPC router for background migrations. The depthfirst platform found it, and the post is depthfirst's own case study.
How it works
The retry, list and status endpoints used tRPC's protectedProcedure. That middleware confirms a valid session but does not check for an admin role. Langfuse allows self-serve sign-up, so anyone could register and reach these controls.
The post describes two impacts:
- Data corruption: retrying a migration that is already running creates a race condition. The database can end up partly migrated and inconsistent.
- Denial of service: triggering many migration jobs at once exhausts database and worker resources.
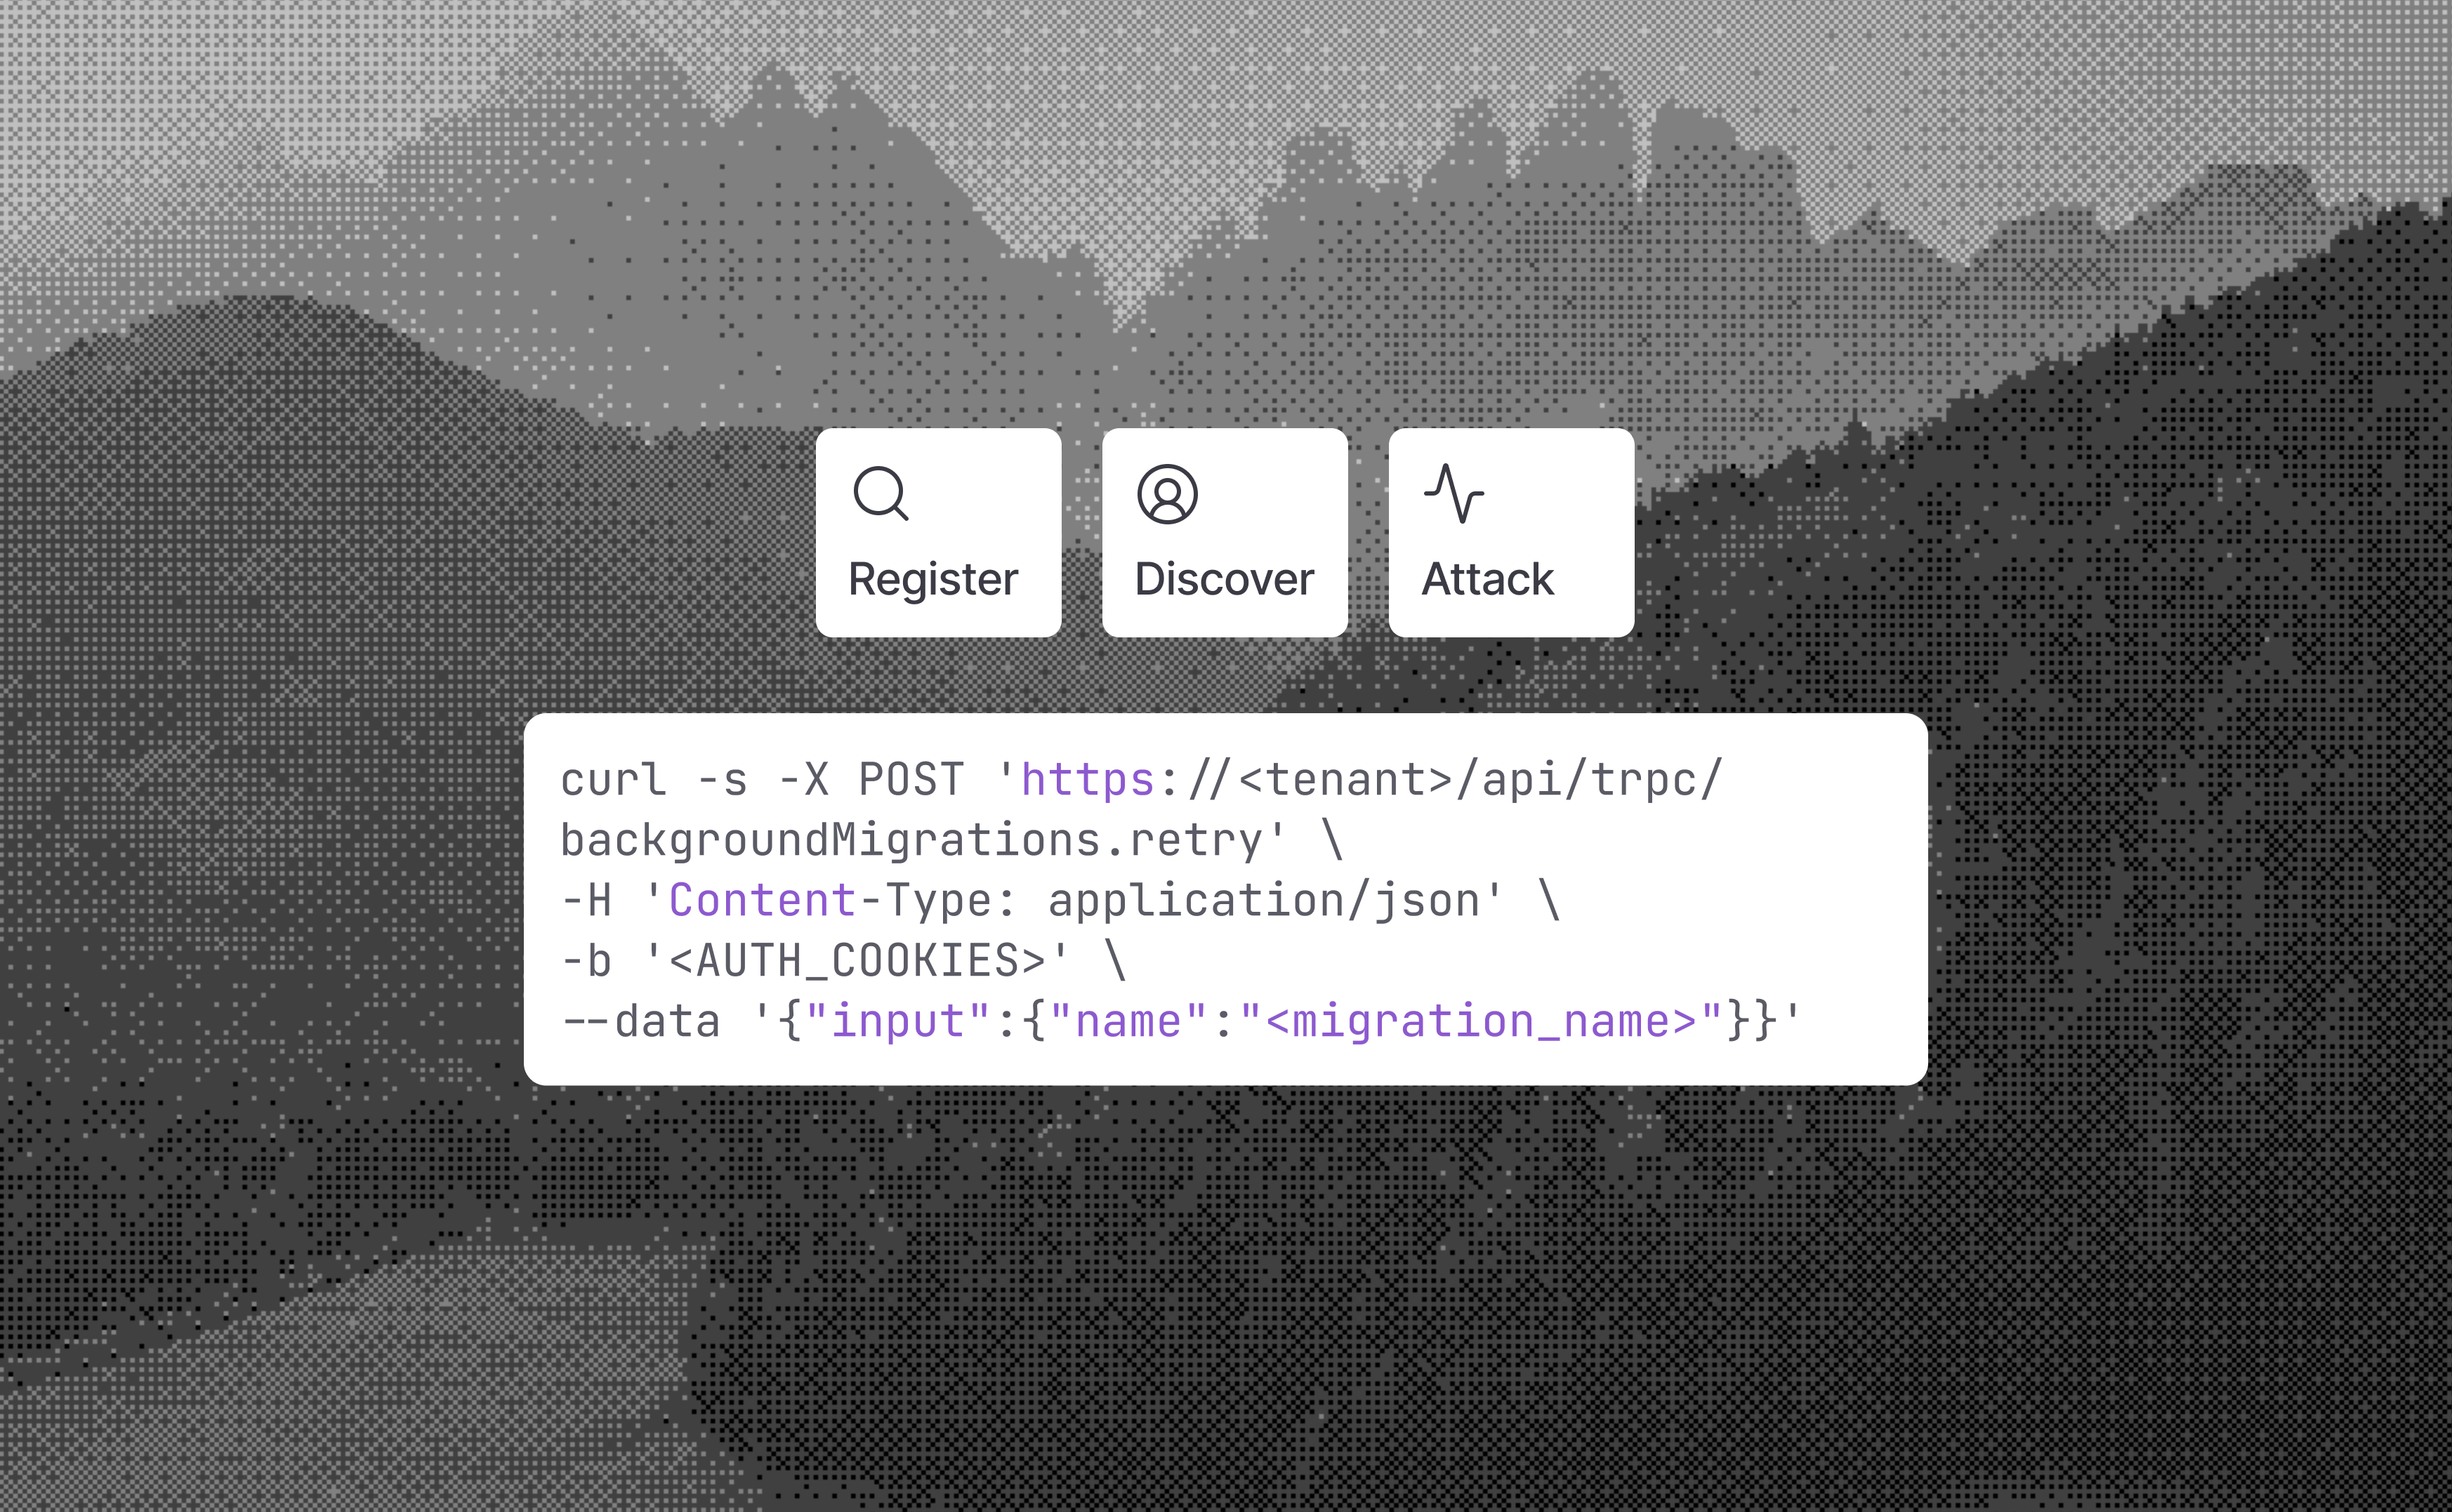
The post gives this exploit path: register an account, call backgroundMigrations.all to list jobs, then call backgroundMigrations.retry on a critical job. Its example request:
curl -s -X POST 'https://<tenant>/api/trpc/backgroundMigrations.retry' \
-H 'Content-Type: application/json' \
-b '<AUTH_COOKIES>' \
--data '{"input":{"name":"<migration_name>"}}'
Preconditions / Affected
- The attacker needs only a valid session. On an instance with open sign-up, that means registering a new account.
- The page does not state affected or fixed Langfuse versions. Check the Langfuse advisory for those.
What to do
Langfuse fixed the flaw by adding an adminProcedure that enforces role-based authorization. Per the post, they shipped the patch the same day as the 9 September 2025 report. Public disclosure followed on 15 September 2025.
The post's broader lesson is to check roles, not just login, on internal routes. It names background jobs, migrations, report generation and maintenance as the areas that get overlooked. Search your own tRPC routers for sensitive mutations that use only an authentication-level procedure.
Caveats
- The post is vendor marketing. It claims that SAST tools cannot find authentication-versus-authorization gaps and that AI code assistants are likely to introduce them. It offers no testing or data to support either claim.
- It does not say whether anyone exploited the flaw. It says only that the fix came before exploitation.
- The impact descriptions are potential outcomes. The post does not show a demonstrated corruption or outage.
Organisations named here
- depthfirst
CVEs named here
- CVE-2025-59305
Technologies named here
- Langfuse
- curl
- TypeScript
- adminProcedure
- depthfirst platform
- Langfuse security Hall of Fame
- protectedProcedure
- SAST scanners
- tRPC
Techniques named here
- Missing authorization check
- Coordinated disclosure
- Broken access control
- Missing Authorization
- Race condition via restarting an in-progress data migration
Related in AppSec
 github.comadvisory
Flowise MCP Security Bypass Enables RCE

 huntress.comwriteup
Inside an Oracle Database SQL Injection Attack | Huntress
github.comrepoOASIS

 blog.trailofbits.comwriteup