 huntress.comarticle
Social Engineering Leveled Up. Has Your Security Program?
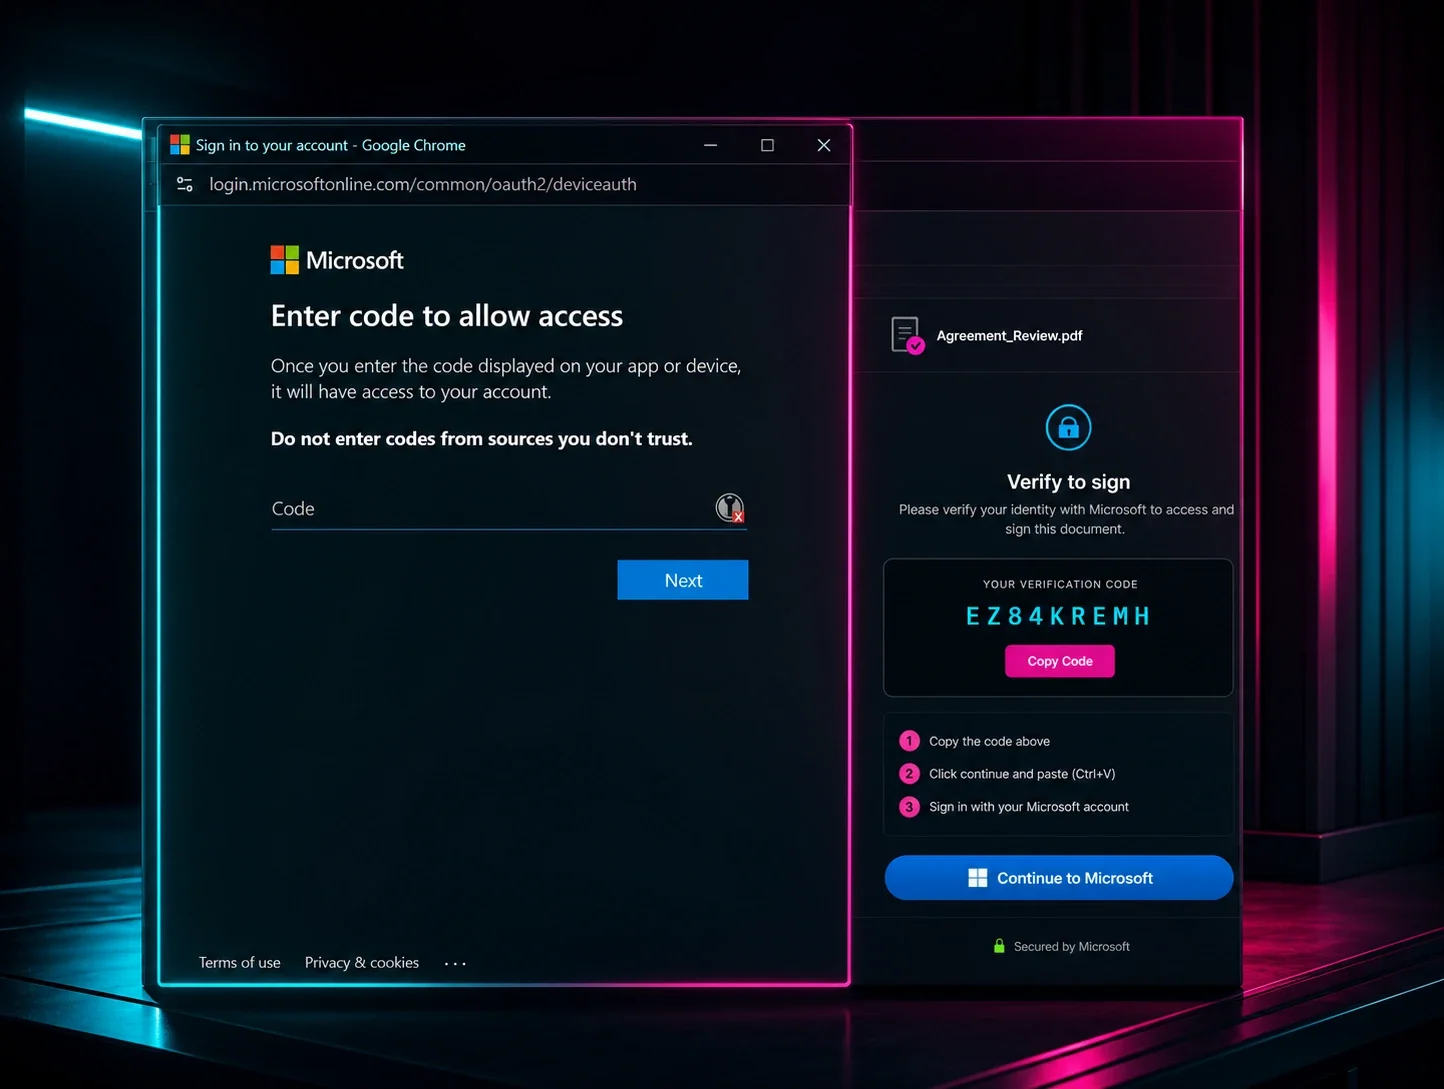
Huntress blog on how social engineering has outpaced traditional prevention-focused security programs, citing specific campaigns: EvilTokens, a phishing-as-a-service operation that weaponized the Railway cloud deployment platform and Cloudflare Workers to run OAuth device code phishing against 340+ organizations, and a campaign using fake ChatGPT/Grok search results to trick macOS users into installing the AMOS infostealer. Also discusses AI-driven deepfake identity attacks and alert fatigue undermining detection.
TL;DR Vendor writeup on device-code phishing, deepfake identity attacks, and the EvilTokens PHaaS campaign abusing Railway/Cloudflare to deliver AMOS infostealer via fake AI-support pages.
Technologies named here
- Microsoft OAuth authentication flow
- Identity Threat Detection and Response
- Huntress platform
- macOS
- Sublime Security
- Railway
- Cloudflare Workers pages
- Claude installer
- Cloudflare Workers
- OAuth
- ChatGPT
- Grok
- Huntress
Techniques named here
- Device code phishing
- Deepfake/AI identity impersonation
- Phishing-as-a-service via legitimate cloud infrastructure
- Calendar phishing / everyday workflow abuse
Threat actors named here
- EvilTokens
- AMOS infostealer
- Railway campaign
Related in Threat Intel
 huntress.comwriteup
Reverse Engineering the Six Stages of MacSync Stealer and RAT
 huntress.comwriteup
AI-Coded Malware | Analyzing Vibe-Coded AD Enumeration | Huntress

 blog.talosintelligence.comtool
Introducing CAIRN: Frontier tracking for AI-integrated malware (Cisco Talos)
 huntress.comwriteup