 huntress.comwriteup
The Gentleman Ransomware | Defense Evasion TTPs Uncovered | Huntress
Huntress SOC details two Gentlemen ransomware incidents showing Windows Event Log clearing, PowerShell-based Defender tampering, and Scheduled Task persistence via a fake svchost32.exe creating a SOCKS proxy C2 connection. Ties findings to a leaked internal RaaS database revealing CVE-2024-55591 exploitation and infrastructure links to Qilin and Lazarus Group.
What it is
Field-level detection detail for The Gentlemen ransomware (RaaS, active since mid-2025, 400+ claimed victims across 70+ countries), from two Huntress SOC incidents in April and May. In both, the Huntress agent was deployed post-incident, so there is no live EDR telemetry — the findings come from residual PowerShell and Windows Event Log artifacts. This adds specific IOCs and Event IDs that the catalog summary does not carry.
How it works
In the shipping/transportation incident, the actor connected via RDP with a compromised account, then ran the encryptor locally from the Documents folder:
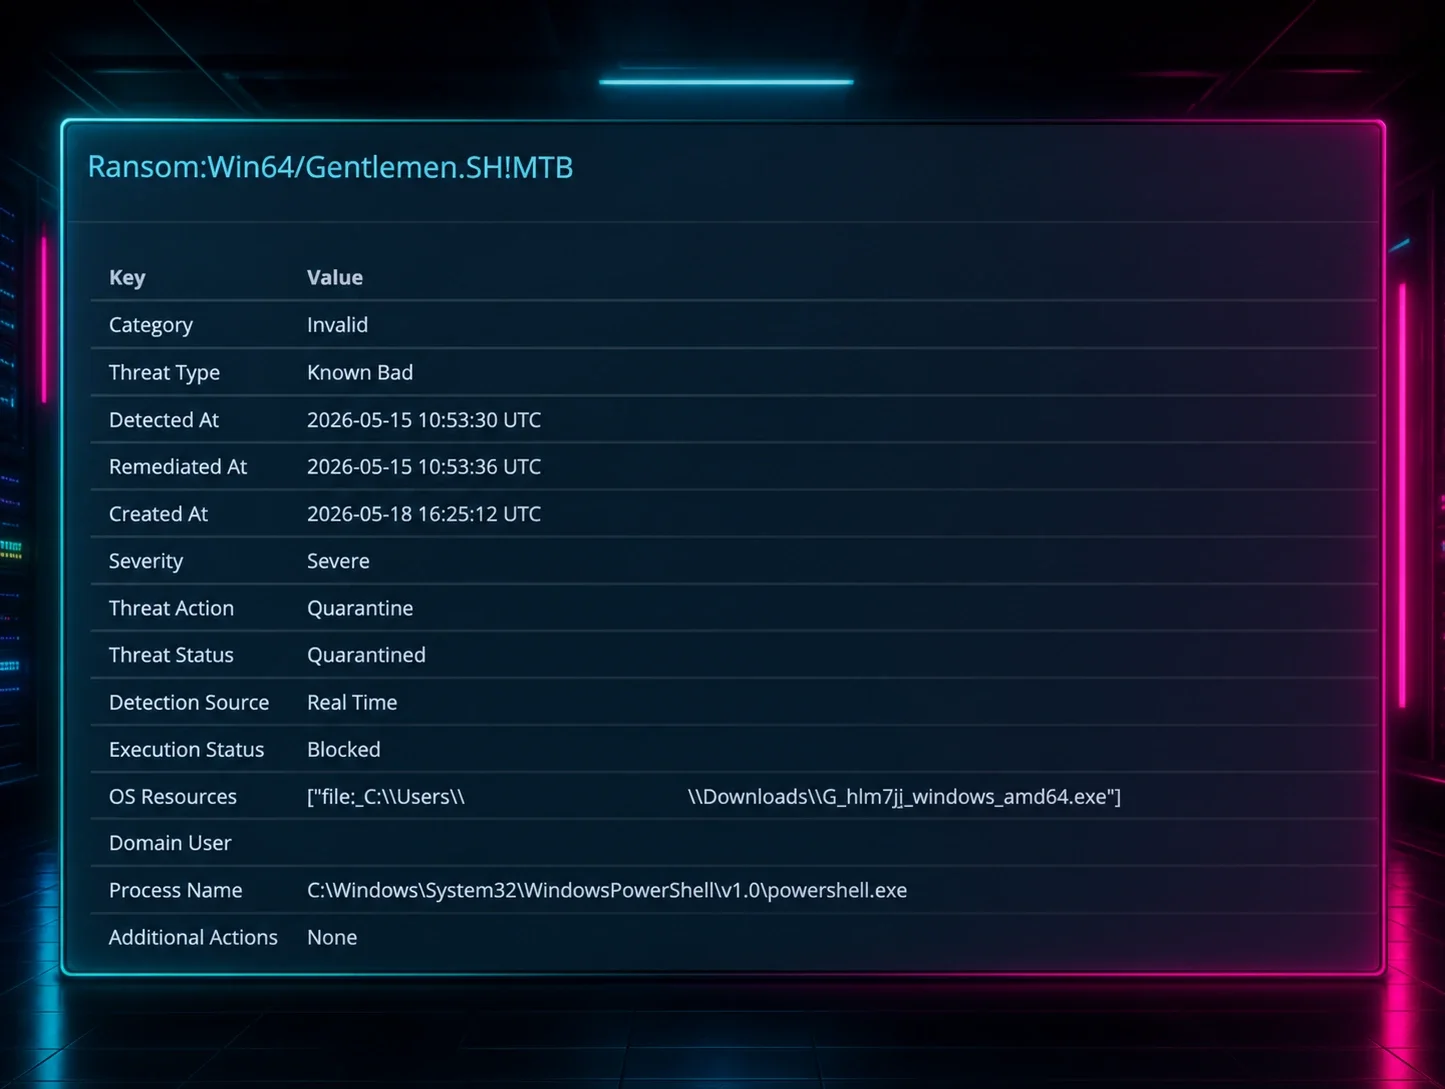
C:\Users\REDACTED\Documents\win.exe --password REDACTED --T 200 --superfastMicrosoft Defender blocked this first attempt (Event IDs 1116 and 1117). Defender also caught the PowerShell exclusion-tampering script, detected as Trojan:Win32/MpTamperBulkExcl.H. The actor then created Scheduled Tasks — assessed as running on the Domain Controller because the expected local Microsoft-Windows-TaskScheduler/140 records were absent — one of which re-ran the encryptor. Finally they cleared the System, Application, and Security logs (Event ID 104 for Application/System, Event ID 1102 for Security).
What to do
Hunt for these concrete artifacts:
- Encryptor named win.exe run from a user Documents folder, with flags
--password,--T,--superfast. - Defender 1116/1117 blocks followed shortly by re-execution attempts.
- Defender signature Trojan:Win32/MpTamperBulkExcl.H (AV exclusion tampering).
- Event IDs 104 and 1102 indicating logs were cleared — treat as a breadcrumb, not a dead end (see caveat).
- Absence of TaskScheduler/140 on an endpoint where tasks clearly ran, suggesting task creation on the DC instead.
Per prior public reporting the page cites: patch Fortinet CVE-2024-55591 (auth bypass) as an initial-access vector, and watch for GPO abuse enabling domain-wide deployment and AnyDesk persistence.
Caveats
- Key limitation the authors state themselves: no EDR telemetry during the attack and no SIEM at either victim, so initial access could not be confirmed — the RDP connection is merely the earliest point of visibility, not proven entry.
- The actors cleared only three logs and left all others intact, so forensic footprints remain — the log-clearing is a lead, not total erasure.
- The DC-task inference rests on the missing TaskScheduler/140 records, not on direct DC evidence.
- Some techniques (custom evasion tooling, driver abuse, GPO, AnyDesk, the eight Tox affiliate IDs) come from Trend Micro, Check Point, and the leaked database rather than from these two incidents directly.
Organisations named here
- FalconFeeds
- Red Asgard
CVEs named here
- CVE-2024-55591
Technologies named here
- Huntress agent
- AnyDesk
- Microsoft Defender
- Fortinet
- Ransomware.live
- Tox messaging network
- Huntress
- PowerShell
- Windows Defender
- RDP
- Windows
- Trend Micro
- Check Point
Techniques named here
- Remote Desktop Protocol abuse
- Scheduled Task creation for execution/persistence
- Windows Event Log clearing
- Defender tampering / exclusion abuse
- Masquerading
- C2 SOCKS proxy beaconing
- GPO abuse for domain-wide deployment
- Legitimate driver abuse
- File encryption / ransomware deployment
Threat actors named here
- The Gentlemen
- Qilin
- Lazarus
- Lazarus Group
Related in Threat Intel
 huntress.comwriteup
Reverse Engineering the Six Stages of MacSync Stealer and RAT
 huntress.comwriteup
AI-Coded Malware | Analyzing Vibe-Coded AD Enumeration | Huntress

 blog.talosintelligence.comtool
Introducing CAIRN: Frontier tracking for AI-integrated malware (Cisco Talos)
 huntress.comwriteup