
 x.comthread
Prasenjit Sarkar (@stretchcloud) on X
Thread on whether infrastructure as code survives AI agents, set off by James Ward's claim that IaC is dead and Darren Shepherd's rebuttal. It describes HCP Terraform's positioning as a governance layer for agent-written infrastructure: project-scoped identities, per-run short-lived OIDC credentials, policy-as-code plan checks, and the tfctl CLI with dry-run and destructive-operation guardrails. It also covers Pulumi's Neo agent and Firefly's point that direct cloud API calls by agents leave no diff, audit trail or rollback.
TL;DR Argues IaC becomes the control plane for AI agents, citing HCP Terraform's scoped identities, short-lived OIDC credentials, policy checks and tfctl guardrails.
Also seen from another angle🧠 AI →
Organisations named here
- Darren Shepherd
- Firefly
- HashiCorp
- James Ward
Technologies named here
- Terraform
- Neo
- OpenID Connect
- AWS CDK
- CDK
- Firefly
- HCP Terraform
- Pulumi
- tfctl
Techniques named here
- Dry-run mode
- policy-as-code
- Project-scoped identities
- Short-lived OIDC credentials
Concepts named here
- Least privilege
- Agent proposes, Terraform governs
- Auditability and rollback
- Control plane around the agent
- Infrastructure as code as discipline tool
Related in DevSecOps

 jfrog.comarticle
JFrog: The Governance Gap Between Your Policy and Your Pipeline

 stepsecurity.ioarticle
Dev Machine Guard Now Supports Windows - StepSecurity
 socket.devwriteup
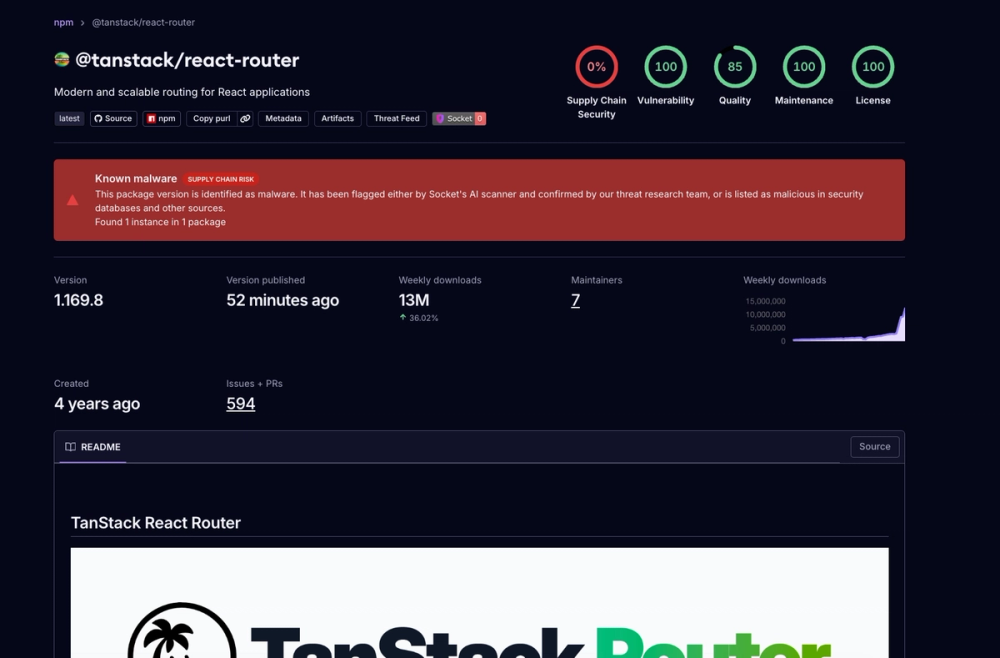
Socket: TanStack npm Packages Compromised
 securitylab.github.comadvisory