 x.comthread
lee1981 (@lee1981b) on X
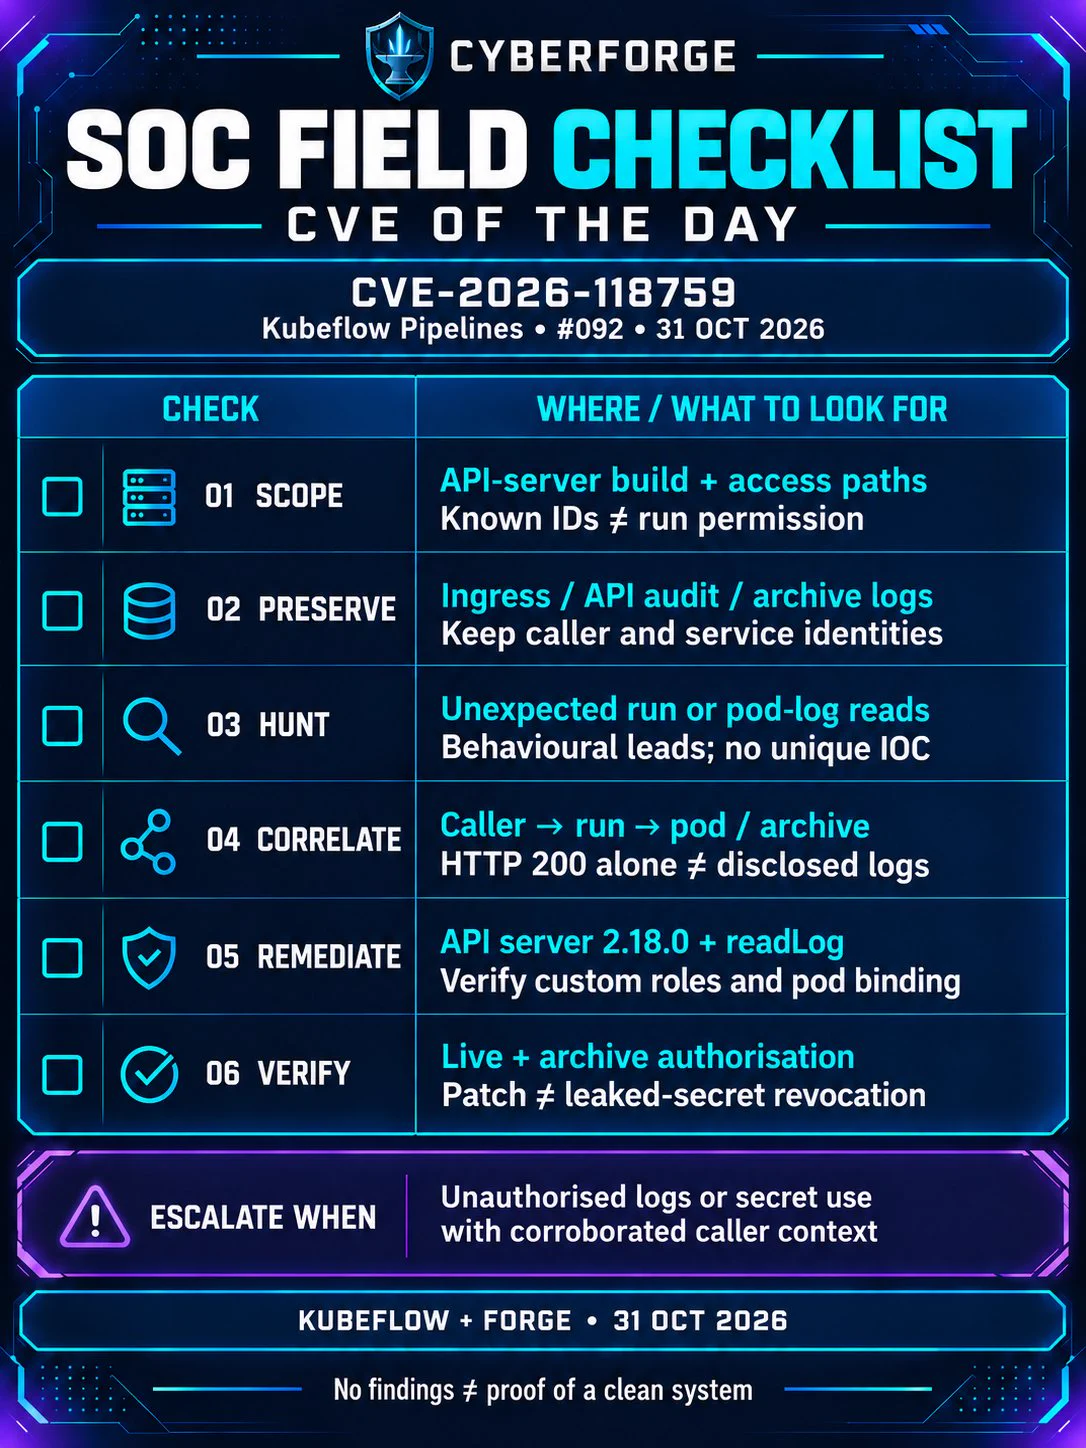
CyberForge "CVE of the Day" #092 covers CVE-2026-118759 in Kubeflow Pipelines. The post says a run-log request must carry permission, not just a run ID: knowing the identifier does not authorize reading that workload's output. It points to Kubeflow's advisory, but the fetched text is cut off before any affected versions, fix or exploit details.
TL;DR Flags CVE-2026-118759, a Kubeflow Pipelines flaw where run-log access relied on a run ID without a permission check.
Organisations named here
- CyberForge
CVEs named here
- CVE-2026-118759
Technologies named here
- Kubeflow Pipelines
Techniques named here
- IDOR
Concepts named here
- Authorization versus identification
Related in AppSec
 github.comadvisory
Flowise MCP Security Bypass Enables RCE

 huntress.comwriteup
Inside an Oracle Database SQL Injection Attack | Huntress
github.comrepoOASIS

 blog.trailofbits.comwriteup