 huntress.comwriteup
Meta Phishers Abuse Business Account Manager Service | Huntress
Huntress researchers analyzed a phishing campaign that abused Meta's legitimate "Business Partner Manager" email feature (from security@facebookmail.com) to send convincing phishing lures that bypass typical email validation checks. The threat actor injected a URL into the field meant for a partner's business name, redirecting victims through Google Sites, a fake "Meta Agency Partner Program" page (aussiecleaningservices[.]com), and later a Facebook Messenger chatbot ("AI Strategic Partner") leading to a fake Meta Verified/Content Monetization phishing page (sw[.]run, framed via Netlify) that harvested credentials, MFA codes, and ID documents, exfiltrating them to a Telegram bot with Vietnamese-language text, before Meta shut down the abuse vector.
What it is
A Huntress writeup of a phishing campaign abusing Meta's Business Manager partner-invitation service, letting the attacker send lures from the legitimate noreply@business.facebook.com address. The key detail the summary omits: Meta has since remediated the abuse and the attacks have subsided. The threat actor set up their own Meta business account and used the partner-invitation flow to reach targets.
How it works
The invitation email auto-inserts the requesting partner's name into a fixed sentence: "[Name] is not part of or affiliated with Meta." The attacker put a short URL-bearing phrase in the name field instead, so the rendered sentence reads as an instruction to visit a link. Because delivery is from a real Meta address, the mail passes SPF/DKIM/DMARC-style validation.
Two distinct lure strings are the most useful detection artifacts the page provides — neither is in the summary:
- May variant: "Get started [URL] – Your information is not part of or affiliated with Meta."
- June variant: "We agree to cooperate with your business [URL] . Other URLs is not affiliated with Meta." (note the stray space/period).
flowchart TD
    A[Meta partner invite email<br/>noreply@business.facebook.com] --> B{Variant}
    B -->|May| C[sites.google.com/view/profile1012]
    C --> D[aussiecleaningservices.com<br/>fake Agency Partner Program]
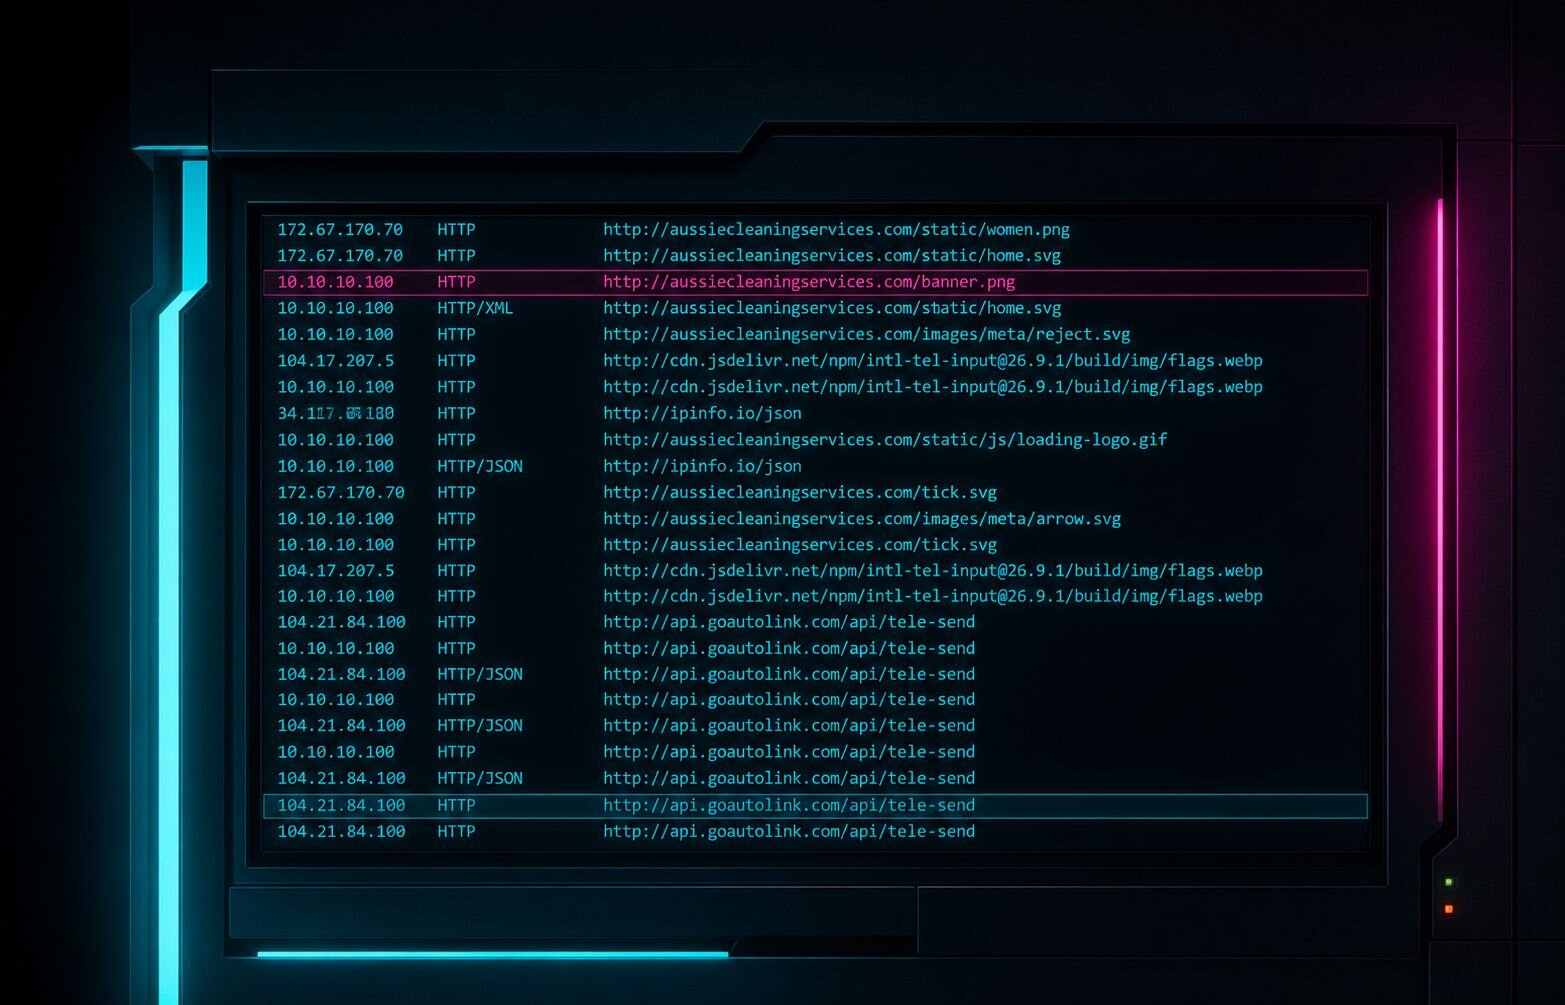
    D --> E[Exfil via api.goautolink.com]
    B -->|June| F[FB Messenger bot<br/>'AI Strategic Partner']
    F --> G[Buttons: Get Verification Badge /<br/>Enable Monetization]
    G --> H[Netlify page framed in sw.run<br/>Cloudflare domain]
    H --> I[Exfil to Telegram channel]
The June phishing pages harvested username, password, MFA code, phone number, email, and business-account names.
Preconditions / Affected
Targets are businesses/individuals managing Facebook or Instagram accounts who could plausibly receive a legitimate Business Manager partner invitation. The June variant funnels victims through a Facebook Messenger bot named AI Strategic Partner carrying a Meta corporate logo but describing itself as an interior/exterior painting and drywall team.
What to do
The page gives no vendor-side fix (Meta closed the vector). Actionable hunting from the text:
- Alert on inbound Meta partner invitations whose "name" field contains a URL or the two lure phrases above.
- Block/watch IOCs:
sites.google[.]com/view/profile1012,aussiecleaningservices[.]com,api.goautolink[.]com,sw[.]run(Cloudflare-fronted, Netlify-hosted pages). - Treat any Messenger bot pushing "Get Verification Badge" / "Enable Monetization" buttons as hostile.
Caveats
Attacks have subsided after Meta's action, so the primary vector is closed — this is largely retrospective/detection value. Huntress observed the June variant via a single honeypot hit (June 2) and notes the abuse had already been reported by other victims and researchers.
Organisations named here
- api.goautolink[.]com
- aussiecleaningservices[.]com
- @bulondondam
- businesshelpcenterpageid563252.netlify[.]app
- data1mdobot
- God of Wealth arrives
- sw[.]run
Technologies named here
- Google Sites
- Meta Business Manager / Business Account Manager service
- Facebook Messenger
- Telegram
- Meta Agency Partner Program
- Netlify
- Meta Verified
- Cloudflare
- ipinfo.io
- Meta Content Monetization program
Techniques named here
- URL injection into auto-generated message fields
- Credential phishing landing pages
- MFA code phishing / fake failure loop
- Chatbot-based phishing lure
- Iframe domain concealment
- Identity document harvesting
- Data exfiltration via bot API
Threat actors named here
- Unknown threat actor
Related in Threat Intel
 huntress.comwriteup
Reverse Engineering the Six Stages of MacSync Stealer and RAT
 huntress.comwriteup
AI-Coded Malware | Analyzing Vibe-Coded AD Enumeration | Huntress

 blog.talosintelligence.comtool
Introducing CAIRN: Frontier tracking for AI-integrated malware (Cisco Talos)
 huntress.comwriteup