 huntress.comwriteup
What a Fake Claude Download Says About Security Today
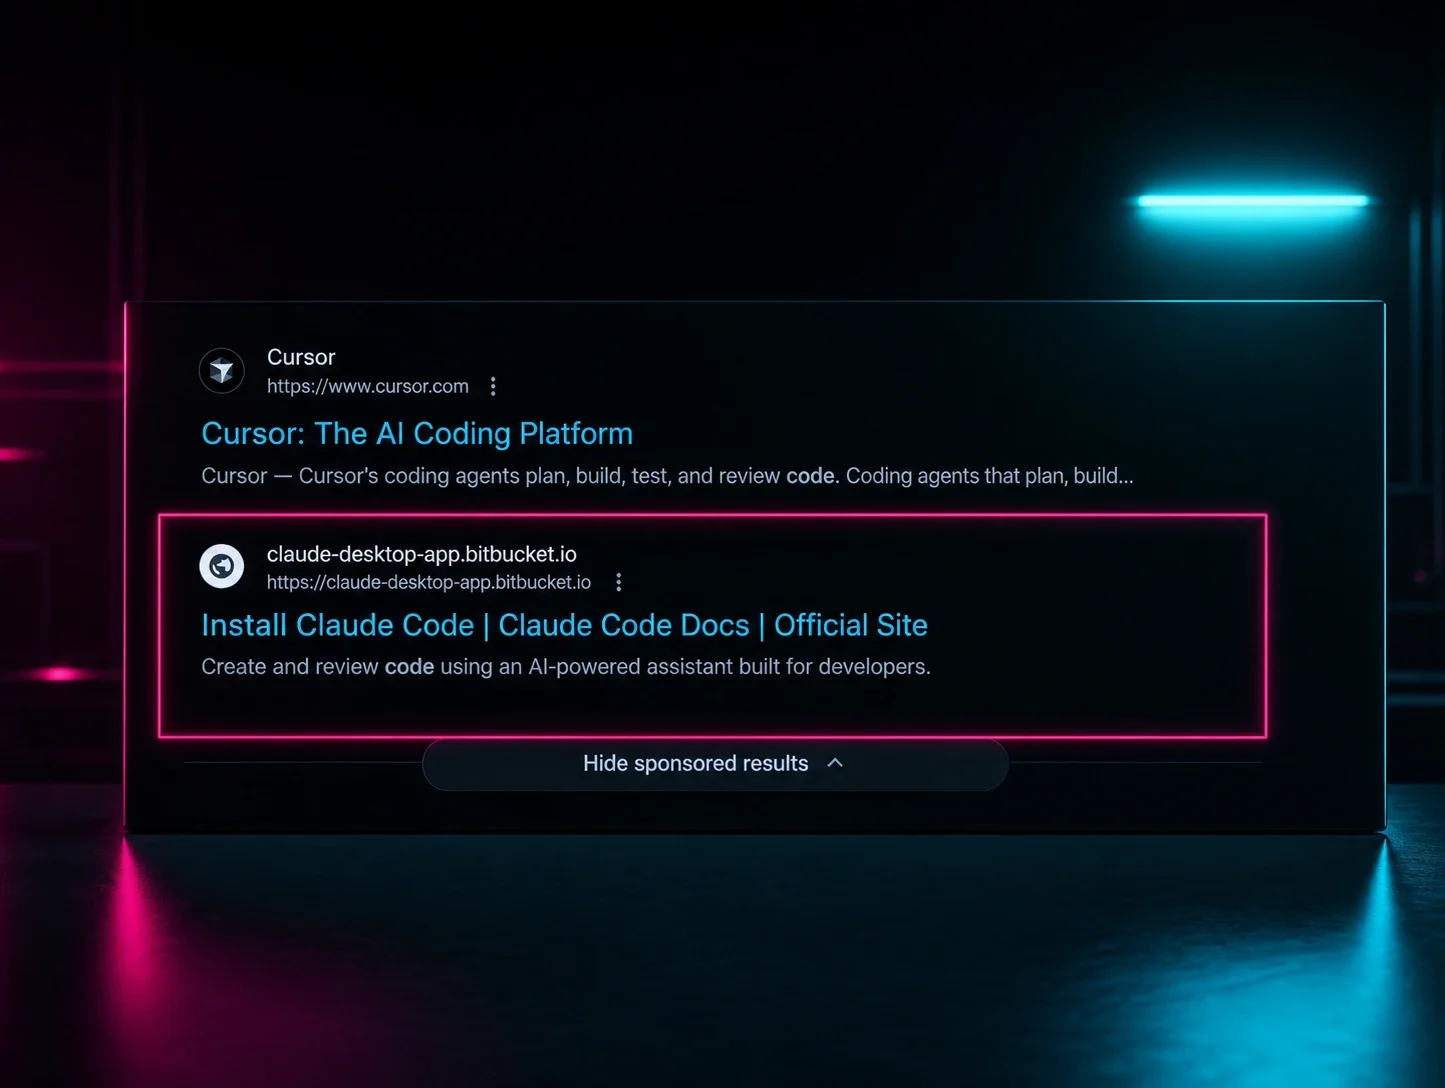
Huntress recounts an incident in which one of its own engineers clicked a sponsored Google Ads result impersonating "Claude Code" and downloaded malware onto his MacBook. The payload used base64 encoding and gzip compression to obfuscate a second-stage script that targeted the macOS keychain for Claude Code credentials, while an obfuscated AppleScript further hid its behavior; the engineer's immediate self-report let Huntress's SOC rotate credentials before attackers could use them. The piece is part technical incident summary, part culture commentary on rewarding fast, blame-free reporting of security mistakes.
TL;DR A malvertised "Claude Code" Google Ads result delivered obfuscated macOS malware that tried to steal keychain credentials from a Huntress engineer, caught in time by immediate self-reporting.
Organisations named here
- Eric Stride
Technologies named here
- Huntress tooling/SOC monitoring
- macOS
- Claude Code
- AppleScript
- MacBook
- Huntress
Techniques named here
- Malvertising via sponsored search results
- Base64 encoding and gzip compression
- Second-stage payload delivery
- Credential theft from macOS keychain
- Obfuscated AppleScript execution
Threat actors named here
- Unnamed attackers
Related in Threat Intel
 huntress.comwriteup
Reverse Engineering the Six Stages of MacSync Stealer and RAT
 huntress.comwriteup
AI-Coded Malware | Analyzing Vibe-Coded AD Enumeration | Huntress

 blog.talosintelligence.comtool
Introducing CAIRN: Frontier tracking for AI-integrated malware (Cisco Talos)
 huntress.comwriteup