 horizon3.aiadvisory
CVE-2026-76268 | Splunk Enterprise Patroni REST API Missing Authentication Vulnerability
CVE-2026-76268 is a critical (CVSS 9.8) missing authentication flaw (CWE-306) in the Patroni REST API on Splunk Enterprise search head cluster members. An unauthenticated attacker with network access can run operating-system commands. Affected: 10.4.0 to 10.4.2 and 10.2.0 to 10.2.6. Fixed in 10.4.3 and 10.2.7. Splunk (SVD-2026-1001, 7 October 2026) suggests disabling the PostgreSQL sidecar as a workaround.
What it is
CVE-2026-76268 is a critical (CVSS v3.1 9.8, vector CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H) missing authentication flaw (CWE-306) in the Patroni REST API on Splunk Enterprise search head cluster members. Splunk published advisory SVD-2026-1001 on 7 October 2026.
How it works
The Patroni REST API does not require authentication for critical configuration operations. An attacker who can reach the interface can abuse those operations to run operating-system commands. The page gives no further detail on the specific endpoints or request sequence.
Preconditions / Affected
Internet exposure is not required. Anyone with internal network access to the affected interface can exploit it, with no credentials and no user interaction.
- Affected: Splunk Enterprise 10.4.0 through 10.4.2, and 10.2.0 through 10.2.6.
- Not affected: 10.0.x and 9.4.x.
- Fixed: 10.4.3 or later in the 10.4 branch, and 10.2.7 or later in the 10.2 branch.
What to do
Upgrade to a fixed version. If you cannot upgrade yet and do not use Edge Processor, OpAmp, or SPL2 data pipelines, Splunk recommends disabling the PostgreSQL sidecar. In $SPLUNK_HOME/etc/system/local/server.conf, set:
[postgres]
disabled = true
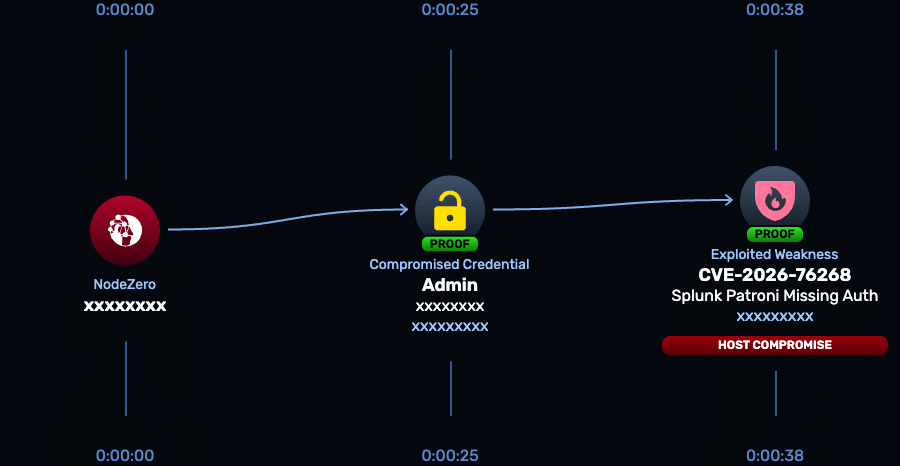
Then restart Splunk Enterprise. Horizon3 also offers a NodeZero Rapid Response test to check exploitability before patching and to confirm the fix afterwards.
Caveats
- The workaround breaks Edge Processor, OpAmp, and SPL2 data pipelines, so use it only when none of them are in use.
- Splunk's advisory does not report active exploitation. A public repository contains code presented as a proof of concept, and the page does not say whether it works.
- The page's timeline leaves the date of the NodeZero test as an unfilled placeholder.
Organisations named here
- NodeZero
- SVD-2026-1001
CVEs named here
- CVE-2026-76268
Technologies named here
- Missing Authentication for Critical Functionality
- Splunk
- PostgreSQL
- CVSS
- CVSS v3.1
- NodeZero Proactive Security Platform Rapid Response
- Patroni
- Splunk advisory SVD-2026-1001
- Splunk Enterprise 10.2.0 through 10.2.6 (Patroni REST API on search head cluster members)
- Splunk Enterprise 10.4.0 through 10.4.2 (Patroni REST API on search head cluster members)
Related in Offensive Security

 huntress.comwriteup
AI-Coded Malware | Analyzing Vibe-Coded AD Enumeration | Huntress
 github.comrepo
YesWeHack Claude Kit
 huntress.comwriteup
Inside an Oracle Database SQL Injection Attack | Huntress
 huntress.comwriteup