 huntress.comwriteup
Threats Plague Educational Organizations
Huntress details three real 2025 incidents against the education sector: an RDP brute-force into a school district's exposed domain controller (10 open ports), an Atera RMM instance at an MSP compromised to deploy AnyDesk and add a backdoor local admin account "WDAGUtilltyAccount" with the reused password Ujmqaz5055 across multiple downstream school customers, and an RClone-based exfiltration of a high school's financial and family-email directories following RDP brute-forcing. It also cites Huntress 2025 Cyber Threat Report stats showing education as 21% of all observed incidents, with malicious scripts, Chromeloader infostealers, and RMM abuse being the top threat categories, alongside references to prior breaches (PowerSchool, LAUSD, Howard University, Minneapolis Public Schools/Medusa ransomware).
What it is
A Huntress EDR field report on how attacks against K‑12 and higher‑ed actually unfold, built around three 2025 incidents. Beyond the headline stats, it names concrete artifacts an engineer can hunt for: a rogue admin account, a specific AnyDesk drop path, and RClone exfiltration targets.
How it works
Three observed intrusion patterns:
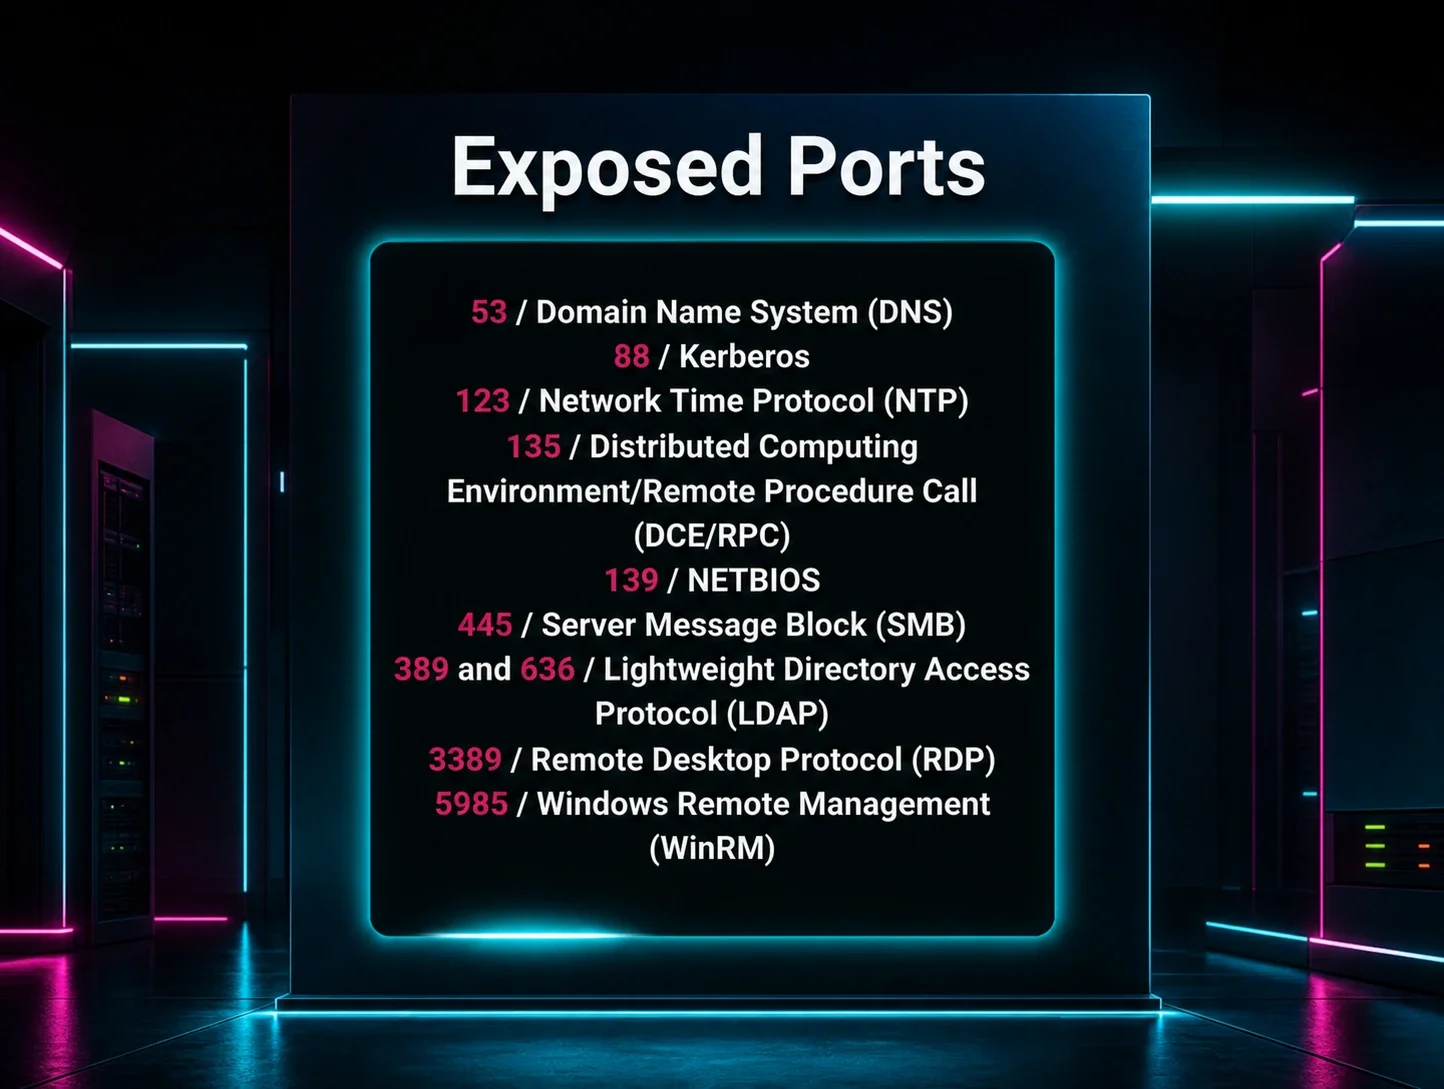
- RDP brute force → exposed DC: A malicious authentication from a known-adversary public IPv4 hit an exposed RDP instance (surfaced via retrospective threat hunt, not real-time alert). The affected host was exposing ~10 ports publicly — RDP through SMB — indicating a misconfigured firewall, and was exposing its domain controller.
- RMM supply-chain: A compromised Atera RMM instance at an MSP was used to reach downstream customers. A process running as SYSTEM executed
C:\ProgramData\AnyDesk.exe, installed a second AnyDesk instance for persistence, then created local admin WDAGUtilltyAccount (note the misspelling) with password Ujmqaz5055 — a password Huntress has seen reused across multiple intrusions. - RClone exfil: An actor downloaded RClone and targeted directories for the main office, financials, and student/family emails.
Preconditions / Affected
Internet-exposed RDP/SMB, DCs reachable from public IPs, and — critically — reliance on RMM tools. Huntress notes RMM abuse ran slightly higher in education than other sectors due to heavy remote-administration dependence, so an MSP compromise cascades to every downstream district.
What to do
Hunt for the named artifacts, all reproducible in your own telemetry:
- Local admin account
WDAGUtilltyAccount(misspelled variant of the legitimateWDAGUtilityAccount) and the passwordUjmqaz5055. - AnyDesk executing from
C:\ProgramData\AnyDesk.exe, especially spawned by a SYSTEM-context RMM process; watch for a second RMM installed on a host that already runs one. - RClone presence or execution — a sync tool with no business appearing on endpoints, used here for exfil.
- Audit external exposure of RDP and SMB; confirm domain controllers are not publicly reachable.
- On RMM compromise: remove the rogue admin, rotate RMM (Atera) credentials, and remove the malicious AnyDesk instance — the exact remediation Huntress performed.
Detection note: the RDP intrusion was caught only by a retrospective hunt pivoting on a known-malicious public IPv4, not by a live alert — so threat hunting on adversary-reused IPs matters.
Caveats
These are point-in-time incidents caught mid-attack; Huntress intervened before escalation, so downstream impact is what could have happened, not what did. The infostealer detail worth carrying: Chromeloader was ~70% of all infostealer incidents in education.
Organisations named here
- Los Angeles Unified School District ransomware attack
- Minneapolis Public Schools breach
- PowerSchool breach
- Ujmqaz5055
- WDAGUtilltyAccount
Technologies named here
- PowerSchool
- Huntress Managed EDR
- Huntress Managed SIEM
- Atera RMM
- AnyDesk
- RClone
- Atera
- RDP
- SMB
- Domain controller
- EDR
- SIEM
Techniques named here
- Phishing against faculty and students
- Exposed RDP targeting / brute force
- RMM abuse
- Malicious authentication via exposed public IPv4
- Adding malicious local administrator account
- Data exfiltration via RClone
- Lateral movement
Threat actors named here
- Chromeloader
- Medusa ransomware
- Unidentified threat actor
Related in Threat Intel
 huntress.comwriteup
Reverse Engineering the Six Stages of MacSync Stealer and RAT
 huntress.comwriteup
AI-Coded Malware | Analyzing Vibe-Coded AD Enumeration | Huntress

 blog.talosintelligence.comtool
Introducing CAIRN: Frontier tracking for AI-integrated malware (Cisco Talos)
 huntress.comwriteup