 x.comthread
Dark Web Informer (@DarkWebInformer) on X
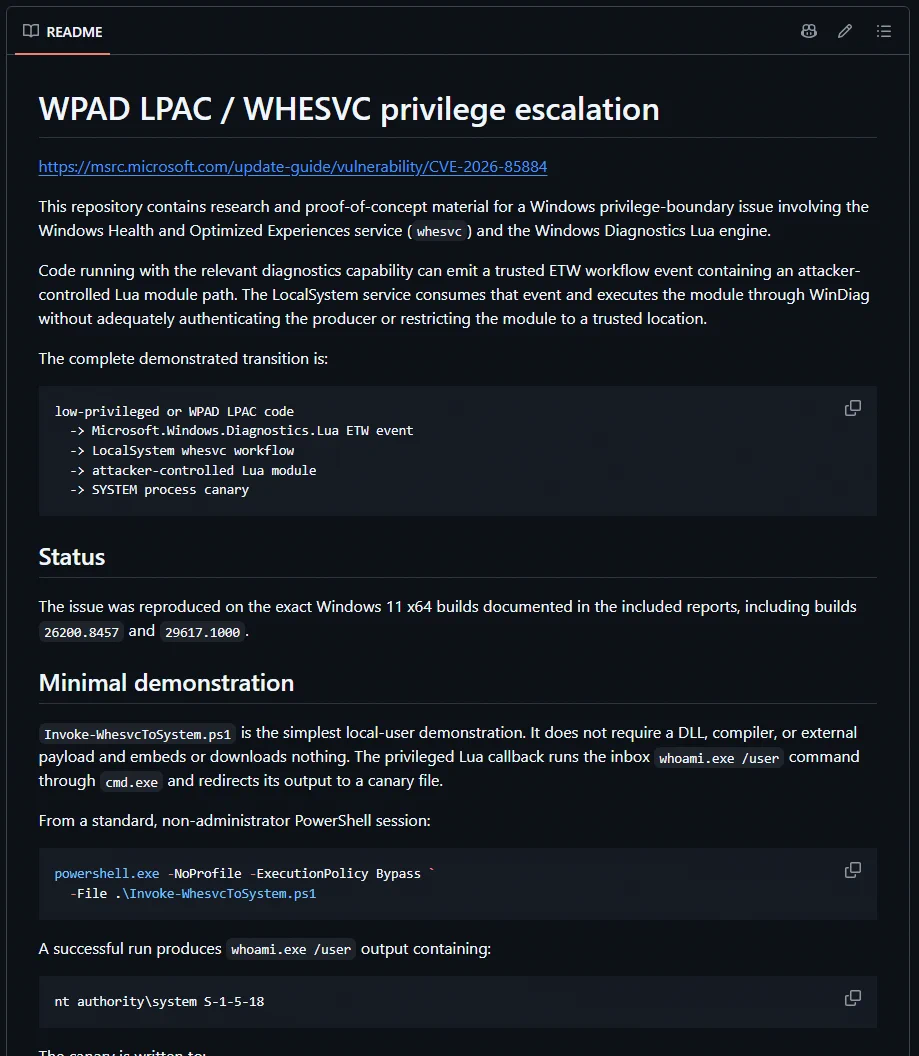
DarkWebInformer post on a PoC for CVE-2026-85884, a Windows 11 local privilege escalation in the Windows Health and Optimized Experiences service. Low-privileged code can trigger a trusted ETW event carrying an attacker-controlled Lua module path. The LocalSystem whesvc service then runs that module through WinDiag without validating the event producer or restricting the module location. The PoC takes a standard non-admin PowerShell session to NT AUTHORITY\SYSTEM on Windows 11 x64 builds including 26200.8457 and 29617.1000.
TL;DR PoC for CVE-2026-85884: Windows 11 whesvc runs an attacker-supplied Lua module from a forged ETW event, giving local SYSTEM.
Organisations named here
- whesvc
- WinDiag
- Windows Health and Optimized Experiences
CVEs named here
- CVE-2026-85884
Technologies named here
- Windows 11 x64 builds including 26200.8457 and 29617.1000
- WinDiag
- Windows
- ETW
- Lua
- PowerShell
Related in Offensive Security

 huntress.comwriteup
AI-Coded Malware | Analyzing Vibe-Coded AD Enumeration | Huntress
 github.comrepo
YesWeHack Claude Kit
 huntress.comwriteup
Inside an Oracle Database SQL Injection Attack | Huntress
 huntress.comwriteup