 socket.devarticle
Socket: Introducing Manifest Alerts
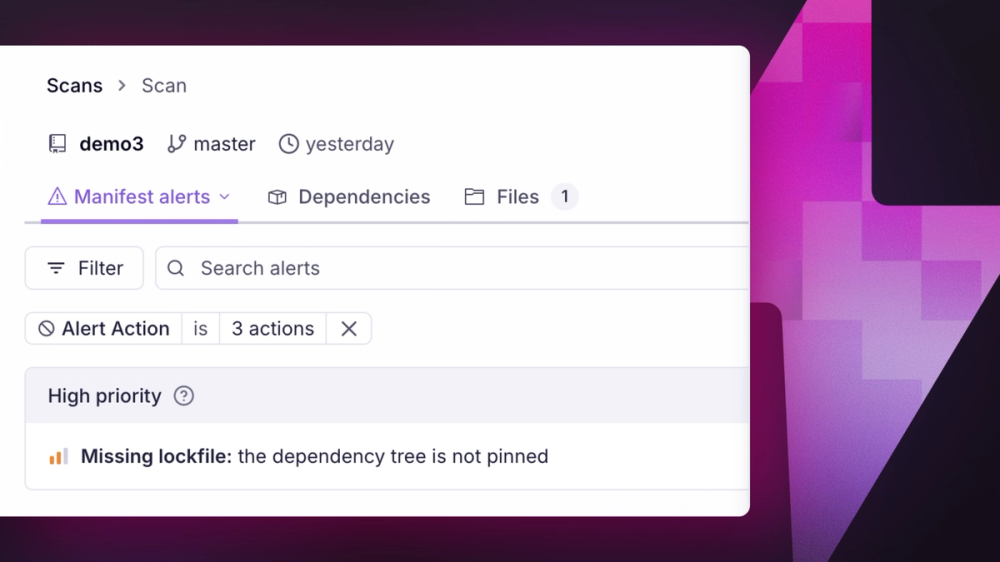
Socket announces Manifest Alerts, a new alert type that flags application repositories missing a lockfile (e.g. package.json without package-lock.json), separate from its existing per-dependency Dependency Alerts. The feature was motivated by the Axios npm compromise, where repos without committed lockfiles had a wider, harder-to-verify blast radius because fresh installs could resolve to different dependency versions than expected. Alerts include impact explanation and package-manager-specific remediation guidance for npm, pnpm, yarn, and bun.
TL;DR Socket adds "Manifest Alerts" to flag missing lockfiles that make dependency resolution non-reproducible, prompted by the Axios npm compromise.
Technologies named here
Techniques named here
- Missing lockfile detection
- Dependency resolution drift
Threat actors named here
- Axios npm compromise
Related in Supply Chain






