 aikido.devarticle
The CVE spike across major software companies is a remediation problem
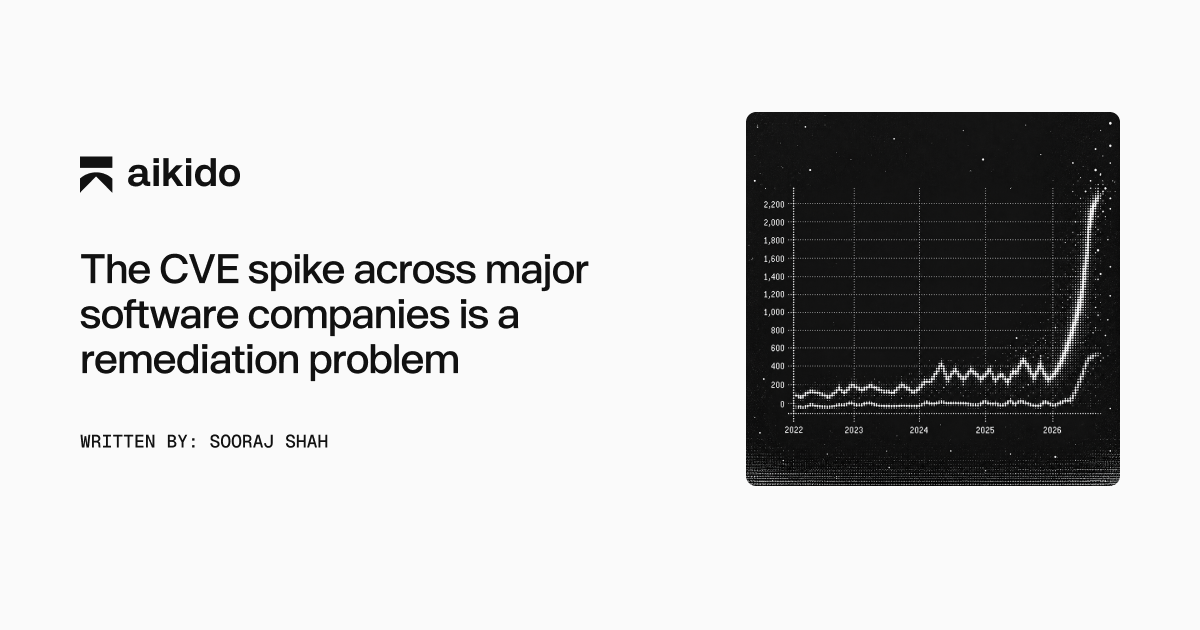
Aikido argues the widely-shared a16z/Epoch AI chart showing critical/high CVEs jumping from under 100/month to over 600/month since spring 2026 reflects AI accelerating vulnerability discovery, not a real spike in danger — since CISA's KEV count has stayed flat. It details how NIST's NVD, overwhelmed by volume, let its scoring backlog balloon from 13,000 to 27,000 CVEs in 18 months and pivoted to only prioritizing federal/critical/KEV-listed CVEs, while Verizon's 2026 DBIR found only 26% of confirmed actively-exploited KEV vulnerabilities were fully remediated in 2025 (down from 38%) with median patch time rising to 43 days. It illustrates the point with StyleSmuggler, an unauthenticated RCE hitting Adobe Commerce and Magento Open Source that had no CVE or vendor advisory, which Aikido Intel flagged and Aikido Libraries auto-patched more than 24 hours before Adobe's own hotfix.
Organisations named here
- a16z
- Epoch AI
- Verizon DBIR
Technologies named here
- Aikido Intel
- Adobe Commerce
- Aikido Libraries
- Magento Open Source
- Aikido Autofix
- Aikido reachability analysis
- Aikido CVE Exploitability Analysis
- CISA KEV list
- Magento
- Aikido Security
- NVD
- CVSS
- CISA KEV
- NIST
Techniques named here
- Unauthenticated remote code execution
- Reachability analysis
- CVE Exploitability Analysis
- AI-assisted vulnerability discovery
Threat actors named here
- Stylesmuggler
Related in AppSec
 github.comadvisory
Flowise MCP Security Bypass Enables RCE

 huntress.comwriteup
Inside an Oracle Database SQL Injection Attack | Huntress
github.comrepoOASIS

 blog.trailofbits.comwriteup