 huntress.comarticle
Phishing Techniques Spotted: Email Examples & Red Flags
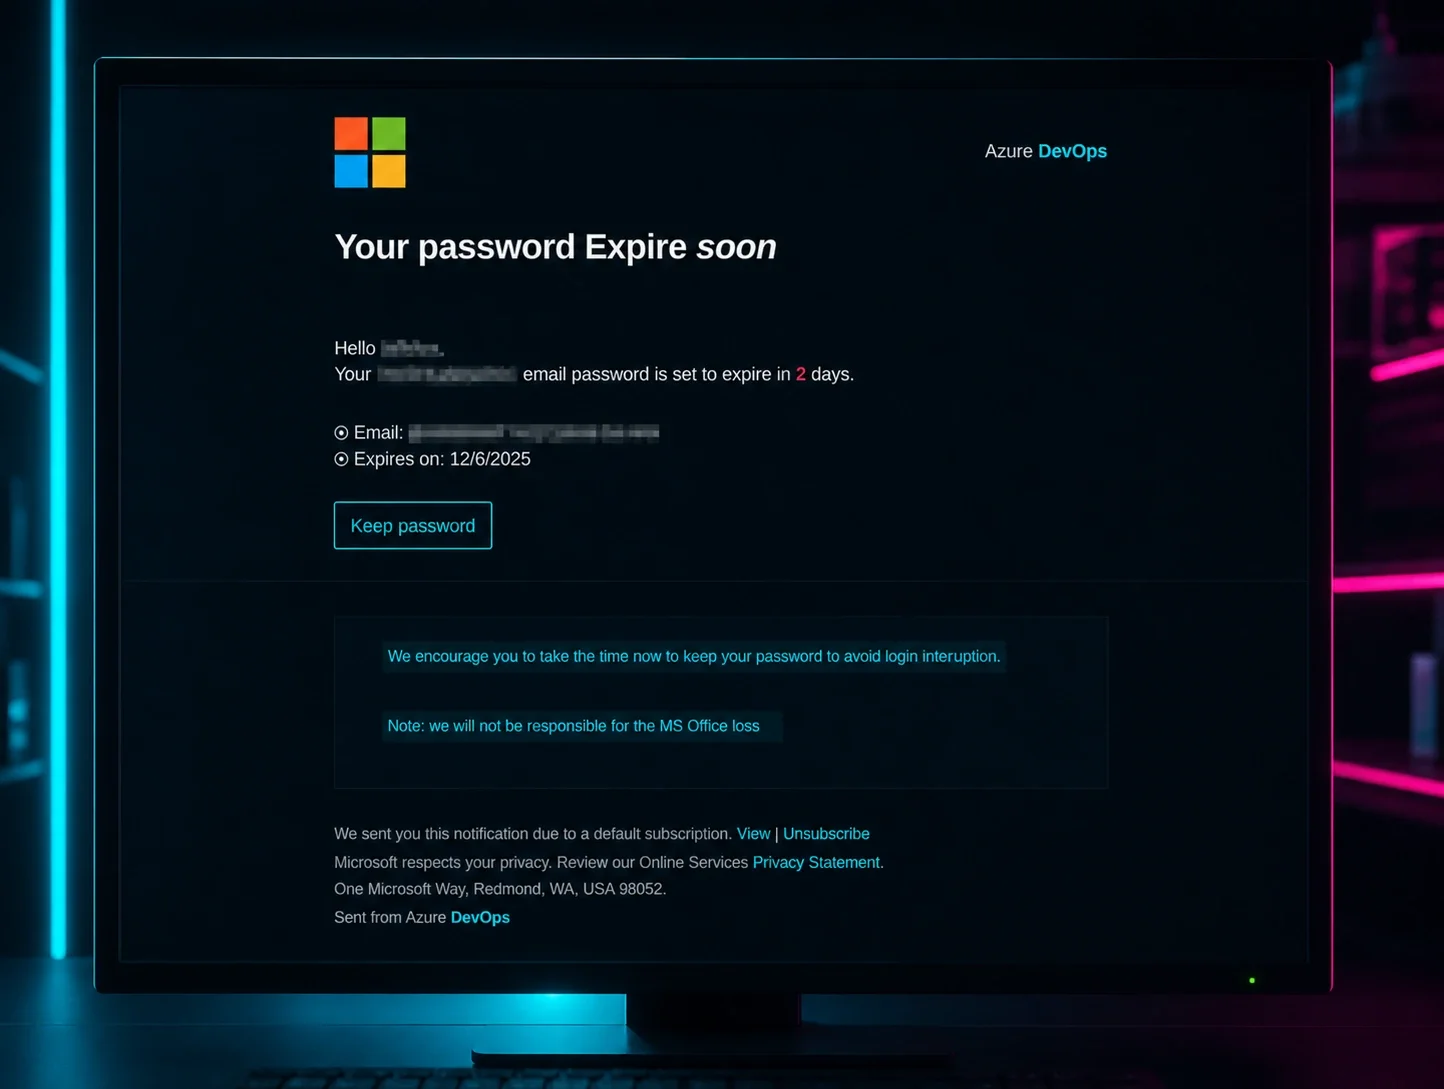
Huntress researchers break down five phishing techniques observed in 2025: voicemail-lure emails using obfuscated SVG attachments and the Raccoon0365 phishing kit to redirect victims to fake Microsoft login pages; callback phishing that lures victims to call a fake Visa support number; Microsoft/Docusign brand impersonation abusing open URL redirects on nypost.com; FedEx shipping-notification phishing using an ASCII-rendered QR code to evade image scanning; and Living off Trusted Sites (LoTS) attacks that route victims through legitimate services like Figma and Cloudflare Turnstile before landing on credential-phishing pages. Each example includes specific evasion tradecraft attackers use to bypass email security gateways and detection tools.
Organisations named here
- ASCII QR code
Technologies named here
- Microsoft 365 / Microsoft Teams
- Cloudflare Turnstile
- Huntress managed security awareness training
- Docusign
- Dropbox
- ShareFile
- FedEx
- Visa
- Figma
- Canva
- Microsoft 365
- Cloudflare
Techniques named here
- Voicemail lure phishing
- SVG attachment obfuscation
- Callback phishing
- Brand impersonation
- Open URL redirect abuse
- Shipping notification phishing
- ASCII QR code phishing
- Living off Trusted Sites
- Sender abuse / platform abuse
- CAPTCHA/Turnstile abuse for detection evasion
Threat actors named here
- Raccoon0365
Related in Threat Intel
 huntress.comwriteup
Reverse Engineering the Six Stages of MacSync Stealer and RAT
 huntress.comwriteup
AI-Coded Malware | Analyzing Vibe-Coded AD Enumeration | Huntress

 blog.talosintelligence.comtool
Introducing CAIRN: Frontier tracking for AI-integrated malware (Cisco Talos)
 huntress.comwriteup