 endorlabs.comarticle
Everything, everywhere, all at once… the week software broke | Endor Labs
Endor Labs roundup of the 20 to 21 October 2026 patch wave: eMudhra certificate authority keys that anyone can recover, PHP2Shell (CVE-2026-109618, CVE-2026-109619), Node2Shell (CVE-2026-111497) and malware in LiteLLM 1.107.0. It lists fixed versions (PHP 8.2.35 to 8.5.12, Node.js 22.23.4, 24.22.1, 26.12.1, LiteLLM back to 1.106.2) and explains why many separate trust-store copies each need updating. It closes with advice on triage, remediation and SBOM/VEX reporting.
What it is
Endor Labs summarised four separate problems disclosed between 20 and 21 October 2026: bad eMudhra certificate authority keys, two PHP bugs (PHP2Shell), a Node.js Brotli bug (Node2Shell) and malware in LiteLLM 1.107.0. In each case the fix is to update something the reader did not write, often a base image, a runtime or a bundled trust store.
How it works
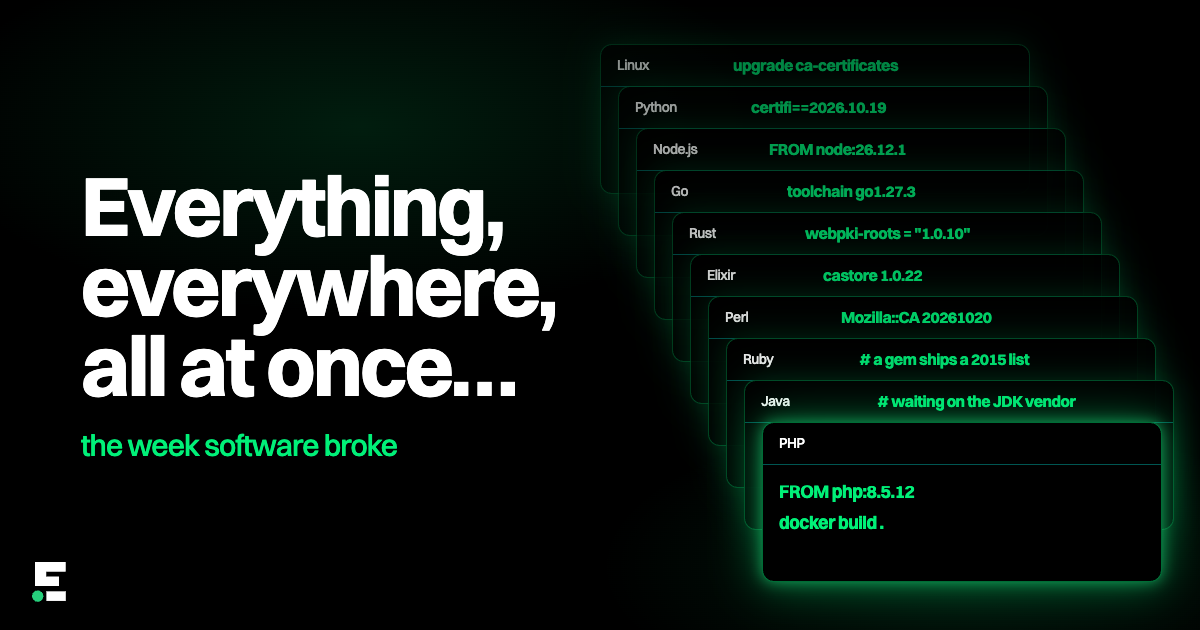
- eMudhra: eight CA keys were generated so badly that anyone can recover them. Six can impersonate any website or service to software that still trusts them. Browsers already block them. Other software keeps its own trust lists (the OS, certifi, pip, uv, Node.js, Go, Java, and private copies inside libraries), so each needs a separate fix. Endor Labs found 25 fairly popular packages with a private copy, 11 already patched.
- PHP2Shell (CVE-2026-109618, CVE-2026-109619): two critical bugs in PHP itself allow unauthenticated code execution. Updating WordPress or its plugins does not help.
- Node2Shell (CVE-2026-111497): a bug in the Brotli decompression code can allow code execution if the app decompresses attacker-controlled data.
- LiteLLM 1.107.0: malware steals cloud credentials, developer secrets and AI tool logins. It runs every time Python starts, even if LiteLLM is never imported. On 21 October the
latest,main-latestandmain-stableDocker tags all pointed to it.
Preconditions / Affected
Anyone running PHP from a Docker base image or hosting provider, Node.js apps that decompress untrusted Brotli data, any Python environment where LiteLLM 1.107.0 was installed, and any stack with a trust store that still includes the eMudhra roots. The page names at least nine languages and six Linux distributions as needing updates.
What to do
- Upgrade PHP to 8.2.35, 8.3.36, 8.4.27 or 8.5.12. Rebuild images that include PHP and ask the hosting provider whether it has patched.
- Upgrade Node.js to 22.23.4, 24.22.1 or 26.12.1, then rebuild images. Node.js 20 has no fix.
- Move LiteLLM back to 1.106.2. If Python ran anywhere 1.107.0 was installed, replace every key and password that machine could reach. Do not run Python or pip on it to investigate.
- For certificates, update to the fixed versions, rebuild images and test that code rejects the bad certificates. The page points to a separate eMudhra write-up for a one-line curl test, a script that finds hidden certificate lists and ready-made queries. It does not reproduce them.
- For triage, the page asks whether every app and container can be queried for vulnerable components, whether upgrades can be checked for breakage, and whether SBOM and VEX files can be generated.
Caveats
The per-language fixed-version table for the certificate fixes is not in the fetched text, and the page says the certificate fix list keeps growing. Endor Labs states it cannot see certificate lists on hosts, network appliances, IoT devices or third-party services. Private copies inside packages are hard to detect through dependency analysis until each is confirmed. The tool coverage claims come from the vendor.
Organisations named here
- eMudhra
CVEs named here
- CVE-2026-109618
- CVE-2026-109619
- CVE-2026-111497
Technologies named here
- Endor Labs SCA scans
- Endor Labs container scanning
- Endor Labs Threat Center
- Endor Labs package firewall
- SBOM and VEX files
- Node.js security advisory
- WordPress sites running on affected PHP versions
- Container images with an outdated ca-certificates package
- PHP
- Node.js
- LiteLLM
- Python
- pip
- Docker
Threat actors named here
- Malicious LiteLLM 1.107.0
- PHP2Shell
- Node2Shell
Related in Supply Chain






