 stepsecurity.ioarticle
New in the Threat Center: Compromised Components, Now Available via API
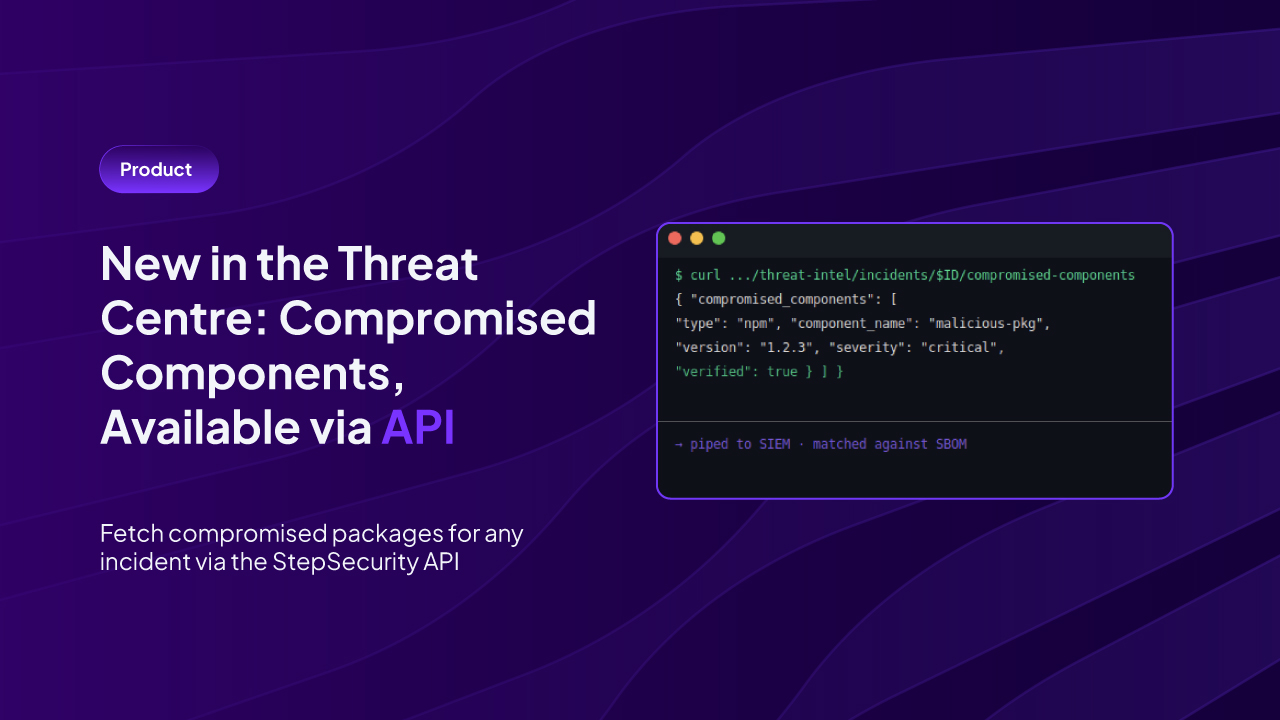
StepSecurity added a GET /github/{owner}/threat-intel/incidents/{incidentId}/compromised-components API endpoint to its Threat Center, returning structured data (package ecosystem, version, severity, verified status) for OSS components tied to a detected supply-chain compromise incident. It's positioned as the automatable counterpart to existing Threat-Intelligence detection events (SIEM/Slack/webhook alerts), PR-level compromised-package checks, and the Secure Registry, letting teams pull exact affected packages/versions on demand to drive incident response and cross-check against their SBOM or lockfiles.
TL;DR StepSecurity's Threat Center now exposes an API returning compromised package/version data per supply-chain incident, for automated response and SBOM correlation.
Technologies named here
- StepSecurity Threat Intelligence
- npm packages
- Threat Center
- GitHub Actions
- StepSecurity Compromised Components API
- NPM Package Compromised Updates Check
- Secure Registry
- SIEM integration
- StepSecurity
- SIEM
- SBOM
- tj-actions/changed-files
Techniques named here
Threat actors named here
- tj-actions incident
- nx incident
Related in Supply Chain







