 huntress.comwriteup
Fake Tech Support Delivers Havoc Command & Control
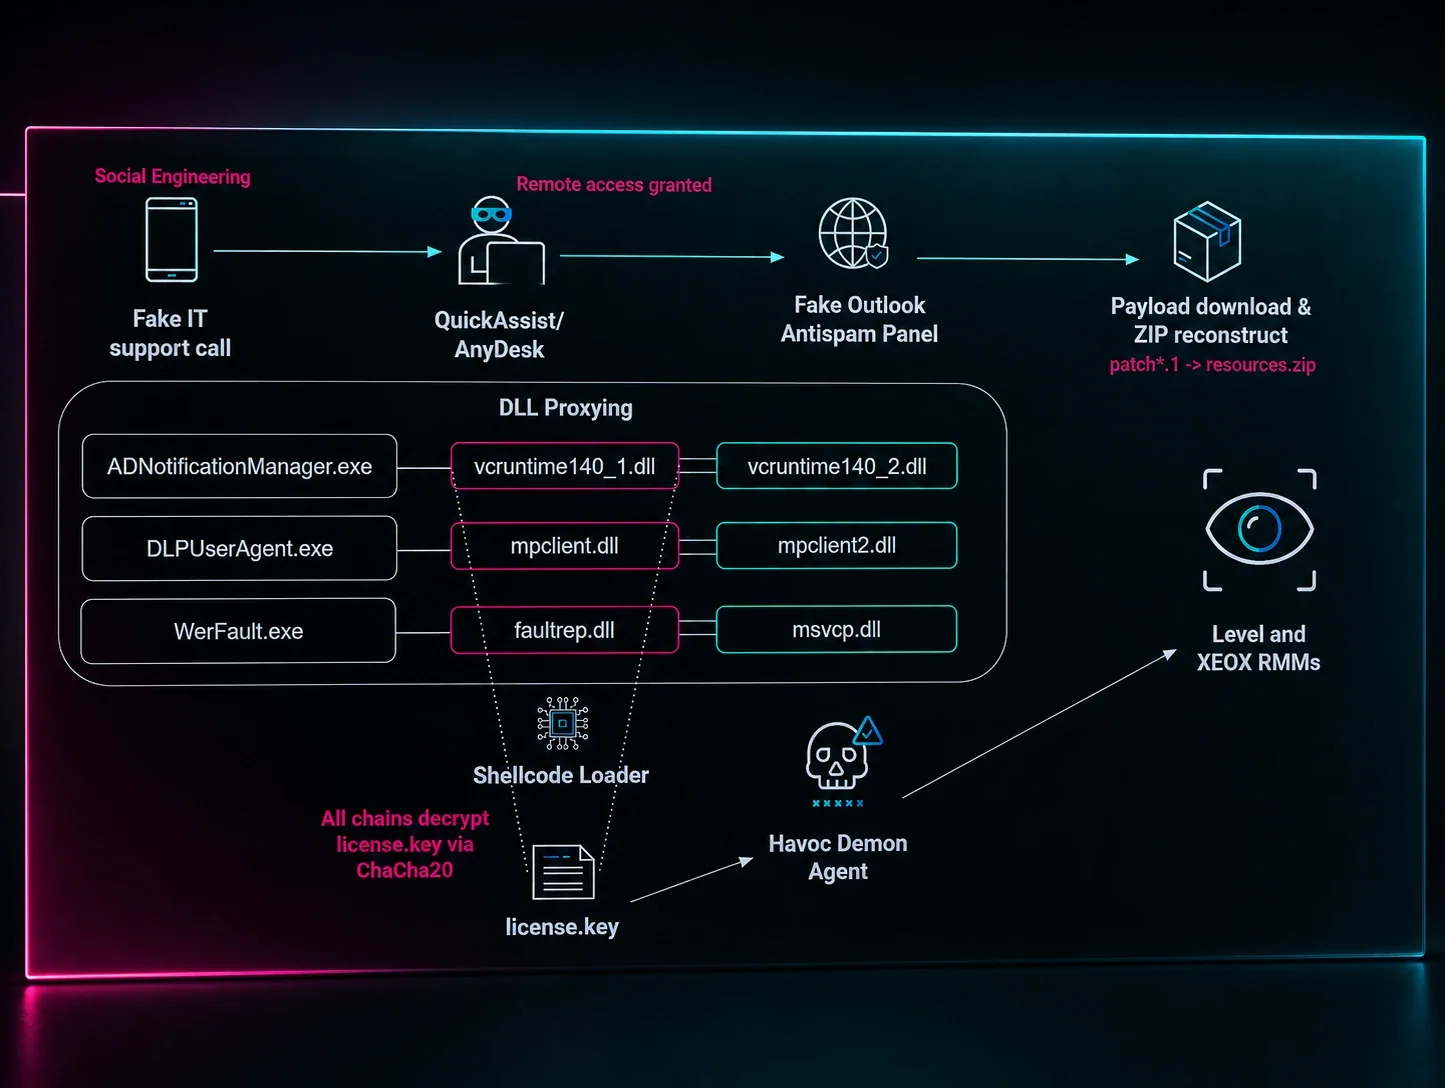
Huntress details a February 2026 intrusion cluster across five partner organizations combining fake tech support social engineering (spam bait, phone calls impersonating IT, QuickAssist/AnyDesk access, fake Outlook Antispam panel on AWS) with a customized Havoc Demon C2 agent using indirect syscalls, registry-based fallback C2, and DLL sideloading to evade EDR. Tradecraft overlaps with prior Sophos-documented Black Basta/FIN7 campaigns, suggesting affiliates or copycats reused the playbook; attackers reached nine additional endpoints within eleven hours, indicating likely ransomware/exfiltration intent.
TL;DR Huntress tracks a fake-IT-support campaign delivering a customized, EDR-evading Havoc C2 (indirect syscalls, DLL sideloading, registry fallback) with tradecraft echoing Black Basta/FIN7.
Organisations named here
- Havoc C2
- Havoc Demon
- QuickAssist
Technologies named here
- Havoc
- AnyDesk
- Microsoft Quick Assist
- Huntress
- Sophos
Threat actors named here
- BlackBasta
- FIN7
Related in Threat Intel
 huntress.comwriteup
Reverse Engineering the Six Stages of MacSync Stealer and RAT
 huntress.comwriteup
AI-Coded Malware | Analyzing Vibe-Coded AD Enumeration | Huntress

 blog.talosintelligence.comtool
Introducing CAIRN: Frontier tracking for AI-integrated malware (Cisco Talos)
 huntress.comwriteup