 x.comthread
Dark Web Intelligence (@DailyDarkWeb) on X
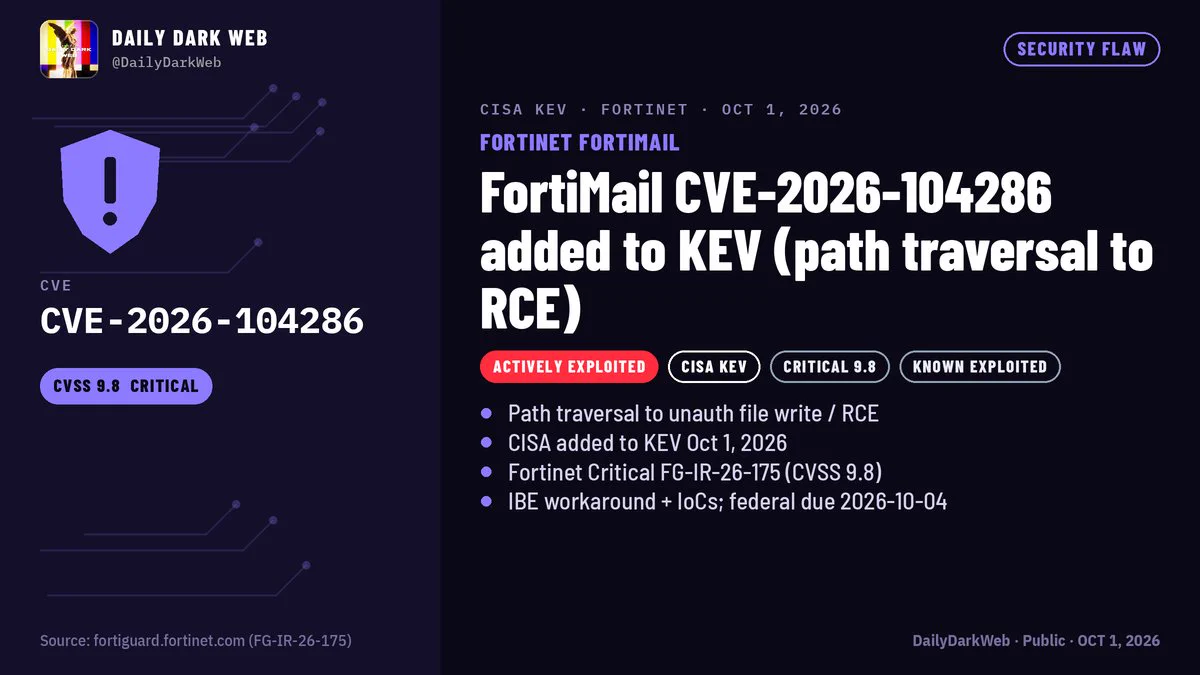
CISA added CVE-2026-104286, a critical (CVSS 9.8) path traversal and NULL-byte neutralization flaw in Fortinet FortiMail, to its Known Exploited Vulnerabilities catalog on October 1, 2026, citing active in-the-wild exploitation. The bug allows unauthenticated arbitrary file write via crafted HTTP/HTTPS requests on FortiMail 7.2.0–7.2.9, 7.4.0–7.4.8, 7.6.0–7.6.6, and 8.0.0–8.0.1, with fixes coming in 8.0.2/7.6.7/7.4.9+ and an interim workaround of disabling IBE and restricting management-interface internet access. Federal agencies face an October 4, 2026 BOD 26-04 remediation deadline, and Fortinet's advisory (FG-IR-26-175) includes IoCs for hunting.
Organisations named here
- FG-IR-26-175
CVEs named here
- CVE-2026-104286
Technologies named here
- Fortinet FortiMail
- CISA KEV
- CVSS
Techniques named here
- Path traversal
Related in Threat Intel

 huntress.comwriteup
Reverse Engineering the Six Stages of MacSync Stealer and RAT
 huntress.comwriteup
AI-Coded Malware | Analyzing Vibe-Coded AD Enumeration | Huntress

 blog.talosintelligence.comtool
Introducing CAIRN: Frontier tracking for AI-integrated malware (Cisco Talos)
 huntress.comwriteup