 huntress.comarticle
Tradecraft Tuesday Recap: axios npm Supply Chain Compromise
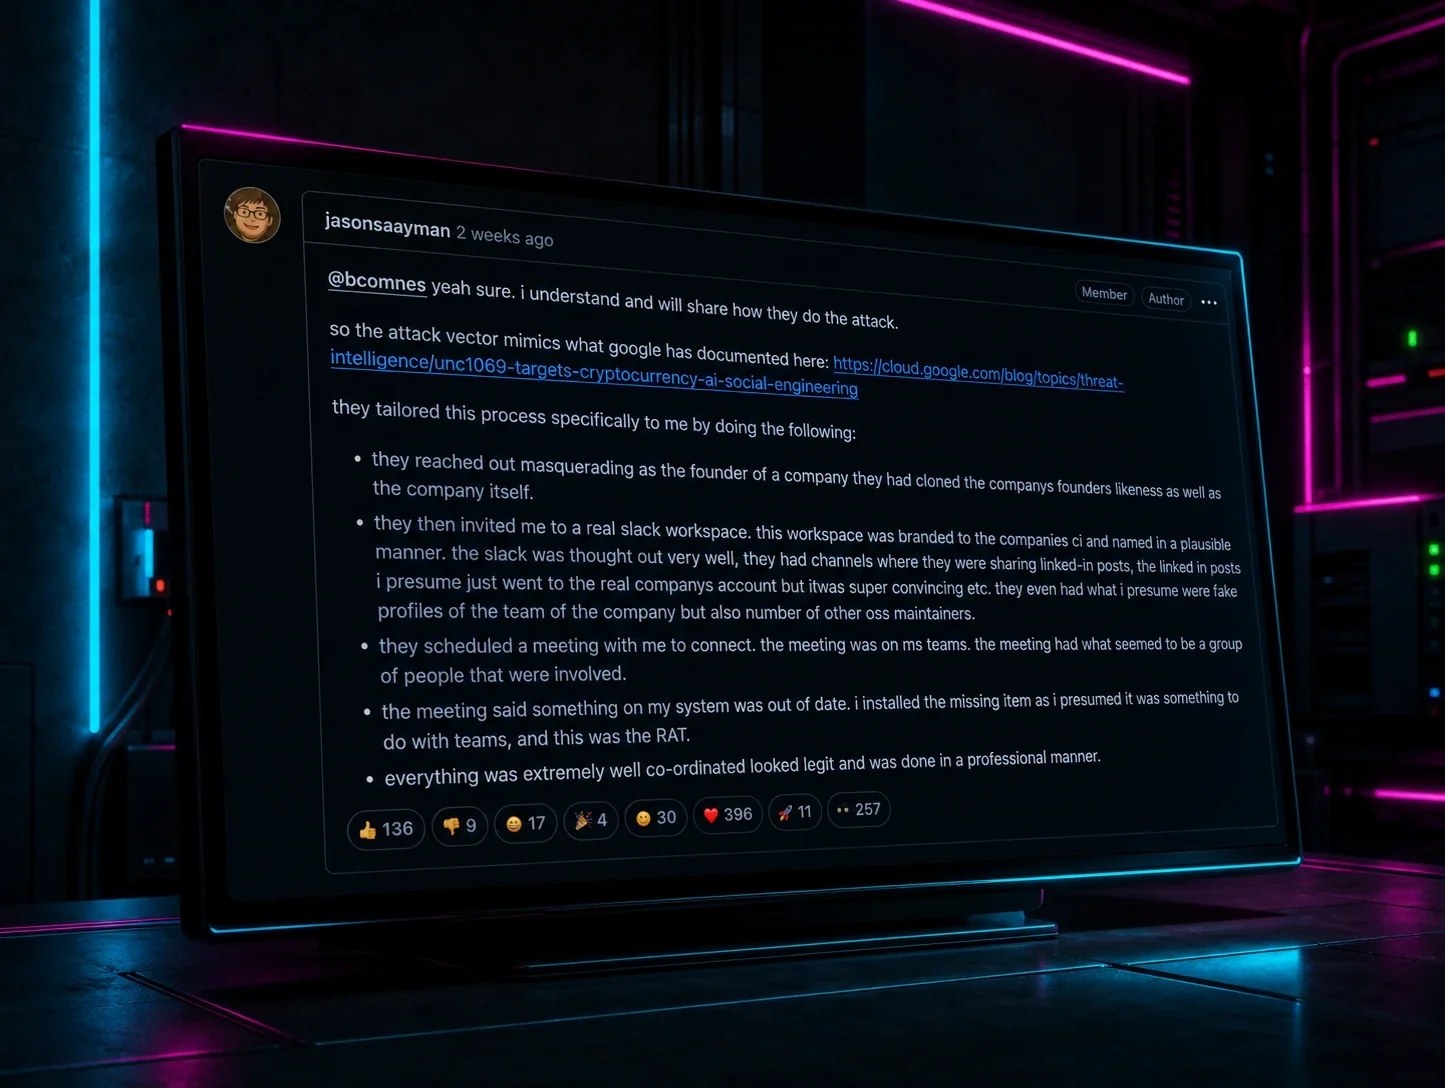
Huntress recaps its April Tradecraft Tuesday panel (with researchers from Wiz and Aikido Security) on the March 2026 axios npm supply chain compromise, in which attackers took over maintainer jasonsaayman's account via an elaborate fake-company/fake-Slack/Teams social-engineering scheme and published two backdoored axios releases ([email protected], [email protected]) carrying a cross-platform RAT. Huntress observed at least 135 endpoints contacting the attacker's C2 during the three-hour exposure window before npm pulled the versions, and Google attributed the campaign to UNC1069, a financially motivated DPRK-linked actor. The piece also contrasts the incident with other 2025-2026 npm attacks (qix account phishing, the Shai-Hulud worm, the Trivy/TeamPCP token-theft spread) and recommends dependency pinning, age-based version gating, and the Clean Source Principle as mitigations.
Organisations named here
- Ben Read
- Charlie Eriksen
- Clean Source Principle
- Jason Saayman
- Joe Desimone
- John Hammond
- Josh Junon
- Logan MacLaren
- Shai-Hulud
Technologies named here
- npm
- axios
- npm packages maintained by Josh Junon
- Trivy
- macOS, Windows, and Linux systems
- Wiz
- Aikido Security
- Huntress
Techniques named here
- Supply chain compromise via maintainer account takeover
- Social engineering of open source maintainer
- Cross-platform RAT deployment
- Command-and-control communication
- Credential harvesting and secret exfiltration to GitHub
- Phishing of package maintainer
- Stolen publish token abuse
Threat actors named here
- UNC1069
- Shai-Hulud
- TeamPCP
- DPRK
Related in Supply Chain







