 huntress.comarticle
LoTL Abuse: How to Spot It vs. Normal Admin Activity | Huntress
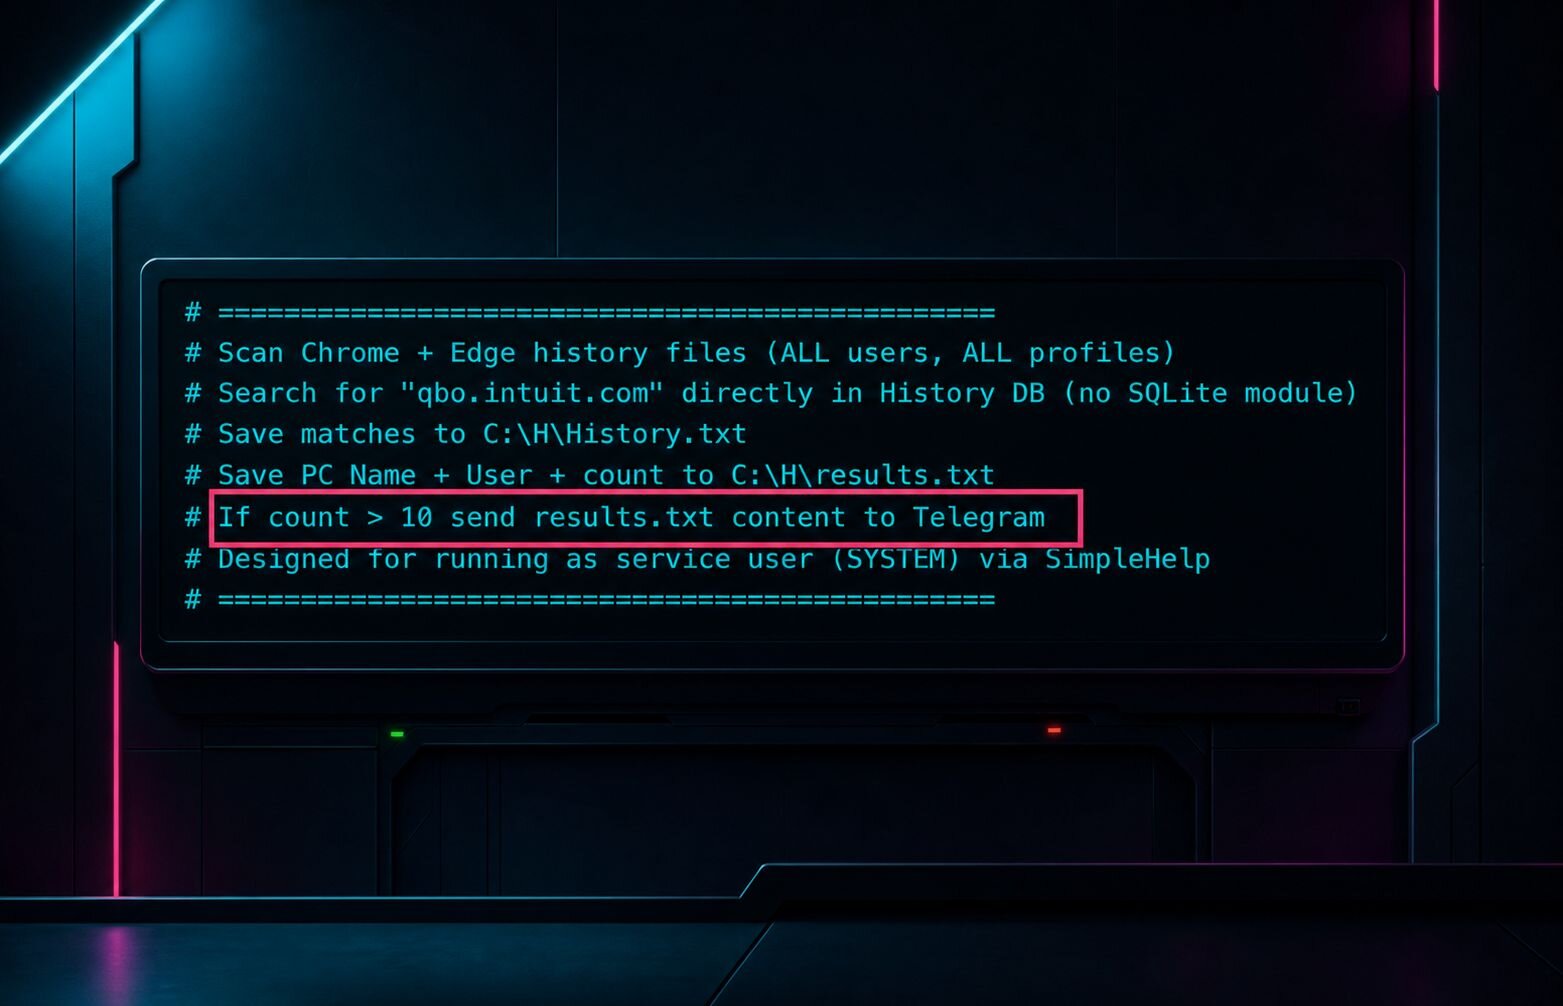
Huntress SOC breaks down how to differentiate legitimate admin use of native tools (PowerShell, WMI, RMM software) from living-off-the-land (LoTL) abuse by attackers, offering a four-point pressure test: who used the tool, where it ran, how it launched, and what followed. It includes real detection examples such as attackers using the legitimate RMM tool Action1 to deploy ScreenConnect for persistent access, a malicious process chain spawning from bomgar-scc.exe, and an LLM-generated script with code comments revealing Telegram-based exfiltration.
TL;DR Huntress SOC guide on spotting LoTL/LOLBins abuse (Action1→ScreenConnect, bomgar-scc.exe process chains) vs normal admin activity.
Technologies named here
- PowerShell
- WMI
- RMM tools
- Action1
- ScreenConnect
- bomgar-scc.exe
- Telegram
Techniques named here
- Living-off-the-land abuse
- RMM abuse
- Abnormal process chain / parent process anomaly
- Near-normal command-line usage
- Follow-on malicious activity after LoTL access
Related in Blue Team & Detection
 huntress.comwriteup
AI-Coded Malware | Analyzing Vibe-Coded AD Enumeration | Huntress

 blog.talosintelligence.comtool
Introducing CAIRN: Frontier tracking for AI-integrated malware (Cisco Talos)
 huntress.comwriteup
Inside an Oracle Database SQL Injection Attack | Huntress
 huntress.comwriteup