 endorlabs.comarticle
Endor Labs: AURI Agents
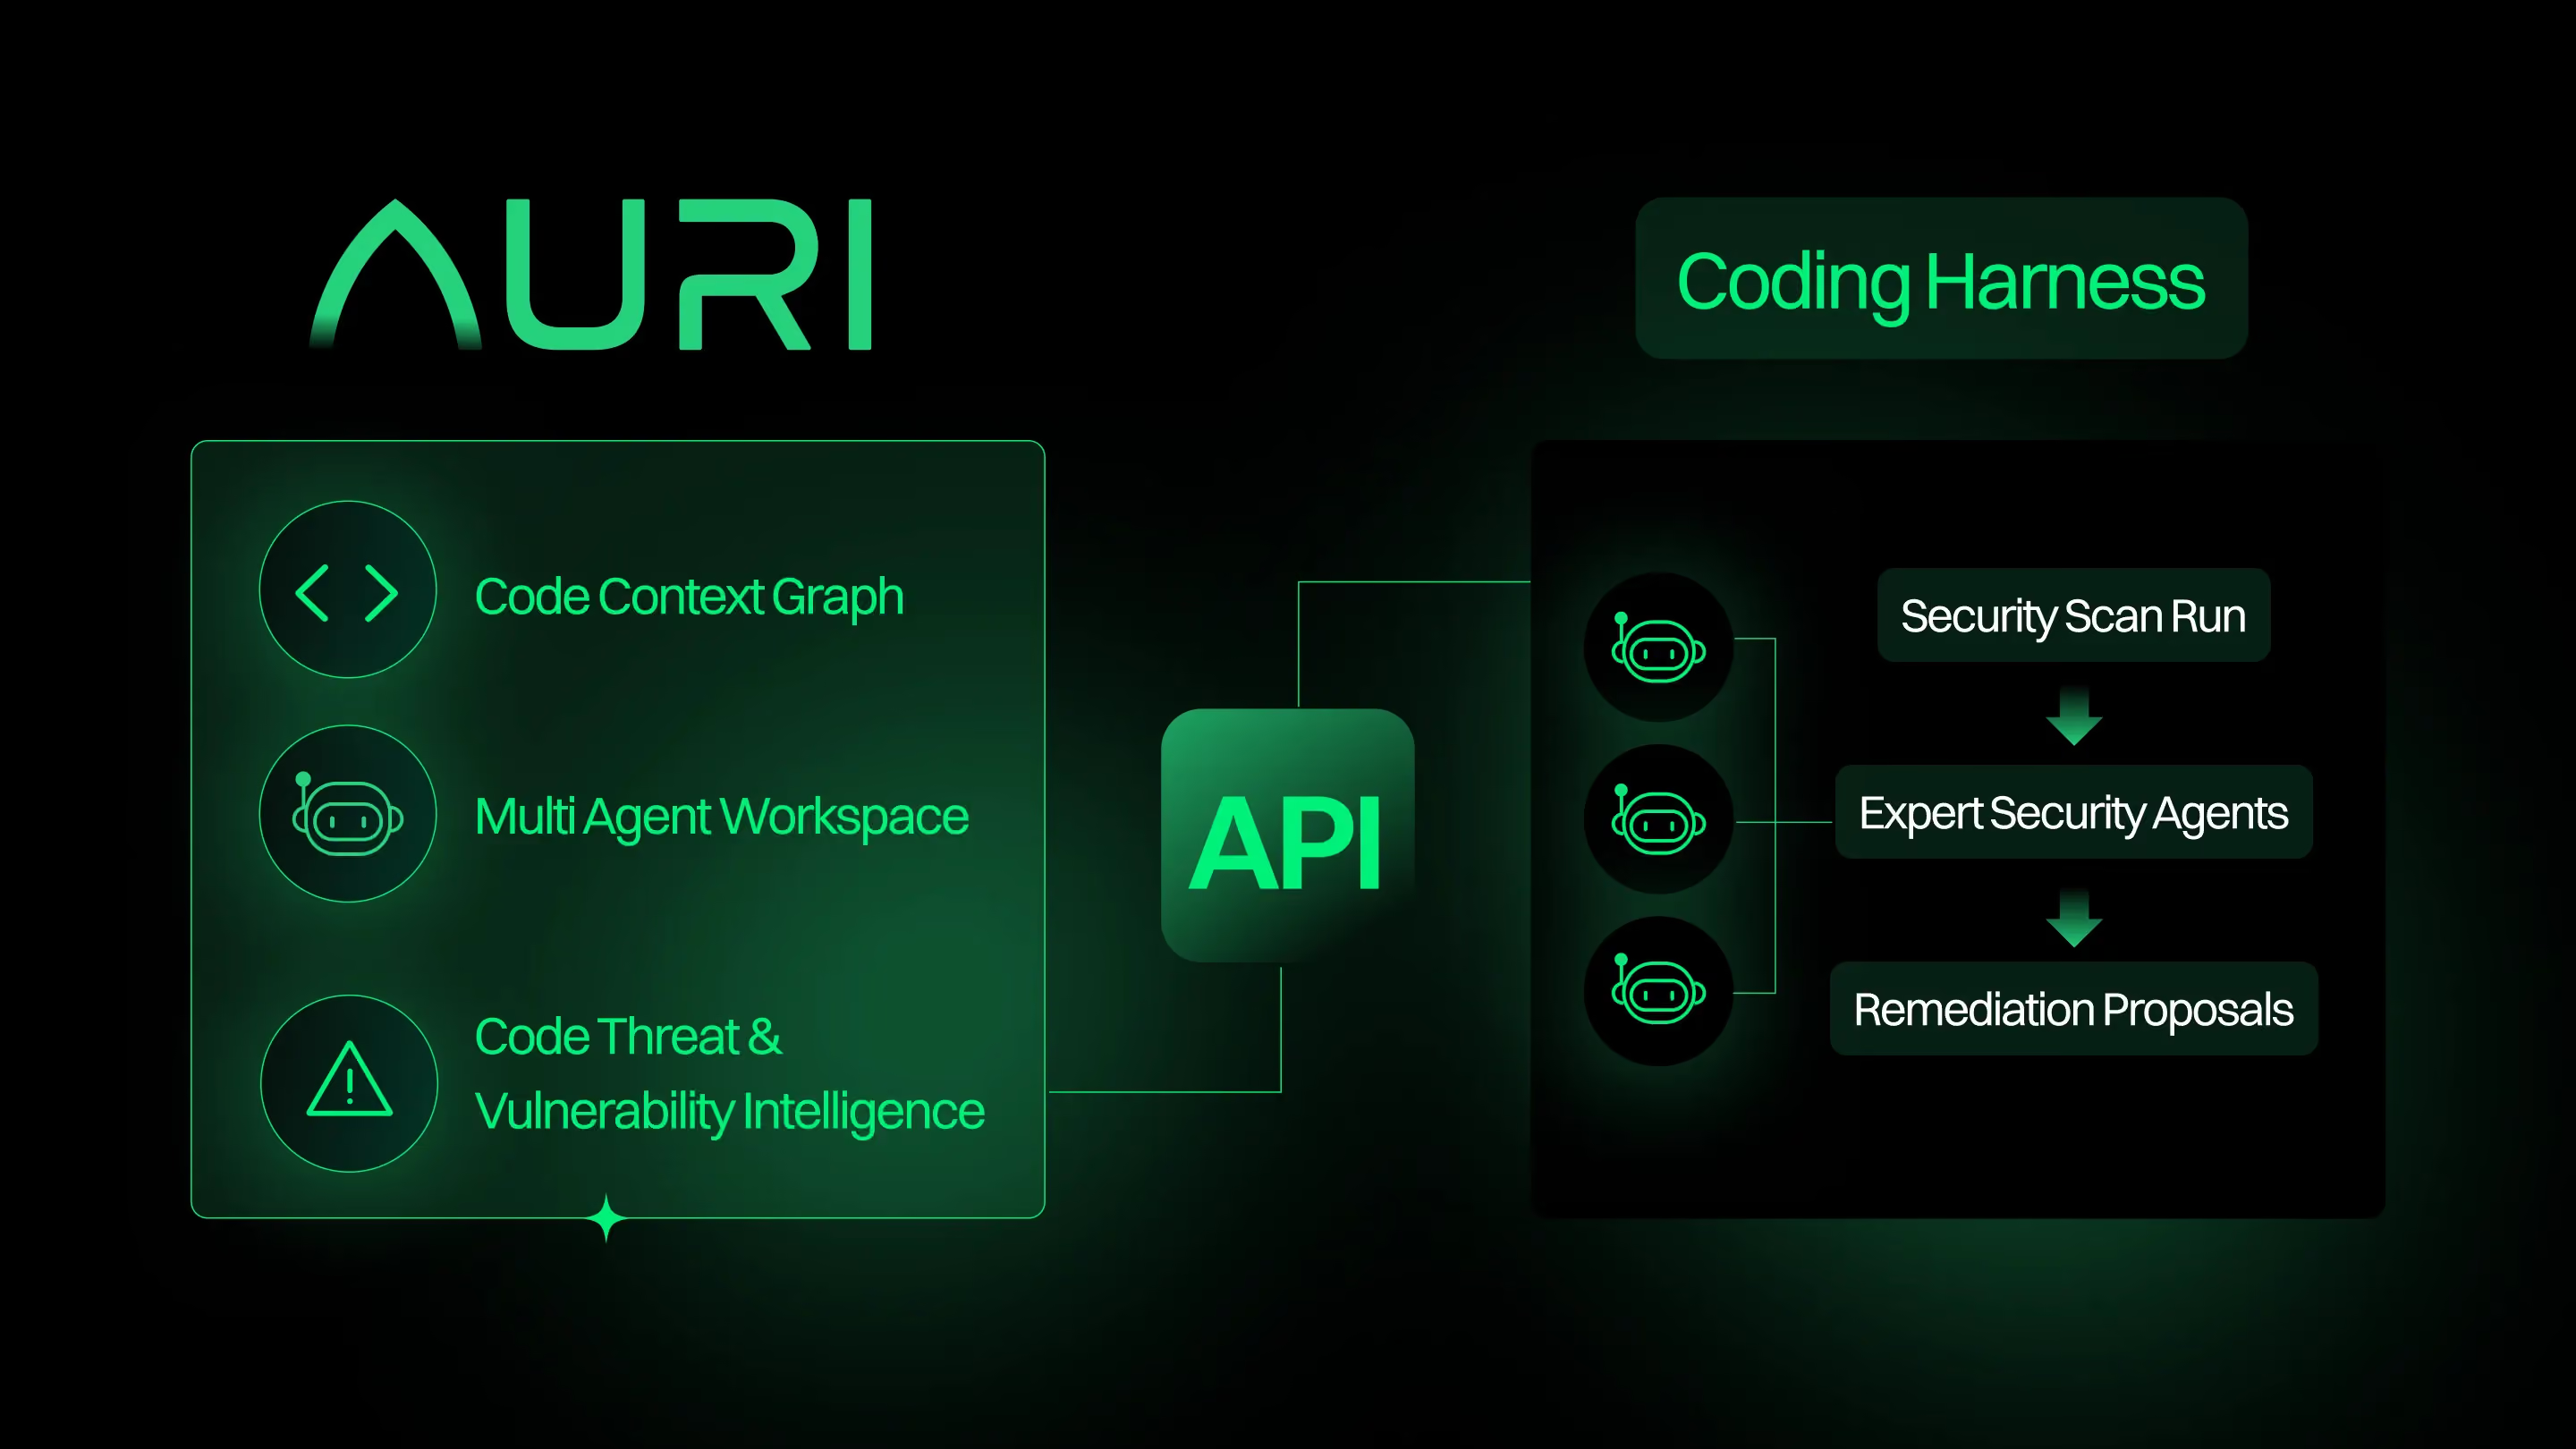
Endor Labs announces AURI Agents, a free catalog of pre-configured security agents (SCA Remediation, AI SAST Triage, Probe Droid, Endor Troubleshooter and six more). They run inside Claude Code, Codex, Cursor and similar hosts, using the user's own LLM keys and git credentials (GitHub via gh, GitLab via glab). The open-source Endor Labs Agent Kit defines each agent as a YAML Source Recipe plus markdown instructions, compiles it into per-host artifacts, and ships a skill that helps users author new agents with eval cases. Endor claims expert agents finish tasks 2.8x faster with 92% fewer tokens than an unaugmented agent. Mutating actions require confirmation and most agents are read-only.
What it claims
AURI Agents are task-specific security agents that pull Endor Labs' own analysis (reachability, upgrade impact, the finding and policy graph) into general-purpose coding agents. The page says they are "free for every Endor Labs customer". That means they assume an existing Endor Labs deployment and are not standalone tools. The page gives the launch count as both "ten" and "twelve". Its named list totals ten:
- Four core agents: SCA Remediation, AI SAST Triage, Probe Droid, Endor Troubleshooter.
- Six specialists: Remediation Planner, Upgrade Impact Analysis, Dependency Decision Helper, Package Risk Summary, Repository Dependency Reviewer, Vulnerability Explainer.
How it works
Each agent is grounded in Endor data, reached through the platform's existing agent surfaces: the API, an MCP server and the endorctl CLI.
- SCA Remediation chooses the fix using reachability and upgrade-impact analysis. It opens a PR with the supporting evidence in the PR body.
- AI SAST Triage confirms findings against the code at the exact commit SHA and patches the confirmed ones. It routes the rest with a stated reason. It also runs an exception flow: a developer requests an exception in a PR comment, and an AppSec reviewer approves it directly into policy.
- Remediation Planner previews fixes without opening PRs. It is the read-only alternative to SCA Remediation.
- Endor Troubleshooter classifies a failed scan and returns ordered remediation steps.
Agents can be chained with each other and with your own agents.
Execution happens on your side. Telemetry still leaves your environment:
flowchart LR
  subgraph Yours[Your infrastructure]
    H[Coding agent host] --> A[AURI agent]
    A -->|your LLM keys| L[LLM]
    A -->|gh / glab, confirm first| G[Git provider PRs]
  end
  A -->|endorctl auth| E[Endor Labs data]
  A -.->|telemetry| Hub[AURI Agent Hub]
How to use it
The prebuilt agents install as plugins or extensions by following the ai-plugins repo. You can also copy them from the Agent Kit repo. Claude Code example, verbatim from the page:
# Claude Code
mkdir -p .claude/agents
cp /path/to/endor-labs-agent-kit/claude-code/sca-remediation/sca-remediation.md \
  .claude/agents/sca-remediation.md
@agent-sca-remediation check this repository for P0 SCA findings I can start remediatingAuthentication uses your local endorctl configuration. Existing Endor users need no new setup.
For custom agents, install the "Create Endor Labs Agent" skill and describe the workflow in plain English. The skill generates:
- the recipe
- the prompt
- eval cases
- an architecture diagram
It then validates the result against the same guardrail checks the shipped agents must pass. You can keep custom agents private or submit them as a PR. Endor reviews submissions, and accepted agents are pushed to all supported hosts.
Evidence
The only number given is the claim that expert agents perform the same tasks 2.8x faster with 92% fewer tokens than an unaugmented agent. It is attributed to a separate study. The page does not give the tasks, the model, the host or the sample size.
The page also says Endor has seen CVEs go from disclosure to active exploitation in under 10 hours. No data is shown for that either.
Limits
- Not yet shipped: Two things are described as a "fast follow-up", not current features:
- agent attribution with scoped credentials
- checksummed, provenance-tracked published artifacts
Until they ship, agent actions run under your own git credentials, and you cannot verify that an installed artifact is the one Endor built.
- Telemetry: Telemetry flows back to Endor's Hub. Check whether that is acceptable for your environment.
- Open-source status: The page calls the agents "open source" but names no licence.
- Inconsistent catalog count: The agent count is ten or twelve depending on where you read.
Organisations named here
- Endor Labs
- Anthropic
- GitHub
- GitLab
- Claude Code
- Cursor
Technologies named here
- AURI Agents
- Claude Code
- Endor Labs Agent Kit
- Source Recipe
- Create Endor Labs Agent skill
- AURI Agent Hub
- SCA Remediation agent
- AI SAST Triage agent
- Probe Droid
- Endor Troubleshooter
- Remediation Planner
- Upgrade Impact Analysis
- Dependency Decision Helper
- Package Risk Summary
- Repository Dependency Reviewer
- Vulnerability Explainer
- endorctl
- Endor Labs MCP server
- Cursor
- Codex
- GitHub CLI
- GitLab CLI
- ai-plugins repo
- Model Context Protocol
- GitHub
- gh CLI
- glab
- YAML
Techniques named here
- Agentic remediation with rich context
- Source Recipe compilation to multiple hosts
Related in coding-agents


