 endorlabs.comarticle
Endor Labs: AURI Agents
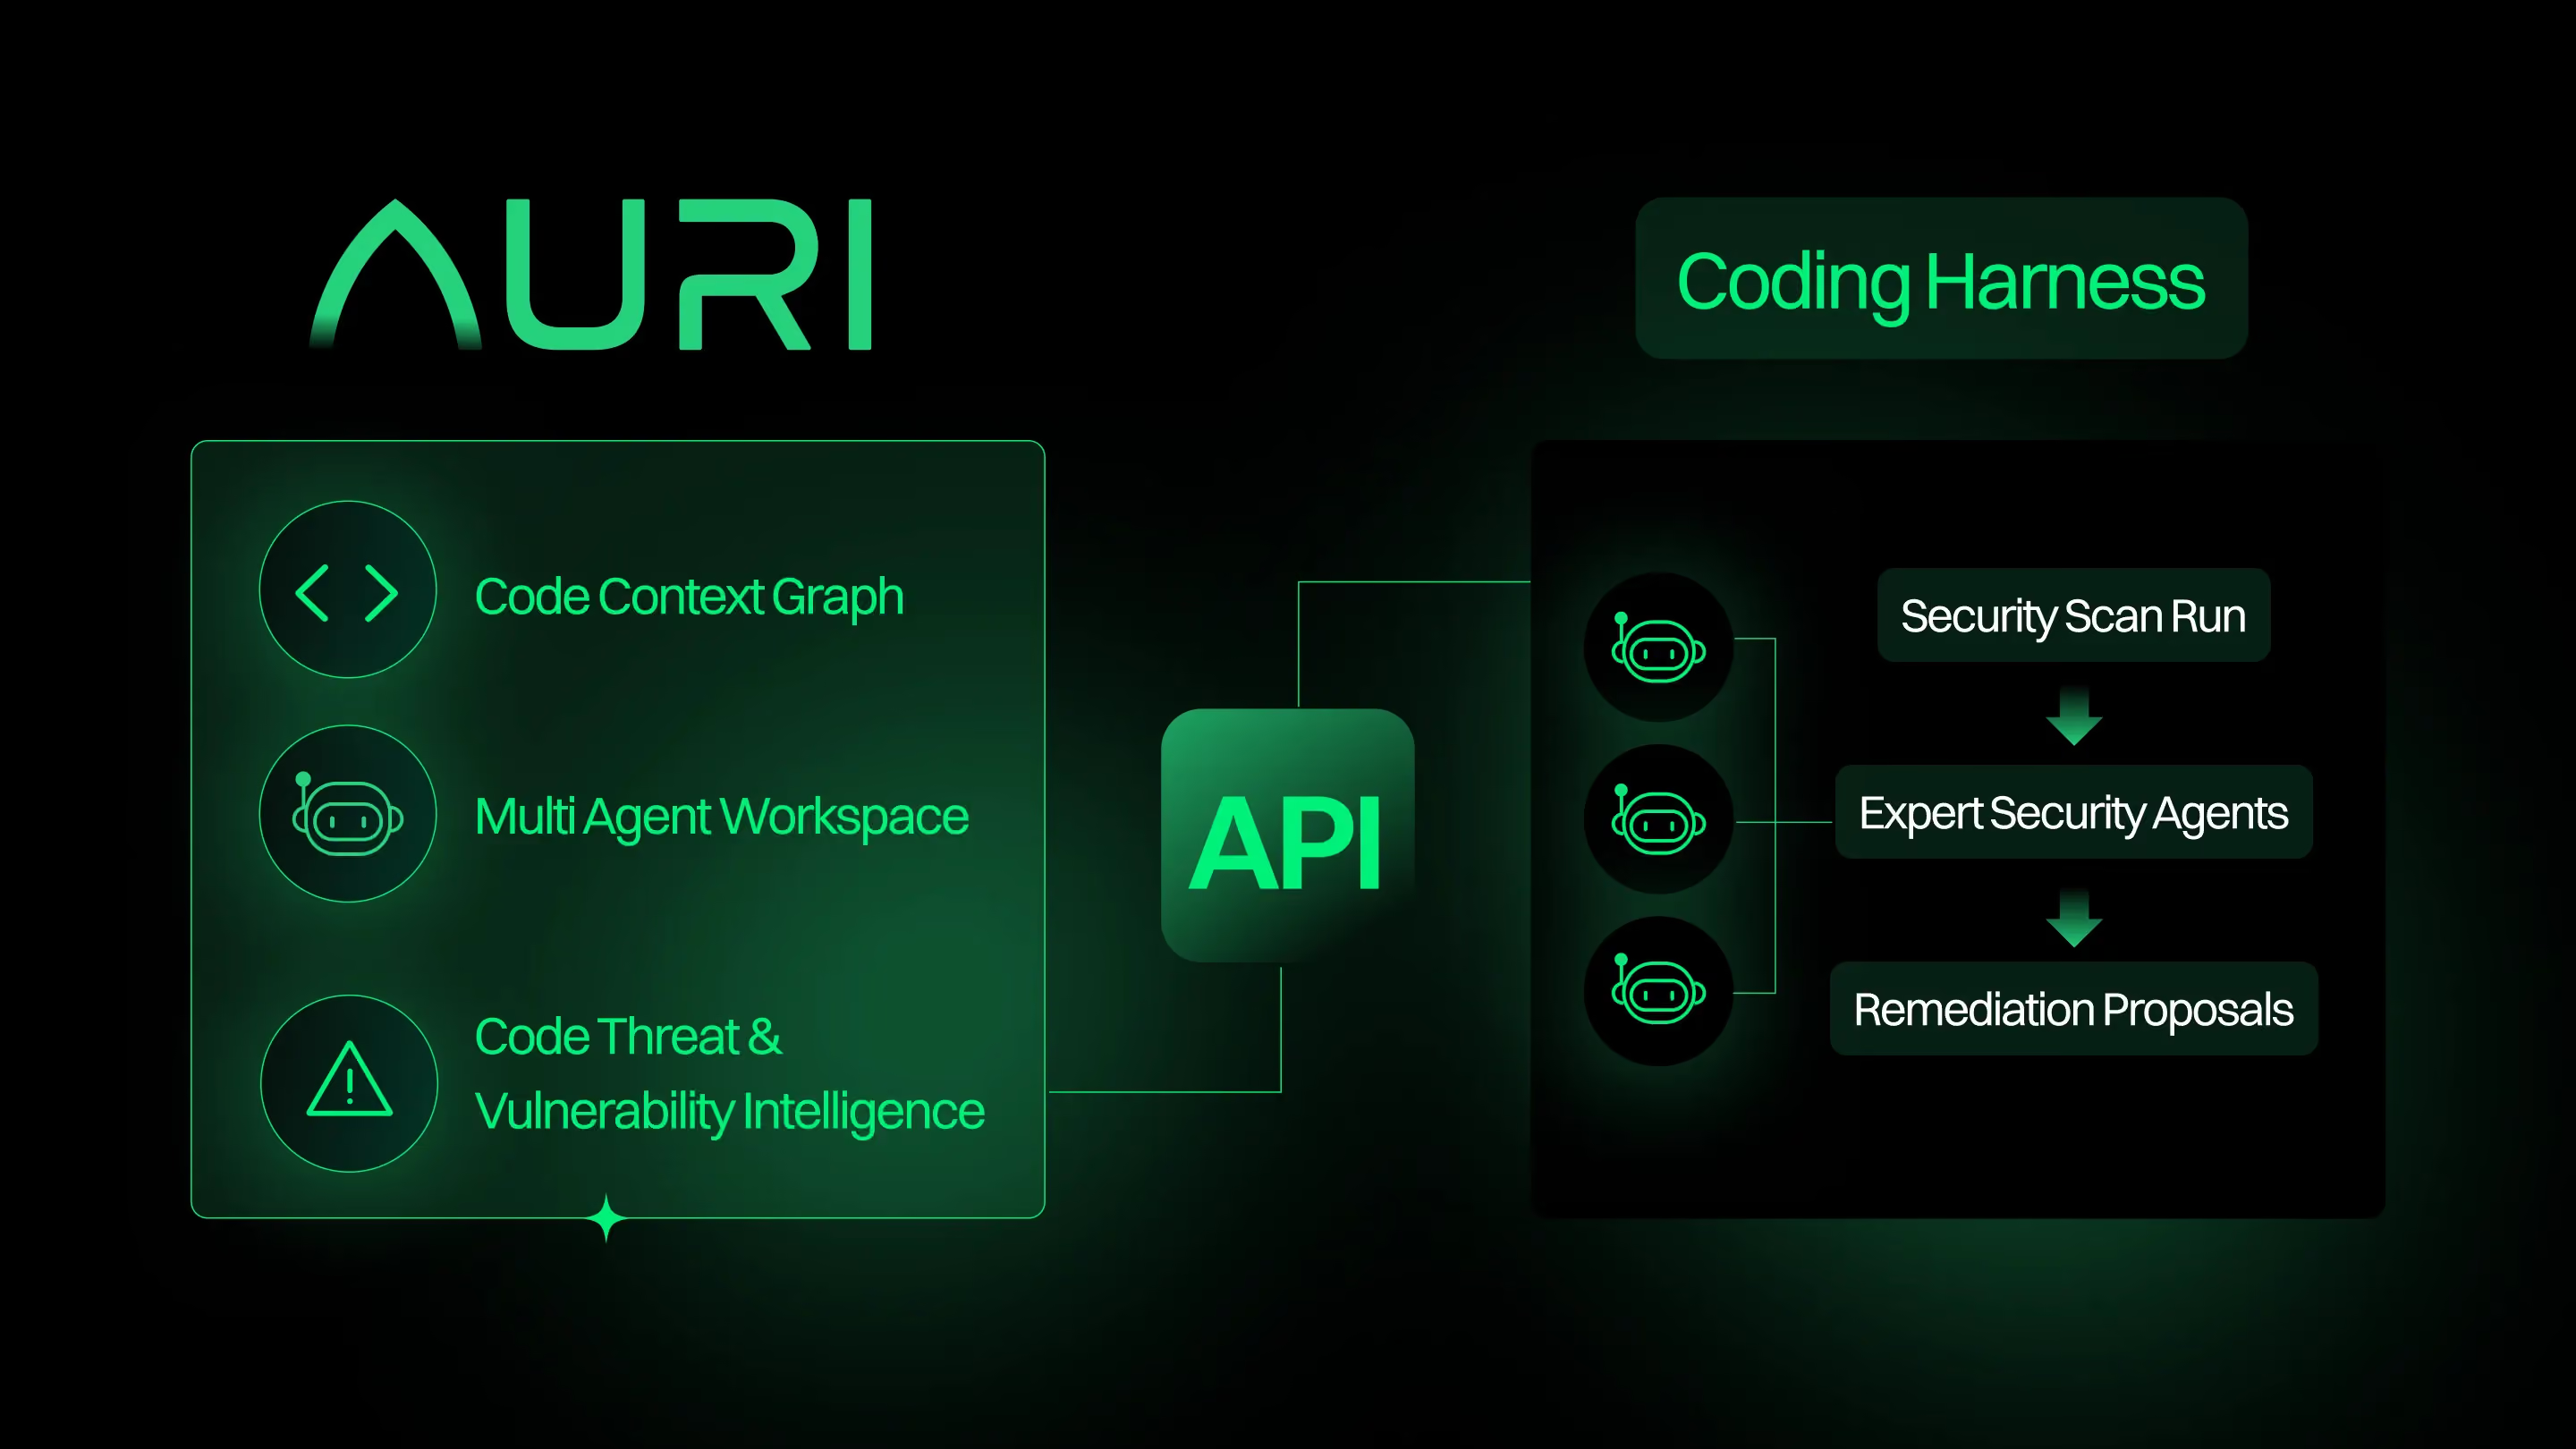
Endor Labs announces AURI Agents, twelve pre-configured AI agents (SCA Remediation, AI SAST Triage, Probe Droid, Endor Troubleshooter and others) that use Endor's reachability, upgrade-impact and policy data. They install into Claude Code, Codex, Cursor and similar hosts, and run on the customer's own LLM keys and git credentials (GitHub via gh, GitLab via glab). The open-source Endor Labs Agent Kit defines each agent as a YAML Source Recipe plus markdown instructions, compiled for each host, with a skill for authoring new agents. Most agents are read-only by default, and the ones that mutate state declare their permissions and require confirmation.
What it is
AURI Agents are Endor Labs' pre-built security agents for coding-agent hosts (Claude Code, Codex, Cursor and similar). They are free for every Endor Labs customer, and the page says they are available now. The companion Endor Labs Agent Kit is an open-source GitHub repo with the agent definitions and tooling for building your own.
How it works
- Execution: agents run on your side, using your LLM keys and your source-control credentials (
ghfor GitHub,glabfor GitLab). The page says code and secrets never cross into Endor's boundary and token spend stays yours. Telemetry does flow back to the Hub for central visibility. - Authentication: it goes through your local
endorctlconfiguration, so existing users have nothing new to set up. - Remaining catalog: besides the four agents named in the summary, there are six more:
- Remediation Planner, which previews fixes without opening PRs
- Upgrade Impact Analysis
- Dependency Decision Helper
- Package Risk Summary
- Repository Dependency Reviewer
- Vulnerability Explainer
- Chaining: agents can be chained together and combined with your own.
- Exception flow (AI SAST Triage): a developer requests an exception in a PR comment, and an AppSec reviewer approves it straight into policy.
- Authoring: a "Create Endor Labs Agent" skill drafts the recipe, prompt, eval cases and architecture diagram from a plain-English description. It then validates the result against the same guardrail checks Endor's own agents pass.
- Contributing: you can keep a custom agent private or open a PR. Endor reviews submissions, and accepted ones are pushed to all supported hosts by the build pipeline.
What to do
The page's Claude Code example, installing from the agent-kit repo:
mkdir -p .claude/agents
cp /path/to/endor-labs-agent-kit/claude-code/sca-remediation/sca-remediation.md \
  .claude/agents/sca-remediation.md
Then invoke it:
@agent-sca-remediation check this repository for P0 SCA findings I can start remediatingAlternatively, install as a plugin or extension by following the instructions in the ai-plugins repo.
Caveats
- Vendor claim: Endor says expert agents do the same tasks as an unaugmented agent 2.8x faster with 92% fewer tokens. This comes from its own published study, which the page does not detail, so treat it as unverified.
- Count mismatch: the page says "ten of them at launch" in one place and "twelve agents" in another.
- Attribution not shipped: scoped-credential agent attribution (to tell a person from their agent) is promised as a fast follow-up, not available now. The same goes for validated, checksummed artifacts with provenance. Until then, mutating actions run under your own credentials.
- Permissions: most agents are read-only by default. Mutating ones declare their permissions and require confirmation. Check which agents you enable, since SCA Remediation opens PRs and the exception workflow writes policy.
- Customers only: the agents draw on Endor's reachability, upgrade-impact and policy data, so they presumably need an existing Endor Labs deployment to be useful.
- Exploitation timing: Endor says it has seen CVEs go from disclosure to active exploitation in under 10 hours. The page gives no data behind this.
Organisations named here
- AURI Agents
- Endor Troubleshooter
- Probe Droid
Technologies named here
- Create Endor Labs Agent skill
- AURI Agent Hub
- SCA Remediation agent
- Probe Droid
- Endor Troubleshooter
- Remediation Planner
- Upgrade Impact Analysis agent
- Dependency Decision Helper
- Package Risk Summary agent
- Repository Dependency Reviewer agent
- Vulnerability Explainer
- endorctl
- Endor Labs MCP server and API
- Claude Code, Codex, Cursor
- gh CLI and glab
- ai-plugins repo
- Endor Labs
- AURI
- Claude Code
- Codex
- Cursor
- GitHub
- Endor Labs Agent Kit
Techniques named here
- Exception workflow
- Scan coverage auditing and failed-scan classification
- Endor Labs study
Related in AI Security

 blog.talosintelligence.comtool
Introducing CAIRN: Frontier tracking for AI-integrated malware (Cisco Talos)
 github.comadvisory
Flowise MCP Security Bypass Enables RCE
github.comrepoYesWeHack Claude Kit

 jfrog.comarticle