 huntress.comarticle
Deobfuscating Files for Flags: Huntress CTF 2025 Retro
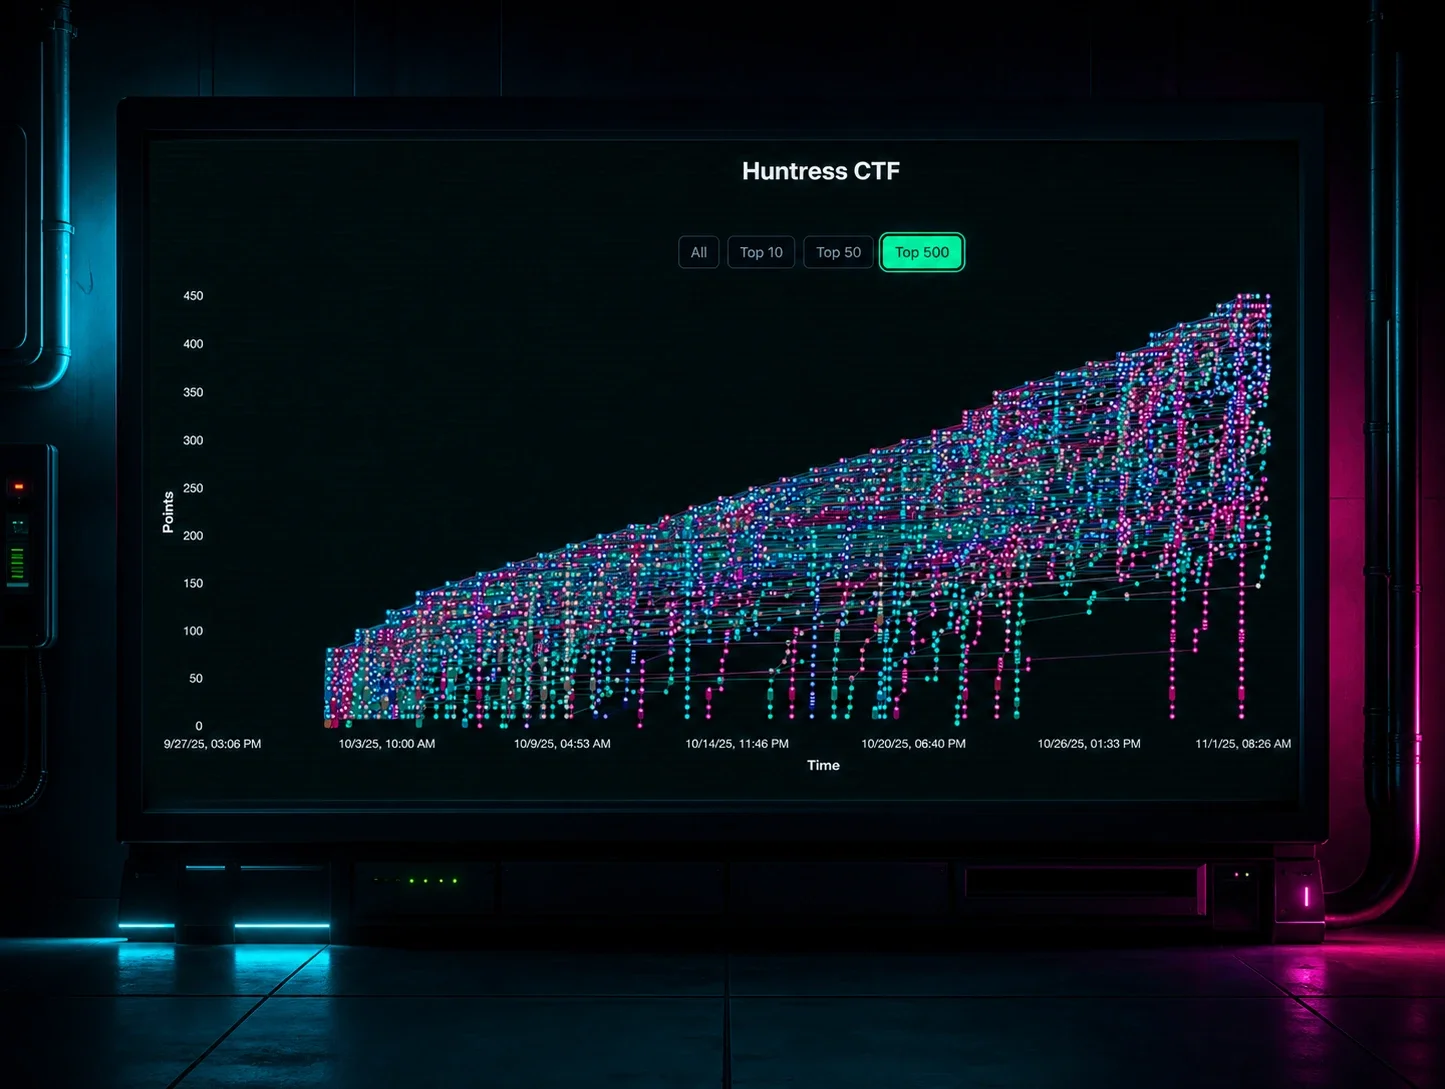
Huntress's recap of its October 2025 CTF event (11,898 registered users, 6,892 teams), covering challenge highlights like an AutoIT-decompiled cryptocurrency stealer ('Sandy'), a Rust-reimplemented supply-chain malware challenge ('Rust Tickler'), a Lua infostealer ('My Hawaii Vacation'), a Linux kernel rootkit reverse-engineering challenge ('Root Canal'), a nested PowerShell malware challenge ('Lizard'), an EntraID phishing challenge ('Angler'), and OSINT/DFIR challenges, with links to community-authored writeups for several. It also notes operational bloopers, including a database overload from launch traffic and participants triggering real Microsoft Defender alerts by analyzing malware outside isolated VMs.
Organisations named here
- HuskyHacks
- Matt Kiely
Technologies named here
- AutoIT
- AutoIT compiled executable
- Exe2Aut
- Crypto wallet browser extensions
- CourseStack
- Linux kernel
- TryHackMe
- Entra ID
- Hack The Box
- Microsoft Defender Antivirus
- PowerShell
- Rust
- Lua
- Microsoft Entra ID
- Microsoft Defender
Techniques named here
- Deobfuscation
- Reverse engineering
- Base64 decoding
- OSINT
- Phishing
- Digital forensics
- Malware analysis
- Threat hunting
Threat actors named here
- BlackCat ransomware
- Cryptocurrency stealer
- Rust-based supply-chain malware
- Lua infostealer malware
- Nested PowerShell malware
- Linux kernel rootkit
- NetSupport
Also named here
- John Hammond
Related in Learning
 hausec.comwriteup
Creating a Red & Blue Team Homelab
 bencteux.frarticle
ELearnSecurity Certified Threat Hunting Professional (eCTHPv2) review
 protocolsoup.comtool
Protocol Soup
 0xv1n.github.iowriteup