 huntress.comarticle
The Hacker's 2026 Playbook: Dark Web Tactics Targeting You
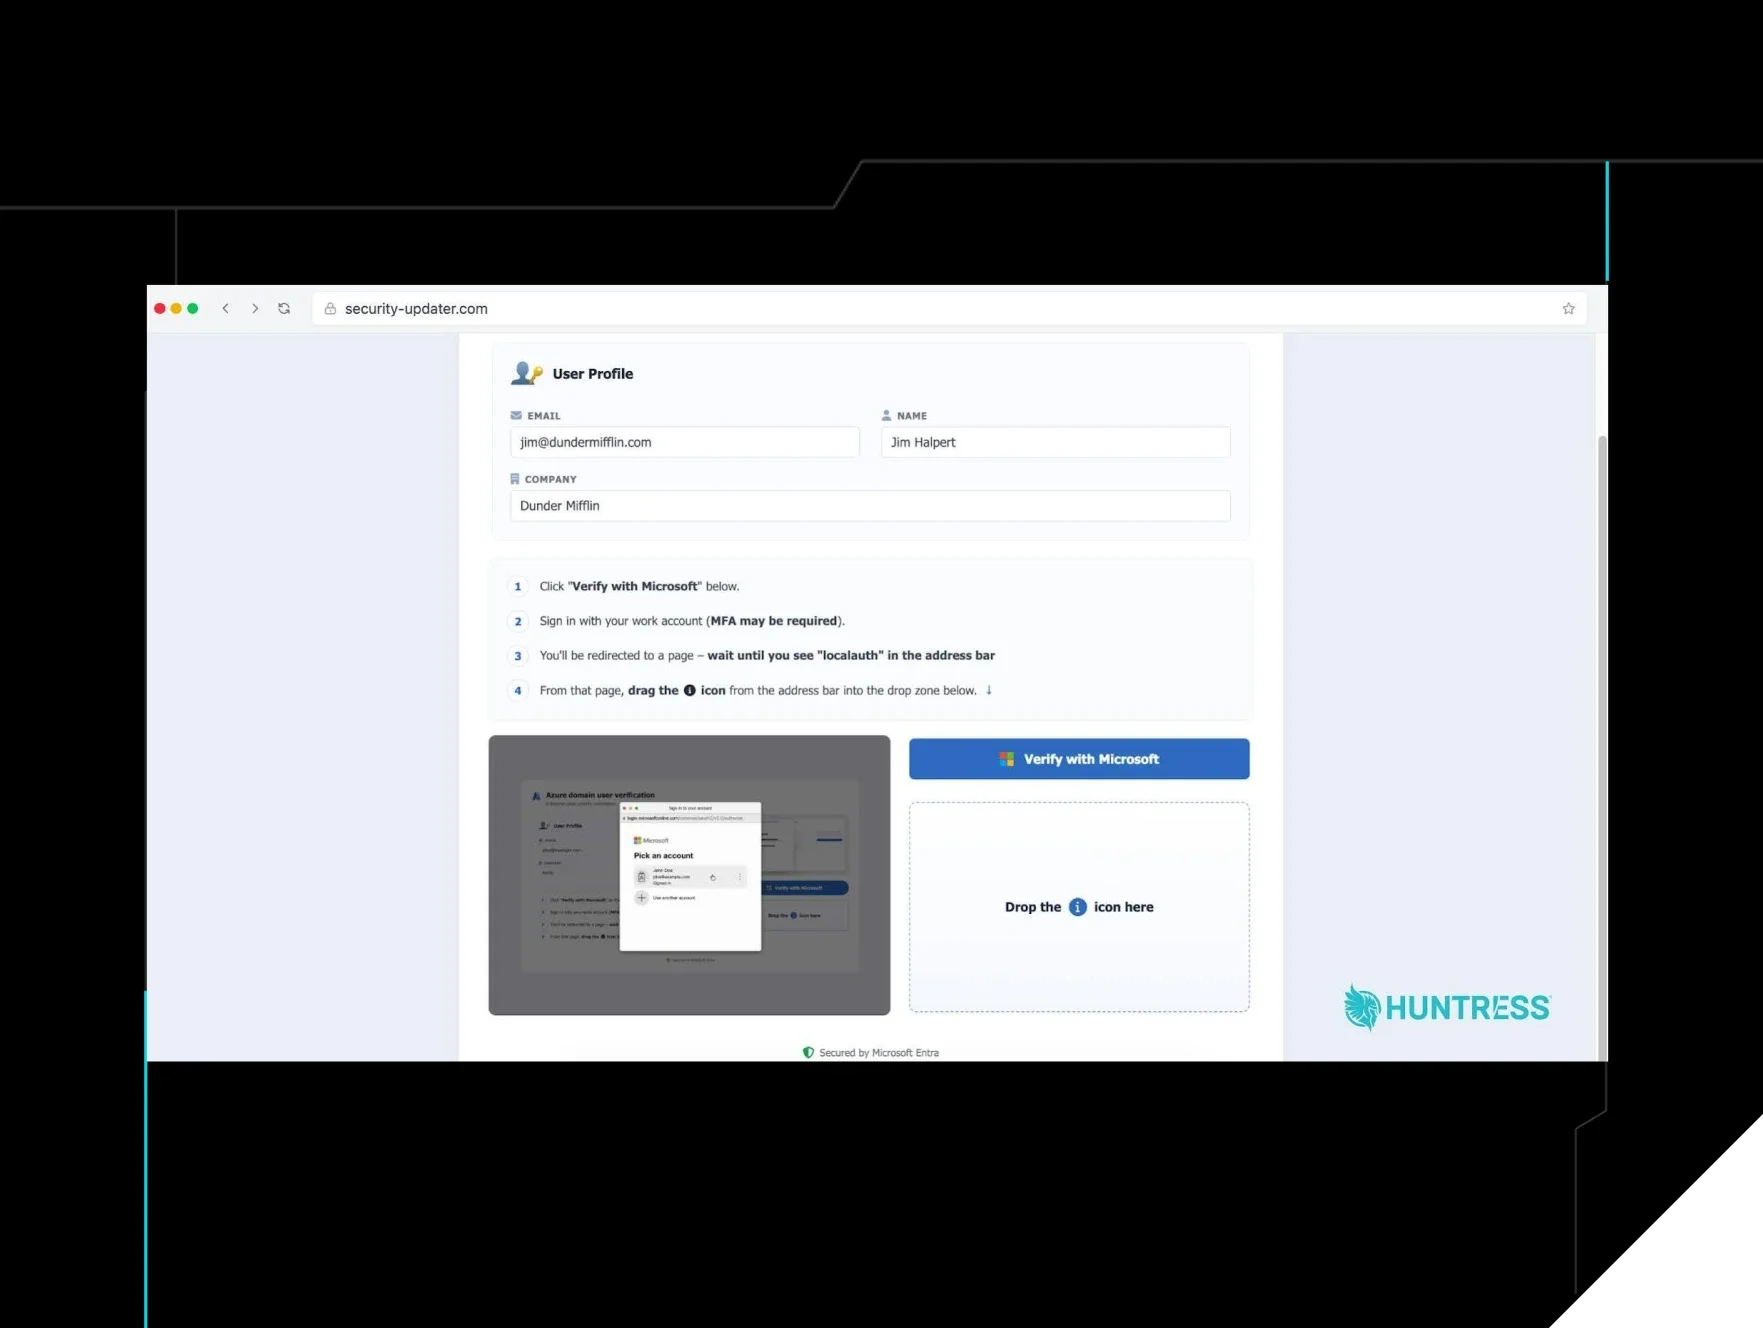
Huntress details ConsentFix, an evolution of ClickFix that abuses Microsoft 365 OAuth sign-in flows: victims are phished via password-protected Dropbox or DocSend lures, shown a fake Microsoft sign-in page, and tricked into dragging a localhost callback link into their browser, which exfiltrates OAuth tokens and hijacks the session without needing a password or triggering MFA. A cybercrime forum post published the full technique with working code and infrastructure such as Cloudflare Pages, workers.dev, and Pipedream webhooks, and showed attackers using LinkedIn, ZoomInfo, and Hunter.io to profile victims before sending lures.
TL;DR ConsentFix, a ClickFix variant, hijacks Microsoft 365 OAuth sessions via a fake sign-in and localhost-callback drag trick, with the full attack playbook now public on a cybercrime forum.
Organisations named here
- ClickFix
- ConsentFix
Technologies named here
- Microsoft 365
- Cloudflare Pages
- workers.dev
- Pipedream webhooks
- Dropbox
- DocSend
- ZoomInfo
- Hunter.io
- OAuth
- PowerShell
Techniques named here
- ClickFix
- ConsentFix
- Target reconnaissance
Threat actors named here
- ClickFix
- ConsentFix
Related in Threat Intel
 huntress.comwriteup
Reverse Engineering the Six Stages of MacSync Stealer and RAT
 huntress.comwriteup
AI-Coded Malware | Analyzing Vibe-Coded AD Enumeration | Huntress

 blog.talosintelligence.comtool
Introducing CAIRN: Frontier tracking for AI-integrated malware (Cisco Talos)
 huntress.comwriteup