 x.comthread
Dark Web Intelligence (@DailyDarkWeb) on X
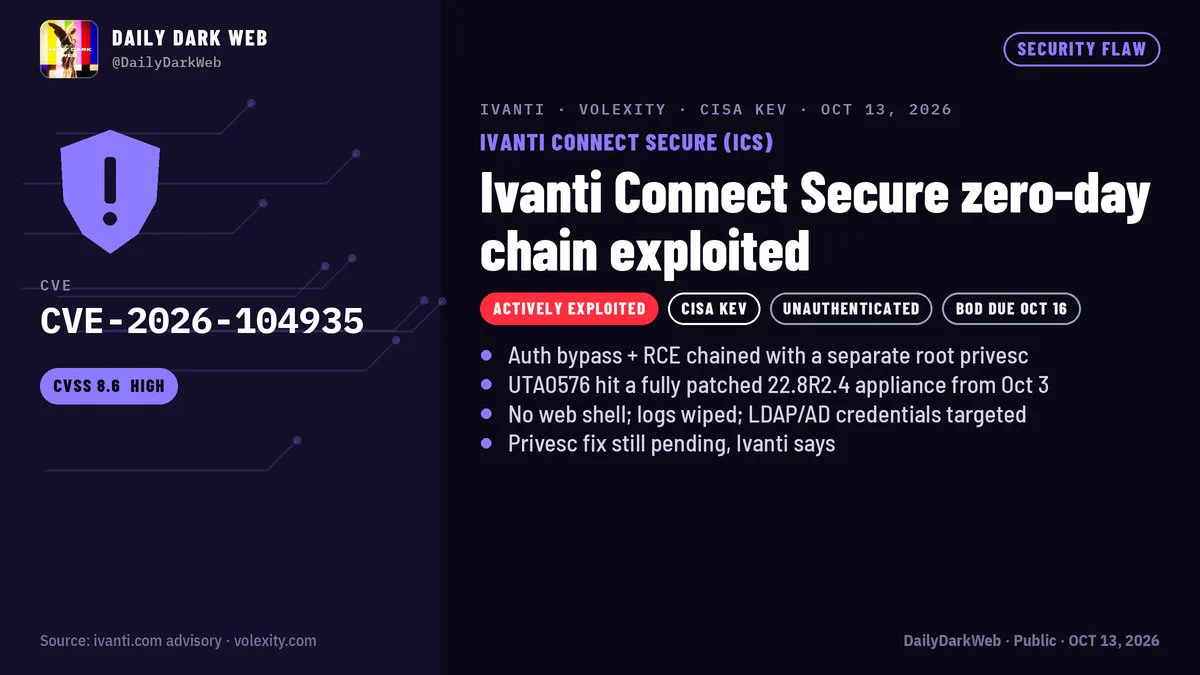
Social post summarizing Volexity's research on an Ivanti Connect Secure (ICS) zero-day chain, CVE-2026-104935. The chain pairs an auth bypass and a race-condition RCE with a separate privilege-escalation bug for root. Actor UTA0576 used it from Oct 3, 2026 against a fully patched 22.8R2.4 appliance, leaving no backdoor or web shell and deleting log entries. Post-exploitation included LDAP/AD credential theft, LAPS and BitLocker key searches, password spraying and packet capture. CISA added it to KEV with a due date of Oct 16. A clean Integrity Checker result does not rule out compromise because the chain patches code in memory only, so memory and network forensics are needed. The hunting lead is heavy requests to /dana-na/auth/url_default/welcome.cgi with a mismatched X-DSCGI-PATH header.
What it is
CVE-2026-104935 is a zero-day chain in Ivanti Connect Secure (ICS). Ivanti disclosed it on Oct 13, 2026 and reports limited exploitation in the wild. Volexity tracks the exploiting actor as UTA0576, which has used the chain since Oct 3, 2026. The post is a secondary summary of Volexity's research and Ivanti's advisory, so check those primary sources before relying on details.
How it works
- Both the auth bypass and the race-condition RCE sit under CVE-2026-104935.
- The actor chained them with a separate privilege-escalation bug to get root.
- There is no persistent implant. The actor re-ran the exploit for each command and then deleted log entries.
- The chain patches code in memory only and restores state afterward, which is why file-based integrity checks stay clean.
Preconditions / Affected
- Volexity saw exploitation against a fully patched 22.8R2.4 appliance, so being current on patches before Oct 13 gave no protection.
- The CVE record lists 22.8R2.5 and 25.1.3.0/25.1.3.1 as unaffected. Confirm your exact fixed build in Ivanti's advisory.
What to do
- Move to the fixed build named in Ivanti's advisory for your appliance. CISA's federal due date is Oct 16, 2026.
- Do not treat a clean Integrity Checker result as evidence of safety. Volexity says memory and network forensics are needed.
- Hunt for heavy requests to
/dana-na/auth/url_default/welcome.cgiwhere theX-DSCGI-PATHheader does not match the URL. - If you find signs of compromise, assume the post-exploitation activity Volexity observed:
- LDAP/AD credential theft
- searches for LAPS passwords and BitLocker recovery keys
- password spraying
- packet capture
Rotate the credentials and secrets reachable from the appliance.
- Expect missing or trimmed logs, so rely on network-side records such as proxy, flow and WAF logs where you have them.
Caveats
- Ivanti says a fix for the privilege-escalation bug is still coming. The patched build addresses the CVE-2026-104935 flaws, but the root step may stay open until that fix ships.
- No victim count is established.
- Volexity's attribution (criminal, low confidence) is tentative.
- The post truncates the advisory and research links, so verify build numbers against Ivanti directly.
Organisations named here
- Integrity Checker
CVEs named here
- CVE-2026-104935
Technologies named here
- Ivanti Integrity Checker
- CISA Known Exploited Vulnerabilities Catalog
- Volexity research blog, incident report on the exploitation
- Ivanti security advisory
- Ivanti Connect Secure
- VPN
- Active Directory
- Volexity
- CISA KEV
- LAPS
- BitLocker
- LDAP
Techniques named here
- Fileless operation
- Log entry deletion
- LDAP/AD credential theft
- Searching for LAPS passwords and BitLocker recovery keys
- Password spraying
- Packet capture
Threat actors named here
- UTA0576
Related in Threat Intel

 huntress.comwriteup
Reverse Engineering the Six Stages of MacSync Stealer and RAT
 huntress.comwriteup
AI-Coded Malware | Analyzing Vibe-Coded AD Enumeration | Huntress

 blog.talosintelligence.comtool
Introducing CAIRN: Frontier tracking for AI-integrated malware (Cisco Talos)
 huntress.comwriteup