 socket.devwriteup
Socket: Bitwarden CLI Compromised in Checkmarx Supply Chain Campaign
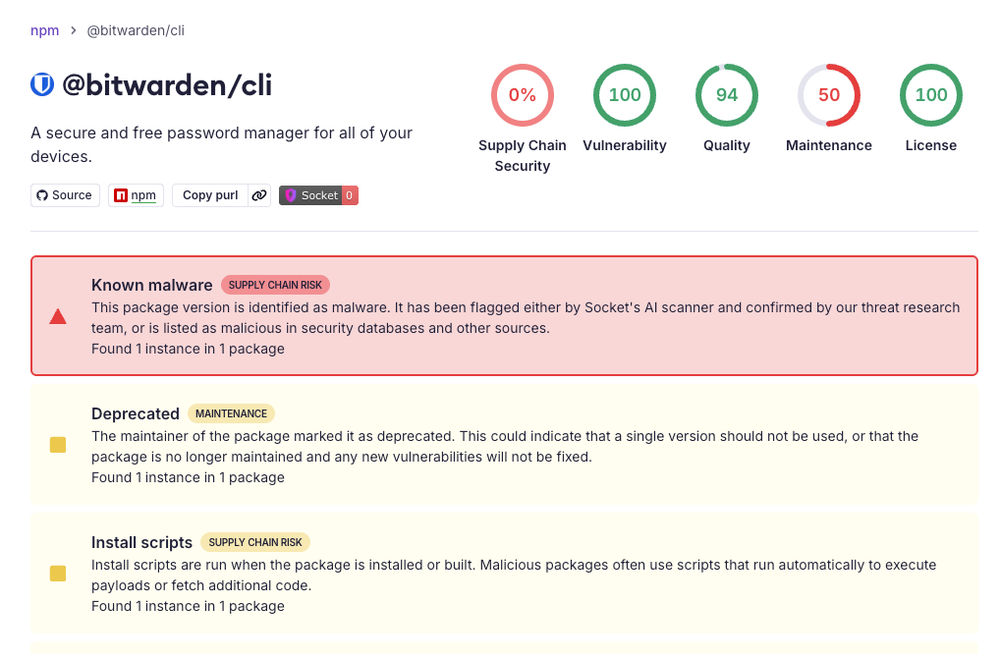
Socket researchers found that Bitwarden CLI 2026.4.0 was compromised via a hijacked GitHub Action in Bitwarden's CI/CD pipeline, part of the ongoing Checkmarx-themed supply chain campaign. The malicious bw1.js payload shares C2 infrastructure and code (gzip+base64 packed Python memory-scraper, Bun-based runtime, GitHub Actions workflow injector) with the earlier Checkmarx mcpAddon.js attack, but adds new indicators like a lock file, shell-profile persistence, and overt "Shai-Hulud: The Third Coming" / Butlerian Jihad ideological branding, plus a kill switch for Russian-locale systems. It harvests GitHub, AWS, Azure, GCP, npm, SSH, and Claude/MCP credentials and exfiltrates via GitHub commits and npm republishing.
What it is
Bitwarden CLI 2026.4.0 (npm @bitwarden/cli) shipped a malicious bw1.js after attackers abused a GitHub Action in Bitwarden's CI/CD pipeline — part of the Checkmarx supply chain campaign. Only the npm CLI package is affected; Bitwarden's Chrome extension, MCP server, and other distributions are not (as of this writing). The payload shares C2 and credential-harvesting code with the earlier Checkmarx mcpAddon.js.
How it works
bw1.js runs under a downloaded Bun v1.3.13 interpreter, exfiltrating to audit.checkmarx[.]cx/v1/telemetry (obfuscated via __decodeScrambled, seed 0x3039), plus GitHub API and npm registry. It scrapes GitHub tokens from Runner.Worker memory and env vars; harvests AWS (~/.aws/), Azure (azd), GCP (gcloud config config-helper), .npmrc, SSH keys, and Claude/MCP configs. Results land in public repos created under the victim account, Dune-themed named {word}-{word}-{3digits}, with tokens in commit messages marked LongLiveTheResistanceAgainstMachines. It propagates by republishing writable npm packages with injected preinstall hooks and injecting GitHub Actions workflows to capture secrets.
New indicators beyond the prior incident: lock file /tmp/tmp.987654321.lock; shell persistence into ~/.bashrc and ~/.zshrc; repo description Shai-Hulud: The Third Coming; a Russian-locale kill switch (exits if locale starts with ru, checking Intl.DateTimeFormat().resolvedOptions().locale and LC_ALL/LC_MESSAGES/LANGUAGE/LANG).
Preconditions / Affected
You installed @bitwarden/cli 2026.4.0 from npm on a developer system or build/CI runner holding any of the harvested credentials.
What to do
Treat this as a credential-exposure and CI/CD-compromise event. Remove the package; rotate GitHub tokens, npm tokens, cloud credentials, SSH keys, and CI/CD secrets exposed to those environments.
Review GitHub for unauthorized repo creation, unexpected files under .github/workflows/, suspicious runs, and public repos matching {word}-{word}-{3digits}. Search newly published repos for these Dune keywords:
atreides cogitor fedaykin fremen futar gesserit ghola harkonnen
heighliner kanly kralizec lasgun laza melange mentat navigator
ornithopter phibian powindah prana prescient sandworm sardaukar
sayyadina sietch siridar slig stillsuit thumper tleilaxu
Audit npm for unauthorized publishes, version changes, or new install hooks. On endpoints/runners, hunt for outbound connections to audit[.]checkmarx[.]cx, unexpected Bun execution, and access to .npmrc, .git-credentials, .env, cloud credential stores, gcloud, az, or azd.
Caveats
This is an ongoing investigation; Socket says a full technical analysis with confirmed affected versions and complete IOCs is still to come — the affected version "appears to be" 2026.4.0. Attribution is unsettled: shared tooling ties it to the Checkmarx ecosystem (claimed by TeamPCP), but the embedded ideological branding suggests a possible different operator or splinter group rather than a single confirmed actor.
Organisations named here
- Shai-Hulud
Technologies named here
- Bitwarden CLI
- Bun v1.3.13
- GitHub Actions
- npm registry
- npm
- Bun
- Bitwarden
- Checkmarx
Techniques named here
- Compromised GitHub Action in CI/CD pipeline
- C2 via obfuscated endpoint
- GitHub API exfiltration
- npm registry exfiltration/token theft
- Memory-scraping credential harvesting
- Credential harvesting from local files and env vars
- Supply chain propagation via npm preinstall hooks
- GitHub Actions workflow injection
- Locale-based kill switch
- Single-instance lock file
- Shell profile persistence
- Embedded RSA public keys and gzip+base64 payload packaging
Threat actors named here
- Checkmarx supply chain campaign
- TeamPCP
- Shai-Hulud
- bw1.js payload
Related in Supply Chain






