 huntress.comarticle
Every Ransomware Attack Has a Backstory
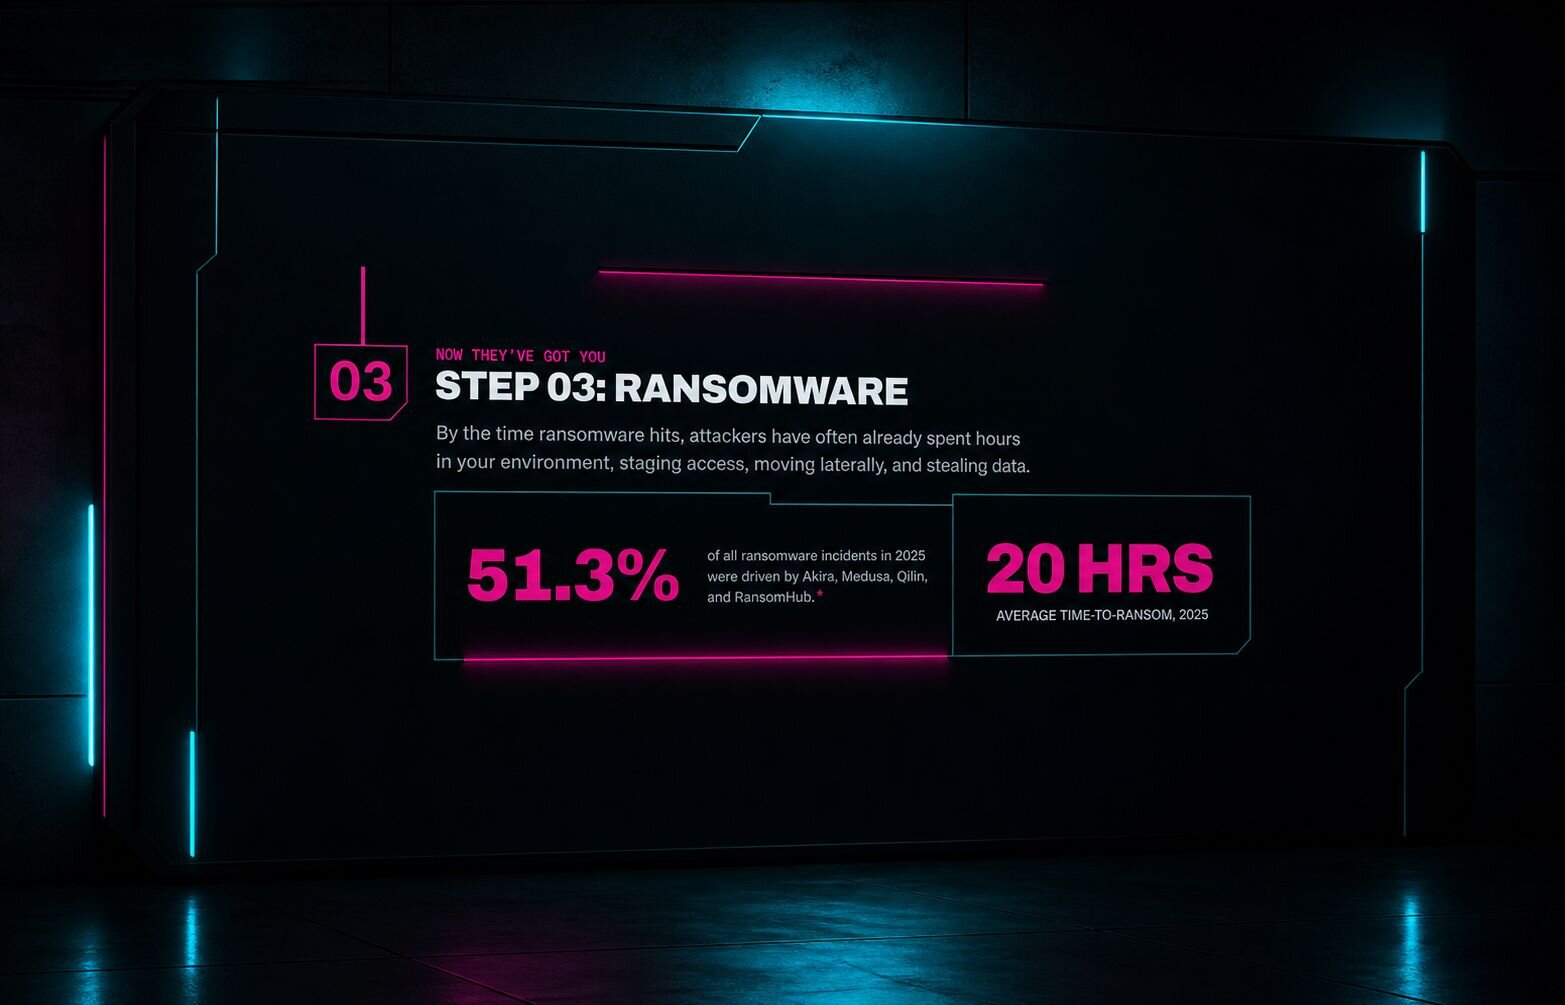
Huntress walks through the ransomware attack chain as a repeatable assembly line: initial access brokers selling footholds (often via infostealers, phishing, or unpatched internet-facing systems), Living-off-the-Land abuse of PowerShell and RMM tools to blend in, and ransomware as the final, visible stage. It cites a real cluster of six ransomware intrusions traced back to the same exposed Citrix NetScaler gateway and session-theft trick culminating in DragonForce ransomware, plus 2026 Cyber Threat Report stats: 37.2% of identity attacks involved suspicious logins, a 277% YoY spike in RMM abuse, ~20 hours average attacker dwell time before detonation, and Akira/Medusa/Qilin/RansomHub driving 51.3% of 2025 ransomware incidents.
Organisations named here
- Huntress 2026 Cyber Threat Report
- Medusa
Technologies named here
- PowerShell
- Citrix NetScaler gateway
- RMM tools
- Windows admin utilities
- Off-the-shelf remote access tool
- Citrix NetScaler
- RDP
- VPN
Techniques named here
- Session theft/hijacking
- Privilege escalation
- Living off the Land
- Lateral movement and data staging
- Access brokering by Initial Access Brokers
Threat actors named here
- DragonForce
- Akira
- Medusa
- Qilin
- Ransomhub
Related in Threat Intel
 huntress.comwriteup
Reverse Engineering the Six Stages of MacSync Stealer and RAT
 huntress.comwriteup
AI-Coded Malware | Analyzing Vibe-Coded AD Enumeration | Huntress

 blog.talosintelligence.comtool
Introducing CAIRN: Frontier tracking for AI-integrated malware (Cisco Talos)
 huntress.comwriteup